In a period where technology plays a crucial role, intelligent security systems have gained immense popularity, revolutionizing how we protect our homes and loved ones.
Among the various components of these systems, motion sensors are widely used for their ability to detect movement and trigger appropriate actions.
However, several myths and misconceptions surround motion sensors and their role in smart security systems. In this article, we will debunk these misconceptions and shed light on the importance and benefits of motion sensors in securing our homes.
Myth: Motion sensors are triggered by any movement
Fact: One common misconception is that motion sensors are sensitive to any movement, including pets or inanimate objects. However, modern motion sensors are designed to differentiate between the movements of humans and other sources. They employ various technologies, such as passive infrared (PIR), microwave, or dual-technology sensors, to detect the unique heat signatures and patterns associated with human movement, thereby minimizing false alarms.
Myth: Motion sensors can’t detect intruders in the dark.
Fact: Some believe motion sensors are ineffective in low-light or dark environments. However, many motion sensors now come equipped with infrared technology, known as “night vision.” These sensors can detect changes in heat signatures even in complete darkness, ensuring accurate detection and reliable security regardless of the lighting conditions.
Myth: Motion sensors are easily fooled by environmental factors.
Fact: Another misconception is that motion sensors can be easily fooled by environmental factors such as moving curtains, plants, or shadows. While it is true that certain environmental conditions can cause false alarms, modern motion sensors are equipped with advanced algorithms that can distinguish between actual threats and environmental changes. They are designed to analyze movement patterns, speed, and duration, ensuring accurate detection and minimizing false alarms.
Myth: Motion sensors are only helpful indoors.
Fact: Many people believe motion sensors are solely intended for indoor use. However, outdoor motion sensors are widely available and designed to withstand various weather conditions. These sensors are crucial for outdoor security, as they can detect and alert homeowners to suspicious activity around the property’s perimeter, providing an added layer of protection.
Myth: It’s challenging to install and use motion sensors.
Fact: Motion sensors are simple to install and use. Since most motion sensors don’t require substantial wiring, installation is simpler. They frequently include comprehensive installation instructions that walk customers through the procedure. Additionally, user-friendly smartphone apps make it easy to control and monitor smart security systems with motion sensors, providing convenience and usability for homeowners.
Leveraging Motion Sensors in Smart Security Systems
Motion sensors play a crucial role in the comprehensive security solutions offered by various companies, including Ajax Systems. Motion sensors from Ajax alam provides homeowners with advanced and reliable protection by incorporating motion sensors into their intelligent security systems.
Let’s explore the benefits and features of smart security systems with motion sensors.
Real-time Intrusion Detection
Motion sensors enable real-time detection of unauthorized movement within the protected area. They can trigger immediate alerts to homeowners, security personnel, or authorities, enabling swift action in the event of a potential break-in or intrusion.
Intelligent security systems with motion sensors allow homeowners to define and customize security zones. This flexibility ensures that the motion sensors are activated only in designated areas, minimizing false alarms and focusing on the highest-vulnerability areas.
Automation and Integration
Motion sensors can be integrated with other smart home devices and automation systems. This integration allows for enhanced security features, such as automatic lighting activation when motion is detected or integration with surveillance cameras to capture real-time video evidence.
Deterrence and Peace of Mind
The presence of motion sensors in a smart security system acts as a strong deterrent to potential intruders. Visible motion sensors can make criminals think twice before attempting any unauthorized entry.
Smart Security Systems and Motion Sensors: Frequently Asked Questions
Are smart security systems complex and difficult to install?
Myth: While some advanced systems require professional installation, many contemporary options are designed for DIY setup. They come with user-friendly apps and clear instructions, making installation straightforward for most tech-savvy individuals.
Do motion sensors trigger on pets and cause false alarms?
Myth: Modern motion sensors offer various sensitivity settings and pet-immune features. These features can distinguish between small pets and actual intruders, significantly reducing false alarms.
Do smart security systems require expensive monthly fees?
Myth: While some systems come with monitoring subscriptions, many offer affordable options with self-monitoring features. These allow you to receive alerts and view live camera feeds without a monthly cost.
Are smart security systems vulnerable to hacking?
Myth: Reputable brands prioritize security with encryption protocols and secure authentication methods. Regularly updating software and choosing strong passwords further reduces hacking risks.
When choosing a smart security system, consider your specific needs, budget, and technical comfort level. Research features like motion sensors, cameras, and compatibility with other smart home devices.
Remember, no system is foolproof, but a well-chosen and properly installed system can significantly increase your home’s security and peace of mind.
Conclusion
Motion sensors are indispensable components of intelligent security systems, contributing to enhanced protection, detection, and deterrence. We can appreciate their importance in securing our homes by debunking common myths about motion sensors.
Whether indoors or outdoors, motion sensors provide an additional layer of security, empowering homeowners with reliable intrusion detection and peace of mind. Embracing the advancements in smart security technology, including motion sensors, ensures that our homes remain safe and protected in the modern age.
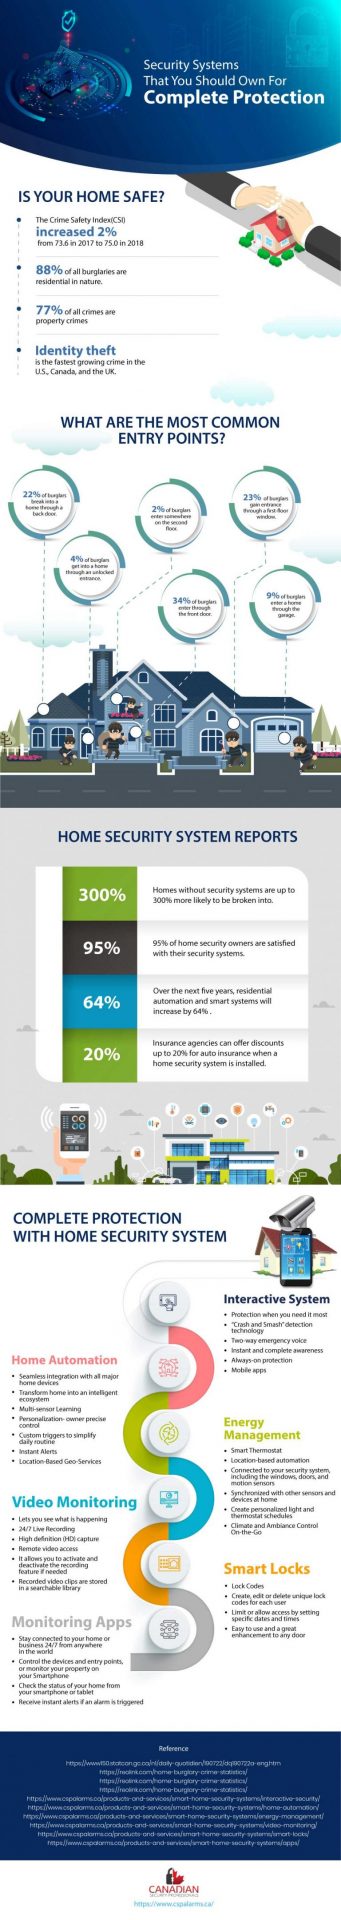
Here, we will show you security tips to protect your home from burglary.
A home security device is an essential system that can quickly alert you and your loved ones if someone breaks into your home. For instance, as soon as a burglar triggers the system, a message will be sent to the police.
Cameras will also start recording immediately, and an alarm will alert you of the break-in. Even better, a state-of-the-art home security system may serve as a deterrent, as many burglars who notice the system may avoid trying to break into your home altogether.
Here, we will discuss alarm systems in Hamilton and pertinent security tips that can help protect your home from burglary.
First and foremost, the most important reason to own an alarm system is that it will help reduce the risk of a crime in your home. A recent study by the Electronic Security Association found that 90% of burglars surveyed said they would not attempt to break into a property with a home security system installed.
Another recent study by the Greenwich Report of Residential Security found that homes without a home security system installed were up to 3.5 times more likely to be broken into. While installing deadbolts on your doors and locks on your windows may help reduce the risk of a burglary, installing a top-of-the-line home security system is arguably the best way to protect your home from criminal activity.
As for cons, some people may worry about the cost of a home security system. For instance, the homeowner may need to pay initial fees, such as installation fees. They may also have to pay a monthly bill, which some homeowners may find inconvenient.
Most people feel that the initial start-up cost is worth it for the peace of mind they receive, knowing that their loved ones and most prized possessions will be protected 24/7, but weighing the pros and cons of owning a home security system is ultimately a decision you will need to make.
Using a Security System to Deter Burglars
A quick and easy way to signal to would-be burglars that a cutting-edge home surveillance system is currently protecting your property is to display yard signs and stickers on your windows. More often than not, such signs will serve as a clear signal that your home is protected, which will make most burglars think twice before breaking.
Install Motion-Sensor Lights
A poorly lit property will also make it easy for criminals to hide and lurk around the targeted home, so installing motion-activated lights will help illuminate hiding spots in and around your property, which may alert neighbors of suspicious activity and scare off any potential criminals.
Motion-activated lights can be integrated into your home security package to provide even more excellent protection. For instance, you can program the system to start recording footage with its cameras as soon as the motion sensors on the lights are triggered.
Install Surveillance Cameras
On that note, installing outdoor and indoor surveillance cameras around your home will quickly alert criminals that your home is always protected. And, if a criminal is foolish enough to try and break in, the cameras will soon track and record their face and movements, so you will have ample evidence to provide to the police to help apprehend the suspect.
Installing alarms may also help protect your home, as the last thing a criminal wants to hear is the blaring sound of a booming alarm. If you wish, you can also program the alarms to be activated by motion-based window and door sensors.
Also, even if you are not home when the break-in occurs, the alarm will notify your neighbors and nearby pedestrians that something is amiss at your home and may galvanize them to act on your behalf.
Reinforce Your Doors
We would also suggest reinforcing your doors. For instance, you can opt for a top-of-the-line solid metallic lock with anti-drilling properties. You can also get three-inch screws for your hinges and strike plates to reinforce your doors. That is, they will bite into the stud, making it difficult for a burglar to try and kick the door in.
Keep Your Home Private
You should also ensure that people walking or driving by cannot see the interior of your home from their vantage point. Use privacy film, blinds, or curtains on the glass so that people cannot “window shop” and quickly check whether you are home and what you own. The last thing you want is to tempt a burglar to break in after having perused your valuables via your large floor-to-ceiling bay windows or sliding doors made of glass.
Invest in a Safe
Finally, we recommend investing in a fireproof safe with the help of a Fireproofing contractor in Vermont so that you can protect your most prized possessions without fear. The safe should also be bolted to either the floor or the wall so that anyone who breaks in won’t be able to extract the safe and walk out the front door with it.
We would also suggest that you keep the passcode private and avoid writing it anywhere that criminals can easily access, including your smartphone, tablet, or computer. The receipts for expensive items should also be stored in the safe, as you may need them for insurance claim processing if someone escapes with your valuables.
Note: This is a guest post by the Canadian Security Professionals. You can reach them via 1-877-494-9911 or their website.
In this post, I will show you the role of artificial intelligence in cybersecurity.
In an increasingly interconnected world where our lives are intricately woven with digital threads, the importance of cybersecurity cannot be overstated.
As technology advances, so do the threats posed by cybercriminals, who constantly seek new ways to exploit vulnerabilities and infiltrate networks.
In this relentless battle, a formidable ally has emerged: Artificial Intelligence (AI). With its ability to analyze massive amounts of data, detect patterns, and make intelligent decisions, AI is revolutionizing the field of cybersecurity.
In this comprehensive article, we explore the multifaceted role of AI in fortifying the digital frontier and examine how it empowers defenders to protect against evolving threats proactively.
Overview Of Artificial Intelligence (AI)
Artificial Intelligence (AI) encompasses computer systems and algorithms that simulate human intelligence, enabling them to learn, reason, solve problems, and make decisions.
It involves techniques like Machine Learning, Deep Learning, Natural Language Processing, and Computer Vision. AI finds applications in healthcare, finance, autonomous vehicles, virtual assistants, cybersecurity, and more.
While AI offers tremendous potential to enhance productivity and transform industries, ethical considerations and challenges related to bias, privacy, and workforce impact must be addressed.
The responsible development and deployment of AI will shape the future as intelligent systems become an integral part of our lives and decision-making processes.
Cybersecurity Overview
Cybersecurity is a critical discipline that safeguards digital systems, networks, and sensitive information from unauthorized access, damage, and exploitation.
In an increasingly interconnected world, where cyber threats continue to increase in sophistication and scale, cybersecurity plays a pivotal role in ensuring data and systems’ confidentiality, integrity, and availability. This has led to the uprising of several AI consulting services.
It encompasses a comprehensive range of strategies, technologies, and practices designed to detect, prevent, and respond to cyber attacks, including malware, phishing, data breaches, and insider threats.
With the potential for significant financial, reputational, and operational consequences, organizations across industries must prioritize robust cybersecurity measures to mitigate risks, establish resilient defenses, and protect against ever-evolving threats in the dynamic digital landscape.
AI Security Software
Kaspersky Lab
Kaspersky Antivirus is an antivirus protection solution that protects your computers from virus attacks and other...Show More
Kaspersky Antivirus is an antivirus protection solution that protects your computers from virus attacks and other threats that may result from internet usage or other forms of usage. Show Less
60% OFF
Panda Dome Security Suite
Your advanced protection suite for home and business needs.
Your advanced protection suite for home and business needs. Show Less
66% OFF
Norton 360
Norton 360 is a security suite that utilizes advanced machine learning technology in dealing with all types of malware...Show More
Norton 360 is a security suite that utilizes advanced machine learning technology in dealing with all types of malware including Trojans, ransomware, etc. 100% guaranteed protection against all types of malware and your best bet for privacy protection. Show Less
Avira Prime
Avira Prime is the ultimate security suite for data safety and protection from online threats that gives you full access...Show More
Avira Prime is the ultimate security suite for data safety and protection from online threats that gives you full access to Avira products like antivirus, Phantom VPN, software updater, system optimization tool, and a password manager. Show Less
25% OFF
ESET HOME Security Premium
ESET HOME Security Premium is a fully-fledged security software with amazing features and even a password manager. Smart...Show More
ESET HOME Security Premium is a fully-fledged security software with amazing features and even a password manager. Smart protection for Windows, Mac, and Android devices. Show Less
G DATA Total Security
G DATA Total Security is a complete protection suite that offers total security online and offline. The suite includes...Show More
G DATA Total Security is a complete protection suite that offers total security online and offline. The suite includes an antivirus engine, a password manager, firewall protection, device control, and internet security tools. Intelligent security suite for all device types. Show Less
38% OFF
AVG Ultimate
A combined antivirus plus VPN for total protection.
A combined antivirus plus VPN for total protection. Show Less
50% OFF
McAfee Total Protection
An easy-to-use security suite for data safety and device protection.
An easy-to-use security suite for data safety and device protection. Show Less
53% OFF
Trend Micro Premium Security Suite
Premium security suite for device protection and identity safety.
Premium security suite for device protection and identity safety. Show Less
VIPRE Advanced Security
Best security solution for emerging threats and data safety.
Best security solution for emerging threats and data safety. Show Less
Total AV
Protects your devices and online activities in real-time.
Protects your devices and online activities in real-time. Show Less
PC Matic Security
PC Matic Security is a security software that protects against malware, viruses, and ransomware.
PC Matic Security is a security software that protects against malware, viruses, and ransomware. Show Less
K7 Total Security
K7 Total Security is a comprehensive security software suite that provides protection against malware, viruses, and...Show More
K7 Total Security is a comprehensive security software suite that provides protection against malware, viruses, and other cyber threats, as well as features such as parental controls, data encryption, and a personal firewall. Show Less
F-Secure Total
F-Secure Total is a security suite that provides protection for your devices against malware, viruses, and online...Show More
F-Secure Total is a security suite that provides protection for your devices against malware, viruses, and online threats with features like antivirus, firewall, VPN, and parental control. Show Less
Sophos
Sophos Antivirus is a security software that helps protect computer systems from various malware and online threats.
Sophos Antivirus is a security software that helps protect computer systems from various malware and online threats. Show Less
Surfshark One
Surfshark One is a cybersecurity bundle that provides users with Surfshark VPN, Alert, Search, and Antivirus that...Show More
Surfshark One is a cybersecurity bundle that provides users with Surfshark VPN, Alert, Search, and Antivirus that combines security, privacy, and convenience into one powerful package. Surfshark is an award-winning VPN service for keeping your digital life secure. Show Less
Avast One
Avast One is an all-in-one security suite offering antivirus protection, VPN, performance optimization, and privacy...Show More
Avast One is an all-in-one security suite offering antivirus protection, VPN, performance optimization, and privacy tools for comprehensive digital security. Show Less
The Role of Artificial Intelligence in Cybersecurity
Intelligent Threat Detection and Prevention
One of the primary roles of AI in cybersecurity lies in its capability to identify and neutralize threats. Traditional security measures often rely on known patterns and signatures, making them susceptible to novel and sophisticated attacks.
Conversely, AI excels at recognizing patterns and anomalies within vast datasets, enabling it to detect emerging threats and zero-day vulnerabilities. Machine Learning (ML) algorithms, a subset of AI, can analyze network traffic, user behavior, and system logs to identify malicious activities in real time.
By continuously learning from new data, AI-based systems adapt and enhance their detection capabilities, providing organizations with proactive defense mechanisms.
To identify potential threats, AI-powered threat intelligence platforms can monitor multiple data sources, including public forums, social media, and dark web marketplaces. By analyzing conversations and indicators of compromise, AI can provide early warnings about possible attacks, enabling organizations to take preemptive action.
In the face of cyber threats, time is of the essence. Human analysts often struggle to keep pace with the volume and speed at which attacks occur. Here, AI-driven automated incident response systems play a vital role.
These systems leverage AI’s decision-making capabilities to swiftly identify, contain, and mitigate potential breaches.
By integrating AI into incident response workflows, organizations can reduce response times, minimize damage, and free up human analysts to focus on complex tasks that require their expertise.
AI can also assist in generating real-time alerts, performing forensic analysis, and providing recommendations for remediation.
Furthermore, AI can analyze historical incident data to identify patterns and develop response strategies. This proactive approach allows organizations to anticipate potential attacks and improve their incident response readiness.
Enhanced User Authentication and Access Control
Securing access to sensitive information and systems is critical in preventing unauthorized access and data breaches. Traditional authentication methods like passwords are increasingly vulnerable to sophisticated attacks.
AI offers robust alternatives, including biometric authentication and behavior-based authentication. Facial recognition, fingerprint scanning, and voice recognition systems utilize AI algorithms to accurately authenticate users, making it significantly harder for cybercriminals to impersonate legitimate users.
Additionally, AI-powered systems can continuously monitor user behavior patterns to detect anomalies and potential insider threats, strengthening access control measures.
By analyzing user activities, AI can identify suspicious behavior deviations from standard patterns, such as unusual login locations or access attempts outside regular working hours.
This proactive monitoring helps organizations prevent unauthorized access and identify potentially compromised accounts promptly.
AI’s predictive capabilities are invaluable in identifying potential vulnerabilities and proactively addressing them before they can be exploited.
AI can identify trends and predict future attack vectors by analyzing historical data. This enables organizations to allocate resources effectively, prioritize security measures, and stay one step ahead of cybercriminals.
Moreover, AI can simulate various attack scenarios, allowing defenders to assess their system’s resilience and devise robust defense strategies.
By analyzing attack patterns, AI can generate insights that help organizations strengthen their defenses by identifying weak points and implementing targeted security measures.
While the potential of AI in cybersecurity is immense, it is crucial to address ethical considerations and limitations. Transparency, accountability, and data privacy must be carefully managed to ensure AI is used responsibly.
Bias in AI algorithms, false positives/negatives, and adversarial attacks are among the challenges that must be mitigated. Human oversight and intervention remain vital to ensure AI-driven decisions align with ethical standards.
Frequently Asked Questions About Artificial Intelligence in Cybersecurity
What is the role of AI in cybersecurity?
Artificial Intelligence (AI) strengthens cybersecurity by analyzing massive amounts of data, detecting patterns, and identifying anomalies that may indicate cyber threats. AI helps organizations proactively detect and prevent attacks, including zero-day vulnerabilities, malware, phishing, and other sophisticated exploits. By continuously learning from new data, AI improves threat detection and response over time.
How does AI detect and prevent cyber threats?
AI-powered systems analyze network traffic, user behavior, and system logs to recognize suspicious patterns. Machine Learning (ML) algorithms can identify anomalies in real time, alerting organizations to potential breaches. AI can also monitor external data sources, such as forums and dark web marketplaces, to provide early warnings about emerging threats, enabling proactive security measures.
What is automated incident response and how does AI help?
Automated incident response leverages AI to quickly identify, contain, and mitigate cyberattacks. Unlike traditional responses, which rely solely on human analysts, AI can generate real-time alerts, perform forensic analysis, and recommend remediation steps. This reduces response times, minimizes damage, and frees human analysts to focus on complex decision-making tasks.
How does AI enhance user authentication and access control?
AI improves access security through advanced methods like biometric authentication (facial recognition, fingerprint, and voice scanning) and behavior-based authentication. AI systems can continuously monitor user activity to detect unusual behavior, such as logins from unexpected locations or unusual access patterns, preventing unauthorized access and insider threats.
Can AI predict and prevent future cyberattacks?
Yes. AI’s predictive capabilities allow it to analyze historical attack data, identify trends, and forecast potential vulnerabilities. Organizations can use these insights to proactively strengthen defenses, allocate resources effectively, and simulate attack scenarios to test system resilience. This predictive approach helps prevent attacks before they occur.
Are there ethical concerns with using AI in cybersecurity?
While AI provides powerful security benefits, it raises ethical considerations. Challenges include algorithmic bias, false positives/negatives, data privacy issues, and potential adversarial attacks. Responsible AI deployment requires human oversight, transparency, and accountability to ensure decisions align with ethical standards.
Why is AI important for organizations in the modern digital landscape?
AI enhances cybersecurity efficiency and effectiveness by providing real-time threat detection, automated response, and predictive insights. Organizations leveraging AI can better protect sensitive data, minimize operational disruptions, and stay ahead of evolving cyber threats. Combining AI with human expertise ensures a robust, ethical, and proactive cybersecurity strategy.
Conclusion
Artificial Intelligence has emerged as a transformative force in the realm of cybersecurity. Its ability to detect, prevent, and respond to threats in real time, coupled with predictive capabilities, empowers defenders to safeguard their digital assets with unprecedented efficiency.
By embracing AI as a powerful ally, we can confidently navigate the complex and dynamic world of cybersecurity, knowing that our defenses are fortified by cutting-edge technology and human ingenuity.
However, a balanced approach that combines AI’s strengths with human expertise and ethical considerations is crucial for realizing its full potential and ensuring a secure digital future.
By leveraging AI’s intelligence and augmenting it with human judgment, we can stay one step ahead in the ongoing battle against cyber threats, fortifying the digital frontier for the benefit of individuals, organizations, and society.
In this post, I will show you why Bingo Philippines stays a community favorite.
Interest in Bingo Philippines often points to more than a classic number-matching game. In many towns and cities, bingo fits into the same spaces where people naturally gather: barangay events, school programs, church socials, neighborhood celebrations, family reunions, and community fundraisers. A short learning curve helps first-time players join quickly, while rotating bingo patterns in the Philippines keeps each round from feeling repetitive. With digital entertainment growing, online bingo Philippines searches also reflect a shift toward screen-based play that can happen beyond a physical venue.
A closer look at culture, social interaction, and format differences helps explain the staying power of bingo—both in community halls and on mobile devices.
Quick Overview: What Keeps Bingo Philippines Popular?
Bingo Philippines draws players through easy gameplay, social connection, and its natural role in local gatherings. In-person bingo supports event programming and fundraising, while online versions provide an alternative option for people who prefer playing through phones or computers. Differences in rules, card layouts, and win validation vary by organizer and platform, so checking game conditions stays essential.
Bingo and Filipino Community Traditions
Community life in the Philippines often includes organized activities designed for broad participation. Bingo works well in that setting because the setup stays straightforward: cards, a caller, and an announced winning pattern. Minimal preparation helps the game slide easily into time-limited programs, whether the event involves a small neighborhood group or a large local celebration.
Fiestas offer a clear example of shared traditions built around participation. The National Commission for Culture and the Arts (NCCA) describes fiestas as significant community traditions tied to collective celebration and local involvement. A bingo segment can match that community rhythm by giving participants something familiar and easy to follow.
Simple Mechanics With Multigenerational Appeal
Bingo relies on a clear objective: match the called numbers to those printed on the card, then complete the required pattern. That clarity allows multiple generations to play in the same space with minimal instruction. A brief introduction to the calling system and the winning condition can be enough for beginners to participate confidently.
Format changes can add learning steps. Some organizers use different number ranges, card designs, or special winning patterns. Digital formats may introduce electronic number boards, auto-marking options, and platform-based win verification. Players used to paper cards may need time to understand how numbers appear on-screen, how digital marking works, and how claims get confirmed. That mix—familiar rules with flexible formats—helps bingo stay accessible without feeling stuck in one style.
Bingo Patterns Philippines: Variety That Shapes Each Round
Search interest around bingo patterns Philippines highlights one of the most important details for new players: the pattern determines what counts as a win. While number matching stays constant, the target formation changes the way a player watches the card.
Common bingo patterns include:
Horizontal line (complete one full row)
Vertical line (complete one full column)
Diagonal line (complete a diagonal path)
Four corners (mark all four corners)
Full house/coverall (complete all required numbers)
Letter or shape patterns (finish a specified design)
A four-corner round pushes attention to the edges, while a horizontal-line round puts pressure on finishing a single row quickly. Shape or letter patterns can create longer, more suspenseful rounds due to scattered required spaces.
Social Play: Why Bingo Feels Like an Event
Bingo can function like structured social time. Players listen, mark cards, and react in real time when someone nears completion. Conversations often happen naturally: beginners ask questions, experienced players explain steps, and families compare cards or double-check markings. That shared energy can make bingo feel different from solo entertainment activities.
Motivations also vary widely. Some participants value the social atmosphere, some enjoy the simplicity, and others focus on prizes or fundraising goals. A single bingo session can accommodate all of these interests, which helps explain its broad community fit.
Online Bingo Philippines: Digital Convenience With Extra Checks
Digital entertainment has expanded how bingo gets accessed. Many people searching online bingo Philippines appear to want play options that do not require travel or attendance at a scheduled community event. Depending on the provider, online bingo platforms may include digital cards, automated number displays, electronic marking tools, and various participation modes.
Online access also introduces checkpoints more common in regulated digital environments. Before joining an online game, players typically review:
platform legitimacy and authorization through official regulatory sources
rules, patterns, number ranges, and win conditions
registration steps, identity checks, and eligibility restrictions
payment, withdrawal, and transaction terms
account security features and customer support channels
responsible gaming tools such as limits, time controls, and self-exclusion options
PAGCOR’s regulatory scope includes traditional bingo, electronic bingo, and online gaming operations, with licensing and approval requirements referenced in official materials. Platform verification becomes a practical step rather than an optional extra. Online availability also should not be confused with guaranteed quality or winning chances.
Traditional vs Online Bingo: Choosing by Preference
Both formats rely on the same foundation, but experiences differ due to environment:
Traditional Bingo Philippines: physical venue, direct social interaction, manual marking, event-based schedule
Preference often depends on social goals, accessibility, and comfort with technology. Online bingo platforms may also differ from one another in interface design, card systems, and winning conditions, making rule review important each time.
Responsible Participation and Practical Limits
Prize-based or wager-based bingo benefits from clear boundaries. PAGCOR responsible gaming guidance commonly emphasizes avoiding gambling as an income source and recognizing warning signs such as chasing losses or spending more than intended. Practical habits often include setting a budget, limiting session time, avoiding borrowed funds, and taking breaks when play feels stressful.
PAGCOR materials also reference age-related restrictions in covered gaming establishments and online gaming platforms, including limits affecting those under 21, with additional restrictions potentially applying depending on the platform and activity.
FAQ
Why is bingo popular in the Philippines? Community-friendly gameplay, easy-to-learn rules, social interaction, and changing bingo patterns.
What bingo patterns are common in the Philippines? Horizontal, vertical, diagonal, four corners, full house/coverall, and letter or shape patterns.
What should beginners check before playing online bingo in the Philippines? Authorization status, rules and patterns, eligibility requirements, payment policies, security features, and responsible gaming controls.
In this post, I will show you what to do in the first 24 hours for a hacked WordPress site.
It usually starts with a message. A customer says your site redirected them somewhere strange. Google shows “This site may be hacked” under your listing. Your host emails to say your account is sending spam.
The urge is to start deleting files right away. Don’t. Cleaning before you’ve contained the problem is how sites get reinfected a week later. Panic also destroys the evidence you need to find out how the attacker got in.
I’ve built WordPress websites since 2005 and worked in SEO for more than 18 years. Over that time I’ve cleaned up enough hacked WordPress sites to know that the order matters more than the tools. Here’s the order.
First, confirm it’s really a hack
Not every strange problem is a hack. An expired domain, a broken plugin update or a full disk can look alarming too. These signs point to a real compromise:
Sign
What it often means
First check
Google shows “This site may be hacked” or a red warning page
Google found spam pages, malware or phishing on the site
Search Console, Security issues report
Visitors are redirected to other sites, often only on mobile or from Google
Injected redirect code in files or the database
.htaccess, wp-config.php and theme files
Pages you didn’t create appear in Google
Spam pages added by the attacker
site:yourdomain.com search
Admin users you don’t recognize
The attacker created a way back in
Users screen in WordPress
Your host reports spam email or suspends the account
The site is being used to send spam
Host notice and server logs
Unfamiliar files, especially PHP files in uploads
A backdoor or web shell was installed
File manager or SFTP
Table 1: Common signs of a hacked WordPress site.
A quick test: search Google for site:yourdomain.com and scroll through the results. Pages you didn’t create, especially in another language or about pills, replica goods or casinos, mean someone else is publishing on your site.
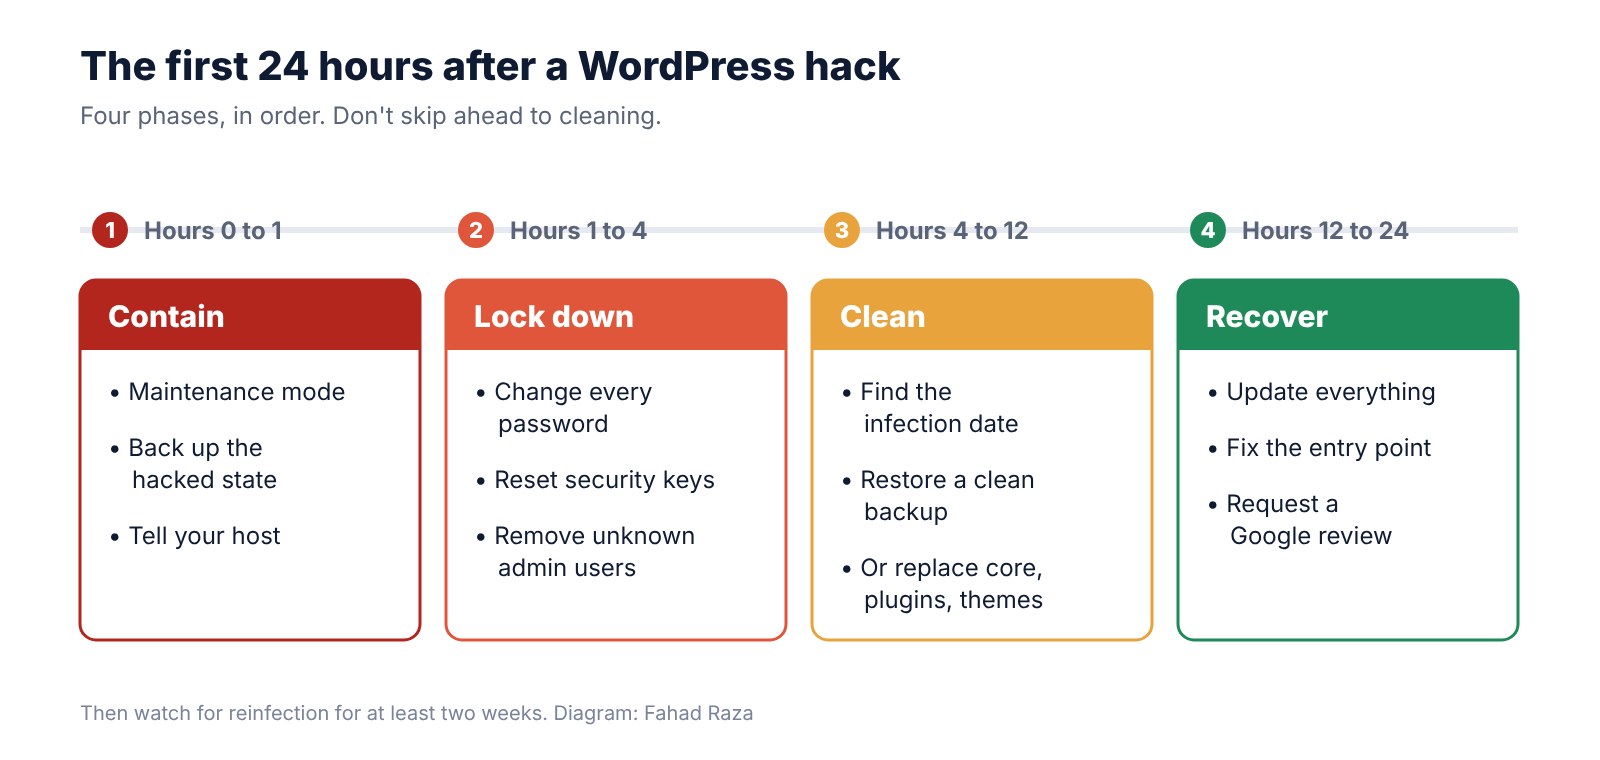
Figure 1: The four phases of the first 24 hours.
Hours 0 to 1: Contain the damage
The goal in the first hour is to stop the harm spreading to your visitors, and to keep a record of what happened.
Take the site offline for visitors
Put the site into maintenance mode, or ask your host to restrict access to your own IP address while you work. A hacked site can redirect visitors to scams or download malware onto their devices. Protecting them comes first.
Back up the hacked site
Take a full copy of the files and the database before you change anything. It sounds backward, but it’s important. That copy shows when files were modified and what was injected, and it’s what you’ll study to find the way in.
Tell your host
Most hosts have seen this before. They can check server logs, tell you whether other sites on your account are affected, and sometimes clean the infection for you. If your host has already suspended the account, they’ll explain what they need to restore it.
Hours 1 to 4: Lock down every way in
Assume the attacker has a password, a hidden admin account or both. Close every door before you clean, or they’ll walk straight back in.
Change every password. That means your hosting account, SFTP or FTP, the database, every WordPress administrator and the email account tied to the site. Use a password manager and make each one unique.
Reset the WordPress security keys. The keys and salts in wp-config.php sign everyone’s login cookies. Replacing them with fresh values from the official WordPress generator logs out every session, including the attacker’s.
Check the user list. Go to Users and look for administrators you don’t recognize. Note the usernames and creation dates before you delete them, because they help date the attack.
Turn on two-factor authentication for every admin account, if it isn’t on already.
Hours 4 to 12: Clean the site
This is the longest phase. There are two ways to do it, and the right one depends on your backups.
Option 1: Restore a clean backup
If you have a backup from before the infection, restoring it is usually the fastest and safest path. The hard part is knowing which backup is clean. Use the hacked copy you took earlier to find the oldest modified or injected file, then restore a backup from before that date.
One warning: a restore brings back whatever let the attacker in. If an outdated plugin caused the hack, the restored site has the same hole. That’s why the next phase matters.
Option 2: Clean in place
Without a clean backup, you rebuild the site from trusted parts. When a small business calls me as a Sydney WordPress developer after a hack, this is the route we usually end up on, because the backups either don’t exist or were taken after the infection.
Replace what you can
Delete and reinstall WordPress core, every plugin and every theme from their official sources. Don’t trust the existing copies, even if they look normal. If you have WP-CLI access, these commands compare your files against the official versions:
wp core verify-checksums
wp plugin verify-checksums –all
Check the places attackers hide
PHP files inside wp-content/uploads. That folder should hold images and documents, not code.
The .htaccess and wp-config.php files, for injected redirects or code.
The database, for script tags inside posts, widgets and the site URL settings.
Scheduled tasks, both WordPress cron events and the server’s own cron jobs.
A security scanner such as Wordfence, Sucuri or MalCare helps here. Treat its report as a starting point, though, not proof the site is clean.
Hours 12 to 24: Recover and close the hole
Find the entry point
Cleaning without knowing how they got in is guesswork. The usual causes are an outdated or abandoned plugin, a “nulled” premium plugin downloaded from an unofficial site, a reused password, or another compromised site on the same hosting account. Your server access logs, read alongside the dates from your hacked backup, often point straight to it.
Update and remove
Update WordPress, every plugin and every theme. Delete anything you don’t use, including inactive themes. Replace any plugin that hasn’t been updated in a year or more.
Ask Google to lift the warning
Open Google Search Console and check the Security issues report. Once the site is clean, request a review there. Reviews can take from a day to a few weeks. Spam pages the attacker created should return a 404 or 410 status, so Google drops them from its index over time.
Check whether customer data was exposed
If the site stored customer details, such as form entries, accounts or orders, work out whether they were accessed. Breach notification rules vary by location. Under the EU’s GDPR, for example, certain breaches must be reported to the regulator within 72 hours. If personal data may be involved, get proper advice quickly.
Five mistakes that make a hack worse
Most of the long, painful cleanups I’ve seen came from one of these.
Restoring the latest backup without checking its date. If the infection is three weeks old, last night’s backup is infected too.
Deleting the hacked files before copying them. You lose the trail that shows how the attacker got in, so you can’t close the hole.
Changing only the WordPress password. Attackers often come back through hosting, SFTP or database access, which a WordPress password change doesn’t touch.
Trusting one scanner’s “all clear”. Scanners miss custom backdoors. Check the uploads folder, the user list and the database yourself.
Reinstalling the same nulled plugin. Pirated premium plugins are one of the most common ways malware gets onto WordPress sites. Buy the license or replace the plugin.
The next two weeks
A cleaned site isn’t finished on day one. Reinfection usually comes from a backdoor that was missed. For at least two weeks:
Run a security scan every day.
Check the user list and the uploads folder for anything new.
Watch Search Console for new spam pages or security alerts.
Keep daily backups going, and store copies away from the hosting account.
How to stop it happening again
Prevention is mostly routine. These five habits close most of the doors attackers use on small business sites:
Update WordPress, plugins and themes at least weekly, and remove anything you don’t use.
Give every person their own login, with a unique password and two-factor authentication.
Keep daily backups stored away from your hosting account, and test a restore once a quarter.
Use a firewall, either from your host, a security plugin or a service such as Cloudflare.
Buy premium plugins and themes only from their official sources.
My take
Most hacked WordPress sites I see weren’t targeted. They were found. Automated tools scan the web for known plugin flaws, weak passwords and forgotten admin pages, and a small business site is as likely to be hit as a big one.
The good news is that the fix is routine work: updates, unique passwords, two-factor login and backups you’ve actually tested. None of it is glamorous. All of it is cheaper than spending the first 24 hours after a hack working through this list.
In ths post, I will show you why employee ID badges still matter in a zero trust world.
Cybersecurity strategies have evolved dramatically over the past decade. Organizations now invest heavily in multifactor authentication, endpoint protection, cloud security, identity governance, and Zero Trust architectures. Yet while businesses strengthen their digital defenses, one fundamental aspect of organizational security often receives less attention: physical employee identification.
Even the most sophisticated cybersecurity infrastructure cannot fully protect an organization if unauthorized individuals can freely enter restricted areas, access unattended workstations, or move through sensitive facilities without being challenged.
This creates an important connection between cybersecurity and physical security. Organizations must understand not only who can access their digital systems but also who is physically present in their workplaces.
Employee identification badges, when combined with appropriate access controls and security policies, remain a practical component of a comprehensive security strategy.
Why Physical Identity Still Matters in a Digital Security Environment
Modern organizations increasingly operate through cloud applications, remote connections, and distributed workforces. As a result, security discussions often focus on protecting digital identities rather than managing physical access.
However, offices, data centers, warehouses, healthcare facilities, and other workplaces still contain valuable assets that require protection.
An unauthorized individual entering a restricted area may gain access to network equipment, confidential documents, company devices, or unattended computer systems.
These risks cannot be addressed exclusively through firewalls or endpoint security software.
Physical security policies help establish boundaries around facilities and sensitive areas, while employee identification procedures make it easier to distinguish authorized personnel from visitors.
A consistent identification system also supports employee accountability and helps security personnel recognize individuals who may require additional verification.
The objective is not to replace digital security controls but to extend organizational security practices into the physical workplace.
Employee ID Badges as a First Layer of Physical Identification
Employee identification badges provide a visible way to associate individuals with an organization.
A typical badge includes an employee’s photograph, name, job title, and company branding. Some organizations also include department identifiers or other information relevant to workplace operations.
When employees consistently display identification, colleagues and security personnel can more easily recognize authorized staff members.
This becomes particularly valuable in larger organizations where employees may not personally know everyone working in the building.
Businesses can use standardized ID badges to establish consistent visual identification across departments, facilities, and employee groups.
For example, an organization might use different badge designs to distinguish permanent employees, contractors, and visitors.
These visual distinctions can support security awareness and make it easier for staff to identify individuals who may need assistance or verification.
However, an important distinction must be maintained: a visible badge is not proof that the person carrying it currently has authorization to enter a restricted area.
Badges can be lost, stolen, duplicated, or retained after employment ends.
For that reason, visual identification should be treated as one security layer rather than a standalone access control mechanism.
How Employee Identification Fits Into Zero Trust Security
Zero Trust has become an influential approach to cybersecurity because it challenges the assumption that users or devices should automatically be trusted based on their location within a network.
Instead, access decisions should be based on appropriate verification, authorization, and contextual security controls.
Although Zero Trust architectures primarily address access to digital resources, their underlying principles can inform physical security practices as well.
For example, an employee who is authorized to enter a corporate office should not automatically receive access to every server room, storage facility, or restricted department.
Physical access permissions should reflect legitimate business requirements.
An identification badge may help establish who an individual claims to be, while an electronic access control system determines whether the associated credential is authorized for a particular location.
Additional verification may be appropriate for highly sensitive facilities.
Organizations should also review access permissions when employees change roles or leave the company.
This approach reinforces the broader principle of granting access according to operational necessity rather than assuming that all employees require identical privileges.
Importantly, implementing employee badges does not itself establish Zero Trust compliance. Badges are supporting tools within a much larger security framework.
RFID, NFC, and Traditional Photo Badges: Understanding the Differences
Not all employee identification cards provide the same capabilities.
Selecting the appropriate technology requires understanding how different badge types operate and what security functions they can support.
Traditional photo ID badges
Standard photo badges are primarily designed for visual identification.
They typically display an employee’s name, photograph, title, and organization.
These credentials are useful for workplace recognition, visitor differentiation, and maintaining consistent professional identification.
However, they do not inherently provide electronic authentication or access control.
RFID and proximity cards
Radio-frequency identification technology allows compatible readers to communicate with electronic credentials without requiring physical contact.
Certain RFID and proximity cards are commonly used with building access control systems.
Depending on the technology, these systems can associate a credential with specific doors, access schedules, or facility permissions.
However, RFID is a broad category that includes technologies with substantially different security characteristics.
Some older proximity systems rely on relatively weak credential identification methods and may be vulnerable to cloning or unauthorized duplication.
Organizations should evaluate the security capabilities of their specific card technology and reader infrastructure rather than assuming all RFID credentials provide equivalent protection.
NFC-enabled cards
Near Field Communication is a short-range contactless technology used in applications such as mobile interactions, information exchange, and certain credential systems.
NFC-enabled cards may support different functions depending on the chip, software, and compatible reader.
Some NFC implementations are suitable for secure applications, while simple NFC tags may only store publicly readable information.
Therefore, NFC capability alone should not be interpreted as evidence that a card provides secure authentication.
Businesses should select credential technologies based on documented compatibility, security requirements, and the capabilities of their existing infrastructure.
The Security Risks of Lost, Stolen, and Unreturned Badges
One of the most common weaknesses in physical credential management is the failure to promptly address lost or unreturned identification cards.
An employee may misplace a badge during travel, leave it in a public location, or forget to return it after leaving the organization.
If the badge is connected to an electronic access system and remains active, it may present an unnecessary security risk.
Organizations should establish clear procedures requiring employees to report missing credentials promptly.
For electronically enabled badges, administrators should be able to revoke or suspend associated access permissions through the appropriate access control platform.
Replacement badges should be issued only after verifying the employee’s identity and following established administrative procedures.
Employers should also discourage employees from lending identification cards to colleagues or allowing unauthorized individuals to use their credentials.
Regular reviews of active access credentials can help identify outdated assignments and reduce the number of unnecessary permissions.
Physical badges without electronic access capabilities should also be managed carefully because they may be used to impersonate employees or create a misleading appearance of authorization.
Why Employee Offboarding Is a Critical Security Process
Employee onboarding receives considerable attention from HR and IT departments, but offboarding is equally important from a security perspective.
When an employee leaves an organization, administrators typically need to disable system accounts, revoke application permissions, recover company equipment, and update relevant records.
Physical identification credentials should be included in this process.
A departing employee may still possess a badge displaying the company’s name and logo, even after digital accounts have been disabled.
If the badge also functions as an electronic access credential, failure to deactivate it could leave physical access permissions active.
This creates an avoidable gap between digital identity management and facility security.
A coordinated offboarding checklist should address both physical and digital credentials.
Human resources, IT, and security personnel should have clearly assigned responsibilities so that access changes occur promptly and consistently.
For example, an employee departure notification can trigger separate tasks for disabling digital accounts, revoking building access, and collecting identification cards.
Organizations should also document exceptions, such as situations where a former employee retains limited authorized access for a defined business purpose.
The objective is to ensure that access permissions reflect current employment status and legitimate operational requirements.
Centralized Badge Management and Identity Lifecycle Security
As businesses expand, managing employee identification across multiple offices can become increasingly complex.
Different departments may use inconsistent badge templates, maintain separate employee records, or follow different procedures for issuing replacements.
These inconsistencies can create administrative inefficiencies and make it harder to maintain reliable identification standards.
Online badge design and management tools can support consistent employee photographs, names, titles, and organizational branding without requiring each location to maintain separate design processes.
For example, a company operating ten regional offices may establish approved identification templates while allowing authorized administrators to prepare badges for employees at their respective locations.
Centralized physical badge management can also support consistent procedures for new hires, departmental transfers, and replacement requests.
However, organizations should distinguish between badge production systems and enterprise access control platforms.
A system used to design and order identification cards does not automatically manage electronic door permissions, digital identities, or security authentication.
Where these capabilities exist in separate systems, organizations should establish clear processes to keep employee information and credential status appropriately coordinated.
The Human Factor: Building a Security-Conscious Workplace
Technology alone cannot prevent every physical security incident.
Employees play an important role in maintaining secure workplaces by following identification policies, reporting suspicious activity, and respecting access restrictions.
For example, an employee may hold a secure door open for an unfamiliar individual out of courtesy, unintentionally allowing that person to bypass access controls.
This behavior, commonly associated with tailgating or unauthorized entry, illustrates why physical security awareness matters.
Organizations should train employees to recognize identification requirements and follow established procedures when encountering unfamiliar individuals.
However, security policies should avoid encouraging confrontational behavior.
Employees should know when to contact reception, facility security, or designated supervisors rather than attempting to personally investigate potentially unsafe situations.
Clear visitor identification, consistent badge use, and well-communicated access procedures can help make security expectations easier to understand.
The goal is to establish a workplace culture in which physical security becomes a routine operational responsibility rather than an occasional concern.
Building a Practical Employee Identification Security Policy
Organizations seeking to strengthen physical identification procedures should begin with a clear written policy.
This policy should define who receives identification credentials, what information appears on badges, and how cards are issued or replaced.
It should also establish procedures for temporary employees, contractors, visitors, and individuals working across multiple locations.
Where electronic access credentials are used, organizations should document how permissions are assigned, reviewed, and revoked.
Regular audits can help identify active credentials that no longer correspond to authorized personnel.
Businesses should also evaluate the information displayed on employee badges.
Names, photographs, and professional roles are often sufficient for visual identification. Unnecessary personal information, sensitive employee identifiers, or confidential internal details should generally be excluded.
Finally, organizations should ensure that badge management procedures remain practical for employees and administrators.
Security controls that are unnecessarily complicated may encourage workarounds, while clear and consistent processes are more likely to be followed.
Conclusion: Physical Identification Remains Relevant in Modern Cybersecurity
As cybersecurity continues to evolve, organizations must avoid overlooking the relationship between digital and physical security.
Cloud protection, multifactor authentication, and Zero Trust architectures are essential components of modern security strategies, but they do not eliminate the need to manage physical access and employee identification.
Well-designed identification badges help organizations distinguish employees from visitors, maintain consistent workplace standards, and support broader security procedures.
When combined with appropriate electronic access controls, employee training, and coordinated onboarding and offboarding processes, they contribute to a more comprehensive approach to organizational protection.
For businesses managing distributed workforces, multiple facilities, and changing employee populations, standardized badge management also offers practical administrative benefits.
Ultimately, effective security depends on more than protecting digital accounts. It requires understanding who has access to organizational resources, whether those resources exist in the cloud, on a corporate network, or behind a physical door.
In this post, I will talk about Fake ID Maker as the key to online identity verification.
In today’s digital age, the concept of identity verification has become increasingly important. With the rise of online transactions and interactions, ensuring that individuals are who they claim to be is crucial.
Enter fake ID makers, tools that have gained fame for their ability to create fake IDs. While often associated with illegal activities, these tools also show the need for strong identity checks.
The primary purpose of identity verification is to protect both individuals and organizations from fraud and identity theft. As more personal and financial transactions move online, the risk of unauthorized access and misuse of personal information grows. This makes secure identity verification a key component of digital security.
Keywords such as fake ID maker, fake ID generator, and fake ID creator often appear in discussions about these tools, reflecting their relevance in the ongoing conversation about online security.
Understanding Fake ID Makers and Their Uses
Fake ID makers are tools or software designed to produce counterfeit identification documents. These can range from simple driver’s licenses to more complex forms of identification, such as passports.
How these tools work is different, but they generally involve changing images and text to create a believable copy of a legitimate ID.
Fake IDs have a variety of applications, both legal and illegal:
Legal Uses: In some cases, fake IDs are used for harmless pranks or as props in movies and theater productions. They may also be used in educational settings for teaching purposes.
Illegal Uses: More commonly, fake IDs are associated with illegal activities such as underage drinking, identity theft, and fraud. These uses pose significant legal risks and ethical concerns.
To understand the context of identification documents, it is helpful to consider thehistorical development of national ID cards. These documents have evolved over time to meet the changing needs of society, highlighting the ongoing challenge of balancing security with privacy.
Legal Risks and Ethical Implications of Using Fake IDs
Using fake IDs can lead to serious legal consequences. While a fake ID might look appealing, it’s crucial to understand the potential repercussions. Here are some key legal risks associated with fake IDs:
Fines and Penalties: Possessing or using a fake ID can result in hefty fines. In many jurisdictions, this is considered a criminal offense.
Criminal Record: Being caught with a fake ID can lead to a lasting criminal record, hurting future job and school chances.
Legal Actions: Depending on the severity, individuals may face legal actions such as probation or even jail time.
Beyond the legal risks, there are ethical and social implications to consider:
Trust Issues: Using a fake ID erodes trust in systems designed to protect individuals and institutions.
Social Impact: It contributes to a culture of deceit, which can have broader societal implications.
The use of fake IDs, whether for purchasing alcohol or accessing restricted areas, has big risks and challenges. It’s important to weigh these against the perceived benefits of a fake license maker or other fake ID online solutions.
The creation of fake IDs involves advanced tools and methods. These can range from simple software applications to advanced printing technologies. Here’s a closer look at how fake IDs are made:
Software Tools: Fake ID makers often use graphic design software to replicate official documents.
Printing Technology: High-quality printers can produce IDs that look like real ones.
Material Use: The use of similar materials to those used in real IDs makes them seem real.
Despite these technologies, fake ID creators face significant challenges due to modern security measures. Many identification documents now include advanced security features such as holograms, barcodes, and embedded chips, making them difficult to replicate accurately.
For instance, the Next Generation Identification (NGI) system illustrates how modern security measures are evolving to combat identity fraud. These advancements in biometrics and other technologies make it increasingly challenging for fake ID generators to succeed.
Alternatives to Fake IDs for Online Verification
In the digital age, verifying one’s identity online is crucial. While the urge to use a fake ID maker can be strong, there are legitimate and safer alternatives available. These methods not only ensure compliance with legal standards but also give better security and trust.
Digital Identity Verification Services: Companies like Jumio and Onfido provide services that use biometric data and AI to verify identities. These services are widely accepted and recognized for their accuracy.
Two-Factor Authentication (2FA): This method adds an extra layer of security by requiring two forms of verification, such as a password and a mobile confirmation code.
Government-Issued Digital IDs: Some countries offer digital versions of official IDs, which can be used for online verification.
Blockchain Technology: Blockchain offers a decentralized and secure way to check identity, ensuring data integrity and security.
Choosing these legitimate methods over a fake drivers license maker or fake ID online offers several benefits:
Compliance with legal standards, avoiding potential fines or legal issues.
Increased trust and credibility when interacting with online platforms.
Enhanced security features that protect personal information from fraud.
For organizational contexts, legitimate photo ID credentials fromID Experts, IdenTrust, or Valid ID can serve as proper identification alternatives.
The use of fake IDs, whether through a fake ID generator or a fake license maker, has big risks. From legal consequences to moral problems, the risks are bigger than any benefits.
It’s essential to focus on legal and right ways in identity verification. By opting for legitimate methods, individuals not only protect themselves but also help make online spaces safer.
As technology continues to evolve, keeping up with new changes in identity verification is crucial. This knowledge empowers individuals to make informed decisions and adapt to new challenges in the digital landscape.
In this post, I will show you the home and building safety documentation for Bosch, Kidde and Notifier Systems.
A smoke alarm in the hallway chirps once a minute. A fire panel in an office building shows a trouble message that nobody on the night shift recognizes. In both cases the tempting move is to press a button until the noise stops. That clears the symptom, not the cause, and it can leave a building without protection.
Good home and building safety documentation tells you what each signal means on your exact device and who is allowed to act on it. Here is how to organize it for Kidde alarms, Bosch equipment and NOTIFIER fire alarm systems.
Start home and building safety documentation with the label
A brand name does not identify a manual. Read the label on each device and panel and record:
the model number;
the serial number;
the manufacture date, which matters for replacement;
firmware or hardware revision, where shown.
On a connected system, the panel’s approved configuration is part of the documentation too. A detector swapped for a “similar” model may not be listed as compatible.
Which document covers which task
Document
Who uses it
What it covers
User or occupant guide
Residents, building staff
Signals, testing, silencing, battery
Installation manual
Installers
Mounting, wiring, placement
Programming or service manual
Qualified technicians
Panel configuration, diagnostics
Compatibility list
Designers, technicians
Which devices work with which panel
An occupant guide never replaces installation or programming instructions.
Check Kidde alarms by model and date
Kidde makes residential smoke, carbon monoxide and combination alarms. Power arrangements differ: some run on replaceable batteries, some on a sealed 10-year battery, others are hardwired with battery backup. So do indicator patterns and end-of-life signals. Find the guide that matches the model on the back of the alarm in thekidde manuals directory.
Test and replacement
The US National Fire Protection Association recommends testing smoke alarms monthly and replacing them 10 years after the date of manufacture. Carbon monoxide alarms have their own replacement period, set by the manufacturer, so check the date and the guide rather than assuming the same figure.
Use the test button as the guide describes. It confirms that the alarm sounds. It does not prove the sensor responds to real smoke or gas.
Chirps and lights
A chirp can mean a low battery, a fault or the end of the alarm’s life, depending on the model and pattern. Look it up before acting:
A low-battery chirp: replace the battery only if the guide allows it, then test.
An end-of-life signal: replace the alarm, because resetting it or fitting a new battery is not a fix.
A fault signal: follow the guide, and replace the unit if the signal returns.
Match Bosch documents to the equipment and task
Bosch’s range includes detectors, fire alarm control panels and intrusion systems. A detector and the unit it reports to usually need separate documents. Use thebosch manuals directory as a starting point, then confirm it lists your model and revision.
Programming instructions are for trained installers. A building manager needs the operating guide for the panel: what each indicator means, how to acknowledge and silence alarms, and which actions are reserved for the service company.
Keep NOTIFIER panel and device records together
NOTIFIER is a Honeywell brand of commercial fire alarm systems. On an addressable panel, each detector, call point and module has its own address, so a message on the display points to a specific device. That only helps if the register says where each one is.
Thenotifier manuals directory can help you find the panel’s operating manual and the documents for its field devices. Programming and service belong to qualified technicians.
Three types of signal
Fire alarm codes and panel manuals separate signals by what they mean:
Signal
What it usually means
First response
Alarm
Possible fire
Follow the emergency plan; evacuate
Supervisory
Fire-protection equipment off normal, such as a closed sprinkler valve
Investigate the named equipment; notify the responsible person
Trouble
A fault in the system itself, such as a wiring or communication fault
Record the message; call qualified service
The installed panel’s manual has the final word. A color or beep pattern is not a diagnosis across brands.
Respond to alarms before thinking about a reset
When a fire alarm sounds, follow the emergency plan and leave. If a carbon monoxide alarm sounds, get everyone into fresh air, call the emergency services and wait until responders say the building is safe. Do not stay inside to find the cause.
For a confirmed non-emergency signal, write down the message, the time and the device address or location first. Then follow the permitted checks in the manual. Silencing, disconnecting or bypassing a device is not an investigation.
When protection is impaired
A fault that leaves part of a building unprotected needs immediate escalation under the site’s impairment procedure. The responsible person decides on notifications and temporary measures, such as a fire watch, according to local requirements. Keep the fault open in the log until the technician has recorded the repair.
Build the testing schedule and the register
Test intervals come from several sources at once: the manufacturer’s instructions, the fire code that applies, the authority having jurisdiction and the site’s own procedures. In the UK, for example, BS 5839-1 calls for a weekly user test of the fire alarm and servicing by a competent person at intervals of no more than six months.
Tests can send signals to a monitoring center or trigger door releases and other outputs. Notify the monitoring company before a test and confirm afterwards that the system is back to normal.
What the register should hold
Record
Details
Identity
Manufacturer, model, serial number, revision
Location
Room or zone, panel and device address
Installation
Dates, installer, manuals used
Configuration
Approved settings and every change, with date and name
Testing and service
Results, defects, corrective action, follow-up
Contacts
Service company, monitoring center, escalation
Update the register after each replacement or service visit, keeping the old and new identifiers. A failed test needs an owner and a date for the return visit, not just the word “failed.”
In this post, we will compare mobile vs residential vs datacenter proxies to answer the question – which one do you need?
A proxy stands between you and the website you visit. The site sees the proxy’s IP address, not yours. That simple idea covers three quite different products, and choosing the wrong one costs either money or results. Datacenter proxies are cheap and fast but easy to spot. Residential proxies look like home users. Mobile proxies look like phones on a carrier network and are the hardest to block. This article explains how each type works, what it is good for, and how to choose.
Why the type of IP address matters
Every IP address belongs to a network, and that ownership is public. Websites and anti-fraud systems look up who owns the address of each visitor. An address owned by a hosting company tells them the visitor is probably a server or a script.
An address owned by a home internet provider or a mobile carrier suggests an ordinary person. Many sites apply stricter limits, more CAPTCHAs or outright blocks to the first group. So the origin of a proxy’s address decides how the rest of the web treats you.
Datacenter proxies
Datacenter proxies run on servers in hosting facilities. Their addresses come from cloud and hosting providers.
Strengths: they are the fastest and cheapest type, with stable connections and usually unlimited or very generous traffic. You can buy large numbers of them.
Weaknesses: they are the easiest to detect. Whole address ranges of hosting companies are flagged by many sites, so one bad neighbour can affect you. Social networks, ticketing sites, marketplaces and search engines often challenge or block them.
Good for: tasks where the target does not care who you are. Examples are monitoring your own websites, accessing public APIs, bulk downloads from tolerant sources and general privacy from a network you do not trust.
Residential proxies
Residential proxies route traffic through addresses that internet providers assign to homes. Providers usually sell them as a large rotating pool and charge by the gigabyte.
Strengths: requests look like they come from ordinary households, so they pass many checks that stop datacenter addresses. Pools cover many countries and cities, which helps with location-specific work such as checking local prices or search results.
Weaknesses: speed and stability vary, because the exit points are consumer connections. Paying per gigabyte gets expensive for heavy pages or video. And you should ask how a provider sources its addresses: a reputable one gets clear consent from the people whose connections are used.
Good for: web scraping at scale, price and ad verification across regions, SEO monitoring and other work that needs many different addresses in many places.
Mobile proxies
Mobile proxies use addresses that mobile carriers give to phones and modems on 4G and 5G networks.
Carriers do not have enough public addresses for every subscriber, so they place many users behind each one. A website that blocks a single mobile address may lock out a large number of real customers at once, and sites know this. As a result, mobile addresses get the highest level of trust of the three types.
Mobile proxies come in two forms. In a shared pool, you rotate through many addresses together with other customers. With a dedicated mobile proxy, one physical device on a carrier network is reserved for you. Providers such as IPVolt rent dedicated devices by the day or month and let you change the device’s IP on demand or on a schedule, so you get a fresh carrier address without sharing the device.
Strengths: the best acceptance on strict platforms, real carrier and location data, and with a dedicated device a stable identity that you control.
Weaknesses: the highest price per proxy, and speeds limited by the mobile network. The carrier chooses the new address on rotation and sometimes returns the same one.
Good for: managing social media and marketplace accounts, testing mobile apps and ads as a real mobile user would see them, and reaching sites that block the other two types.
A quick comparison
Cost: datacenter is lowest, residential is in the middle and billed by traffic, mobile is highest.
Speed: datacenter is fastest, residential varies, mobile depends on the carrier signal.
Detection risk: datacenter is high, residential is low, mobile is lowest.
Best use: datacenter for volume on tolerant sites, residential for wide geographic coverage, mobile for strict platforms and long-lived accounts.
How to choose
Start with the target, not the proxy. If the site you work with does not block hosting addresses, a datacenter proxy does the job for the least money. If you need thousands of addresses across many countries for data collection, residential pools fit best. If you run accounts that must look like one consistent phone user, or the site rejects everything else, use a mobile proxy and keep one proxy per account.
Whatever you pick, check a few things before paying: which protocols are supported (HTTP and SOCKS5 cover almost everything), how rotation works, whether you can test for a short period, and what the provider’s rules on acceptable use are. Setup guides, such as the ones at https://ipvolt.com/guides, show how to connect a proxy to browsers, scripts and automation tools.
Stay away from free proxy lists. Nobody runs a server for nothing: free proxies are often slow, short-lived and able to read or change unencrypted traffic.
Final thoughts
There is no single best proxy type. Datacenter proxies win on price and speed, residential proxies on reach, and mobile proxies on trust.
Match the type to how strict your target is and how much a block would cost you, and you will avoid both overpaying and getting stopped at the door.