Home Blog Page 2

Hacked WordPress Site? What to Do in the First 24 Hours

0
Hacked WordPress Site? What to Do in the First 24 Hours
Feature image: Fahad Raza.

In this post, I will show you what to do in the first 24 hours for a hacked WordPress site.

It usually starts with a message. A customer says your site redirected them somewhere strange. Google shows “This site may be hacked” under your listing. Your host emails to say your account is sending spam.

The urge is to start deleting files right away. Don’t. Cleaning before you’ve contained the problem is how sites get reinfected a week later. Panic also destroys the evidence you need to find out how the attacker got in.

I’ve built WordPress websites since 2005 and worked in SEO for more than 18 years. Over that time I’ve cleaned up enough hacked WordPress sites to know that the order matters more than the tools. Here’s the order.

First, confirm it’s really a hack

Not every strange problem is a hack. An expired domain, a broken plugin update or a full disk can look alarming too. These signs point to a real compromise:

SignWhat it often meansFirst check
Google shows “This site may be hacked” or a red warning pageGoogle found spam pages, malware or phishing on the siteSearch Console, Security issues report
Visitors are redirected to other sites, often only on mobile or from GoogleInjected redirect code in files or the database.htaccess, wp-config.php and theme files
Pages you didn’t create appear in GoogleSpam pages added by the attackersite:yourdomain.com search
Admin users you don’t recognizeThe attacker created a way back inUsers screen in WordPress
Your host reports spam email or suspends the accountThe site is being used to send spamHost notice and server logs
Unfamiliar files, especially PHP files in uploadsA backdoor or web shell was installedFile manager or SFTP

Table 1: Common signs of a hacked WordPress site.

A quick test: search Google for site:yourdomain.com and scroll through the results. Pages you didn’t create, especially in another language or about pills, replica goods or casinos, mean someone else is publishing on your site.
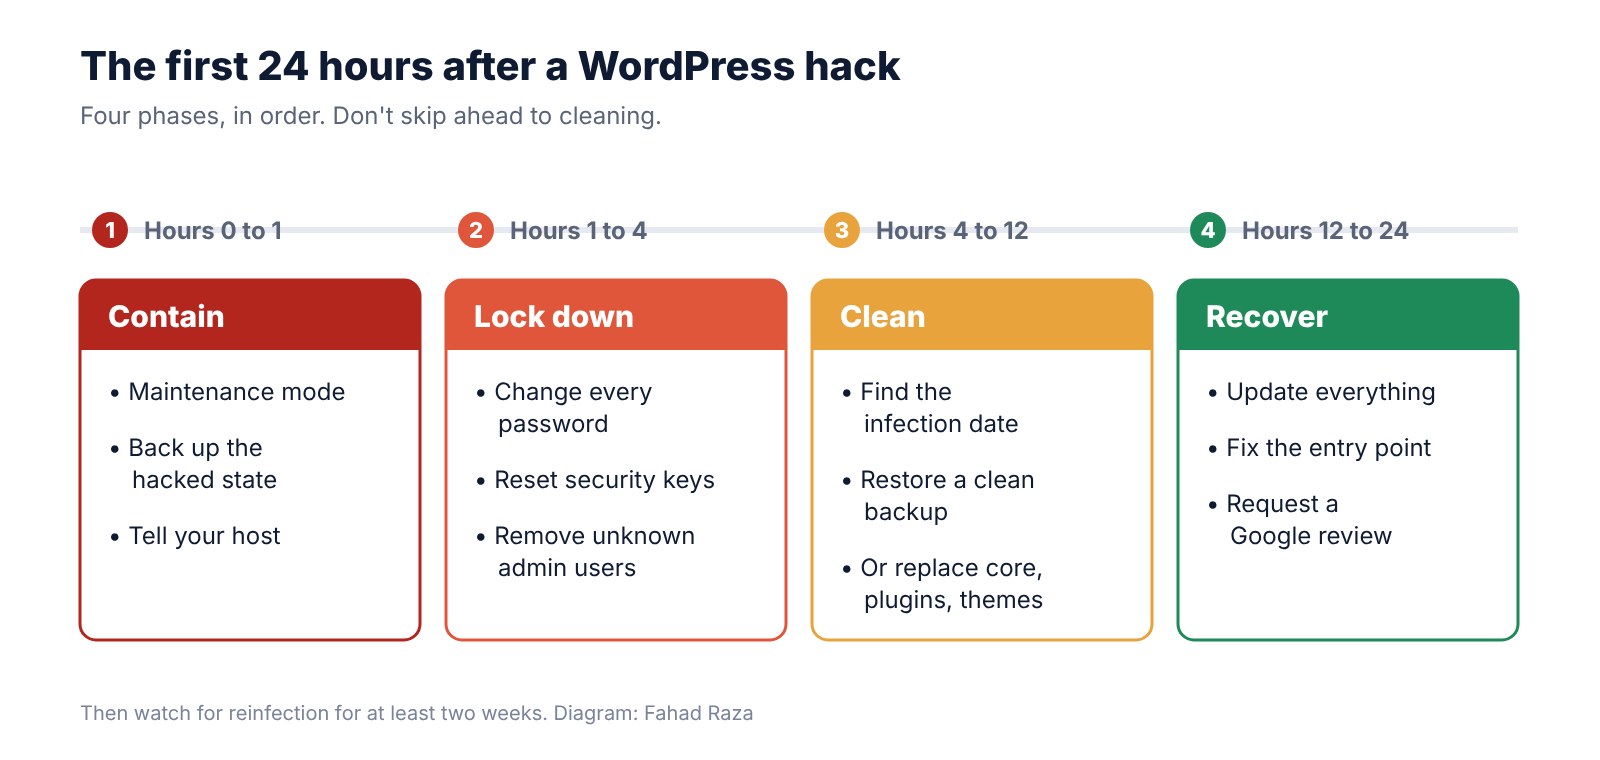
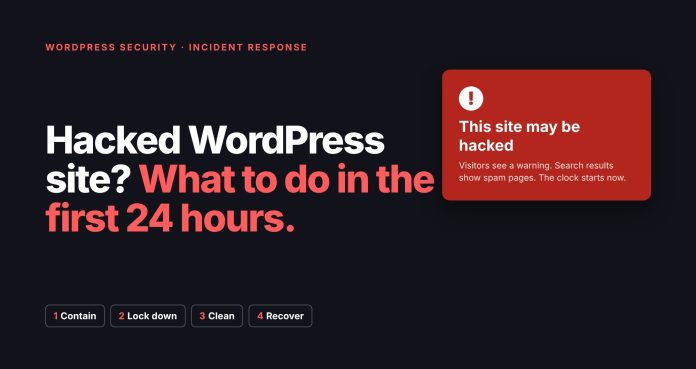
the First 24 Hours after a WordPress hack
Figure 1: The four phases of the first 24 hours.

Hours 0 to 1: Contain the damage

The goal in the first hour is to stop the harm spreading to your visitors, and to keep a record of what happened.

Take the site offline for visitors

Put the site into maintenance mode, or ask your host to restrict access to your own IP address while you work. A hacked site can redirect visitors to scams or download malware onto their devices. Protecting them comes first.

Back up the hacked site

Take a full copy of the files and the database before you change anything. It sounds backward, but it’s important. That copy shows when files were modified and what was injected, and it’s what you’ll study to find the way in.

Tell your host

Most hosts have seen this before. They can check server logs, tell you whether other sites on your account are affected, and sometimes clean the infection for you. If your host has already suspended the account, they’ll explain what they need to restore it.

Hours 1 to 4: Lock down every way in

Assume the attacker has a password, a hidden admin account or both. Close every door before you clean, or they’ll walk straight back in.

  1. Change every password. That means your hosting account, SFTP or FTP, the database, every WordPress administrator and the email account tied to the site. Use a password manager and make each one unique.
  2. Reset the WordPress security keys. The keys and salts in wp-config.php sign everyone’s login cookies. Replacing them with fresh values from the official WordPress generator logs out every session, including the attacker’s.
  3. Check the user list. Go to Users and look for administrators you don’t recognize. Note the usernames and creation dates before you delete them, because they help date the attack.
  4. Turn on two-factor authentication for every admin account, if it isn’t on already.

Hours 4 to 12: Clean the site

This is the longest phase. There are two ways to do it, and the right one depends on your backups.

Option 1: Restore a clean backup

If you have a backup from before the infection, restoring it is usually the fastest and safest path. The hard part is knowing which backup is clean. Use the hacked copy you took earlier to find the oldest modified or injected file, then restore a backup from before that date.

One warning: a restore brings back whatever let the attacker in. If an outdated plugin caused the hack, the restored site has the same hole. That’s why the next phase matters.

Option 2: Clean in place

Without a clean backup, you rebuild the site from trusted parts. When a small business calls me as a Sydney WordPress developer after a hack, this is the route we usually end up on, because the backups either don’t exist or were taken after the infection.

Replace what you can

Delete and reinstall WordPress core, every plugin and every theme from their official sources. Don’t trust the existing copies, even if they look normal. If you have WP-CLI access, these commands compare your files against the official versions:

wp core verify-checksums

wp plugin verify-checksums –all

Check the places attackers hide

  • PHP files inside wp-content/uploads. That folder should hold images and documents, not code.
  • The .htaccess and wp-config.php files, for injected redirects or code.
  • The database, for script tags inside posts, widgets and the site URL settings.
  • Scheduled tasks, both WordPress cron events and the server’s own cron jobs.

A security scanner such as Wordfence, Sucuri or MalCare helps here. Treat its report as a starting point, though, not proof the site is clean.

Hours 12 to 24: Recover and close the hole

Find the entry point

Cleaning without knowing how they got in is guesswork. The usual causes are an outdated or abandoned plugin, a “nulled” premium plugin downloaded from an unofficial site, a reused password, or another compromised site on the same hosting account. Your server access logs, read alongside the dates from your hacked backup, often point straight to it.

Update and remove

Update WordPress, every plugin and every theme. Delete anything you don’t use, including inactive themes. Replace any plugin that hasn’t been updated in a year or more.

Ask Google to lift the warning

Open Google Search Console and check the Security issues report. Once the site is clean, request a review there. Reviews can take from a day to a few weeks. Spam pages the attacker created should return a 404 or 410 status, so Google drops them from its index over time.

Check whether customer data was exposed

If the site stored customer details, such as form entries, accounts or orders, work out whether they were accessed. Breach notification rules vary by location. Under the EU’s GDPR, for example, certain breaches must be reported to the regulator within 72 hours. If personal data may be involved, get proper advice quickly.

Five mistakes that make a hack worse

Most of the long, painful cleanups I’ve seen came from one of these.

  1. Restoring the latest backup without checking its date. If the infection is three weeks old, last night’s backup is infected too.
  2. Deleting the hacked files before copying them. You lose the trail that shows how the attacker got in, so you can’t close the hole.
  3. Changing only the WordPress password. Attackers often come back through hosting, SFTP or database access, which a WordPress password change doesn’t touch.
  4. Trusting one scanner’s “all clear”. Scanners miss custom backdoors. Check the uploads folder, the user list and the database yourself.
  5. Reinstalling the same nulled plugin. Pirated premium plugins are one of the most common ways malware gets onto WordPress sites. Buy the license or replace the plugin.

The next two weeks

A cleaned site isn’t finished on day one. Reinfection usually comes from a backdoor that was missed. For at least two weeks:

  • Run a security scan every day.
  • Check the user list and the uploads folder for anything new.
  • Watch Search Console for new spam pages or security alerts.
  • Keep daily backups going, and store copies away from the hosting account.

How to stop it happening again

Prevention is mostly routine. These five habits close most of the doors attackers use on small business sites:

  1. Update WordPress, plugins and themes at least weekly, and remove anything you don’t use.
  2. Give every person their own login, with a unique password and two-factor authentication.
  3. Keep daily backups stored away from your hosting account, and test a restore once a quarter.
  4. Use a firewall, either from your host, a security plugin or a service such as Cloudflare.
  5. Buy premium plugins and themes only from their official sources.

My take

Most hacked WordPress sites I see weren’t targeted. They were found. Automated tools scan the web for known plugin flaws, weak passwords and forgotten admin pages, and a small business site is as likely to be hit as a big one.

The good news is that the fix is routine work: updates, unique passwords, two-factor login and backups you’ve actually tested. None of it is glamorous. All of it is cheaper than spending the first 24 hours after a hack working through this list.


INTERESTING POSTS
The Overlooked Security Risk: Why Employee ID Badges Still Matter in a Zero Trust World

0
The Overlooked Security Risk: Why Employee ID Badges Still Matter in a Zero Trust World

In ths post, I will show you why employee ID badges still matter in a zero trust world.

Cybersecurity strategies have evolved dramatically over the past decade. Organizations now invest heavily in multifactor authentication, endpoint protection, cloud security, identity governance, and Zero Trust architectures. Yet while businesses strengthen their digital defenses, one fundamental aspect of organizational security often receives less attention: physical employee identification.

Even the most sophisticated cybersecurity infrastructure cannot fully protect an organization if unauthorized individuals can freely enter restricted areas, access unattended workstations, or move through sensitive facilities without being challenged.

This creates an important connection between cybersecurity and physical security. Organizations must understand not only who can access their digital systems but also who is physically present in their workplaces.

Employee identification badges, when combined with appropriate access controls and security policies, remain a practical component of a comprehensive security strategy.

Why Physical Identity Still Matters in a Digital Security Environment

Modern organizations increasingly operate through cloud applications, remote connections, and distributed workforces. As a result, security discussions often focus on protecting digital identities rather than managing physical access.

However, offices, data centers, warehouses, healthcare facilities, and other workplaces still contain valuable assets that require protection.

An unauthorized individual entering a restricted area may gain access to network equipment, confidential documents, company devices, or unattended computer systems.

These risks cannot be addressed exclusively through firewalls or endpoint security software.

Physical security policies help establish boundaries around facilities and sensitive areas, while employee identification procedures make it easier to distinguish authorized personnel from visitors.

A consistent identification system also supports employee accountability and helps security personnel recognize individuals who may require additional verification.

The objective is not to replace digital security controls but to extend organizational security practices into the physical workplace.

Employee ID Badges as a First Layer of Physical Identification

Employee identification badges provide a visible way to associate individuals with an organization.

A typical badge includes an employee’s photograph, name, job title, and company branding. Some organizations also include department identifiers or other information relevant to workplace operations.

When employees consistently display identification, colleagues and security personnel can more easily recognize authorized staff members.

This becomes particularly valuable in larger organizations where employees may not personally know everyone working in the building.

Businesses can use standardized ID badges to establish consistent visual identification across departments, facilities, and employee groups.

For example, an organization might use different badge designs to distinguish permanent employees, contractors, and visitors.

These visual distinctions can support security awareness and make it easier for staff to identify individuals who may need assistance or verification.

However, an important distinction must be maintained: a visible badge is not proof that the person carrying it currently has authorization to enter a restricted area.

Badges can be lost, stolen, duplicated, or retained after employment ends.

For that reason, visual identification should be treated as one security layer rather than a standalone access control mechanism.

How Employee Identification Fits Into Zero Trust Security

Zero Trust has become an influential approach to cybersecurity because it challenges the assumption that users or devices should automatically be trusted based on their location within a network.

Instead, access decisions should be based on appropriate verification, authorization, and contextual security controls.

Although Zero Trust architectures primarily address access to digital resources, their underlying principles can inform physical security practices as well.

For example, an employee who is authorized to enter a corporate office should not automatically receive access to every server room, storage facility, or restricted department.

Physical access permissions should reflect legitimate business requirements.

An identification badge may help establish who an individual claims to be, while an electronic access control system determines whether the associated credential is authorized for a particular location.

Additional verification may be appropriate for highly sensitive facilities.

Organizations should also review access permissions when employees change roles or leave the company.

This approach reinforces the broader principle of granting access according to operational necessity rather than assuming that all employees require identical privileges.

Importantly, implementing employee badges does not itself establish Zero Trust compliance. Badges are supporting tools within a much larger security framework.

How Employee Identification Fits Into Zero Trust Security

RFID, NFC, and Traditional Photo Badges: Understanding the Differences

Not all employee identification cards provide the same capabilities.

Selecting the appropriate technology requires understanding how different badge types operate and what security functions they can support.

Traditional photo ID badges

Standard photo badges are primarily designed for visual identification.

They typically display an employee’s name, photograph, title, and organization.

These credentials are useful for workplace recognition, visitor differentiation, and maintaining consistent professional identification.

However, they do not inherently provide electronic authentication or access control.

RFID and proximity cards

Radio-frequency identification technology allows compatible readers to communicate with electronic credentials without requiring physical contact.

Certain RFID and proximity cards are commonly used with building access control systems.

Depending on the technology, these systems can associate a credential with specific doors, access schedules, or facility permissions.

However, RFID is a broad category that includes technologies with substantially different security characteristics.

Some older proximity systems rely on relatively weak credential identification methods and may be vulnerable to cloning or unauthorized duplication.

Organizations should evaluate the security capabilities of their specific card technology and reader infrastructure rather than assuming all RFID credentials provide equivalent protection.

NFC-enabled cards

Near Field Communication is a short-range contactless technology used in applications such as mobile interactions, information exchange, and certain credential systems.

NFC-enabled cards may support different functions depending on the chip, software, and compatible reader.

Some NFC implementations are suitable for secure applications, while simple NFC tags may only store publicly readable information.

Therefore, NFC capability alone should not be interpreted as evidence that a card provides secure authentication.

Businesses should select credential technologies based on documented compatibility, security requirements, and the capabilities of their existing infrastructure.

The Security Risks of Lost, Stolen, and Unreturned Badges

One of the most common weaknesses in physical credential management is the failure to promptly address lost or unreturned identification cards.

An employee may misplace a badge during travel, leave it in a public location, or forget to return it after leaving the organization.

If the badge is connected to an electronic access system and remains active, it may present an unnecessary security risk.

Organizations should establish clear procedures requiring employees to report missing credentials promptly.

For electronically enabled badges, administrators should be able to revoke or suspend associated access permissions through the appropriate access control platform.

Replacement badges should be issued only after verifying the employee’s identity and following established administrative procedures.

Employers should also discourage employees from lending identification cards to colleagues or allowing unauthorized individuals to use their credentials.

Regular reviews of active access credentials can help identify outdated assignments and reduce the number of unnecessary permissions.

Physical badges without electronic access capabilities should also be managed carefully because they may be used to impersonate employees or create a misleading appearance of authorization.

Why Employee Offboarding Is a Critical Security Process

Employee onboarding receives considerable attention from HR and IT departments, but offboarding is equally important from a security perspective.

When an employee leaves an organization, administrators typically need to disable system accounts, revoke application permissions, recover company equipment, and update relevant records.

Physical identification credentials should be included in this process.

A departing employee may still possess a badge displaying the company’s name and logo, even after digital accounts have been disabled.

If the badge also functions as an electronic access credential, failure to deactivate it could leave physical access permissions active.

This creates an avoidable gap between digital identity management and facility security.

A coordinated offboarding checklist should address both physical and digital credentials.

Human resources, IT, and security personnel should have clearly assigned responsibilities so that access changes occur promptly and consistently.

For example, an employee departure notification can trigger separate tasks for disabling digital accounts, revoking building access, and collecting identification cards.

Organizations should also document exceptions, such as situations where a former employee retains limited authorized access for a defined business purpose.

The objective is to ensure that access permissions reflect current employment status and legitimate operational requirements.

Centralized Badge Management and Identity Lifecycle Security

As businesses expand, managing employee identification across multiple offices can become increasingly complex.

Different departments may use inconsistent badge templates, maintain separate employee records, or follow different procedures for issuing replacements.

These inconsistencies can create administrative inefficiencies and make it harder to maintain reliable identification standards.

A centralized approach to employee identification and physical access control can help organizations coordinate badge issuance and physical credential workflows across locations.

Online badge design and management tools can support consistent employee photographs, names, titles, and organizational branding without requiring each location to maintain separate design processes.

For example, a company operating ten regional offices may establish approved identification templates while allowing authorized administrators to prepare badges for employees at their respective locations.

Centralized physical badge management can also support consistent procedures for new hires, departmental transfers, and replacement requests.

However, organizations should distinguish between badge production systems and enterprise access control platforms.

A system used to design and order identification cards does not automatically manage electronic door permissions, digital identities, or security authentication.

Where these capabilities exist in separate systems, organizations should establish clear processes to keep employee information and credential status appropriately coordinated.

The Human Factor: Building a Security-Conscious Workplace

Technology alone cannot prevent every physical security incident.

Employees play an important role in maintaining secure workplaces by following identification policies, reporting suspicious activity, and respecting access restrictions.

For example, an employee may hold a secure door open for an unfamiliar individual out of courtesy, unintentionally allowing that person to bypass access controls.

This behavior, commonly associated with tailgating or unauthorized entry, illustrates why physical security awareness matters.

Organizations should train employees to recognize identification requirements and follow established procedures when encountering unfamiliar individuals.

However, security policies should avoid encouraging confrontational behavior.

Employees should know when to contact reception, facility security, or designated supervisors rather than attempting to personally investigate potentially unsafe situations.

Clear visitor identification, consistent badge use, and well-communicated access procedures can help make security expectations easier to understand.

The goal is to establish a workplace culture in which physical security becomes a routine operational responsibility rather than an occasional concern.

Building a Practical Employee Identification Security Policy

Organizations seeking to strengthen physical identification procedures should begin with a clear written policy.

This policy should define who receives identification credentials, what information appears on badges, and how cards are issued or replaced.

It should also establish procedures for temporary employees, contractors, visitors, and individuals working across multiple locations.

Where electronic access credentials are used, organizations should document how permissions are assigned, reviewed, and revoked.

Regular audits can help identify active credentials that no longer correspond to authorized personnel.

Businesses should also evaluate the information displayed on employee badges.

Names, photographs, and professional roles are often sufficient for visual identification. Unnecessary personal information, sensitive employee identifiers, or confidential internal details should generally be excluded.

Finally, organizations should ensure that badge management procedures remain practical for employees and administrators.

Security controls that are unnecessarily complicated may encourage workarounds, while clear and consistent processes are more likely to be followed.

Conclusion: Physical Identification Remains Relevant in Modern Cybersecurity

As cybersecurity continues to evolve, organizations must avoid overlooking the relationship between digital and physical security.

Cloud protection, multifactor authentication, and Zero Trust architectures are essential components of modern security strategies, but they do not eliminate the need to manage physical access and employee identification.

Well-designed identification badges help organizations distinguish employees from visitors, maintain consistent workplace standards, and support broader security procedures.

When combined with appropriate electronic access controls, employee training, and coordinated onboarding and offboarding processes, they contribute to a more comprehensive approach to organizational protection.

For businesses managing distributed workforces, multiple facilities, and changing employee populations, standardized badge management also offers practical administrative benefits.

Ultimately, effective security depends on more than protecting digital accounts. It requires understanding who has access to organizational resources, whether those resources exist in the cloud, on a corporate network, or behind a physical door.


INTERESTING POSTS
Fake ID Maker: Key to Online Identity Verification

0
Fake ID Maker: Key to Online Identity Verification

In this post, I will talk about Fake ID Maker as the key to online identity verification.

In today’s digital age, the concept of identity verification has become increasingly important. With the rise of online transactions and interactions, ensuring that individuals are who they claim to be is crucial.

Enter fake ID makers, tools that have gained fame for their ability to create fake IDs. While often associated with illegal activities, these tools also show the need for strong identity checks.

The primary purpose of identity verification is to protect both individuals and organizations from fraud and identity theft. As more personal and financial transactions move online, the risk of unauthorized access and misuse of personal information grows. This makes secure identity verification a key component of digital security.

Keywords such as fake ID maker, fake ID generator, and fake ID creator often appear in discussions about these tools, reflecting their relevance in the ongoing conversation about online security.

Understanding Fake ID Makers and Their Uses

Understanding Fake ID Makers and Their Uses

Fake ID makers are tools or software designed to produce counterfeit identification documents. These can range from simple driver’s licenses to more complex forms of identification, such as passports.

How these tools work is different, but they generally involve changing images and text to create a believable copy of a legitimate ID.

Fake IDs have a variety of applications, both legal and illegal:

  • Legal Uses: In some cases, fake IDs are used for harmless pranks or as props in movies and theater productions. They may also be used in educational settings for teaching purposes.
  • Illegal Uses: More commonly, fake IDs are associated with illegal activities such as underage drinking, identity theft, and fraud. These uses pose significant legal risks and ethical concerns.

To understand the context of identification documents, it is helpful to consider the historical development of national ID cards. These documents have evolved over time to meet the changing needs of society, highlighting the ongoing challenge of balancing security with privacy.

Legal Risks and Ethical Implications of Using Fake IDs

Using fake IDs can lead to serious legal consequences. While a fake ID might look appealing, it’s crucial to understand the potential repercussions. Here are some key legal risks associated with fake IDs:

  • Fines and Penalties: Possessing or using a fake ID can result in hefty fines. In many jurisdictions, this is considered a criminal offense.
  • Criminal Record: Being caught with a fake ID can lead to a lasting criminal record, hurting future job and school chances.
  • Legal Actions: Depending on the severity, individuals may face legal actions such as probation or even jail time.

Beyond the legal risks, there are ethical and social implications to consider:

  • Trust Issues: Using a fake ID erodes trust in systems designed to protect individuals and institutions.
  • Social Impact: It contributes to a culture of deceit, which can have broader societal implications.

The use of fake IDs, whether for purchasing alcohol or accessing restricted areas, has big risks and challenges. It’s important to weigh these against the perceived benefits of a fake license maker or other fake ID online solutions.

READ ALSO: Why Employee ID Badges Still Matter in a Zero Trust World

The Technology Behind Fake ID Creation

The Technology Behind Fake ID Creation

The creation of fake IDs involves advanced tools and methods. These can range from simple software applications to advanced printing technologies. Here’s a closer look at how fake IDs are made:

  • Software Tools: Fake ID makers often use graphic design software to replicate official documents.
  • Printing Technology: High-quality printers can produce IDs that look like real ones.
  • Material Use: The use of similar materials to those used in real IDs makes them seem real.

Despite these technologies, fake ID creators face significant challenges due to modern security measures. Many identification documents now include advanced security features such as holograms, barcodes, and embedded chips, making them difficult to replicate accurately.

For instance, the Next Generation Identification (NGI) system illustrates how modern security measures are evolving to combat identity fraud. These advancements in biometrics and other technologies make it increasingly challenging for fake ID generators to succeed.

Alternatives to Fake IDs for Online Verification

In the digital age, verifying one’s identity online is crucial. While the urge to use a fake ID maker can be strong, there are legitimate and safer alternatives available. These methods not only ensure compliance with legal standards but also give better security and trust.

  • Digital Identity Verification Services: Companies like Jumio and Onfido provide services that use biometric data and AI to verify identities. These services are widely accepted and recognized for their accuracy.
  • Two-Factor Authentication (2FA): This method adds an extra layer of security by requiring two forms of verification, such as a password and a mobile confirmation code.
  • Government-Issued Digital IDs: Some countries offer digital versions of official IDs, which can be used for online verification.
  • Blockchain Technology: Blockchain offers a decentralized and secure way to check identity, ensuring data integrity and security.

Choosing these legitimate methods over a fake drivers license maker or fake ID online offers several benefits:

  • Compliance with legal standards, avoiding potential fines or legal issues.
  • Increased trust and credibility when interacting with online platforms.
  • Enhanced security features that protect personal information from fraud.

For organizational contexts, legitimate photo ID credentials from ID Experts, IdenTrust, or Valid ID can serve as proper identification alternatives.

READ ALSO: Top Business Card Makers of 2026 for Quick, Professional Results Without Design Experience

Final Thoughts on Fake ID Use

The use of fake IDs, whether through a fake ID generator or a fake license maker, has big risks. From legal consequences to moral problems, the risks are bigger than any benefits.

It’s essential to focus on legal and right ways in identity verification. By opting for legitimate methods, individuals not only protect themselves but also help make online spaces safer.

As technology continues to evolve, keeping up with new changes in identity verification is crucial. This knowledge empowers individuals to make informed decisions and adapt to new challenges in the digital landscape.


INTERESTING POSTS
Home and Building Safety Documentation for Bosch, Kidde and Notifier Systems

0
Home and Building Safety Documentation for Bosch, Kidde and Notifier Systems

In this post, I will show you the home and building safety documentation for Bosch, Kidde and Notifier Systems.

A smoke alarm in the hallway chirps once a minute. A fire panel in an office building shows a trouble message that nobody on the night shift recognizes. In both cases the tempting move is to press a button until the noise stops. That clears the symptom, not the cause, and it can leave a building without protection.

Good home and building safety documentation tells you what each signal means on your exact device and who is allowed to act on it. Here is how to organize it for Kidde alarms, Bosch equipment and NOTIFIER fire alarm systems.

Start home and building safety documentation with the label

A brand name does not identify a manual. Read the label on each device and panel and record:

  • the model number;
  • the serial number;
  • the manufacture date, which matters for replacement;
  • firmware or hardware revision, where shown.

On a connected system, the panel’s approved configuration is part of the documentation too. A detector swapped for a “similar” model may not be listed as compatible.

Which document covers which task

DocumentWho uses itWhat it covers
User or occupant guideResidents, building staffSignals, testing, silencing, battery
Installation manualInstallersMounting, wiring, placement
Programming or service manualQualified techniciansPanel configuration, diagnostics
Compatibility listDesigners, techniciansWhich devices work with which panel

An occupant guide never replaces installation or programming instructions.

Check Kidde alarms by model and date

Kidde makes residential smoke, carbon monoxide and combination alarms. Power arrangements differ: some run on replaceable batteries, some on a sealed 10-year battery, others are hardwired with battery backup. So do indicator patterns and end-of-life signals. Find the guide that matches the model on the back of the alarm in the kidde manuals directory.

Test and replacement

The US National Fire Protection Association recommends testing smoke alarms monthly and replacing them 10 years after the date of manufacture. Carbon monoxide alarms have their own replacement period, set by the manufacturer, so check the date and the guide rather than assuming the same figure.

Use the test button as the guide describes. It confirms that the alarm sounds. It does not prove the sensor responds to real smoke or gas.

Chirps and lights

A chirp can mean a low battery, a fault or the end of the alarm’s life, depending on the model and pattern. Look it up before acting:

  • A low-battery chirp: replace the battery only if the guide allows it, then test.
  • An end-of-life signal: replace the alarm, because resetting it or fitting a new battery is not a fix.
  • A fault signal: follow the guide, and replace the unit if the signal returns.

Match Bosch documents to the equipment and task

Bosch’s range includes detectors, fire alarm control panels and intrusion systems. A detector and the unit it reports to usually need separate documents. Use the bosch manuals directory as a starting point, then confirm it lists your model and revision.

Programming instructions are for trained installers. A building manager needs the operating guide for the panel: what each indicator means, how to acknowledge and silence alarms, and which actions are reserved for the service company.

Keep NOTIFIER panel and device records together

NOTIFIER is a Honeywell brand of commercial fire alarm systems. On an addressable panel, each detector, call point and module has its own address, so a message on the display points to a specific device. That only helps if the register says where each one is.

The notifier manuals directory can help you find the panel’s operating manual and the documents for its field devices. Programming and service belong to qualified technicians.

Three types of signal

Fire alarm codes and panel manuals separate signals by what they mean:

SignalWhat it usually meansFirst response
AlarmPossible fireFollow the emergency plan; evacuate
SupervisoryFire-protection equipment off normal, such as a closed sprinkler valveInvestigate the named equipment; notify the responsible person
TroubleA fault in the system itself, such as a wiring or communication faultRecord the message; call qualified service

The installed panel’s manual has the final word. A color or beep pattern is not a diagnosis across brands.

Respond to alarms before thinking about a reset

Respond to alarms before thinking about a reset

When a fire alarm sounds, follow the emergency plan and leave. If a carbon monoxide alarm sounds, get everyone into fresh air, call the emergency services and wait until responders say the building is safe. Do not stay inside to find the cause.

For a confirmed non-emergency signal, write down the message, the time and the device address or location first. Then follow the permitted checks in the manual. Silencing, disconnecting or bypassing a device is not an investigation.

When protection is impaired

A fault that leaves part of a building unprotected needs immediate escalation under the site’s impairment procedure. The responsible person decides on notifications and temporary measures, such as a fire watch, according to local requirements. Keep the fault open in the log until the technician has recorded the repair.

Build the testing schedule and the register

Test intervals come from several sources at once: the manufacturer’s instructions, the fire code that applies, the authority having jurisdiction and the site’s own procedures. In the UK, for example, BS 5839-1 calls for a weekly user test of the fire alarm and servicing by a competent person at intervals of no more than six months.

Tests can send signals to a monitoring center or trigger door releases and other outputs. Notify the monitoring company before a test and confirm afterwards that the system is back to normal.

What the register should hold

RecordDetails
IdentityManufacturer, model, serial number, revision
LocationRoom or zone, panel and device address
InstallationDates, installer, manuals used
ConfigurationApproved settings and every change, with date and name
Testing and serviceResults, defects, corrective action, follow-up
ContactsService company, monitoring center, escalation

Update the register after each replacement or service visit, keeping the old and new identifiers. A failed test needs an owner and a date for the return visit, not just the word “failed.”


INTERESTING POSTS
Mobile vs Residential vs Datacenter Proxies: Which One Do You Need?

0
Mobile vs Residential vs Datacenter Proxies: Which One Do You Need?

In this post, we will compare mobile vs residential vs datacenter proxies to answer the question – which one do you need?

A proxy stands between you and the website you visit. The site sees the proxy’s IP address, not yours. That simple idea covers three quite different products, and choosing the wrong one costs either money or results. Datacenter proxies are cheap and fast but easy to spot. Residential proxies look like home users. Mobile proxies look like phones on a carrier network and are the hardest to block. This article explains how each type works, what it is good for, and how to choose.

Why the type of IP address matters

Every IP address belongs to a network, and that ownership is public. Websites and anti-fraud systems look up who owns the address of each visitor. An address owned by a hosting company tells them the visitor is probably a server or a script.

An address owned by a home internet provider or a mobile carrier suggests an ordinary person. Many sites apply stricter limits, more CAPTCHAs or outright blocks to the first group. So the origin of a proxy’s address decides how the rest of the web treats you.

Datacenter proxies

Datacenter proxies run on servers in hosting facilities. Their addresses come from cloud and hosting providers.

Strengths: they are the fastest and cheapest type, with stable connections and usually unlimited or very generous traffic. You can buy large numbers of them.

Weaknesses: they are the easiest to detect. Whole address ranges of hosting companies are flagged by many sites, so one bad neighbour can affect you. Social networks, ticketing sites, marketplaces and search engines often challenge or block them.

Good for: tasks where the target does not care who you are. Examples are monitoring your own websites, accessing public APIs, bulk downloads from tolerant sources and general privacy from a network you do not trust.

Residential proxies

Residential proxies route traffic through addresses that internet providers assign to homes. Providers usually sell them as a large rotating pool and charge by the gigabyte.

Strengths: requests look like they come from ordinary households, so they pass many checks that stop datacenter addresses. Pools cover many countries and cities, which helps with location-specific work such as checking local prices or search results.

Weaknesses: speed and stability vary, because the exit points are consumer connections. Paying per gigabyte gets expensive for heavy pages or video. And you should ask how a provider sources its addresses: a reputable one gets clear consent from the people whose connections are used.

Good for: web scraping at scale, price and ad verification across regions, SEO monitoring and other work that needs many different addresses in many places.

Mobile proxies

Mobile proxies use addresses that mobile carriers give to phones and modems on 4G and 5G networks.

Carriers do not have enough public addresses for every subscriber, so they place many users behind each one. A website that blocks a single mobile address may lock out a large number of real customers at once, and sites know this. As a result, mobile addresses get the highest level of trust of the three types.

Mobile proxies come in two forms. In a shared pool, you rotate through many addresses together with other customers. With a dedicated mobile proxy, one physical device on a carrier network is reserved for you. Providers such as IPVolt rent dedicated devices by the day or month and let you change the device’s IP on demand or on a schedule, so you get a fresh carrier address without sharing the device.

Strengths: the best acceptance on strict platforms, real carrier and location data, and with a dedicated device a stable identity that you control.

Weaknesses: the highest price per proxy, and speeds limited by the mobile network. The carrier chooses the new address on rotation and sometimes returns the same one.

Good for: managing social media and marketplace accounts, testing mobile apps and ads as a real mobile user would see them, and reaching sites that block the other two types.

A quick comparison

  • Cost: datacenter is lowest, residential is in the middle and billed by traffic, mobile is highest.
  • Speed: datacenter is fastest, residential varies, mobile depends on the carrier signal.
  • Detection risk: datacenter is high, residential is low, mobile is lowest.
  • Best use: datacenter for volume on tolerant sites, residential for wide geographic coverage, mobile for strict platforms and long-lived accounts.

How to choose

Start with the target, not the proxy. If the site you work with does not block hosting addresses, a datacenter proxy does the job for the least money. If you need thousands of addresses across many countries for data collection, residential pools fit best. If you run accounts that must look like one consistent phone user, or the site rejects everything else, use a mobile proxy and keep one proxy per account.

Whatever you pick, check a few things before paying: which protocols are supported (HTTP and SOCKS5 cover almost everything), how rotation works, whether you can test for a short period, and what the provider’s rules on acceptable use are. Setup guides, such as the ones at https://ipvolt.com/guides, show how to connect a proxy to browsers, scripts and automation tools.

Stay away from free proxy lists. Nobody runs a server for nothing: free proxies are often slow, short-lived and able to read or change unencrypted traffic.

Final thoughts

There is no single best proxy type. Datacenter proxies win on price and speed, residential proxies on reach, and mobile proxies on trust.

Match the type to how strict your target is and how much a block would cost you, and you will avoid both overpaying and getting stopped at the door.


INTERESTING POSTS
How To Secure Your WordPress Website From Hackers

How To Secure Your WordPress Website From Hackers

This post will show you how to secure your WordPress website from hackers.

In today’s digital landscape, securing your WordPress website is paramount. WordPress’s popularity as a content management system (CMS) has become a prime target for hackers and malicious actors.

In this post, I will show you the essential steps and best practices to protect your WordPress website from potential security vulnerabilities and keep it safe from unauthorized access.

By implementing these measures, you can enhance the security of your website and mitigate the risk of potential attacks.

How To Secure Your WordPress Website From Hackers

Here are tips on how to secure your WordPress website from hackers.

1. Keep your computer and network protected

Keep your computer and network protected

First, you should ensure that your computer is clean and free from viruses and malware.

Perform occasional scanning to locate and eliminate viruses, as they can be anywhere in your system.

Here are some antivirus programs that you can use:

kaspersky total security
Kaspersky Lab
Kaspersky Antivirus is an antivirus protection solution that protects your computers from virus attacks and other...Show More
Kaspersky Antivirus is an antivirus protection solution that protects your computers from virus attacks and other threats that may result from internet usage or other forms of usage. Show Less
Panda Dome Security Suite60% OFF
Panda Dome Security Suite
Your advanced protection suite for home and business needs.
Your advanced protection suite for home and business needs. Show Less
Norton 36066% OFF
Norton 360
Norton 360 is a security suite that utilizes advanced machine learning technology in dealing with all types of malware...Show More
Norton 360 is a security suite that utilizes advanced machine learning technology in dealing with all types of malware including Trojans, ransomware, etc. 100% guaranteed protection against all types of malware and your best bet for privacy protection. Show Less
Avira Prime
Avira Prime
Avira Prime is the ultimate security suite for data safety and protection from online threats that gives you full access...Show More
Avira Prime is the ultimate security suite for data safety and protection from online threats that gives you full access to Avira products like antivirus, Phantom VPN, software updater, system optimization tool, and a password manager. Show Less
ESET Smart Security Premium25% OFF
ESET HOME Security Premium
ESET HOME Security Premium is a fully-fledged security software with amazing features and even a password manager. Smart...Show More
ESET HOME Security Premium is a fully-fledged security software with amazing features and even a password manager. Smart protection for Windows, Mac, and Android devices. Show Less
G DATA Total Security
G DATA Total Security is a complete protection suite that offers total security online and offline. The suite includes...Show More
G DATA Total Security is a complete protection suite that offers total security online and offline. The suite includes an antivirus engine, a password manager, firewall protection, device control, and internet security tools. Intelligent security suite for all device types. Show Less
AVG Ultimate38% OFF
AVG Ultimate
A combined antivirus plus VPN for total protection.
A combined antivirus plus VPN for total protection. Show Less
McAfee Total Protection50% OFF
McAfee Total Protection
An easy-to-use security suite for data safety and device protection.
An easy-to-use security suite for data safety and device protection. Show Less
Trend Micro Premium Security Suite53% OFF
Trend Micro Premium Security Suite
Premium security suite for device protection and identity safety.
Premium security suite for device protection and identity safety. Show Less
VIPRE Advanced Security
Best security solution for emerging threats and data safety.
Best security solution for emerging threats and data safety. Show Less
Total AV
Total AV
Protects your devices and online activities in real-time.
Protects your devices and online activities in real-time. Show Less
PC Matic Security
PC Matic Security
PC Matic Security is a security software that protects against malware, viruses, and ransomware.
PC Matic Security is a security software that protects against malware, viruses, and ransomware. Show Less
K7 Total Security
K7 Total Security
K7 Total Security is a comprehensive security software suite that provides protection against malware, viruses, and...Show More
K7 Total Security is a comprehensive security software suite that provides protection against malware, viruses, and other cyber threats, as well as features such as parental controls, data encryption, and a personal firewall. Show Less
F-Secure Total
F-Secure Total
F-Secure Total is a security suite that provides protection for your devices against malware, viruses, and online...Show More
F-Secure Total is a security suite that provides protection for your devices against malware, viruses, and online threats with features like antivirus, firewall, VPN, and parental control. Show Less
Sophos
Sophos
Sophos Antivirus is a security software that helps protect computer systems from various malware and online threats.
Sophos Antivirus is a security software that helps protect computer systems from various malware and online threats. Show Less
Surfshark One
Surfshark One
Surfshark One is a cybersecurity bundle that provides users with Surfshark VPN, Alert, Search, and Antivirus that...Show More
Surfshark One is a cybersecurity bundle that provides users with Surfshark VPN, Alert, Search, and Antivirus that combines security, privacy, and convenience into one powerful package. Surfshark is an award-winning VPN service for keeping your digital life secure. Show Less
Avast One
Avast One
Avast One is an all-in-one security suite offering antivirus protection, VPN, performance optimization, and privacy...Show More
Avast One is an all-in-one security suite offering antivirus protection, VPN, performance optimization, and privacy tools for comprehensive digital security. Show Less

Your network should also be protected; try to avoid visiting websites that are not secure, and do not share your site admin details on any site other than WordPress.

If you use a Windows PC, ensure that the Firewall is active and running whenever you go online.

2. Keep WordPress Core, Themes, and Plugins Updated

Regularly updating your WordPress core installation, themes, and plugins is crucial for maintaining a secure website. Outdated software can have known vulnerabilities that hackers can exploit. Follow these steps:

  • Enable automatic updates for the WordPress core, themes, and plugins.
  • Regularly check for updates manually and install them promptly.
  • Remove unused themes and plugins to minimize potential risks.

READ ALSO: Website Security Check: How Secure Is Your Website?

3. Use Strong and Unique Login Credentials

Use Strong and Unique Login Credentials

Weak or easily guessable login credentials make your WordPress website vulnerable to brute-force attacks.

Whenever you want to access the dashboard of your WordPress website, you are to visit the admin login page and log in using a username and password. These details are set by you and you alone should know them.

First, change the default “admin” username to something unique and choose a secure password.

Most WordPress websites get hacked because their owners use weak passwords that are easy for hackers to guess. Implement the following measures:

  • Use strong, complex passwords that combine uppercase and lowercase letters, numbers, and special characters.
  • Avoid using common passwords or personal information in your login credentials.
  • Consider using a password manager to generate and securely store unique passwords for each account.

4. Limit Login Attempts and Enforce Two-Factor Authentication (2FA)

Limit Login Attempts and Enforce Two-Factor Authentication

You should know what 2-factor authentication is all about; it is a security process whereby 2 different authentication processes must be completed before access will be granted.

If you are concerned about your WordPress website’s security, then you should be using 2FA. That way, even if hackers manage to get your password, they will find it difficult to bypass the 2FA process.

You can install several 2FA WordPress plugins, but I recommend installing the Google Authenticator plugin. It is a free plugin with a 4.5 out of 5 stars rating by WordPress users.

Limiting the number of login attempts and implementing two-factor authentication adds an extra layer of security to your WordPress website:

  • Install a plugin that limits failed login attempts, such as Login Lockdown or Limit Login Attempts.
  • Enforce two-factor authentication using a plugin like Google Authenticator or Authy, which requires a second verification step, such as a unique code sent to your mobile device.

READ ALSO: Top 8 WordPress LMS Plugins to Use in 2026

5. Secure Your WordPress Admin Area

The WordPress admin area is a critical access point that requires special attention. Apply the following measures:

  • Change the default login URL (/wp-admin/) to a custom one to avoid easy identification.
  • Restrict access to the admin area by IP address using plugins like Limit Login Attempts Reloaded or WPS Hide Login.
  • Implement a web application firewall (WAF) to filter out malicious traffic and protect against common attacks.

6. Add Security Questions

Add Security Questions

As with the 2FA Authentication, you can add security questions to your login page. Login will only be accepted if the answer to your security question is entered correctly. This is a very efficient way of securing your WordPress website, as hackers will have difficulty figuring out the answer.

You can use multiple plugins to implement this security process, and you can go for any of them. When setting your questions, avoid very easy ones; even if it’s easy, make sure the answer you provide is not simple.

For example, you can set “What is the name of your Pet?” That’s a relatively easy question, and guess answers would be a dog, cat, etc. Your answer should be something like “A brown hairy dog”; that would be difficult to decipher.

7. Use Reliable Themes and Plugins

Using reputable and regularly updated themes and plugins significantly reduces the risk of vulnerabilities. Follow these guidelines:

  • Download themes and plugins from trusted sources, such as the official WordPress repository or reputable third-party marketplaces.
  • Read user reviews and ratings before installing any theme or plugin.
  • Don’t use nulled themes or plugins, irrespective of how legit they may appear.
  • Regularly update themes and plugins to benefit from security patches and bug fixes.

8. Scan your WordPress site

Scan your WordPress

Your WordPress software can become infected by a virus, so you should scan it once in a while to be on the safe side. This can be done using related WordPress plugins or online URL scanners.

Some trusted websites you can use to scan include virustotal.com, siteguarding.com, Wpsec.com and many more.

You are not at risk using these websites as all you supply is just your website’s URL. At the end of a scan, you will get results to know if malware is present or other vulnerabilities in your WordPress site. You will also get insights on how to get rid of them.

READ ALSO: Hacked WordPress Site? What to Do in the First 24 Hours

9. Secure Your Hosting Environment

The security of your WordPress website is not solely dependent on the CMS itself; your hosting environment also plays a crucial role.

Take the following precautions:

  • Choose a reputable hosting provider that prioritizes security and offers features like SSL certificates and firewalls.
  • Keep your hosting environment up to date, including the server software, PHP version, and other dependencies.
  • Regularly monitor server logs and set up intrusion detection systems to identify potential security breaches.

10. Update your software, themes, and plugins

Update your software

You must run the latest versions of the themes and plugins you use, as they often carry new security patches.

It would be easier for a hacker to hack old WordPress versions than the new ones, and your site would be at risk if you do not update it.

Also, stay away from unofficial sources of WordPress themes and plugins. Purchase and download from trusted ones only.

11. Back-Up Your Website Regularly

secure wordpress website from hackers

Backing up your website regularly is essential, and it is another tip to secure a WordPress website from hackers that I’ll be talking about.

You should back up your website regularly because if it eventually gets hacked, it would be a lot easier to recover posts, pages, and other things.

Even if your site is not hacked, it can happen to your hosting service provider (Yeah! They get hacked too) and will affect your site.

Backups are easy to perform on WordPress, and the XML files are very low-sized. You can use WordPress plugins to perform site backups at scheduled intervals.

Creating regular WordPress website backups is crucial for recovering from potential security incidents or data loss. Consider the following:

  • A reliable backup plugin, such as UpdraftPlus or BackupBuddy, schedules automated backups.
  • Store backups in secure, off-site locations like cloud storage or a separate server.
  • Test the backup restoration process periodically to ensure its integrity and functionality.

12. Install a Security Plugin

Install a Security Plugin

Adding a security plugin can provide additional layers of protection and simplify the implementation of various security measures. Consider the following:

  • Install a reputable security plugin like Sucuri, Wordfence, or iThemes Security.
  • Configure the security plugin to perform regular scans for malware, monitor file integrity, and block suspicious IP addresses.
  • Enable features like firewall protection, brute force attack prevention, and login lockdown options provided by the security plugin.

13. Protect Against Malware and Vulnerabilities

Malware and vulnerabilities can compromise the security of your WordPress website. Take the necessary steps to protect against them:

  • Regularly scan your website for malware using security plugins or online tools like VirusTotal.
  • Remove any malicious code or infected files identified during the scanning process.
  • Update your security plugin’s malware signature database to protect against the latest threats.

14. Educate Yourself and Your Users

Security is a shared responsibility. Educate yourself and any users who have access to your WordPress website about best security practices:

  • Stay informed about the latest security threats and vulnerabilities related to WordPress.
  • Train users on the importance of using strong passwords, identifying phishing attempts, and avoiding suspicious links or downloads.
  • Encourage users to report any suspicious activities or potential security breaches immediately.

15. Disable File Editing within the WordPress Dashboard

WordPress allows administrators to edit theme and plugin files directly from the dashboard by default. However, disabling this feature can prevent unauthorized access and minimize the risk of accidental code modifications. To disable file editing:

  1. Open the wp-config.php file of your WordPress installation.
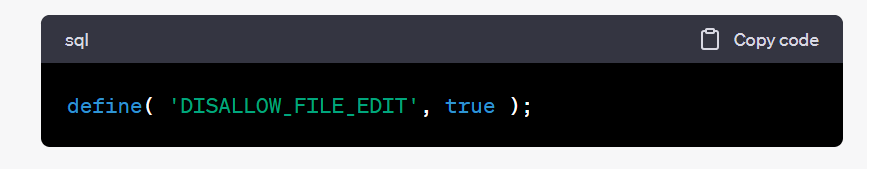
  2. Add the following line of code before the “That’s all, stop editing!” comment
    SQL code
  3. Save and upload the modified wp-config.php file back to your server.

Disabling file editing adds an extra layer of security, as even if an attacker gains access to your WordPress admin area, they won’t be able to modify your theme or plugin files directly.

Remember to always take a backup of your wp-config.php file before making any modifications for safety purposes.

By implementing this additional security measure, you further reduce the potential attack surface and enhance the overall security of your WordPress website.

Conclusion

Securing your WordPress website from hackers requires a proactive approach and a combination of technical measures, regular updates, and user awareness.

Implementing the steps outlined in this comprehensive guide can significantly reduce the risk of unauthorized access, malware infections, and other security breaches.

Maintaining a secure website is an ongoing process, so stay vigilant, keep up with the latest security practices, and regularly review and update your security measures to protect your valuable online presence.

By following the security tips listed in this article, you should be able to secure your WordPress website from hackers.


INTERESTING POSTS
AI APIs for Developers: A Practical Guide to Building Reliable Features

0
AI APIs for Developers A Practical Guide to Building Reliable Features

For developers, AI APIs for developers are useful when they turn a model capability into a dependable product feature. That requires more than sending a prompt and displaying the answer. The application must define the task, control data flow, validate output, handle outages, measure cost, and monitor whether the result helps users. The model is one dependency inside a larger software system.

The best design begins with the user’s job. A team building document search needs to retrieve relevant source material and enforce permissions before a language model writes a response. A voice interface needs to manage audio capture, transcription, model latency, and playback. A coding assistant needs boundaries around repository access and generated code. Each use case calls for a different combination of models and controls.

Start with a product requirement, not a model name

Describe the feature in terms a product and engineering team can test. “Make support better” does not define success. “Draft a response using the approved return policy and show the source section to the agent” is more precise. It identifies the inputs, expected output, and the human who can review the result.

Write success criteria before choosing a model. For a drafting tool, those criteria might include factual consistency with the source, correct tone, response time, and the share of drafts accepted with minor edits. For data extraction, schema validity and field accuracy may matter more. Use criteria that correspond to product behavior rather than model reputation.

Collect representative examples and review their permissions. If the dataset contains customer or business information, use synthetic or redacted examples for early experiments. Later testing with real data should follow the organization’s privacy and security process.

Choose the API boundary

An application can call one provider directly, use a managed gateway for several model providers, or run a gateway in its own infrastructure. A direct connection can be simplest when one model meets the product’s needs. A gateway can reduce integration and billing work when a feature needs multiple models. A self-hosted layer can help with network control but requires an operations owner.

The API boundary should preserve the capabilities the feature uses. If the application depends on streaming, tool calls, structured outputs, image input, or a specific safety setting, confirm that the selected route supports them. A nominally compatible API can still differ in edge cases or optional parameters.

When evaluating a common access layer, developers can review a service such as AI APIs for developers. The site currently describes one API and account for a range of models and tools. Treat that as an evaluation starting point; check the current model catalog, SDK support, endpoint schemas, pricing, and privacy documentation against the feature’s requirements.

Design for output uncertainty

Model responses are generated and may vary. Do not use a natural-language answer as a substitute for deterministic application logic. If the output changes an account, sends a payment, or performs an irreversible action, require a separate authorization and validation path.

For structured data, define a schema, parse the response, and reject values outside the allowed set. For summaries or recommendations, ground the answer in approved documents where possible and show the source references. For tool use, validate each argument and enforce permissions in application code before executing it.

Set maximum input and output sizes. Restrict the number of conversation turns or tool calls. Add a total workflow deadline so a chain of model calls cannot keep a request open indefinitely. For long tasks, use a job queue and return a status to the user rather than holding a web connection open.

Keep data and credentials under control

Trace every part of a request: user message, system instruction, retrieved document, file, tool output, and metadata. The content actually sent may be larger than the visible prompt. Remove fields that the model does not need, and ensure retrieval systems enforce user permissions before adding documents to context.

Use server-side credentials stored in an approved secret manager. Scope API keys to the needed operations if the provider supports it, rotate them, and avoid exposing them in browser code or mobile bundles. A browser application should send requests to a backend service that can enforce authorization, rate limits, and input validation.

Review data retention and processing terms for each service in the request path. A gateway may add another processor, so assess it alongside the upstream model provider. Decide what can be logged, who may access those logs, and when they are deleted. Operational telemetry can often use request IDs, model names, status, duration, and usage without storing raw content.

Make reliability a feature requirement

A user-facing AI feature needs a defined behavior for slow or unavailable services. Set a timeout that reflects user expectations. Use bounded retries for transient errors and avoid repeating invalid requests. If a fallback model is available, verify that its output fits the same schema and meets the feature’s minimum quality bar.

Show a useful state when the model cannot respond: allow the user to retry, offer a non-AI path, or save work for later. Avoid presenting a partial or stale answer as if it were complete. The product should distinguish an empty response, a provider error, and an application validation failure in telemetry.

Monitor both system behavior and user outcomes. System signals include errors, latency, rate limits, usage, and fallback frequency. Product signals include edits, acceptance, completion, escalation, or correction. A low error rate does not prove the feature is useful, while user dissatisfaction can reveal prompt or retrieval problems that infrastructure metrics miss.

Evaluate with the real workflow

Build a small regression set from representative tasks. Score the outputs against a rubric that reflects the feature’s purpose. Keep edge cases and negative examples. Repeat the tests when the prompt, model, endpoint, or retrieval configuration changes.

For model comparisons, use the same inputs and record the exact model identifier, prompt version, response time, usage, and result. Review failures rather than relying only on an aggregate score. If the application uses tools or retrieval, test the complete loop, because an excellent model response cannot compensate for a missing document or incorrect permission check.

After deployment, sample outputs in a privacy-conscious way and collect user feedback. Define an owner who can respond to a model update, provider incident, or cost spike. Keep a rollback path and a feature flag so the team can disable or redirect the feature without a full application release.

Keep costs understandable

Calculate cost per completed user task. Include prompt history, retrieved context, generated output, tools, retries, and any multimodal steps. Cost per token is one input to the calculation, not the whole picture. A model that requires several follow-up calls can cost more than a stronger model that finishes in one pass.

Set budgets at the workflow or account level where possible. Alert on unexpected usage, cap user-controlled input, and prevent untrusted callers from turning an API key into an open proxy. If the product offers several models, explain which one a user is selecting and whether a more capable model has a different cost or response time.

A concise design checklist

Before release, confirm that the feature has a narrow task definition, an evaluation set, data minimization, secure credentials, output validation, bounded timeouts, safe failure behavior, and cost monitoring. Document who owns model changes and how to roll back. Test the full experience with realistic user inputs, not only an API playground prompt.

AI APIs make capabilities accessible, but reliable products come from the surrounding engineering. When the application controls data flow, validates results, monitors cost, and gives users a graceful path through failure, model access can become a useful part of the product rather than an unpredictable side effect.

FAQ

What is the first step in building with an AI API?

Define one user task and how success will be measured before selecting a model or endpoint.

Can a model API enforce application permissions?

No. The application must check access rights and validate actions independently of model output.

What metrics matter after release?

Track system behavior such as latency, errors, and usage alongside product outcomes such as completion, edits, and escalations.


INTERESTING POSTS
20 Online Security Tips For Kids

1

Here, we will show you online security tips for Kids.

In today’s digital age, where children have easy access to the internet, ensuring their online security is a paramount concern for parents and guardians.

With the prevalence of online fraud and cyber threats, it’s essential to equip children with the knowledge and tools they need to stay safe online.

This guide outlines various online security tips for kids and offers practical steps to protect their digital well-being.

Online Security Tips For Kids

1. Educate your kids on the importance of online security

Educate your kids on the importance of online security

The first and most important step in ensuring your kid’s safety online is educating them about the importance of online security. All other safety measures might be futile if your kids do not know the right thing to do.

Teach them to look out for suspicious activity and avoid the prying eyes of internet fraudsters.

Here are some specific topics you can cover with your kids:

READ ALSO: Most Dangerous Websites You Should Avoid

2. Take password management measures

Strong passwords are essential for online security, but they can be difficult to remember and manage. Help your kids create and manage strong passwords by using a password manager.

A password manager is a software application that helps you store and manage your passwords securely.

Here are some tips for using a password manager:

  • Choose a reputable password manager with a strong security track record.
  • Create a strong master password for your password manager. This is the password that you will use to access all of your other passwords.
  • Use a unique password for every website and online account.
  • Enable two-factor authentication for your password manager and all your online accounts.

Public Security tips on kids avoiding public Wi-Fi 

3. Public Security tips on kids avoiding public Wi-Fi 

Public Wi-Fi networks are not secure and should be avoided whenever possible. If your kids must use public Wi-Fi, there are a few things they can do to protect their privacy and security:

  • Use a VPN. A VPN service encrypts your traffic, making it more difficult for hackers to intercept your data. You can check out the best VPN services.
  • Avoid logging into sensitive accounts, such as your bank account or email, on public Wi-Fi.
  • Be careful about what information you share on public Wi-Fi. Avoid sharing personal information, such as your home address or phone number.

READ ALSO: 10 Best Safety Tips for Online Shopping

4. Secure your wireless home network

Your home wireless network should be secure to protect your family’s devices and data from unauthorized access.

Here are some tips for securing your wireless home network:

  • Use a strong password for your Wi-Fi network. Your Wi-Fi password should be at least 12 characters long and include a mix of uppercase and lowercase letters, numbers, and symbols.
  • Enable WPA2 encryption. WPA2 is the most secure type of Wi-Fi encryption.
  • Keep your router’s firmware up to date. Router manufacturers regularly release firmware updates that include security patches.
  • Change the default username and password for your router. Many routers come with default usernames and passwords that are easy to guess. Change the default username and password to something more secure.

Best Parental Control Software Deals

Qustodio
Qustodio
Trusted by over 4 million parents as the all-in-one parental control application
Trusted by over 4 million parents as the all-in-one parental control application Show Less
Kaspersky Safe Kid
Kaspersky Safe Kids
Kaspersky Safe Kids is a parental control app that helps parents monitor and control their child's online activity...Show More
Kaspersky Safe Kids is a parental control app that helps parents monitor and control their child's online activity, including web browsing, app usage, and location tracking. Show Less
Wondershare FamiSafe Parental Control
FamiSafe
This is one of the most reliable parental control apps for controlling screen time, regulating content, and tracking...Show More
This is one of the most reliable parental control apps for controlling screen time, regulating content, and tracking your kids' location in real-time. Show Less
ESET Parental Control
This parental monitoring app allows you to monitor and control your kids' online activity find their location in...Show More
This parental monitoring app allows you to monitor and control your kids' online activity find their location in real-time, and set screentime limits for gaming and other activities. Show Less
Norton Family
Norton Family
Gives your kids free access to the internet while giving you total control over their online activities.
Gives your kids free access to the internet while giving you total control over their online activities. Show Less
mSpy
mSpy
mSpy is a mobile monitoring and tracking software that allows users to monitor the activity on a smartphone or tablet...Show More
mSpy is a mobile monitoring and tracking software that allows users to monitor the activity on a smartphone or tablet, including tracking location, text messages, call history, and social media activity, and in some cases, it can also be used to monitor activities on a computer. Show Less
EyeZy
EyeZy
EyeZy is an advanced parental control software that allows parents to monitor and control their children's internet...Show More
EyeZy is an advanced parental control software that allows parents to monitor and control their children's internet activity, including monitoring their browsing history, blocking websites, setting time limits, and more. Show Less
uMobix
uMobix
uMobix is a phone monitoring app offering features like call tracking, text message spying, and GPS location, raising...Show More
uMobix is a phone monitoring app offering features like call tracking, text message spying, and GPS location, raising privacy concerns despite aiming to help parents monitor children's online activity. Show Less
SpyBubble
SpyBubble
SpyBubble is a phone monitoring app used for parental control, employee monitoring, or catching cheating spouses...Show More
SpyBubble is a phone monitoring app used for parental control, employee monitoring, or catching cheating spouses, raising privacy concerns due to its ability to track calls, messages, location, and more. Show Less

5. Make use of a reliable VPN

A VPN (virtual private network) encrypts your internet traffic and routes it through a server in another location. This makes it more difficult for hackers to track your online activity and steal your data.

When choosing a VPN for your kids, look for one with a good reputation and strong security features. Some of the recommended VPN service providers include:

Read Also: Top 5 Checklist for Choosing a VPN Service Provider

6. Set a limit to time usage and internet access for your kids

Set a limit to time usage and internet access for your kids

It is important to set limits on how much time your kids spend online and which websites they can visit. This will help to protect them from online dangers and prevent them from becoming addicted to the internet.

Here are some tips for setting limits on your kids’ internet usage:

  • Use a parental control app to block inappropriate websites and set time limits for internet access.
  • Talk to your kids about the importance of having a balanced life and spending time offline.
  • Make sure your kids have other activities to enjoy besides spending time online, such as sports, hobbies, and spending time with family and friends.

7. Teach Critical Thinking

In the age of information overload, it’s essential to teach your children critical thinking skills. Encourage them to question the credibility of online content and discern between reliable sources and potentially misleading information.

Explain the importance of verifying facts and cross-referencing information from multiple sources to develop a well-rounded perspective.

8. Establish Open Communication

Creating an environment of open communication is crucial. Let your kids know that they can approach you with any concerns or online encounters they may have.

Assure them that they won’t face punitive measures for sharing their experiences, which will make them more likely to seek guidance and support when needed.

READ ALSO: What 700 Hacked Fridges Teach About Your Router

9. Monitor Social Media Activity

Monitor Social Media Activity

Regularly reviewing your children’s social media profiles and friends lists allows you to stay informed about their online interactions. Use these moments as opportunities for discussion.

Talk about appropriate behavior, the importance of setting privacy settings to limit who can see their posts, and the potential consequences of sharing too much information publicly.

READ ALSO: The Ultimate Social Media Security Guide for Individuals and Businesses

10. Beware of Cyberbullying

Cyberbullying is a serious concern in the digital age. Explain to your kids what cyberbullying is and how it can affect individuals emotionally and psychologically.

Encourage them to report any instances of online harassment, whether they are the victim or witness it happening to someone else. Make it clear that they should never participate in such behavior.

11. Privacy Settings

Help your children navigate the privacy settings of social media platforms and apps. Show them how to adjust these settings to limit the visibility of their personal information, posts, and interactions.

Discuss the importance of periodically reviewing these settings, as platforms may update their privacy features.

12. Use Kid-Friendly Search Engines

Introduce your children to kid-friendly search engines like Kiddle or KidzSearch.

These search engines filter out inappropriate content and ensure that the search results are age-appropriate, providing a safer online experience.

13. Safe Online Gaming

Safe Online Gaming

Online gaming can be a fun and social experience, but it’s important to teach your kids about in-game chat safety.

Emphasize the importance of not sharing personal details with strangers they meet in games and the value of using mute or block features when encountering inappropriate behavior.

14. Avoid Stranger Danger

In the virtual world, the concept of “stranger danger” is just as relevant as in the physical world.

Teach your children never to share personal information, such as their full name, address, school, or contact details, with individuals they encounter online.

Stress the importance of not accepting friend requests or engaging in private conversations with unknown individuals.

15. Keep Software Updated

Regularly updating the operating systems, apps, and software on your children’s devices is crucial.

These updates often include security patches that protect against vulnerabilities that hackers can exploit.

Set devices to automatically update when possible to ensure they are always equipped with the latest security features.

16. Teach Safe Downloading

Teach Safe Downloading

Instruct your children to only download apps, games, and files from reputable sources, such as official app stores like the Apple App Store or Google Play Store.

Explain the risks of downloading software or files from unverified websites or links in unsolicited emails, as these can contain malware or viruses that can harm their devices and compromise their security.

17. Encourage Two-Factor Authentication

Two-factor authentication (2FA) adds an extra layer of security to online accounts. Teach your kids about the importance of enabling 2FA wherever possible.

This additional step, often involving a code sent to their mobile device, helps prevent unauthorized access to their accounts, even if someone has their password.

18. Caution with Webcams

While webcams are useful for video calls and streaming, they can also pose risks if used improperly. Emphasize the importance of only sharing video with people your children know and trust.

Teach them how to disable their webcam when not in use to prevent any unauthorized access or surveillance.

19. Be Wary of Phishing Attempts

Be Wary of Phishing Attempts

Phishing attempts and email scams are prevalent online. Educate your children about the signs of phishing emails, such as suspicious sender addresses, misspelled links, and requests for personal information.

Stress that they should never click on suspicious links or download attachments from unknown senders, as these could contain malware or lead to fraudulent websites.

20. Online Etiquette

Instill good online etiquette in your children. Teach them to be respectful and kind in their online interactions, just as they would be in person.

Explain the importance of avoiding online arguments and cyberbullying, and encourage them to report any inappropriate behavior they encounter online.

Best Parental Control Software Deals

Qustodio
Qustodio
Trusted by over 4 million parents as the all-in-one parental control application
Trusted by over 4 million parents as the all-in-one parental control application Show Less
Kaspersky Safe Kid
Kaspersky Safe Kids
Kaspersky Safe Kids is a parental control app that helps parents monitor and control their child's online activity...Show More
Kaspersky Safe Kids is a parental control app that helps parents monitor and control their child's online activity, including web browsing, app usage, and location tracking. Show Less
Wondershare FamiSafe Parental Control
FamiSafe
This is one of the most reliable parental control apps for controlling screen time, regulating content, and tracking...Show More
This is one of the most reliable parental control apps for controlling screen time, regulating content, and tracking your kids' location in real-time. Show Less
ESET Parental Control
This parental monitoring app allows you to monitor and control your kids' online activity find their location in...Show More
This parental monitoring app allows you to monitor and control your kids' online activity find their location in real-time, and set screentime limits for gaming and other activities. Show Less
Norton Family
Norton Family
Gives your kids free access to the internet while giving you total control over their online activities.
Gives your kids free access to the internet while giving you total control over their online activities. Show Less
mSpy
mSpy
mSpy is a mobile monitoring and tracking software that allows users to monitor the activity on a smartphone or tablet...Show More
mSpy is a mobile monitoring and tracking software that allows users to monitor the activity on a smartphone or tablet, including tracking location, text messages, call history, and social media activity, and in some cases, it can also be used to monitor activities on a computer. Show Less
EyeZy
EyeZy
EyeZy is an advanced parental control software that allows parents to monitor and control their children's internet...Show More
EyeZy is an advanced parental control software that allows parents to monitor and control their children's internet activity, including monitoring their browsing history, blocking websites, setting time limits, and more. Show Less
uMobix
uMobix
uMobix is a phone monitoring app offering features like call tracking, text message spying, and GPS location, raising...Show More
uMobix is a phone monitoring app offering features like call tracking, text message spying, and GPS location, raising privacy concerns despite aiming to help parents monitor children's online activity. Show Less
SpyBubble
SpyBubble
SpyBubble is a phone monitoring app used for parental control, employee monitoring, or catching cheating spouses...Show More
SpyBubble is a phone monitoring app used for parental control, employee monitoring, or catching cheating spouses, raising privacy concerns due to its ability to track calls, messages, location, and more. Show Less

Internet Safety Tips for Different Age Groups:

Age GroupKey ConcernsSafety Tips
7-10 Years OldLimited online experience, susceptible to manipulation* Parental supervision: Use parental controls, monitor activity, discuss online safety rules.

* Focus on fun and learning: Choose age-appropriate websites and games, encourage educational content.

* Privacy and passwords: Teach basic privacy concepts, create strong passwords together.

* Beware of strangers online: Explain the potential dangers of online interactions with strangers.

11-12 Years OldExpanding online presence, increased social media usage* Gradual independence: Allow more online freedom with clear boundaries and expectations.

* Cyberbullying awareness: Discuss cyberbullying risks, empower them to seek help if needed.

* Digital footprint: Explain the lasting impact of online actions and posts.

* Responsible social media: Set appropriate social media guidelines, discuss responsible sharing.

13 Years OldIncreased autonomy, seeking online identity* Open communication: Encourage open and honest conversations about online experiences.

* Critical thinking: Teach them to evaluate online information critically and identify scams.

* Digital reputation: Discuss the importance of maintaining a positive online image.

* Managing emotions: Help them understand and manage online emotions and relationships.

TeensNavigating complex social interactions, exploring adult content* Privacy and boundaries: Respect their privacy, but discuss boundaries and responsible sharing.

* Sexual content and relationships: Discuss online risks associated with sexual content and relationships.

* Balancing online and offline life: Encourage a healthy balance between online and offline activities.

* Mental health: Be aware of potential mental health risks associated with excessive screen time and social media use.

Online Security Tips For Kids – Frequently Asked Questions

Wrapping Up…

By following the online security tips for kids above, you can help to keep your kids safe online. However, it is important to remember that there is no foolproof way to protect your kids from all online dangers.

It is important to talk to your kids about online safety regularly and to monitor their online activity.


RELATED POSTS
What 700 Hacked Fridges Teach About Your Router

0

In this post, I will show you what 700 hacked fridges teach about your router.

On 11 October 2026, someone logged into the refrigeration controllers of up to 700 French supermarkets and switched them to defrost, with the stock still inside. Cabinets that should sit near 4°C climbed towards 50°C. One store in Normandy recorded 80°C. Sprinklers went off, equipment melted, food spoiled, and the bill passed EUR 10 million. On 2 November it happened again, this time in Belgium, Luxembourg, Estonia, the Netherlands, Ireland and Sweden.

No zero-day. No nation-state magic. The controllers ran a small web server so they could be monitored remotely, many still accepted the username admin with a password derived from the current date, and two of the affected families had been end of life since 2016 and 2021. A known vulnerability, a default credential and hardware nobody wanted to replace. If you want the full timeline of both incidents and what the investigators found, the full timeline of the fridge attacks covers the controllers, the credentials and the response.

The interesting part is not the supermarkets. It is that the same three ingredients sit in almost every home in Britain.

The attack was boring on purpose

Danfoss published an advisory in March 2025 and a fix in August 2025. Claroty had documented the flaw earlier that year. The controllers were reachable from the public internet because remote monitoring was sold as a feature, not an accident. Nobody patched, nobody retired the hardware, and a year later a stranger was turning supermarket freezers into heaters.

That is the pattern behind most successful intrusions, and it has nothing to do with sophistication. It is convenience left switched on, plus a device that outlived its support window.

Your home has the same shape, only smaller

The 2026 IoT Security Landscape Report, published by Bitdefender and NETGEAR on 28 October 2026, looked at telemetry from roughly 10.4 million smart homes between January and September. It analysed 5.4 billion security events and 1.2 billion vulnerability observations. The average connected home now runs 24 internet-capable devices, up from 22 a year earlier.

The router is the one device every other gadget trusts

Three numbers from that report matter more than the rest. Reconnaissance accounted for 90.1% of detected attack activity, which means most traffic hitting a home network is automated scanning for weak spots. Smart TVs, smart plugs and network attached storage produced 67.1% of vulnerability observations, and those are exactly the devices people buy once and never think about again. And 99.97% of the observed vulnerabilities were publicly known CVEs. Almost nothing arriving at a home network is exotic. It is old and unpatched.

The router is the supermarket controller

A domestic fridge usually talks to a vendor cloud and sits behind your router, so the appliance itself is one step removed from the internet. The router is not. It is the front door, the DNS server, the firewall and the device that decides which gadget may talk to which.
When a router falls, the symptoms are quiet. Someone changes the DNS server and you land on a convincing copy of your bank’s login page while the address bar looks right. Someone enables remote management and now the admin panel answers from the internet. Someone maps a port with UPnP and an always-on device becomes reachable. None of this breaks your connection, which is why people notice months later, or never.

Remote administration is convenient until it is the way in

Botnets do not disappear, they rebuild

Cloudflare’s Q3 2026 DDoS report counted 18.2 million network-layer attacks in the quarter, roughly 8,226 every hour. Law enforcement dismantled four of the largest IoT botnets, Aisuru, KimWolf, JackSkid and Mossad, and hyper-volumetric attacks above 1 Tbps fell by nearly 69% as a result. New variants such as Dysphoria are already filling the gap.

The pool those botnets recruit from is the same pool the supermarket controllers came from, and it is the pool your fridge, television and vacuum cleaner sit in. Nothing about the next campaign requires a new technique.

Five checks worth doing this weekend

  1. Change the router admin password, not just the WiFi password. They are different logins, and most people never touch the first one.
  2. Turn off remote administration. Look for remote management, cloud management or web access from WAN, and disable it if you do not actively use it.
  3. Move to WPA3 and switch WPS off. The WPS PIN is brute-forceable, and convenience is not worth an open door.
  4. Put smart devices on a separate network. Most ISP routers offer a guest network with client isolation. Fridges, plugs, cameras and televisions belong there.
  5. Patch the router firmware, then replace the hardware when support ends. An end-of-life router is the domestic version of a 2016 refrigeration controller.

The UK already requires more than it did. Since 29 April 2024, the Product Security and Telecommunications Infrastructure Act has banned easily guessable universal default passwords on consumer-connectable products, required a published vulnerability-reporting route, and demanded transparency about support periods, with penalties of up to GBP 10 million or 4% of worldwide turnover.

That raises the floor for new hardware. It does nothing for the devices already on your shelf, and it does nothing for a router that was installed in 2019 and has never been updated. The French supermarkets had a public advisory and more than a year to act. Their freezers still ended up at 80°C.

Your kitchen is smaller. The mechanics are the same.


INTERESTING POSTS