Home Blog Page 46

Corporate OSINT for Defensive Exposure Management: Mapping Public Attack Surface Before Adversaries Do

0
Corporate OSINT for Defensive Exposure Management: Mapping Public Attack Surface Before Adversaries Do

In this post, I will discuss about corporate OSINT for defensive exposure management and reveal mapping public attack surface before adversaries do.

Modern attack surface management is no longer limited to ports, banners, and internet-facing servers. For many organizations, the most useful information available to an adversary is not a vulnerable service at all. It is the public context around the business: domains, identity providers, cloud services, job posts, repositories, documents, suppliers, email patterns, certificates, and forgotten SaaS integrations.

That is why corporate OSINT should be treated as a defensive exposure-management discipline, not just a reconnaissance phase. The goal is simple: understand what an outside observer can infer about your organization before an attacker turns those clues into a targeted campaign.

This guide is written for security teams that want a practical, repeatable, and ethical way to map public exposure and convert findings into remediation work.

Why Corporate OSINT Matters

A mature attacker does not look at a company as a list of IP addresses. They look at it as a graph of trust relationships: people, applications, domains, vendors, cloud assets, login portals, repositories, documentation, and business processes.

A single public signal may not be dangerous by itself. A job post mentioning Kubernetes is normal. A certificate for `vpn.company.com` is normal. A GitHub repository with deployment scripts may be normal. A PDF with department names may be normal.

The risk appears when those signals are correlated.

For example, an attacker may combine:

  • certificate transparency logs showing old subdomains;
  • job posts revealing cloud and CI/CD tooling;
  • public repositories exposing naming conventions;
  • LinkedIn profiles identifying DevOps and cloud administrators;
  • DNS records showing SaaS providers and email infrastructure;
  • public documents revealing internal terminology and suppliers.

Together, those clues reduce uncertainty. The attacker can build better wordlists, select better targets, craft more convincing pretexts, and avoid noisy scanning. Defensive teams should perform the same analysis first, under authorization, and use the results to reduce exposure.

Start With an Exposure Graph
Start With an Exposure Graph

A useful corporate OSINT program starts by mapping relationships, not collecting random artifacts.

Think in terms of nodes and edges:

  • Nodes: domains, subdomains, IPs, certificates, repositories, SaaS tenants, login portals, vendors, people, email formats, documents, APIs, mobile apps, package names, cloud resources.
  • Edges: resolves to, belongs to, authenticates with, mentions, integrates with, was created by, uses the same naming pattern, appears in the same business process.

This graph mindset matters because many exposures are only meaningful in context. A dangling CNAME is one issue. A dangling CNAME under a trusted brand domain, referenced by old documentation, and connected to an authentication callback is much more serious.

For teams building their first workflow, a lightweight spreadsheet or graph database is enough. The important part is to record the evidence, source, confidence level, owner, and remediation status.

Key Sources to Review

1. DNS, MX, SPF, DKIM, and DMARC

DNS records reveal more than routing information. MX records identify mail providers. SPF records can reveal third-party senders. TXT records often expose SaaS verification entries for platforms such as Microsoft 365, Google Workspace, Atlassian, GitHub, Slack, Zendesk, HubSpot, Webflow, Vercel, and other tools.

Defensive questions:

  • Are all authorized mail senders still valid?
  • Is DMARC progressing toward enforcement?
  • Are old SaaS verification records still needed?
  • Do DNS records point to services that no longer exist?

2. Certificate Transparency Logs

Certificate Transparency logs are a historical map of public hostnames. They may reveal staging environments, retired systems, regional naming conventions, VPN portals, API gateways, legacy applications, and development patterns.

Useful review points:

  • subdomains containing `dev`, `stage`, `test`, `preview`, `old`, `vpn`, `sso`, `adfs`, `jira`, `git`, `jenkins`, `grafana`, or `api`;
  • hostnames that no longer resolve but reveal internal vocabulary;
  • recently issued certificates that indicate new projects;
  • wildcard certificates that expand the possible naming space.

3. Public Repositories and Packages

GitHub, GitLab, Docker registries, npm, PyPI, container images, and public package metadata can reveal build systems, dependencies, internal naming conventions, scripts, API paths, and sometimes secrets.

Security teams should not stop at secret scanning. Even when no credential is exposed, repository structure can reveal how software reaches production. That context can help an attacker design supply-chain scenarios or craft realistic social engineering.

4. Job Posts and Professional Profiles

Hiring pages and professional profiles often reveal the technologies that matter inside the organization: identity platforms, EDR, cloud providers, CI/CD systems, SIEM tools, programming languages, monitoring stacks, and business-critical applications.

The defensive goal is not to hide every technology. That is unrealistic. The goal is to avoid unnecessary operational detail and to understand which public statements make targeting easier.

5. Public Documents and Metadata

PDFs, presentations, proposals, manuals, and public reports can expose usernames, author names, department structures, document paths, software versions, internal project names, suppliers, and approval workflows.

A good publication-review process should sanitize metadata and assess whether the content reveals sensitive operational context.

Convert Findings Into Confidence Levels

Not every OSINT finding is a vulnerability. Treat each observation as a hypothesis until validated.

A simple confidence model works well:

  • Low confidence: one old or ambiguous source.
  • Medium confidence: two independent sources suggesting the same pattern.
  • High confidence: current technical evidence, such as an active login portal or live DNS record.
  • Critical: confirmed exploitable exposure, such as a takeoverable subdomain, exposed token, public storage bucket, or misconfigured authentication flow.

This prevents teams from overreacting to weak signals while still prioritizing evidence-backed issues.

Defensive Controls That Reduce OSINT Risk
Defensive Controls That Reduce OSINT Risk

Corporate OSINT findings should lead to process improvements, not just one-off cleanup tickets. Practical controls include:

  • continuous external asset inventory;
  • DNS ownership and lifecycle management;
  • monitoring for dangling CNAMEs and abandoned SaaS resources;
  • DMARC, SPF, and DKIM alignment with a plan for enforcement;
  • secret scanning across repositories, forks, and package registries;
  • metadata sanitization before publishing documents;
  • review of job descriptions for unnecessary operational detail;
  • SaaS inventory and OAuth app review;
  • phishing-resistant MFA for high-value roles;
  • alerting for low-volume login attempts against executives, help desk, cloud administrators, and DevOps users;
  • regular review of public documentation, mobile apps, API docs, and support portals.

The key is continuity. A yearly OSINT report becomes stale quickly. Public exposure changes whenever a new SaaS tool is adopted, a certificate is issued, a marketing page is launched, a repository is published, or a vendor is onboarded.

A Practical How-To Workflow

A simple defensive workflow can be implemented in five steps:

  1. Collect: Gather public data from DNS, CT logs, repositories, documents, job posts, SaaS records, app stores, and public APIs.
  2. Normalize: Convert findings into consistent entities: domains, people, vendors, applications, technologies, identities, and documents.
  3. Correlate: Link related entities and look for patterns, abandoned resources, repeated naming conventions, and high-value identities.
  4. Validate: Confirm whether each finding is current, relevant, and exploitable under authorized scope.
  5. Remediate and monitor: Assign owners, fix root causes, and continue watching for new exposure.

Teams that need a starting template can use a practical corporate OSINT checklist and adapt it to their own asset inventory, identity stack, and cloud environment.

Ethical Boundaries

Corporate OSINT must be performed with authorization and clear scope. Defensive teams should avoid intrusive testing, credential attacks, employee targeting, or interaction with third-party systems unless explicitly approved.

A safe internal program should define:

  • approved domains, subsidiaries, and brands;
  • allowed sources and collection methods;
  • rules for handling personal data;
  • escalation paths for critical exposures;
  • restrictions around suppliers and employees;
  • reporting format and evidence retention.

The objective is not to simulate harm. The objective is to reduce the attacker’s informational advantage.

Final Thoughts

Corporate OSINT is powerful because it shows how much an attacker can learn before sending a packet to your infrastructure. In modern environments, the public attack surface includes identity, cloud, SaaS, software supply chain, documentation, vendors, and people.

Security teams that continuously map those signals gain a practical advantage. They can remove abandoned assets, harden identity controls, reduce spoofing risk, improve publication hygiene, and detect targeted activity earlier.

The best question to ask is not simply, “What do we expose?”

The better question is: “What can an adversary infer from what we expose, and how do we reduce the value of those inferences?”


INTERESTING POSTS

Why Your PC Feels Slower and Sketchier Than It Did Two Years Ago

0
Why Your PC Feels Slower and Sketchier Than It Did Two Years Ago

In this post, I will talk about why your PC feels slower and sketchier than it did two years ago.

You didn’t do anything different. You haven’t changed how you use your computer. But somewhere along the way, things got worse. It takes longer to start up. Popups appear from applications you don’t remember installing. Your browser occasionally redirects you somewhere you didn’t ask to go. Searches that used to be instant now have a noticeable lag.

Most people notice this and assume it’s just what happens to computers over time — a kind of inevitable decay. Some of it is. But a lot of it isn’t, and the causes are more specific than “it’s getting old.”

Understanding what’s actually happening is the first step to fixing it.

What’s Actually Going On

There are a few distinct things that tend to accumulate on a Windows PC over time, each with a different cause and a different fix.

Startup programs that weren’t there before. Every application you install asks, somewhere in the process, whether it can start automatically when your computer turns on. Most people click through installation screens without reading them, and the default answer is usually yes. Over a year or two of installing software, the list of programs launching at startup grows — each one consuming memory and processing power before you’ve opened a single window. A computer that used to be ready in thirty seconds now takes two minutes, and you’re not sure why.

Software you don’t remember installing. Free software often comes bundled with things you didn’t explicitly choose. A PDF reader comes with a browser toolbar. A video player comes with a “system optimiser.” A game launcher comes with an update manager that runs in the background indefinitely. These aren’t viruses in the traditional sense, but they’re not things you wanted either — and they add up.

Actual malware. Sometimes something genuinely harmful gets through. Drive-by downloads from sites that serve malicious ads, fake update prompts that install something when you click them, email attachments that looked plausible. Modern malware is often designed to be invisible — it’s not trying to crash your computer, it’s trying to run quietly in the background, using your connection or your processor for purposes you’re unaware of, while everything on the surface looks normal. You’d only know it was there if you looked deliberately.

Browser behaviour changes. If your default search engine changed without you changing it, if new toolbars appeared, if pages load with more ads than they used to — these are signs that something has been modifying your browser settings. This is one of the more visible symptoms, which is why people notice it but often don’t know what caused it.

Why It’s Hard to Notice Until It’s Bad

The frustrating thing about most of these problems is that they accumulate gradually. No single installation makes your computer noticeably slower. The startup program list grows by one. Then another. Then another. By the time the slowdown is obvious, it’s been building for months, and there’s no single moment you can point to.

This is why most people don’t catch these things early. There’s no alert, no warning, no moment where the computer says “you now have fourteen programs starting automatically.” It just gets slower, and you adjust.

The same is true for malware. By the time you notice something is wrong, it’s often been running for weeks.

Why One Tool That Does All Three Makes Sense

Why One Tool That Does All Three Makes Sense

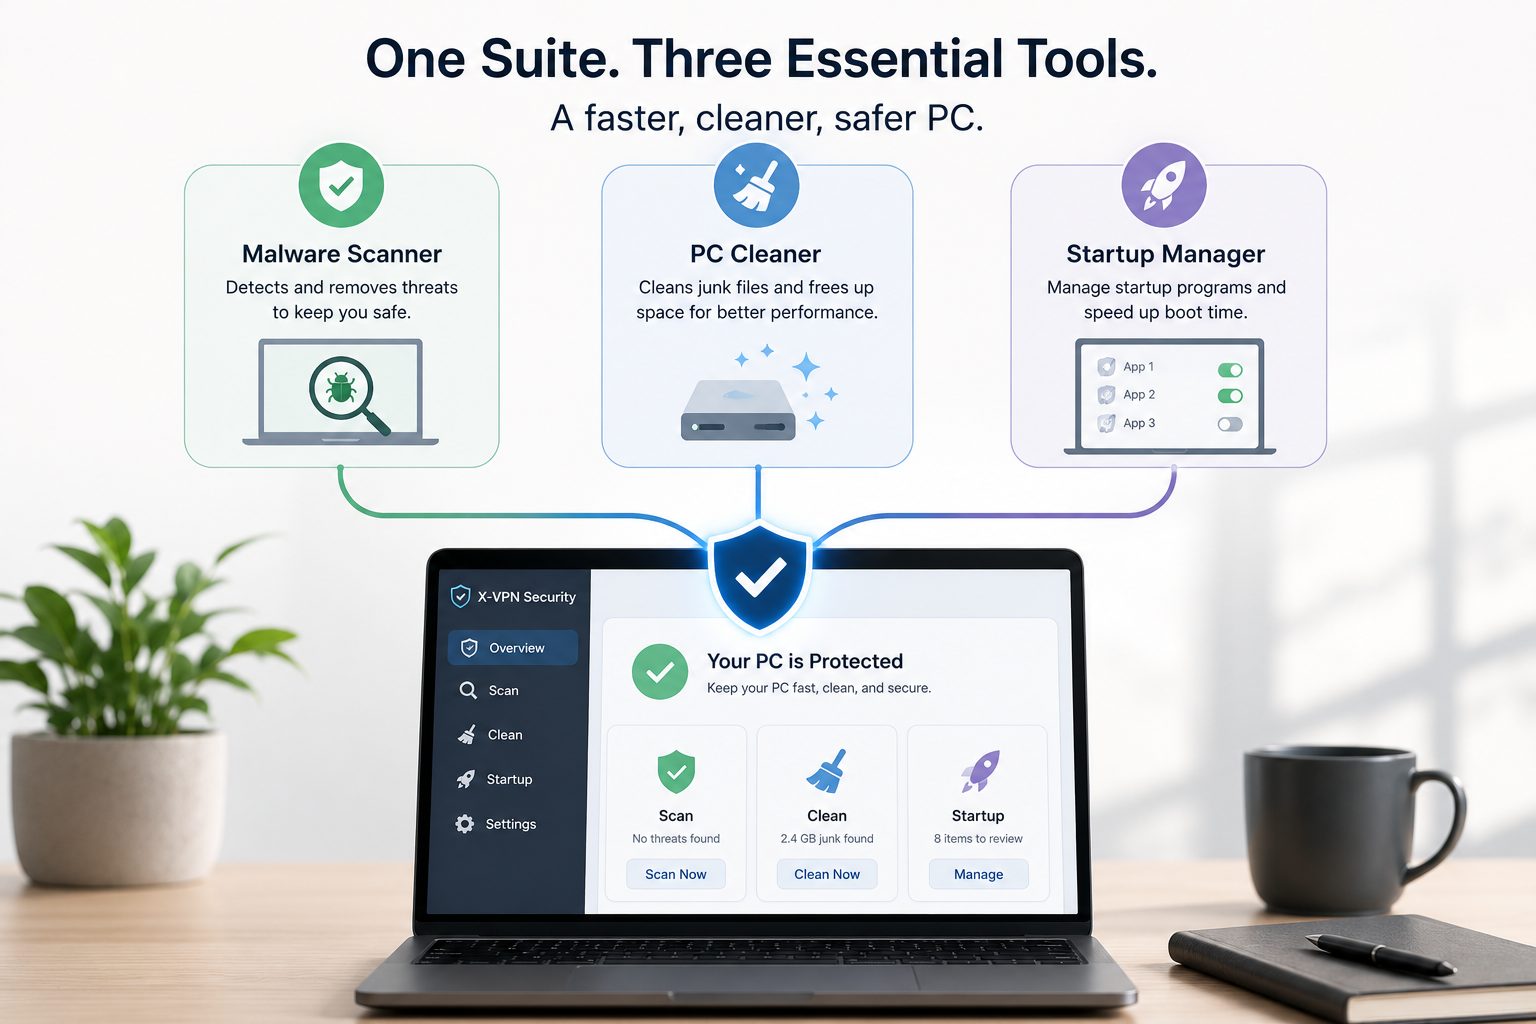
Addressing these problems properly involves three distinct tasks, which is why people often end up with three separate tools: an antivirus for malware, a system cleaner for accumulated junk, and a startup manager to see and control what’s launching automatically.

A computer security suite brings these together. X-VPN’s desktop security offering bundles a malware scanner, a PC cleaner, and a startup manager alongside the VPN — which means the things most likely to be causing your computer’s problems can be addressed from one place, without downloading and managing three separate applications.

For most home users and small business owners without dedicated IT support, having these tools in one place is more than a convenience. It simplifies a process that would otherwise involve researching which tools to trust, finding them, and keeping them updated separately.

Where to Download It: The Case for the Microsoft Store

There’s a practical reason to care about where you download security software. Search for “PC cleaner” or “malware scanner” and you’ll find a mix of legitimate tools and convincing fakes — and the difference isn’t always obvious from a website or an ad. Fake “system optimiser” downloads are, in fact, one of the more common ways malware ends up on computers in the first place.

Installing from the Microsoft Store removes most of that uncertainty. Apps in the Store go through a review process, are associated with verified publisher accounts, and can’t request the kind of system access that would make a malicious app dangerous. For someone who isn’t sure which download source to trust, it’s the lowest-risk route.

X-VPN’s full security suite — including the VPN, malware scanner, and PC cleaning tools — is available on the Microsoft Store, which means the install process is the same as any other Store app: straightforward, verified, and without the need to judge the safety of a third-party download link.

The Practical Upshot

If your computer has been getting slower, producing unexpected popups, or behaving in ways you can’t explain, the cause is more likely software clutter or something running in the background than hardware failure. Running a proper scan and clearing out startup bloat typically makes a more noticeable difference than people expect — and it’s worth trying before assuming the situation is unfixable.

The problems described in this article are fixable. They just require the right tools, from a source you can trust.


INTERESTING POSTS

Practical Event Handouts That People Actually Keep

0
Practical Event Handouts That People Actually Keep

In this post, I will talk about the practical event handouts that people actually keep.

When businesses plan trade shows, local fairs, campus events, or community campaigns, printed handouts are often treated as a routine box to tick. Flyers get stacked on tables, brochures are skimmed and forgotten, and many giveaway items end up in the nearest bin before the day is over.

That does not mean physical marketing has lost its value. It usually means the item was not useful enough to earn a place in someone’s day-to-day life.

The most effective event materials tend to do two things at once. They communicate a brand message, and they solve a small practical need. When that balance is right, a handout can keep working long after the event ends.

Why usefulness matters more than volume

It is easy to assume that success comes from giving away as many items as possible. In practice, distribution numbers do not always tell the full story.

A business might hand out 2,000 leaflets in one afternoon and still see little response. Another might give away a smaller number of practical branded items that remain in offices, cars, kitchens, or shopping bags for months.

People keep things that fit naturally into their routines. A good event handout should feel less like clutter and more like something worth using again.

This is especially important for small and mid-sized businesses with limited marketing budgets. Instead of spreading resources across too many low-impact materials, it often makes more sense to invest in fewer items with a longer lifespan.

Common event materials that lose attention quickly

Some printed materials still have a place. A clear brochure can be useful when a buyer needs details. A postcard can support a limited-time promotion. A well-designed one-sheet can help explain a service at a booth.

Still, many businesses rely too heavily on materials that require immediate attention.

That creates a problem in busy event settings. Attendees are usually juggling conversations, schedules, and bags full of mixed materials. If something is not immediately relevant, it often gets ignored.

Items that tend to disappear quickly include:

  • Generic flyers with too much text
  • Discount cards without context
  • Thin paper handouts with no practical value
  • Novelty giveaways that break or wear out quickly

None of these are automatically ineffective. But they often struggle in crowded environments where people are making quick decisions about what to keep.

Practical branded items create longer exposure

Useful merchandise stands out because it stays with the recipient beyond the event itself. That continued use creates repeat exposure without demanding attention all at once.

For example, a notebook may remain on a desk for weeks. A reusable water bottle might travel between home and work. A durable shopping tote can be used for groceries, library visits, or everyday errands.

This repeated visibility can be especially valuable for organizations that depend on local recognition, seasonal foot traffic, or event-based networking.

Businesses exploring custom printed tote bags often use them at conferences, retail promotions, school events, and charity programs because they combine branding with a practical purpose people already understand, with suppliers such as toteprint.com often used for sourcing custom production options. 

The key is not simply putting a logo on an item. It is choosing something that matches the setting and the audience.

Matching the handout to the event

Not every event calls for the same approach. A handout that works well at a university open day may not be right for a hospitality expo or a neighborhood fundraiser.

Before ordering any printed material, it helps to ask a few simple questions:

  • What is the attendee likely carrying already?
  • Will they need something useful during or after the event?
  • Is the audience more likely to value information, convenience, or durability?
  • Does the item fit the brand without feeling forced?

At a trade show, for example, attendees often collect catalogs, business cards, and samples. A durable tote is practical because it helps carry other materials while also extending the brand’s presence after the event.

At a community health fair, simple printed guides may work better if they address specific concerns and are easy to reference later.

At a retail launch, a reusable bag can tie directly into the shopping experience and feel like part of the visit rather than a separate promotion.

Design choices that make a difference

A practical item can still fall short if the design feels overly crowded or disconnected from the brand.

The strongest event materials usually share a few characteristics. They are easy to understand, visually clean, and built around one clear message.

For printed merchandise, that may mean:

  • A simple logo placement
  • Readable typography
  • Limited color use that supports brand recognition
  • A short phrase or visual element that fits the audience
  • Material choices that support repeated use

Restraint often works better than trying to include every detail. If an item feels too promotional, people may be less likely to use it in public.

This is one reason subtle branding can outperform louder designs. A well-made item with a clear visual identity often gets more real-world use than one covered in oversized slogans and contact details.

Thinking beyond the event table

A useful handout should not be treated as a one-day tactic. It can be part of a broader customer experience.

For example, a local retailer might include reusable bags during a store opening, then use the same design language on packaging and in-store signage. A nonprofit may hand out practical items at a fundraiser and later feature them again in volunteer kits. A school program might distribute bags during orientation and continue using them for future campus activities.

This kind of consistency helps printed materials feel intentional. It also makes branding more memorable because people encounter it in multiple settings rather than only once.

Physical materials can support digital follow-up too. A clean design, short URL, or simple call to learn more can create a bridge between the in-person interaction and later action, without overwhelming the item itself.

Small decisions can improve results

Businesses do not always need a major event budget to create something worthwhile. Often, the impact comes from practical decisions made early.

That includes choosing the right quantity, using better materials, simplifying the design, and focusing on usefulness rather than novelty.

It can also help to observe what people do at live events. Which items do they reach for first? What gets left behind on tables? What do they keep carrying as they move through the venue?

These small observations reveal a lot about what audiences actually value.

When teams look at event materials through that lens, they often move away from disposable handouts and toward items with a clearer purpose.

Conclusion

Printed event materials still matter, but people are more selective about what they keep. That makes usefulness one of the most important factors in any handout strategy.

When a branded item serves a real purpose, it has a better chance of staying in circulation and keeping the business visible in an ordinary, low-pressure way.

For companies planning conferences, promotions, school events, or local campaigns, the goal should not be to hand out more things. It should be to choose materials that people are genuinely willing to use. That is what gives a printed item the chance to last beyond the event itself.


INTERESTING POSTS

Nano Banana Review: Features, Benefits, and User Experience

0
Nano Banana Review: Features, Benefits, and User Experience

In this post, I will give you the Nano Banana review and disclose its features, benefits, and user experience.

Artificial intelligence is transforming the digital creative industry faster than ever before. From AI-powered writing assistants to automated video generation platforms, creators now have access to tools that simplify complex creative tasks. One of the most interesting developments in this space is the rise of AI image generators, which allow users to create visuals from simple text prompts. Among these emerging platforms, Nano Banana has started gaining attention for its approach to AI-powered visual content creation.

This nano banana review explores the platform’s features, usability, speed, creative potential, and overall user experience. Whether you are a designer, marketer, content creator, or someone exploring AI creative tools for the first time, understanding how Nano Banana works can help you decide if it fits your workflow.

What Is Nano Banana?

Nano Banana is an AI image generator designed to help users create digital visuals using artificial intelligence. Instead of relying on traditional graphic design software that often requires advanced technical skills, Nano Banana simplifies the process by allowing users to generate images through descriptive text prompts.

The platform falls into the growing category of visual content AI systems that automate parts of the creative workflow. Users can describe scenes, art styles, lighting, themes, or concepts, and the AI produces visual outputs based on those instructions.

Modern AI design platforms like Nano Banana are becoming increasingly popular because they save time, reduce production costs, and make content creation accessible to a wider audience.

The Rise of AI Image Generators

Before diving deeper into this nano banana review, it is important to understand why AI image tools are becoming so popular.

Visual content has become one of the most important parts of digital communication. Businesses need graphics for advertising, creators need social media visuals, bloggers need featured images, and marketers constantly require fresh content for campaigns.

Traditional design workflows often involve:

  • Professional software
  • Editing skills
  • Long production times
  • Expensive creative resources

AI image generators reduce many of these barriers by automating image creation using machine learning technology. This is one reason why AI creative tools are growing rapidly across industries.

Nano Banana Interface and User Experience

One of the strongest aspects of Nano Banana is its relatively simple and beginner-friendly interface.

Many users avoid advanced design software because of the steep learning curve. Nano Banana focuses on accessibility by providing a cleaner workflow that allows users to focus on creativity rather than technical setup.

Dashboard Simplicity

The platform interface appears designed for ease of use. Most actions revolve around:

  • Entering prompts
  • Selecting image styles
  • Generating visuals
  • Refining outputs

This straightforward structure helps beginners get started quickly while still giving experienced creators enough flexibility for experimentation.

Prompt-Based Workflow

Like many modern AI design platforms, Nano Banana relies heavily on prompt engineering. Users describe the image they want, and the AI generates visuals accordingly.

For example:

  • “Cyberpunk city street at night”
  • “Minimalist workspace with futuristic gadgets”
  • “Realistic mountain landscape during sunset”

The prompt-based system encourages creative exploration and experimentation.

Nano Banana Features

This nano banana review would not be complete without discussing the platform’s major features.

AI Image Generation

The core feature of Nano Banana is AI-powered image creation. Users can generate visuals across different styles and concepts without manually designing every element.

This makes the platform useful for:

  • Social media content
  • Marketing graphics
  • Blog visuals
  • Concept art
  • Creative projects

Style Flexibility

AI image generators are often judged by their ability to handle multiple artistic styles. Nano Banana appears to support a variety of visual aesthetics, including:

  • Realistic images
  • Digital illustrations
  • Futuristic designs
  • Artistic concepts
  • Minimalist visuals

Style flexibility is important because creators across industries need different types of visual content.

Fast Image Processing

Speed is another key factor in user satisfaction. Many creators need visuals quickly for campaigns, blogs, or content schedules. Nano Banana aims to provide relatively fast generation times, helping users produce multiple concepts efficiently.

In the modern digital environment, rapid content production is becoming increasingly valuable.

Creative Experimentation

One of the biggest benefits of AI creative tools is the ability to experiment rapidly. Users can test multiple prompt variations, compositions, and visual ideas within minutes.

This improves creative exploration and allows creators to iterate faster than traditional design workflows.

Benefits of Using Nano Banana

Improved Productivity

One of the main reasons people adopt AI image generators is productivity. Nano Banana can help users produce visuals much faster compared to manual graphic design processes.

This is especially valuable for:

  • Bloggers
  • Agencies
  • Content marketers
  • Small businesses
  • Freelancers

Lower Design Barriers

Not everyone has professional design experience. Nano Banana lowers technical barriers by making image creation more accessible through natural language prompts.

Content Scalability

Businesses often need large amounts of visual content for websites, advertisements, and social media campaigns. AI-generated visuals help scale content production more efficiently.

Inspiration for Designers

Even professional designers can use Nano Banana as a brainstorming tool for generating concepts, mood boards, or early creative ideas.

Comparing Nano Banana With Modern AI Image Tool Trends

Comparing Nano Banana With Modern AI Image Tool Trends

The AI image generation market has become increasingly competitive. Many AI creative tools now focus on:

  • Better realism
  • Faster rendering
  • Improved prompt understanding
  • Commercial content workflows
  • Multi-style image support

Nano Banana fits into this broader trend of accessible visual content AI platforms aimed at simplifying creativity.

Modern users are no longer looking only for design software. They want intelligent systems that:

  • Speed up workflows
  • Reduce repetitive tasks
  • Generate creative inspiration
  • Improve production efficiency

This shift is changing how creators approach visual production.

Practical Use Cases

Social Media Marketing

Marketers can use Nano Banana to generate graphics for:

  • Instagram posts
  • YouTube thumbnails
  • Facebook ads
  • Pinterest visuals
  • Promotional campaigns

Blogging and Content Websites

Website owners often need featured images and custom illustrations. AI image generators can help create more original visuals instead of relying entirely on stock photography.

Branding Concepts

Startups and creators may use Nano Banana for:

  • Mood boards
  • Creative direction
  • Branding inspiration
  • Visual experimentation

Content Creation

YouTubers, influencers, and digital creators constantly require visual assets. AI design platforms simplify this process significantly.

Pros and Limitations

Pros

  • Beginner-friendly interface
  • Fast image generation
  • Creative flexibility
  • Useful for multiple industries
  • Supports scalable content workflows
  • Encourages creative experimentation

Limitations

  • AI-generated visuals may still require editing
  • Prompt quality strongly affects output quality
  • Complex artistic requirements may need manual refinement
  • AI creativity can sometimes produce inconsistent details

These limitations are common across most modern AI image generators and are part of the evolving nature of machine learning technology.

Is Nano Banana Worth Using?

For creators interested in AI-powered visual workflows, Nano Banana offers several useful advantages. It simplifies image generation, improves production speed, and supports creative experimentation without requiring advanced technical skills.

The platform may be particularly useful for:

  • Content creators
  • Social media marketers
  • Bloggers
  • Freelancers
  • Designers seeking inspiration
  • Businesses scaling visual production

As AI design platforms continue evolving, tools like Nano Banana are becoming part of everyday digital workflows.

Final Thoughts

This nano banana review shows how AI image generators are changing the future of digital creativity. Platforms like Nano Banana help simplify visual production through text-based workflows, allowing creators to generate ideas and graphics faster than traditional methods.

While AI-generated visuals still benefit from human creativity and editing, the technology is improving rapidly. Nano Banana represents part of a larger movement toward more accessible and scalable visual content AI systems.

For creators looking to experiment with AI creative tools, improve content workflows, or generate digital visuals more efficiently, Nano Banana offers an interesting platform worth exploring. Humans spent years mastering advanced design software only to arrive at an era where typing “space banana warrior in neon armor” into a prompt box counts as a creative workflow. Evolution took a strange turn somewhere.

FAQ

What is Nano Banana?

Nano Banana is an AI image generator that allows users to create visuals using text prompts and artificial intelligence technology.

Is Nano Banana beginner-friendly?

Yes, the platform appears designed for both beginners and experienced creators with a relatively simple interface and prompt-based workflow.

What can Nano Banana be used for?

Nano Banana can be used for social media graphics, marketing visuals, blog images, concept art, branding ideas, and creative digital content.

How do AI image generators work?

AI image generators analyze text prompts and create visuals using machine learning models trained on large datasets of images and artistic patterns.

Is Nano Banana suitable for marketers?

Yes, marketers can use Nano Banana for ad creatives, social media campaigns, visual branding, and scalable content production.

Why are AI creative tools becoming popular?

AI creative tools help users save time, reduce costs, improve productivity, and make content creation more accessible without requiring advanced technical skills.


INTERESTING POSTS

From Stadiums to Sofas: How Sports Entertainment is Evolving

0

In this post, I’ll talk about from stadiums to sofas and how sports entertainment is evolving.

Sports entertainment has been around for a while. One can say it’s been around for centuries upon centuries and although sports have changed over the many years we’ve seen on Earth, we are still entertained by people competing against each other.

In the last 50+ years, sports viewing has changed in more ways than one. Mainly, it’s changed with more viewers watching their favorite teams from the comfort of their homes.

While people still go to stadiums when they want a live experience, many people are entertained by sports at home. Here are a few ways that sports entertainment has evolved and is evolving:

When TV first brought us sports

Let us remember when sports “left” the stadiums and showed up in our living rooms. In 1939, a baseball game was aired. Television technology wasn’t like how it would become as years passed, in the 60s, 70s, 80s, and then on to the early 2000s.

But with the arrival of the internet, sports viewing wasn’t only available with a cable setup. With Wi-Fi and advancements in technology came the “blessing” of live streaming and streaming platforms.

Beyond traditional sports

Another aspect of modern technology changing how we view sports is that it also brought new sports to our households, offering us the opportunity to get involved with micro-betting and watching non-traditional sports, even including eSports.

With live stream technology, people are able to enjoy more types of sport like entertainment from the comfort of their homes, making for a unique yet equally enjoyable experience.

From Stadiums to Sofas: How Sports Entertainment is Evolving

Comfortable and affordable viewing

Stadium games are fun, but they are pricey, and people aren’t always in the mood for them. Watching a great game from the comfort of your home can make for a fun time when you’re tired and just want to unwind with your favorite game.

It’s more affordable than a stadium and with streaming platforms, more affordable than cable. Who doesn’t want to catch a game while sitting in their jammies at home while sipping on a hot toddy or cold beer, depending on the season? To find affordable sports streaming, shop around.

There are plenty of platforms offering sports viewing, some providing better visuals and uninterrupted streaming while others offer great features that make for a more immersive experience.

More connection and features

Another reason why sports viewing at home is so appealing in this day and age is the fact that we can enjoy all kinds of features and even get the option of connecting with our favorite sports idols through social media streaming features.

Some streaming platforms go beyond the games themselves, offering a view of behind the scenes, in depth player information, and game analysis. It’s not just about the game anymore. People want a closer glimpse at everything else that goes into the game, including the lifestyle and analytics of the games and sport.

READ ALSO: Spyrix Employee Monitoring Employee: All-In-One Business Solution

View games anytime and anywhere

Obviously, our ability to view sports has improved in more ways than one. We can now view our favorite games at home or away from home. We can watch them on our phones if we like while we wait to board a flight.

The options for sports viewing are endless, making it easier for sports to be seen by more people than ever before and from a broader demographic than they were previously. Fans can stay up to date with games even when they have to be somewhere other than the stadium or their sofa.

In Conclusion

For people who love sports, it’s the best time to be alive. Great sports viewing, at home or at the stadium, is the norm these days. You can view your favorite sport anywhere you want and what could possibly be better than that?


INTERESTING POSTS

How To Remotely Access Corporate Data Securely Without A VPN

0
How To Remotely Access Corporate Data Securely Without A VPN

This post will show how to remotely access corporate data securely without a VPN.

VPNs are one of the most common tools used for remote access. However, they are not the only solution for securely accessing corporate data. The VPN protocol is outdated and can be broken by hackers. And using a VPN is no longer necessary because there are other ways to do so securely.

Remote access to your company’s data is necessary for today’s modern business. With the rise of cloud computing and the expansion of wireless and cellular networks, many organizations now store and process data remotely.

This has changed the way we think about enterprise security. The advent of cloud computing has put more pressure on IT departments to secure data stored off-premises.

Here are some ways to access corporate data remotely without using a VPN.

How To Remotely Access Corporate Data Securely Without A VPN

Remote Access Server

Remote Access Server

Remote access servers are designed to secure the connection between your remote employees and the corporate data center. The most significant benefit of this solution is that the communication between the employee and the server is always encrypted. This reduces the bandwidth employees need to download or upload, making it ideal for mobile workers.

Remote access servers differ from VPNs because the server is not inside the company’s premises. It is situated in the cloud, often in a separate location from the building. Typically, a remote access server is a service offered by a third-party cloud provider.

This approach is one of the best ways to secure remote access without a VPN, since the server never touches a corporate network and is, therefore, safer from attack.

Web Proxy Applications

As an alternative to VPNs, web proxy applications allow companies to mask the locations of their data. The data can then be accessed from any device, including a mobile phone, an IP-enabled TV, or even a personal computer.

A web proxy application works as an encryption layer on top of an internet connection. This acts as a bridge between the user’s data and the server that hosts the data. In other words, the user’s data never connects directly to the server. Instead, it is routed through the web proxy.

The advantage of this solution is that the data doesn’t have to go through the VPN to be accessed. This allows the employee to access and edit corporate data securely from anywhere, without logging into a corporate domain.

READ ALSO: Corporate Anonymity: How Modern Enterprises Obscure Their Digital Tracks from Competitors

Identity and Access Management (IAM)

Identity and Access Management (IAM)

An IAM solution creates a secure access policy, which will be applied to each employee. This way, you can configure access rules for specific employees or locations. Thus, the access policy will never get confused. For example, you can set a time limit for an employee’s access to a particular project or repository.

There is no specific software billed as an IAM, instead it is a suite of tools that enables a company to configure the access policies. The challenge with this method is that the vendor will charge for each employee’s access policy. This can be a barrier to most enterprises’ adoption.

READ ALSO: CCIE Data Center Training

SSH or Secure Shell (SSH)

An SSH connection works similarly to remote access servers. However, the main difference is that an SSH connection is a peer-to-peer system. It makes it impossible for a single user to access the data fully. It’s like the internet, where only a single IP address is allotted per user.

This method is ideal for larger enterprises. Many software vendors are offering this solution. Generally, it is meant to be used by enterprise IT departments, although small businesses can also benefit from it.

Securely Reaching the Office: Remote Data Access Beyond VPNs (FAQs)

While VPNs (Virtual Private Networks) are a popular solution for remote access, they aren’t the only option. Here are some FAQs to explore secure alternatives for accessing corporate data remotely:

Can I access corporate data securely without a VPN?

Yes, there are alternative methods for secure remote access, but they might come with different functionalities and security considerations compared to VPNs. Here are some options:

  • Zero Trust Network Access (ZTNA): ZTNA grants access based on user identity and device verification, providing a more granular security approach than traditional VPNs.
  • Cloud-based applications: Accessing corporate data through secure cloud-based applications eliminates the need for a VPN connection entirely. Data resides in the cloud, and the provider’s security measures control access.
  • Remote Desktop Protocol (RDP) with enhanced security: RDP allows remote access to specific desktops within the corporate network. However, RDP should be coupled with multi-factor authentication and strong password policies for enhanced security.

What factors should I consider when choosing an alternative to VPN?

Here are some key considerations:

  • Security features: Ensure the chosen method employs robust encryption and authentication protocols to protect data in transit and at rest.
  • Ease of use: Consider how user-friendly the solution is for both employees and IT administrators.
  • Scalability: If your organization has a growing remote workforce, choose a scale solution to accommodate future needs.
  • Compliance requirements: Certain industries have data security regulations that might influence the choice of remote access method.

Is remote desktop access (like RDP) secure without a VPN?

RDP itself doesn’t provide the same level of security as a VPN. To enhance RDP security, consider:

  • Multi-factor authentication: Adding an extra layer of verification beyond just a password.
  • Strong password policies: Enforce complex password requirements and regular password changes.
  • Limiting access: Restrict RDP access only to authorized devices and users.
  • Network segmentation: Segregate the RDP environment from the rest of the corporate network for added protection.

Are there any security risks to consider when avoiding VPNs?

While alternatives offer advantages, they might also introduce different security risks:

  • Complexity: Managing and securing some alternatives can be more complex than using a VPN.
  • Vendor dependence: Cloud-based solutions rely on the security practices of the cloud provider.
  • Potential compatibility issues: Some solutions might not work seamlessly with all devices or operating systems.

Conclusion

In conclusion, while VPNs are a standard solution, other methods can provide secure remote access to corporate data.

Carefully consider your organization’s specific needs, security posture, and technical expertise before choosing the most suitable alternative


INTERESTING POSTS

Corporate Anonymity: How Modern Enterprises Obscure Their Digital Tracks from Competitors

0
Corporate Anonymity: How Modern Enterprises Obscure Their Digital Tracks from Competitors

In this post, I will talk about corporate anonymity and show you how modern enterprises obscure their digital tracks from competitors.

Corporate anonymity is not about hiding illegal activity. For many enterprises, it is a practical layer of operational security. Competitive teams monitor hiring pages, ad libraries, public tests, landing pages, app behavior, supplier traces, and traffic patterns. Every visible action can reveal priorities before a product, market entry, or campaign is ready.

Companies in fintech, ad tech, cybersecurity, SaaS, e-commerce, affiliate marketing, and data intelligence face higher exposure because their work depends on online research, testing, automation, and regional checks. Managing the digital footprint in high-risk business operations helps reduce unnecessary signals, protect strategic plans, and keep research activity separated from customer-facing systems.

What Competitors Can Learn From Open Signals

A company may reveal more through routine work than through press releases. New landing pages show target markets. Job posts reveal technology stack and expansion plans. Repeated visits to competitor pages can expose research patterns. Test accounts, tracking tags, browser fingerprints, and IP addresses can connect separate activities to the same organization.

Competitors do not need secret access to build a picture. Public traces can be combined with ad monitoring, WHOIS data, source code snippets, review platforms, social profiles, Git repositories, marketplace listings, and employee updates. The risk grows when every department acts independently without shared security rules.

For modern enterprises, anonymity means reducing predictable links between identity, intent, and action. A company may still act openly where trust matters, such as sales, support, legal, and investor communication. Research, testing, market checks, and sensitive experiments need more separation.

Separating Public Identity From Research Activity

The public side of a company should be controlled and consistent. Domains, official emails, branded social accounts, support channels, and payment details must be easy for customers and partners to verify. Research activity has different needs. It should not expose the same infrastructure, accounts, devices, or traffic routes.

A clean separation plan starts with clear categories. Customer support, sales, finance, product testing, competitor research, ad verification, and public data collection should not share the same browser profiles or network routes. This reduces the chance that one flagged workflow affects another part of the business.

Teams can reduce exposure by reviewing several weak points:

  • shared browsers used for unrelated projects;
  • personal email addresses tied to business testing;
  • repeated logins from the same office IP;
  • test accounts created with visible brand details;
  • public documents containing internal project names;
  • contractor access that remains active after work ends.

These issues are common because they look small during daily work. Fixing them early is easier than cleaning reputation problems after accounts, traffic, or public pages become linked.

Contractor and Vendor Controls

External partners can weaken anonymity without meaning to. Agencies may manage several clients from one dashboard. Contractors may reuse browser profiles. Vendors may access sensitive platforms from shared devices. These habits can connect unrelated brands, campaigns, and traffic patterns.

Enterprise teams should define access rules before a partner starts work. Credentials, allowed tools, approved networks, and data handling requirements should be written into the workflow. Temporary access should expire automatically or be reviewed after each project.

A practical vendor policy should cover:

  • dedicated accounts for each project;
  • restricted access to only needed tools;
  • approved login methods and two-factor authentication;
  • no storage of credentials in private files;
  • no mixing of client work in one browser profile;
  • access removal after project completion.

These rules protect both sides. Partners get clear boundaries, and the company keeps better control over its digital presence.

Choosing Tools for Controlled Anonymity

The right toolset depends on risk level, team size, and daily operations. Small teams may need a password manager, separate browser profiles, basic device rules, and clean proxy routing. Larger enterprises may need role-based access, detailed logging, secure workspaces, mobile and residential IP coverage, and approval flows for sensitive actions.

Good tools should give control without making normal work difficult. If security steps are too complex, teams will create shortcuts. The best setup gives employees clear options for each task: which account to use, which network route to select, where to store credentials, and who can approve exceptions.

Corporate anonymity is a practical discipline for companies that operate in competitive or regulated niches. It does not replace legal transparency, customer trust, or responsible data use. It reduces avoidable exposure during research, testing, market entry, and product development.

Enterprises that manage accounts, devices, IP routes, vendors, and public materials with care can work with less noise and fewer unwanted links between activities. The business stays visible where credibility matters, while sensitive workflows remain controlled, separated, and harder for competitors to map.


INTERESTING POSTS

Common Privacy Mistakes That Expose Your Real IP Address

0
Common Privacy Mistakes That Expose Your Real IP Address

What mistakes most often expose a user’s real IP address and why a VPN alone is not always enough for privacy protection.

Why Your IP Address Matters for Online Privacy

Online privacy is no longer a topic only for cybersecurity specialists. Today, marketers, researchers, automation teams, online businesses, and regular users all face data protection issues.

At the same time, many people still believe that incognito mode or a VPN is enough for complete protection. In practice, a real IP address can still be exposed even when additional security tools are used.

Using Public Wi-Fi Networks

One of the most common mistakes is using public Wi-Fi networks without additional protection. In cafes, airports, and coworking spaces, internet traffic is often less secure than it appears. Even when using HTTPS, some technical connection data may still remain visible for analysis.

DNS Leaks and Request Exposure

Another common issue is DNS leaks. A user hides their IP through a VPN or proxy, but DNS requests still pass through the local internet provider. As a result, websites and services may still receive part of the real connection information.

Browser Fingerprinting and Digital Profiles

Many users also underestimate browser fingerprinting. Modern platforms analyze not only IP addresses, but also browser settings, system language, screen resolution, timezone, installed fonts, and other technical parameters. Together, they create a unique digital profile of the user.

How WebRTC Can Expose an IP Address

How WebRTC Can Expose an IP Address

A separate issue is related to WebRTC. This technology is used for video calls and voice communication in browsers, but incorrect settings may expose a local or real IP address even when a VPN connection is active.

Why Using One IP for All Tasks Is Risky

Another common mistake is using one IP address for all tasks and accounts. When multiple sessions operate through the same IP, platforms can more easily connect activity between them. This is especially important for teams working with analytics, automation, testing, or large online infrastructures.

To reduce such risks, companies often separate traffic between different connection types. For example, ISP proxies are commonly used for long stable sessions, while residential pools are used for distributed requests across different regions.

The Role of Proxy Infrastructure in Privacy Protection

In addition to the IP itself, infrastructure quality also matters. Unstable connections, overloaded networks, and frequently reused IP addresses are quickly detected by modern monitoring systems.

For this reason, many teams use proxy infrastructure with HTTP and SOCKS5 support, API access, and IP addresses from multiple regions. For example, MangoProxy provides residential, ISP, mobile, and datacenter proxy solutions for tasks where stable connections and traffic distribution are important. MangoProxy also offers the promo code SECUREBLITZ for an 8% discount on static ISP proxies.

Common Privacy Configuration Mistakes

Users often enable a VPN but forget to check for DNS and WebRTC leaks, continue using the same browser profile for different tasks, or work through unstable public Wi-Fi networks. As a result, some connection data may still become visible to platforms and online services.

Why IP Stability Matters

For long-term sessions and multi-account workflows, not only the IP geolocation matters, but also connection stability. Frequent IP changes or unstable networks may trigger additional checks from online platforms and monitoring systems.

Conclusion

Completely hiding a digital footprint is almost impossible today. However, most IP exposure problems are caused not by sophisticated attacks, but by basic configuration mistakes and lack of attention to technical details.

Regular DNS and WebRTC leak checks, proper session separation, careful browser profile management, and stable network infrastructure can significantly reduce the risks of exposing a real IP address and improve online privacy.

FAQ

Can a VPN fully hide a real IP address?

Not always. Incorrect settings may still expose an IP address through DNS leaks, WebRTC, or browser-related issues.

What is browser fingerprinting?

It is a technology that allows websites to analyze device and browser parameters in order to create a digital profile of a user.

Why is using one IP for all tasks not recommended?

Using one IP address makes it easier to connect activity between different accounts and sessions.

What are ISP and residential proxies used for?

ISP proxies are commonly used for stable long-term sessions, while residential proxies are often used for distributed requests and work across different geographic regions.


INTERESTING POSTS

Solana vs Base Copy Trading: Which Chain Executes Faster in 2026?

0
Solana vs Base Copy Trading Which Chain Executes Faster in 2026

In this post, I will discuss Solana vs Base copy trading and tell you which chain executes faster in 2026?

Block timing determines whether your copy trade lands before the market moves, or after. Solana processes transactions inside ~400ms slot windows, using Jito-based MEV protection to compete for block inclusion. Base, built on Ethereum’s L2 stack, takes a different approach: it splits each ~2-second block into ten ~200ms preconfirmation sub-blocks called Flashblocks, which lets copy trades target block 0 confirmation before the full block settles. The mechanics are genuinely different, and choosing the wrong chain for your copy-trading strategy costs real money.

This breakdown covers how each chain’s execution model works in practice, what DEXes are in scope on each side, and how Banana Gun Pro runs both chains inside a single interface without asking you to switch bots or wallets.

How Solana Handles Copy Trade Execution

Solana produces a new block roughly every 400 milliseconds. That slot time is fast compared to most chains, but it still means your copy trade competes inside that window against every other transaction trying to confirm at the same moment. The determining factor is MEV tip: a higher tip increases the probability that Jito’s block-building infrastructure includes your transaction in the next slot rather than a later one.

On Solana, copy trading routes through Raydium AMM, Raydium CP, Raydium CLMM, Orca, Meteora Dynamic, Meteora DLMM, Pump.fun, and Pump AMM. Sniping is restricted to Raydium AMM and Raydium CP only, which matters if you want to combine copy trading with snipe mechanics on the same setup. The MEV tip parameter is directly configurable in the copy trade settings, so you can tune the aggressiveness of your block-inclusion bids without touching anything else.

Jito’s architecture also provides MEV protection on the buy side, which reduces exposure to sandwich attacks that Solana’s mempool structure would otherwise create. For copy traders targeting high-volume memecoins on Pump.fun or Raydium launches, that protection is worth understanding before you start.

How Base Handles Copy Trade Execution with Flashblocks

Base Flashblocks change the 2-second finality picture significantly. According to Base’s official Flashblocks documentation, the protocol is a preconfirmation feature built into the Base sequencer: it divides each ~2-second block into ten sub-blocks, each carrying a ~200ms preconfirmation window. Base produces about 10 Flashblock sub-blocks per ~2-second block (2,000ms / 200ms), which means a copy trade set to target block 0 on Base lands inside the first available sub-block before the parent block finalizes and before most other traders are aware the target transaction exists. The correct framing is that the ~200ms figure describes sub-block granularity, not a guaranteed execution latency for your trade. What it means in practice is that Banana Gun Pro’s block 0 copy trading on Base puts your transaction at the front of the confirmation queue within the Flashblock architecture, a structural position that is categorically different from simply having a fast chain. That advantage compounds on high-volume Base DEXes where competition for block 0 inclusion is meaningful.

Base DEXes in scope for copy trading include Uniswap v2 and v3, Sushiswap v2 and v3, Baseswap v2 and v3, Aerodrome, and Pancakeswap v2 and v3. Because Base is an EVM chain, there are no sniping-DEX restrictions analogous to Solana’s Raydium-only limitation. You can copy-trade across all supported Base DEXes without a separate configuration for sniping targets.

A broader look at how copy trading operates across five chains, including block time comparisons and MEV mechanics, is covered in detail on the Banana Gun blog.

Copy Trade Configuration: What You Actually Set Up

Copy Trade Configuration: What You Actually Set Up

The configuration experience is identical whether you are on Solana or Base, which is worth stating plainly because most multi-chain tools force you to relearn the interface per chain. On Banana Gun Pro, you pick your chain, open the COPY TRADE widget, and work through the same parameter set either way.

Three setup modes are available. Simple mode covers the core fields: target wallet address, a custom name for that target, MAX BUY (the per-transaction cap), SPEND LIMIT (the total capital allocated across all copy trades for that target), slippage, duration, and MEV tip if you have buy MEV enabled. Toggle the LIMIT ORDER option and you can attach TAKE PROFIT and STOP LOSS levels directly to the copy trade without a separate order.

Advanced mode adds granular controls: Buy Only Once (copies just the first qualifying transaction from the target, then stops), Buy Exact, Buy % (mirrors a percentage of the target’s position size, so if they buy 1 SOL or 1 ETH worth and you set 20%, you buy 0.2), and Buy Fixed (always enters a fixed amount regardless of what the target does). Copy Sell mirrors exit signals as well as entries. Advanced Presets lets you save any of these configurations as named templates and load them instantly without re-entering values.

The COPY TRADE OVERVIEW panel shows three tabs: ACTIVE (live targets with their spend pace, duration countdown, and status), HISTORY (filterable by date, token, type, amount, and contract address), and BLOCKED (tokens blocked from re-purchase after a Buy Only Once fill, which prevents duplicate entries).

READ ALSO: How the Fastest Crypto Trading Bots Fill Orders Before the Chart Moves

Finding Targets with the TOP TRADERS Widget

The wallet-selection problem is usually more painful than the execution problem, and the TOP TRADERS widget addresses it directly. For any token you are analyzing, the widget surfaces the top 50 wallets by PNL. Hovering over any address pulls up a PNL summary card, and one-click copy trade from that card sets the target wallet without manual entry.

The widget’s label filters are what make it practically useful: you can isolate developers, bundlers, snipers, wallets with active positions, top holders, and cluster-connected addresses. If the wallet you are about to copy-trade carries a “developer” or “bundler” label, that is a direct signal to investigate before committing capital. A wallet that built the token and is now sitting on a large bag is categorically different from an independent trader with a verified win rate.

This connects to a practical risk that any serious copy trader on either chain needs to account for: target wallets can turn malicious after you start copying them. A wallet that previously posted strong returns might pivot to aping into pump-and-dump setups or honeypot contracts, using your automated buy as exit liquidity. Checking a target’s recent transaction history with a wallet scanner before starting a copy trade is not optional hygiene; it is the main variable separating profitable copy traders from those funding someone else’s exit.

Running Both Chains from One Interface

Banana Gun Pro at bananagun.io runs Solana and Base inside the same web terminal, the same Telegram bot session, and the same wallet management panel. Login uses Privy OAuth via Google, Twitter, or Telegram, with no MetaMask requirement. The platform is non-custodial throughout.

The unified structure matters for multi-chain copy trading because switching chains does not mean switching tools, relearning widget layouts, or managing separate bots. Positions on both chains appear in the same POSITIONS panel, the same COPY TRADE OVERVIEW tabs, and the same TRANSACTION HISTORY. If you are running a Solana copy trade alongside a Base copy trade on the same target or on different targets, the monitoring overhead is the same as running a single-chain setup.

Fees sit at approximately 1% per trade on standard swaps, with 0% on stablecoin pairs. The fee structure is the same across chains, so chain selection is a pure execution-mechanics decision, not a cost decision.

Which Chain Fits Your Copy Trading Strategy

The answer depends on where your target wallets operate, not on which chain sounds faster in the abstract.

Solana’s memecoin volume, Pump.fun launch activity, and Raydium liquidity depth make it the natural home for high-frequency copy trading on new token launches. The ~400ms slot time combined with a competitive MEV tip gives you a real shot at front-running the general mempool, and the Jito infrastructure reduces the cost of that competition through better slot-inclusion probability per tip unit.

Base suits copy traders targeting EVM-native activity, particularly tokens launching or migrating on Aerodrome, Baseswap, or Uniswap v3 on the L2. The block 0 copy trading via Flashblocks is a structural advantage for any scenario where being in the first sub-block of a block matters, and the lack of sniping-DEX restrictions gives you more flexibility in how you combine copy trading with other position strategies across the supported Base DEXes.

Most active copy traders end up running both, because the wallets worth copying do not limit themselves to one chain either.

READ ALSO: Solana Trading Bot in 2026: How to Buy, Copy Trade and Exit From One Chat

Frequently Asked Questions

Is Base or Solana faster for copy trading?

It depends on the execution model you are comparing. Solana has ~400ms slot times with Jito MEV routing for block inclusion. Base uses Flashblocks, which split each ~2-second block into ten ~200ms preconfirmation sub-blocks, enabling block 0 copy trading. Neither is categorically faster in all scenarios: Solana’s advantage is raw slot speed; Base’s advantage is first-sub-block confirmation before the full block settles.

What are Base Flashblocks?

Base Flashblocks are preconfirmation sub-blocks produced within each ~2-second Base block. Each standard Base block is divided into roughly ten sub-blocks, each carrying a ~200ms preconfirmation window. A transaction targeting block 0 on Base gets included in the first available Flashblock sub-block, which means it confirms before the parent block finalizes and before standard transactions compete for the same slot.

Can one bot copy trade on both Base and Solana?

Yes. Banana Gun Pro runs both chains inside the same web terminal and the same Telegram bot session. You do not switch bots or wallets between chains. The COPY TRADE widget, COPY TRADE OVERVIEW, TOP TRADERS widget, and all advanced configuration modes work identically on Base and Solana. Login is via Privy OAuth (Google, Twitter, or Telegram), non-custodial, no MetaMask required.

Why does block time matter for copy trading?

Copy trading works by detecting a target wallet’s transaction and submitting your own transaction before or within the same block. If your transaction lands one block later, the price has already moved in response to the target’s buy. Block time sets the outer boundary of how quickly you can respond to a signal. Faster block times or preconfirmation sub-blocks (as with Base Flashblocks) reduce the window between signal detection and your transaction confirming, which directly affects the entry price you get relative to the wallet you are copying.


INTERESTING POSTS