Home Blog Page 55

Best VPN For Gaming You Should Consider

best vpn for gaming

Are you an ardent gamer? In this post, we will show you some of the best VPN for gaming.

For gamers, a smooth online experience is paramount. Lag, disconnects, and geo-restrictions can shatter the immersion and leave you frustrated.

A Virtual Private Network (VPN) can be a powerful tool to combat these issues, offering a secure and optimized connection for your online gaming adventures. But with a plethora of VPN providers in the market, choosing the right one can be overwhelming.

This comprehensive guide dives deep into the world of VPNs for gamers, exploring the key features you need and analyzing the strengths and weaknesses of each VPN service provider.

Why Use a VPN for Gaming?

There are several compelling reasons why gamers might consider using a VPN:

  • Reduced Lag and Improved Ping: A VPN can help reduce lag by routing your connection through a less congested server, potentially improving your ping (response time) and overall online gaming experience.
  • Bypass Geo-Restrictions: Certain games or in-game content might be geo-locked, or unavailable in your region. A VPN allows you to connect to a server in a region where the content is accessible, letting you bypass these restrictions.
  • Enhanced Security and Privacy: A VPN encrypts your internet traffic, making it harder for hackers or snoopers to intercept your data. This is especially important when playing on public Wi-Fi networks.
  • Protection Against DDoS Attacks: In competitive online gaming, some players might resort to DDoS (Distributed Denial-of-Service) attacks to disrupt your connection. A VPN can help mitigate these attacks by masking your IP address.

READ ALSO: The Ultimate VPN Guide – What Is A VPN?

Choosing the Best Gaming VPN: Key Considerations

Here are some crucial factors to weigh when selecting a VPN for gaming:

  • Speed: Fast connection speeds are vital for a seamless gaming experience. Look for providers with a global network of high-bandwidth servers and protocols optimized for speed, like WireGuard.
  • Ping: Low ping times are essential for real-time games. Choose a VPN with minimal latency impact and servers geographically close to your preferred gaming servers.
  • Server Network: A larger server network offers more options for finding a low-ping server and bypassing geo-restrictions.
  • Security and Privacy: Ensure the VPN uses strong encryption protocols (like AES-256) and has a no-logs policy to protect your online activity and data.
  • Simultaneous Connections: If you plan to use the VPN on multiple devices, like your PC, smartphone, and console, check the provider’s allowed simultaneous connections.
  • Device Compatibility: Make sure the VPN offers apps for your preferred gaming devices, including Windows, Mac, Android, iOS, and gaming consoles (if supported).
  • Price and Value: Compare features and pricing plans to find a VPN that fits your budget and offers the best value.

Now, let’s delve into the specifics of each VPN provider, highlighting their strengths and weaknesses for gaming:

Top 10 Best VPNs for Gaming

1. ExpressVPN

ExpressVPN stands out for its lightning-fast speeds, making it an ideal choice for avid gamers. With servers in over 94 countries, it offers unparalleled access to geo-restricted gaming content.

Additionally, its robust security features, including AES-256 encryption and a strict no-logs policy, ensure your gaming sessions remain secure and private.

  • Strengths: ExpressVPN consistently ranks high for speed and offers a vast global server network with excellent ping times. Its user-friendly interface and robust security features make it a favourite among gamers.
  • Weaknesses: ExpressVPN is on the pricier side compared to some competitors.
ExpressVPN
ExpressVPN
A dependable VPN service that works on all devices and platforms.
A dependable VPN service that works on all devices and platforms. Show Less

2. NordVPN

Renowned for its advanced security features and vast server network, NordVPN is a top contender for gaming enthusiasts.

Its CyberSec suite blocks malware and intrusive ads, enhancing your online gaming experience.

Moreover, NordVPN’s specialized servers for gaming minimize latency and ensure stable connections, even during peak gaming hours.

  • Strengths: NordVPN is a powerful contender with a massive server network, strong security features, and a focus on privacy. It offers features like Double VPN for an extra layer of protection.
  • Weaknesses: NordVPN’s speeds can be slightly slower than some top competitors. Some users report occasional connection drops.
NordVPN
NordVPN
The best VPN service for total safety and freedom.
The best VPN service for total safety and freedom. Show Less

3. Surfshark

Surfshark’s unlimited simultaneous connections make it a cost-effective solution for gamers with multiple devices.

Its proprietary NoBorders mode bypasses geo-blocks effortlessly, granting access to international gaming servers and exclusive content.

Furthermore, Surfshark’s CleanWeb feature blocks trackers and malware, optimizing your gaming performance and protecting your privacy.

  • Strengths: Surfshark boasts exceptional speeds thanks to its WireGuard protocol. It allows unlimited simultaneous connections, making it ideal for multi-device setups. Additionally, Surfshark offers strong security features at a competitive price.
  • Weaknesses: Surfshark’s server network, while growing, is not as extensive as some established competitors.
Surfshark
Surfshark
Surfshark is an award-winning VPN service for keeping your digital life secure. Surfshark VPN has servers located in...Show More
Surfshark is an award-winning VPN service for keeping your digital life secure. Surfshark VPN has servers located in more than 60 countries worldwide. Show Less

4. Private Internet Access (PIA)

PIA boasts a vast network of servers spanning 78 countries, ensuring optimal connectivity for gamers worldwide.

Its customizable encryption options and SOCKS5 proxy support offer advanced security and flexibility for gaming enthusiasts.

Additionally, PIA’s dedicated gaming servers minimize ping and latency, providing a competitive edge in online multiplayer games.

  • Strengths: PIA is a budget-friendly option with a substantial server network and decent speeds. It offers advanced customization options for experienced users.
  • Weaknesses: PIA’s interface can be less user-friendly compared to some competitors. Its speeds, while acceptable, might not be the best for fast-paced online games.
Private Internet Access
Private Internet Access uses world-class next-gen servers for a secure and reliable VPN connection, any day, anywhere.
Private Internet Access uses world-class next-gen servers for a secure and reliable VPN connection, any day, anywhere. Show Less

5. CyberGhost VPN

With dedicated gaming servers and specialized gaming VPN profiles, CyberGhost VPN prioritizes performance and speed for gamers.

Its user-friendly interface and one-click connect feature make it accessible to beginners and seasoned gamers alike.

Moreover, CyberGhost’s robust security protocols and strict no-logs policy guarantee a secure gaming environment, free from surveillance and intrusions.

  • Strengths: CyberGhost offers a user-friendly interface and a vast server network with decent speeds. It has a strong focus on ease of use and provides dedicated gaming server options.
  • Weaknesses: CyberGhost’s speeds might not be the absolute fastest compared to top contenders. There have been some concerns about its logging policies in the past, although the company maintains a no-logs claim.
CyberGhost VPN
CyberGhost VPN
CyberGhost VPN is a VPN service provider with more than 9,000 VPN servers spread in over 90 countries. Complete privacy...Show More
CyberGhost VPN is a VPN service provider with more than 9,000 VPN servers spread in over 90 countries. Complete privacy protection for up to 7 devices! Show Less

6. Ivacy VPN

Ivacy VPN’s optimized gaming servers and low-latency connections make it a favourite among competitive gamers.

Its split tunnelling feature allows you to route gaming traffic through the VPN while keeping other applications unaffected, optimizing bandwidth and reducing lag.

Furthermore, Ivacy’s integrated DDoS protection shields you from potential attacks, ensuring uninterrupted gameplay.

  • Strengths: Ivacy VPN offers a good value with affordable pricing and a vast server network. It provides decent speeds and strong security features.
  • Weaknesses: Ivacy VPN’s speeds can be inconsistent at times, and its interface might not be as intuitive as some competitors.
No coupons found.

7. PureVPN

PureVPN’s extensive server network and high-speed connections make it a reliable choice for gamers seeking seamless performance.

Its dedicated IP addresses provide added security and stability, reducing the risk of IP bans in online gaming communities.

Additionally, PureVPN’s NAT firewall and anti-DDoS features offer an extra layer of protection against cyber threats, enhancing your gaming experience.

  • Strengths: PureVPN offers a large server network with a focus on security and strong encryption protocols. It boasts dedicated gaming servers optimized for performance.
  • Weaknesses: PureVPN’s speeds can be inconsistent at times. Some users have reported past privacy concerns, although the company has taken steps to address them.
PureVPN
PureVPN
PureVPN is one of the best VPN service providers with presence across 150 countries in the world. An industry VPN leader...Show More
PureVPN is one of the best VPN service providers with presence across 150 countries in the world. An industry VPN leader with more than 6,500 optimized VPN servers. Show Less

8. ProtonVPN

ProtonVPN’s commitment to privacy and security makes it a trustworthy option for discerning gamers.

Its Secure Core architecture routes your traffic through multiple servers, safeguarding against network attacks and surveillance.

Furthermore, ProtonVPN’s strong encryption protocols and Swiss-based jurisdiction ensure maximum privacy and data protection, allowing you to game with peace of mind.

  • Strengths: ProtonVPN prioritizes privacy and offers a secure and transparent service with a Swiss-based no-logs policy. It provides decent speeds and a growing server
  • Weaknesses: ProtonVPN’s free tier has limited features and server locations. While the paid plans offer more options, the overall server network is smaller compared to some competitors. Speeds can also be inconsistent, particularly on the free tier.
ProtonVPN
ProtonVPN
A swiss VPN service that goes the extra mile to balance speed with privacy protection.
A swiss VPN service that goes the extra mile to balance speed with privacy protection. Show Less

9. TunnelBear VPN

TunnelBear VPN’s user-friendly interface and intuitive design make it an excellent choice for casual gamers.

While its server network is relatively smaller compared to other providers, TunnelBear’s strong encryption and GhostBear feature help bypass restrictive networks and censorship, ensuring unrestricted access to gaming content worldwide.

  • Strengths: TunnelBear offers a simple and user-friendly interface, making it ideal for beginners. It provides decent speeds for casual gaming and has a transparent no-logs policy.
  • Weaknesses: TunnelBear has a limited server network compared to other providers. Its free plan has a data cap, and paid plans offer a smaller number of simultaneous connections compared to competitors.
TunnelBear VPN
TunnelBear VPN
TunnelBear is a VPN service provider that provides you with privacy, security, and anonymity advantages. It has VPN...Show More
TunnelBear is a VPN service provider that provides you with privacy, security, and anonymity advantages. It has VPN servers in more than 46 countries worldwide. Show Less

10. ZoogVPN

ZoogVPN’s affordable pricing plans and robust security features cater to budget-conscious gamers without compromising on quality.

Its high-speed servers and unlimited bandwidth facilitate smooth gaming experiences, even for bandwidth-intensive games.

Additionally, ZoogVPN’s ad-blocking and malware protection features enhance your online gaming environment, minimizing distractions and potential threats.

  • Strengths: ZoogVPN offers a budget-friendly option with decent speeds and a growing server network. It boasts strong security features and a no-logs policy.
  • Weaknesses: ZoogVPN’s server network is not as extensive as established competitors. It might not be the best choice for bypassing geo-restrictions on highly localized content. Customer support options might be limited compared to bigger providers.
ZoogVPN
ZoogVPN
ZoogVPN is the complete and trusted all-in-one VPN service that protects your sensitive personal and financial...Show More
ZoogVPN is the complete and trusted all-in-one VPN service that protects your sensitive personal and financial information online. Show Less

Testing Methodology: How We Tested, Reviewed And Ranked The Gaming VPNs
Testing Methodology: How We Tested, Reviewed And Ranked The Gaming VPNs

Choosing the best VPN for gaming requires a nuanced approach. We analyzed the ten VPN providers based on the following key criteria:

  • Speed: We conducted speed tests using various servers across different regions to assess download and upload speeds. Lower speeds can lead to lag and a compromised gaming experience.
  • Ping: We measured ping times to gaming servers in different locations. Lower ping times are crucial for real-time games, minimizing delays between your actions and the game’s response.
  • Server Network: We evaluated the size and distribution of each provider’s server network. A larger and geographically diverse network offers more options for finding low-ping servers and bypassing geo-restrictions.
  • Security and Privacy: We assessed the VPN’s encryption protocols, logging policies, and features like leak protection. Strong security and a no-logs policy ensure your data and online activity remain protected.
  • Simultaneous Connections: We considered the number of devices you can connect simultaneously with a single subscription. This is important if you want to use the VPN on multiple devices, including your PC, smartphone, and gaming console.
  • Device Compatibility: We checked if the VPN provider offers dedicated apps for your preferred gaming devices, including Windows, Mac, Android, iOS, and gaming consoles (where supported). Not all VPNs offer native apps for consoles, so compatibility is crucial.
  • Price and Value: We compared the pricing plans of each VPN provider and assessed the overall value proposition based on features, performance, and cost.

Read Also: Surfshark Antivirus Review

Can You Use a VPN on Gaming Consoles?
Can You Use a VPN on Gaming Consoles?

Yes, you can use a VPN on gaming consoles such as PlayStation, Xbox, and Nintendo Switch to enhance your gaming experience and improve security. While not all gaming consoles natively support VPN applications, there are alternative methods to set up a VPN connection:

  1. Router Configuration: Many modern routers support VPN configuration, allowing you to protect all devices connected to your home network, including gaming consoles. By configuring the VPN directly on your router, you can encrypt your console’s internet traffic without the need for individual VPN apps.
  2. Smart DNS Services: Some VPN providers offer Smart DNS services designed specifically for gaming consoles. Smart DNS reroutes your DNS queries through VPN servers, enabling you to bypass geo-restrictions and access region-locked content on gaming consoles.
  3. Virtual Router: If your PC or laptop is connected to a VPN, you can create a virtual router and share your VPN connection with your gaming console. This method involves using your computer as a bridge between the console and the VPN server.

While using a VPN on gaming consoles can provide benefits such as accessing geo-restricted content and protecting against DDoS attacks, it’s essential to consider potential limitations, such as decreased connection speeds and compatibility issues with certain games or services.

READ ALSO: Essential Gaming Guide

Can a VPN Help You Circumvent Bans in Games?

While a VPN can provide some degree of anonymity and security, it’s important to note that using a VPN to circumvent bans in games may not always be effective or advisable. Here’s why:

  1. Detection by Game Publishers: Many game publishers employ sophisticated anti-cheat systems that can detect and block VPN usage. If a player is caught using a VPN to bypass a ban or engage in prohibited activities, they risk facing more severe penalties, including permanent account suspension.
  2. Violation of Terms of Service: Most online games have strict terms of service that prohibit the use of VPNs or any other means to manipulate or circumvent game mechanics. Engaging in such activities can result in account bans, loss of progress, and even legal consequences in some cases.
  3. Impact on Gameplay Experience: Using a VPN to mask your IP address may introduce additional latency and affect your gameplay experience, particularly in fast-paced and competitive multiplayer games where split-second reactions are crucial.

While VPNs offer valuable benefits such as enhanced privacy, security, and access to region-locked content, it’s essential to use them responsibly and in accordance with the terms of service of the games you play.

Instead of attempting to circumvent bans, players are encouraged to abide by the rules of fair play and engage in positive gaming behavior.

Best VPN For Gaming: FAQs

Which VPN server is best for gaming?

The best VPN server for gaming depends on several factors, including your location, the location of the game server, and the VPN provider’s infrastructure.

Generally, it’s advisable to choose a server closest to the gaming server to minimize latency and reduce ping times. However, reputable VPN providers often offer specialized gaming servers optimized for low latency and high performance, making them ideal choices for gaming purposes.

Is a VPN better for gaming?

Using a VPN can enhance your gaming experience by providing security, privacy, and the ability to bypass geo-restrictions. VPNs encrypt your internet connection, protecting you from DDoS attacks and other cyber threats prevalent in online gaming communities.

Additionally, VPNs allow you to access region-locked gaming content and servers, expanding your gaming options regardless of your physical location. However, it’s essential to choose a VPN provider with optimized servers for gaming to ensure minimal impact on speed and latency.

Which is the strongest VPN to use?

The strength of a VPN depends on various factors, including encryption standards, server infrastructure, and logging policies. VPNs renowned for their robust security features and commitment to privacy are often considered the strongest options.

Providers like ExpressVPN, NordVPN, and Surfshark are frequently praised for their military-grade encryption, strict no-logs policies, and extensive server networks, making them reliable choices for safeguarding your online activities, including gaming.

What is the best free VPN for gaming?

While free VPNs may seem appealing, they often come with limitations that can hinder your gaming experience, such as data caps, bandwidth throttling, and fewer server options. Additionally, free VPNs may compromise your privacy by logging your activities or serving ads.

If you’re looking for a free VPN for gaming, options like ProtonVPN and TunnelBear offer limited free plans with basic features and data allowances. However, for optimal performance and security, investing in a reputable paid VPN service is recommended.

Does a VPN slow gaming?

Using a VPN can potentially slow down your gaming experience due to the encryption and rerouting of your internet traffic. However, the extent of the slowdown largely depends on factors such as the VPN provider’s server infrastructure, your internet connection speed, and the distance between your location and the VPN server.

High-quality VPN providers often mitigate speed reductions by offering optimized servers for gaming and prioritizing performance. Additionally, using a VPN with minimal impact on speed can help ensure a smooth gaming experience without significant slowdowns.

Which VPN has the fastest server?

Several VPN providers offer fast servers optimized for gaming and streaming purposes. While the speed of VPN servers can vary depending on factors like server load and network congestion, providers like ExpressVPN, NordVPN, and Surfshark are known for their consistently high speeds and low latency.

Additionally, VPNs with large server networks and advanced infrastructure tend to offer faster and more reliable connections. Conducting speed tests and selecting servers closest to your location can help maximize your gaming performance while using a VPN.

Conclusion

Listed above are the best VPNs for gaming. As you can see, a reliable VPN is essential for ensuring security, privacy, and optimal performance.

Each of the VPN providers mentioned above offers unique features tailored to the needs of gamers, allowing you to find the perfect shield for your gaming adventures.

Whether you prioritize speed, security, or affordability, rest assured that there’s a VPN solution to elevate your gaming experience to new heights. So, equip yourself with the best VPN for gaming and embark on your virtual quests with confidence and peace of mind.


RELATED POSTS:

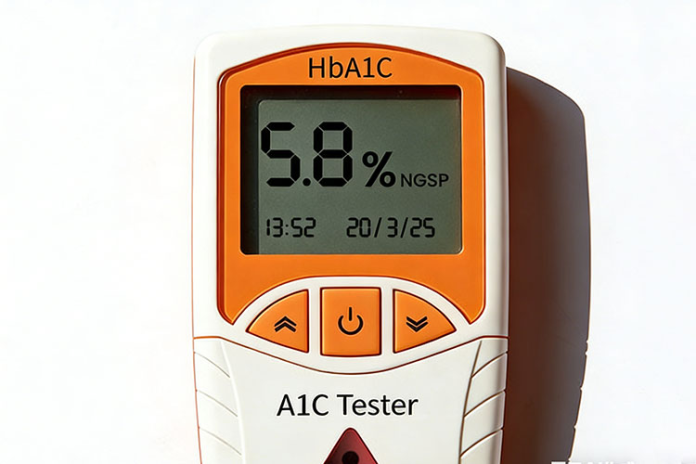
A1C Tester: A Complete Guide to At-Home HbA1c Monitoring for Better Diabetes Control

0
A1C Tester: A Complete Guide to At-Home HbA1c Monitoring for Better Diabetes Control

In this post, I will talk about A1C Tester and give you a complete guide to At-Home HbA1c monitoring for better diabetes control.

A convenient health tool is increasingly used by individuals who want to track their blood sugar levels without frequent laboratory visits. The A1C tester measures average glucose levels over the past two to three months using a simple finger-prick blood sample at home.

In this guide, you will learn how it works, its benefits and limitations, and how it can support more effective diabetes management in everyday life.

What is an A1C Tester and Why It Matters

An A1C tester is a portable diagnostic device designed to measure HbA1c levels from a small blood sample. HbA1c reflects the percentage of sugar attached to hemoglobin in red blood cells, giving a long-term view of blood glucose control.

The A1C tester is especially useful for individuals who want quick insights into their glucose trends without waiting for laboratory results.

Key points about A1C testing

  • Measures average blood sugar over 2–3 months
  • Uses a small finger-prick blood sample
  • Helps monitor diabetes management at home
  • Provides faster results compared to lab testing visits
  • Useful for tracking lifestyle and diet changes

Unlike daily glucose meters that show instant readings, A1C testing focuses on long-term trends, making it an essential part of diabetes care planning.

How an A1C Tester Works at Home

Modern A1C testers are designed to be simple and user-friendly so that individuals can perform the test without medical assistance.

The process generally involves collecting a small blood sample and analyzing it through a built-in chemical reaction that measures glycated hemoglobin levels.

Step-by-step working process

  • A finger is pricked to collect a small blood drop
  • The blood sample is placed into the test cartridge or strip
  • The device processes the sample using HbA1c detection technology
  • The result is displayed on the screen within minutes
  • The reading shows average glucose control over recent months

Important usage considerations

  • Follow instructions carefully for accurate results
  • Use fresh and properly stored test kits
  • Avoid contamination of the sample area
  • Ensure hands are clean before testing
  • Store devices in recommended temperature conditions

This simple process makes the A1C tester a convenient option for home-based monitoring, especially for users who prefer quick feedback without clinical appointments.

Benefits of Using an A1C Tester for Daily Health Monitoring

The growing popularity of home testing devices is linked to convenience and faster access to health insights. The A1C tester offers several advantages for people managing diabetes or monitoring metabolic health.

Advantages of at-home A1C testing

  • Provides quick results within minutes instead of days
  • Eliminates the need for frequent lab visits
  • Helps users track long-term glucose trends regularly
  • Supports better lifestyle and diet decision-making
  • Easy to use with minimal training required

Practical benefits for diabetes management

  • Encourages consistent health monitoring
  • Helps detect changes in glucose control early
  • Useful for adjusting diet, exercise, or medication routines
  • Reduces dependency on healthcare facility access
  • Convenient for elderly users or people with mobility issues

With regular use, the A1C tester can help users stay more aware of their health patterns and respond quickly to changes in blood sugar control.

Limitations and Things to Keep in Mind

While A1C testers offer convenience, they are not perfect substitutes for professional laboratory testing. Understanding their limitations is important for safe and accurate use.

Key limitations

  • May not be as precise as certified lab tests
  • Results can vary depending on sample quality
  • Not intended for diagnosing medical conditions
  • Requires proper handling to maintain accuracy
  • Can be affected by improper storage or expired kits

When to be cautious

  • If results are inconsistent over multiple tests
  • If symptoms do not match readings
  • If used without proper instructions
  • When making major treatment decisions without medical advice

The A1C tester should be viewed as a supportive monitoring tool rather than a replacement for professional healthcare diagnostics. Regular consultation with a healthcare provider remains essential for proper diabetes management.

Who Should Use an A1C Tester and How It Helps

The A1C tester is designed for individuals who need regular monitoring of their long-term blood sugar levels. It is especially helpful for people already managing diabetes or those at risk of developing glucose-related conditions.

Ideal users of an A1C tester

  • Individuals with Type 1 or Type 2 diabetes
  • People tracking prediabetes conditions
  • Users adjusting diet and lifestyle habits
  • Caregivers monitoring family members’ health
  • Individuals who prefer home-based health tracking

How it supports better health decisions

  • Encourages regular monitoring habits
  • Helps identify patterns in glucose control
  • Supports informed lifestyle changes
  • Assists in evaluating diet effectiveness
  • Provides motivation for better health discipline

By offering accessible and frequent feedback, the A1C tester helps users stay proactive about their health instead of relying only on occasional lab reports.

A1C Tester in Everyday Diabetes Management

Integrating an A1C tester into daily health routines can improve awareness and control of blood sugar levels. It works best when combined with a balanced lifestyle and professional medical guidance.

Many users find it helpful for tracking progress after dietary changes or medication adjustments. Over time, it becomes a practical tool for understanding how daily habits influence long-term glucose levels.

Building Better Health Awareness with Regular A1C Tracking

Using an A1C tester consistently can help individuals develop a stronger understanding of how their lifestyle affects long-term blood sugar control. Instead of waiting for occasional lab results, users can stay more engaged with their health on a regular basis.

This ongoing awareness encourages better decisions around food choices, physical activity, and medication adherence. Over time, it can also help reduce health risks associated with poorly managed glucose levels.

The A1C tester works best when it becomes part of a routine rather than a one-time check. When combined with medical advice, it supports a more informed and balanced approach to diabetes care and long-term wellness.


INTERESTING POSTS

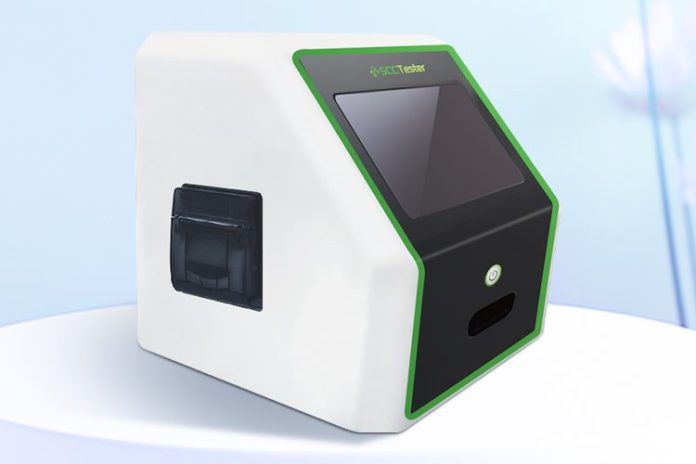
SCC Tester: Complete Guide to Somatic Cell Count Testing in Milk Quality Control

0
SCC Tester: Complete Guide to Somatic Cell Count Testing in Milk Quality Control

In this post, I will discuss SCC Tester and provide a comprehensive guide to somatic cell count testing in milk quality control.

An important diagnostic tool is widely used in the dairy industry to evaluate milk quality and detect potential health issues in cows.

The SCC tester helps farmers, dairy laboratories, and processors measure Somatic Cell Count (SCC), a key indicator of mastitis and overall milk hygiene.

Understanding SCC levels is important because it directly affects milk safety, production efficiency, and dairy herd health management. With proper SCC testing, dairy producers can detect infections early, reduce economic losses, and maintain high-quality milk standards.

What is an SCC Tester and How It Works in Dairy Analysis

An SCC tester is a device or system used to measure the number of somatic cells in milk. These somatic cells mainly include white blood cells and epithelial cells that naturally appear in milk in small quantities. When the udder becomes infected, these cells increase significantly, signaling a health issue.

The SCC tester works by analyzing a milk sample and estimating the concentration of somatic cells. Depending on the technology used, it may rely on optical, electrical, or fluorescent methods to detect cell levels. Modern SCC testers are designed for fast, accurate, and on-site testing, making them highly useful for farms and dairy collection centers.

Common uses of SCC tester include:

  • Detecting mastitis at an early stage in dairy cows
  • Monitoring udder health regularly in dairy herds
  • Supporting milk quality grading in dairy plants
  • Helping veterinarians diagnose infections quickly
  • Improving herd management decisions based on health data

Importance of SCC Tester in Milk Quality and Mastitis Detection

Regular use of an SCC tester plays a major role in maintaining milk quality and ensuring the health of dairy animals. High somatic cell counts usually indicate inflammation or infection in the udder, most commonly mastitis, which is one of the most common diseases in dairy farming.

Early detection through SCC testing helps farmers take timely action before the condition becomes severe. This not only protects animal health but also reduces treatment costs and prevents milk quality loss.

Key benefits of SCC testing in dairy management:

  • Early detection of mastitis before visible symptoms appear
  • Improved milk quality and safety for consumers
  • Reduced dependence on antibiotics through timely intervention
  • Better herd health monitoring and record keeping
  • Increased milk yield due to healthier cows
  • Prevention of economic losses caused by infected milk rejection

By continuously monitoring SCC levels, dairy producers can maintain consistent milk quality and ensure compliance with industry standards. This makes the SCC tester an important investment for both small and large dairy operations.

Types of SCC Tester Devices Used in Dairy Farms and Laboratories

Different SCC tester systems are available depending on accuracy needs, testing environment, and budget. Some are designed for quick on-farm checks, while others are used in professional laboratories for detailed analysis.

Common types of SCC testers include:

  • Portable SCC testers used on farms for quick milk checks
  • Automated laboratory SCC analyzers for high-precision testing
  • Flow cytometry-based SCC systems for advanced cell counting
  • Electronic milk analyzers that estimate SCC along with fat and protein levels
  • Dipstick-style test kits for basic screening purposes

Each type of SCC tester offers different levels of accuracy and speed. Portable devices are ideal for daily farm monitoring, while lab-based systems are better suited for regulatory compliance and bulk milk testing.

Choosing the right SCC tester depends on:

  • Size of the dairy operation
  • Required accuracy level
  • Testing frequency
  • Budget and maintenance capability
  • Integration with milk management systems

Benefits of Using SCC Tester for Dairy Herd Management

Using an SCC tester consistently helps dairy farmers make better management decisions. It provides real-time insights into animal health and milk quality, allowing quick responses to potential problems.

Important advantages include:

  • Early identification of infected animals before symptoms spread
  • Better segregation of healthy and unhealthy milk
  • Improved breeding decisions based on udder health history
  • Reduced veterinary costs through preventive care
  • Enhanced productivity due to healthier dairy cows
  • Stronger quality control in milk supply chains

In modern dairy farming, data-driven decisions are becoming essential. SCC testing provides reliable data that helps farmers track trends, identify recurring health issues, and improve overall herd performance. This leads to a more efficient and sustainable dairy operation.

Why SCC Tester is Essential for Modern Dairy Quality Control

The SCC tester has become a critical tool in modern dairy production systems where quality and safety standards are increasingly strict. Milk buyers and processing companies often require SCC limits to ensure product quality, making regular testing a necessity rather than an option.

By integrating SCC testing into daily operations, dairy farms can maintain consistent milk quality and meet regulatory requirements. It also helps build trust with consumers who demand safe and high-quality dairy products.

The SCC tester supports long-term dairy sustainability by:

  • Reducing waste caused by contaminated milk
  • Supporting responsible antibiotic usage
  • Improving animal welfare through early disease detection
  • Enhancing profitability through higher-quality milk output

As dairy technology continues to evolve, SCC testers are becoming more advanced, accurate, and user-friendly. Their role in ensuring milk hygiene and herd health will continue to grow in importance.

Final Thoughts on SCC Tester in Dairy Farming and Milk Quality Management

An SCC tester is more than just a testing device; it is a practical tool for maintaining milk safety and protecting dairy animal health. By monitoring somatic cell count regularly, farmers can detect mastitis early, improve herd management, and ensure high-quality milk production.

In modern dairy systems, the SCC tester remains a key part of quality control strategies. Its ability to provide fast and reliable insights makes it essential for both small farms and large dairy industries aiming for consistent milk standards and healthier herds.


INTERESTING POSTS

How Addressing Cloud Misconfigurations Disrupts the Cyber Kill Chain

0
How Addressing Cloud Misconfigurations Disrupts the Cyber Kill Chain

In this post, I will show you how addressing cloud misconfigurations disrupts the cyber kill chain.

Cloud environments offer speed and flexibility, but they introduce new risks. One common issue is misconfiguration. Small mistakes, such as overly broad access permissions or publicly exposed resources, can open the door to attackers. These gaps sometimes go unnoticed until they’re exploited.

The cyber kill chain provides a useful way to look at how attacks unfold step by step. It includes stages like reconnaissance, initial access, persistence, and data exfiltration. When cloud settings are misconfigured, they can support attackers at multiple stages of this process. Fixing those weaknesses early can disrupt the attack path.

How misconfigurations enable early attack stages

How misconfigurations enable early attack stages

Attackers often begin with reconnaissance. They scan for exposed assets such as open storage buckets or mismanaged identity roles. Cloud platforms make it easy to deploy resources quickly, but without proper controls, those resources can become visible to anyone.

A simple misconfiguration like a publicly accessible database can give attackers valuable information. Even metadata or system details can help them plan their next move. Once they identify a target, they move to initial access. Weak identity and access management settings, such as excessive privileges, make this step much easier.

By tightening configurations at this stage, organizations reduce the chances of attackers gaining a foothold in the first place.

Stopping lateral movement through better controls

After gaining access, attackers rarely stay in one place. They move laterally across systems to expand their reach. Misconfigured permissions are a major factor here. If users or services have more access than they need, attackers can exploit those privileges to move deeper into the environment.

Network misconfigurations also play a role. Poor segmentation allows attackers to jump between workloads without much resistance. This increases the potential damage and makes detection harder.

Security teams that regularly audit permissions and enforce least privilege can limit this movement. Strong segmentation and access boundaries create friction for attackers, slowing them down or stopping them entirely.

Reducing persistence and data exposure risks

Reducing persistence and data exposure risks

Persistence allows attackers to maintain access over time. In cloud environments, this often involves creating new credentials, modifying roles, or deploying hidden resources. Misconfigurations can make these actions easier to perform and harder to detect.

Data exposure is often the final goal. Misconfigured storage services or weak encryption settings can lead to sensitive data being accessed or stolen. Even a single overlooked setting might have serious consequences.

To break the kill chain in cloud security, organizations need to address these risks before attackers reach this stage. Continuous checks for configuration drift help ensure that security settings remain intact as environments evolve.

Building a proactive cloud security approach

Cloud environments change constantly. New resources are created, updated, and removed at a rapid pace. This makes manual security checks difficult to maintain. Automated tools can help identify misconfigurations in real time and enforce consistent policies.

Clear visibility is also important. Security teams need to know what assets exist and how they are configured. Without that visibility, gaps can remain hidden.

Training and shared responsibility also matter. Developers and operations teams play a key role in setting up cloud resources. When they follow secure configuration practices, the overall risk decreases.

Addressing cloud misconfigurations is among the most effective early-stage controls. It reduces opportunities for attackers at every stage, from initial discovery to data exfiltration. By focusing on prevention and maintaining strong configuration hygiene, organizations can limit exposure and improve their security posture.


INTERESTING POSTS

Security Services For Technology Campuses in San Francisco

0
Security Services For Technology Campuses in San Francisco

In this post, I will talk about security Services for technology campuses in San Francisco.

The technology sector in San Francisco has its own pace. People come in early, stay late, move between buildings, meet in common areas, take calls outside, receive deliveries throughout the day. It’s not a static environment. It’s constantly moving, which means security can’t just be a presence at the front desk.

A lot of campuses still start there. A guard at the entrance, someone checking badges, maybe someone walking the property. And that’s fine at a basic level. But it doesn’t go far enough, especially in San Francisco where you have a mix of high foot traffic, public access areas, and a real risk of theft, trespassing, and people trying to blend in.

Why Integrated Security Matters

What companies in the tech sector really need is a security team that becomes part of the environment. A San Francisco security company that trains their security guards to come to work every day engaged and motivated. Engagement will lift the morale of the security officers but also increases security and early detection of issues. VP Security Guards consistently holds their security guards to hire standards. Supervisors will observe behavior on the job and give feedback. Account managers will observe, but also solicit feedback from customers. That way the security of the location is constantly improving, security officers are highly engaged and consistently raising their level of service

Not just people standing post, but people who understand how the campus works. Who recognize employees by name, who notice when someone doesn’t belong, who understand timing patterns without having to think about it. When people usually arrive. When they leave. When things feel off.

That kind of awareness doesn’t come from just showing up to a shift. It comes from being integrated.

Security officers on a well-run campus become familiar with the routine. They know the schedule of employees leaving and showing up to work. They know the layout of the property, when deliveries arrive and where and when people park. Once they understand the routine of the property, they understand when someone or something is out of place. That helps with detecting security issues that need to be addressed. Familiarity and experience will enhance security and safety. That will only happen if security officers are trained to integrate and improve familiarity daily.

Noticing small things that are out of the ordinary like an unfamiliar person or car trying to gain access, an out-of-scheduling delivery when questioned can make a huge difference. Visible and inquisitive security guards can stop larger security issues. In addition, they are a great deterrent.

Proactive Detection and Employee Trust

Because most issues don’t come out of nowhere. There are small signs first. Someone lingering too long. Someone asking the wrong questions. Someone trying to follow employees into secured areas. If security is paying attention early, those situations get handled before they turn into something bigger.

But for that to work, employees also need to feel comfortable with the security team.

That’s a big part that gets overlooked.

If employees see security as outsiders, they don’t engage. They don’t report things. They don’t ask questions. But when security is part of the team, when they recognize people, greet them, and interact naturally, that changes everything.

Employees start to speak up. They mention things that feel off. They trust the people around them, which creates another layer of protection that you can’t really train into a system. It just develops over time.

Adapting Security to Open Campus Design

In San Francisco, where many tech campuses are open by design and encourage movement and collaboration, that balance matters even more. You can’t turn a campus into a locked-down environment. That would go against how these companies operate, which means security needs to adapt.

It has to be present without being intrusive. Aware without being overbearing while consistent without feeling rigid. That’s not something you get from a checklist. It comes from having the right people and keeping them engaged.

That’s why integration is such a big part of how we approach these environments.

The security team needs to understand not just security protocols, but how the company itself operates. What kind of culture it has. How employees interact. What’s normal for that specific location, because every campus is different.

Some have heavy visitor traffic. Others are more controlled. Some have multiple buildings spread out. Others are compact but busy. Some rely heavily on deliveries and vendors throughout the day. Others don’t.

Consistency, Supervision, and Long-Term Value

All of that affects how security should be handled. When guards are familiar with delivery schedules, they know when something doesn’t line up. When they recognize employee vehicles, they can spot something unusual in a parking area. When they understand the layout, they can respond faster and more effectively if something does happen.

But again, that only works if they’re consistent and actually part of the environment.

That’s also where supervision and support come in.

It’s not enough to place guards and hope they figure it out. They need guidance. They need to be held accountable. And they need to stay engaged over time. Because the longer they’re on a site, the more valuable they become.

They pick up on details that no report will ever capture. Small patterns. Small changes. Things that don’t stand out unless you’ve been there long enough and those details matter.

At the same time, the client shouldn’t have to manage all of that. They shouldn’t have to deal with coverage issues, callouts, or performance concerns. That needs to be handled behind the scenes, so the experience remains consistent.

That’s where a structured approach makes a difference. You get a team that feels in-house, but you still have the support, supervision, and accountability of a professional security company behind it.

That combination works, because in the end, security in a tech environment isn’t just about stopping incidents. It’s about creating an atmosphere where people can focus on their work without thinking about safety all the time.

If employees feel uncomfortable, if things feel unpredictable, it affects how they work. It affects productivity. It affects the environment overall.

The Real Goal: Stability Without Disruption

But when security is done right, it fades into the background in the best possible way.

People feel safe. They move freely. They focus on what they’re there to do whilethe security team is still there, paying attention, catching things early, and making sure everything runs the way it should.

That’s really the goal. Not just protection, but stability. And in a place like San Francisco, with how fast things move, that makes all the difference.


INTERESTING POSTS

Cybersecurity Challenges Facing Small Businesses Today

0
Cybersecurity Challenges Facing Small Businesses Today

In this post, I will talk about cybersecurity challenges facing small businesses today.

Key Takeaways

  • Small businesses are now primary targets for threat actors who view them as high-value, low-resistance gateways compared to heavily fortified enterprise organizations.
  • The use of generative A and machine learning has allowed criminals to automate sophisticated phishing campaigns and malware campaigns at a scale and quality that was previously impossible.
  • The rapid integration of cloud services, IoT devices, and remote work protocols has created a sprawling attack surface that many SMBs have yet to properly map or secure.
  • With the rise of credential theft and business email compromise, securing user identities through zero trust frameworks and tools is now more critical than traditional firewalls.
  • Technical cybersecurity tools alone cannot protect a business without boardroom buy-in and a proactive effort to close the cyber skills gap through continuous staff education.

Many small business owners operate under a dangerous assumption: that their size makes them invisible to threat actors. This mindset isn’t just wrong: it’s becoming increasingly costly. In reality, limited budgets, understaffed IT teams, and a general lack of formalized cybersecurity measures make small and medium-sized businesses (SMBs) extraordinarily appealing targets.

The cybersecurity landscape today looks nothing like it did even three years ago. Generative AI and machine learning have handed cybercriminals sophisticated, low-cost tools at scale, from hyper-personalized phishing emails to adaptive malware that evades traditional defenses.

As enterprise organizations continue to harden their defenses and invest heavily in threat intelligence and zero trust architectures, attackers are pivoting and small businesses are squarely in their crosshairs. SMBs have quietly become the low-hanging fruit of the digital world, and the window to act is narrowing fast.

Beyond Simple Viruses

Today’s cyber attacks are engineered with a level of precision and speed that was unthinkable a decade ago. Generative AI and machine learning algorithms now allow even low-skilled cybercriminals to automate entire malware campaigns, spinning up thousands of unique attack variants, testing them against live defenses, and self-correcting in real time. Adaptive malware, in particular, can now analyze its environment and modify its own code to slip past conventional antivirus solutions.

Sophisticated Social Engineering

The era of the poorly worded, obviously suspicious email is fading fast. Modern phishing campaigns are tailored, contextually aware, and often indistinguishable from legitimate correspondence. Powered by generative AI, attackers now scrape social media profiles, LinkedIn pages, and public business records to craft messages that feel personal. An employee might receive what appears to be a follow-up email from a known vendor only to find it was a social engineering trap designed to harvest credentials or deploy infostealer malware.

Social engineering tactics have crossed into an even more unsettling frontier with the rise of deepfake technology. Fraudsters are no longer limited to written impersonation. Increasingly, they are deploying AI-generated audio and video to impersonate executives in real time, instructing employees over a ‘video call’ to authorize wire transfers or hand over sensitive login details.

Ransomware 2.0: The New Hostage Economy

Early ransomware was blunt: lock the victim’s files, demand payment, and hope for the best. Today’s ransomware groups operate with the structure and strategy of organized crime syndicates. The modern playbook combines remote encryption of critical systems with aggressive data exfiltration, meaning that even if a business restores from backup, attackers still hold sensitive customer records, financial data, or proprietary information as leverage.

Modern Vulnerabilities

Here are some of the key attack surfaces a small business must cover:

1. The Cloud Complexity

The rapid migration to cloud services over the past several years has delivered undeniable benefits like flexibility, scalability, and cost savings that are particularly attractive to SMBs. However, speed of adoption has consistently outpaced security readiness. Many small businesses configure cloud environments with default settings, overly permissive access controls, and little understanding of the shared-responsibility model that most cloud providers operate under.

Without deliberate cloud security protocols in place (e.g., proper identity management, encryption standards, and continuous monitoring), these environments become wide-open windows. Misconfigured storage buckets, exposed application programming interfaces (APIs), and poorly managed cloud systems have been responsible for some of the most damaging data breaches in recent years, and SMBs are no exception.

2. The IoT Explosion

Walk through almost any modern small business office, and you’ll find a quiet army of connected devices (e.g., smart thermostats, networked printers, IP security cameras, voice assistants, and smart devices of every variety). Each one represents a potential entry point. IoT devices (or Internet-of-Things devices) are notorious for shipping with weak default passwords, infrequent firmware updates, and minimal built-in security features.

Because they often operate outside the visibility of whatever cybersecurity tools a business has in place, they go unmonitored for months or even years. For attackers, a single compromised smart device can serve as a foothold to pivot deeper into a business network quietly, and without triggering a single alert.

3. Vulnerable Infrastructure

Legacy systems represent one of the most persistent and underappreciated risks in the SMB threat landscape. Older platforms (e.g., outdated versions of widely used server software) frequently harbor known, unpatched vulnerabilities that threat actors actively scan for and exploit. The problem is compounded when SMBs integrate these aging systems with modern cloud services or connected devices, creating hybrid environments riddled with security gaps.

Known Exploited Vulnerabilities published in resources like the KEV catalog often remain unpatched in small business environments for months, simply because there is no dedicated cybersecurity professional on staff or a managed IT company to prioritize remediation.

4. The Remote Work Residue

The mass shift to remote work fundamentally and permanently redefined the corporate attack surface. What began as an emergency measure has settled into a hybrid norm, and the security gaps it introduced have never been fully closed. Employees working from home connect over personal routers, use unmanaged personal devices, and access sensitive business systems through a patchwork of VPNs (virtual private networks) and cloud services of varying security quality.

Each remote endpoint is, in effect, a small branch office with none of the protections a traditional office network might provide. For SMBs without a zero trust framework to verify every user and device regardless of location, ‘work from anywhere’ has quietly become ‘breach from anywhere.’

The ‘Human Factor’ and Internal Risks

Technology alone does not explain why so many small businesses fall victim to cyber attacks: human psychology plays an equally decisive role. Threat actors have long understood that it is often far easier to manipulate a person than to break through a firewall.

1. Social Engineering Tactics

Credential theft remains one of the most effective and common entry points, frequently achieved through social engineering tactics that create false urgency, impersonate authority figures, or exploit moments of distraction.

Fake ads, or malicious advertisements disguised as legitimate software downloads or service sign-ups, have also surged as a delivery mechanism, luring unsuspecting employees into voluntarily handing over login information or installing Infostealer malware without a single line of hostile code ever needing to breach the network perimeter directly.

2. Insider Threats

While deliberately malicious insider threats do exist (e.g., disgruntled employees exfiltrating data, or contractors exceeding their access privileges), the far more common scenario is far more mundane: an untrained staff member clicking a link they shouldn’t, misconfiguring a shared folder, or reusing a compromised password across multiple platforms.

Accidental data breaches caused by well-meaning but underprepared employees are quietly responsible for a significant share of SMB security incidents, and yet formal cybersecurity training remains an afterthought in most small business operations.

3. The Cyber Skills Gap

Even when SMB leadership recognizes the need for stronger defenses, the talent simply may not be within reach. The cyber skills gap, or the widening gulf between the demand for qualified cybersecurity professionals and the available supply, hits small businesses disproportionately hard. Enterprise organizations can offer competitive salaries, career development pathways, and the prestige of working on complex, large-scale security challenges.

SMBs can offer none of these things at the same level. The result is a two-tier system in which the businesses most vulnerable to attack are also the least equipped to hire the people who could protect them, a structural disadvantage that no amount of goodwill or awareness alone can bridge.

Critical Technical Hurdles for SMBs

Some particularly technical fronts SMBs need to watch out for, and monitor are:

1. DDoS Trends

Distributed denial-of-service attacks were once the exclusive weapon of sophisticated, well-resourced criminal organizations. That barrier to entry has effectively collapsed. The proliferation of DDoS-for-hire service platforms (sometimes called ‘booter’ or ‘stresser’ services) has placed the ability to knock a business offline squarely in the hands of low-level criminals, disgruntled competitors, or even teenagers with a grudge and a credit card.

For SMBs that depend on e-commerce storefronts, appointment booking systems, or cloud-hosted customer portals, even a brief DDoS attack can translate into significant revenue loss, reputational damage, and operational chaos. Unlike enterprise organizations that can absorb such disruptions through redundant infrastructure and dedicated incident response teams, most small businesses have no continuity plan for weathering a sustained denial-of-service event.

2. Identity as the New Perimeter

As traditional network boundaries have dissolved in the era of remote work and cloud services, identity has emerged as the true frontline of defense. Identity attacks (e.g., credential theft, adversary in the middle interception, and session hijacking) now represent one of the most actively exploited categories of vulnerability facing SMBs.

The strategic answer is a shift toward robust identity and access management platforms, such as Microsoft Entra, which enforce granular access controls, multi-factor authentication, and continuous verification principles aligned with zero trust architecture. However, implementing and maintaining such systems requires both technical expertise and budget commitment: two resources that remain chronically scarce in small business environments.

3. Managing the KEV

The Cybersecurity and Infrastructure Security Agency’s (CISA) KEV catalog serves as an authoritative, regularly updated registry of vulnerabilities that have been confirmed as actively exploited in the wild. For well-resourced security teams, it is an invaluable prioritization tool.

For SMBs, it is an overwhelming and largely inaccessible document. Without dedicated cybersecurity professionals to monitor the catalog, assess applicability to their specific systems, and execute timely patch management, most small businesses have no reliable mechanism for translating threat intelligence into action.

Improving Security Posture

Even for small businesses, posturing should involve:

1. Adopting Zero Trust

For SMBs still operating on implicit trust (i.e., assuming that anyone inside the network is safe), the zero trust model represents an urgent and necessary correction. ‘Never trust, always verify’ is no longer an enterprise luxury; it is a baseline expectation in a threat environment where identity attacks, compromised connected devices, and insider threats can originate from anywhere at any time.

2. Investment and Culture

Purchasing cybersecurity tools is not the same as building a security culture. Lasting protection requires boardroom buy-in: leadership that treats cybersecurity not as an IT expense but as a core business risk. When executives champion security from the top down, budgets follow, training becomes consistent, and employees at every level understand their role in maintaining a resilient security posture.

3. Leveraging Threat Intelligence

Modern threat intelligence platforms give SMBs something previously reserved for large security operations centers: actionable, real-time visibility into emerging threats. By integrating threat intelligence feeds into their defenses, small businesses can anticipate and respond to adaptive malware, infostealer malware, and evolving phishing campaigns before they translate into costly breaches.

Conclusion

The cybersecurity threats facing small businesses today, from AI-driven malware campaigns and ransomware groups to identity attacks, IoT devices, and widening attack surfaces, are real, evolving, and unforgiving. No single tool or policy eliminates the risk entirely. What separates surviving businesses from compromised ones is not perfection: it is the disciplined, continuous commitment to improvement.

Cybersecurity is not a one-time purchase. It is an ongoing practice, and for SMBs, starting that practice today is always better than waiting until tomorrow’s breach forces the conversation.


INTERESTING POSTS

Going Keyless: How Modern Access Control Is Reshaping Building Security

0
Going Keyless: How Modern Access Control Is Reshaping Building Security

Want to learn about going keyless? In this post, I will show you how modern access control is reshaping building security.

The way we secure buildings is changing fast. Traditional metal keys are giving way to smarter, more manageable solutions that give facility managers greater control over who gets in and when.

The Problem With Traditional Keys

Anyone who has managed a large building or multi-site facility knows the headache that comes with physical keys. They get copied, lost, or passed on without authorisation. Every time a key goes missing, you face a costly rekeying process and a potential security gap that can last days or even weeks.

Beyond the cost, there is the administrative burden. Tracking who holds which key, which doors they can access, and whether that access is still valid requires significant time and effort. In high-turnover environments like student housing, co-working spaces, or commercial properties, this quickly becomes unmanageable.

The limitations of mechanical locking systems have pushed many organisations to look seriously at digital alternatives, and the market has responded with increasingly sophisticated options.

What Digital Locking Systems Actually Offer

What Digital Locking Systems Actually Offer

Modern digital locking systems do more than simply replace a metal key with an app or card. They give administrators real-time visibility into access events, the ability to revoke credentials instantly, and the flexibility to set time-based permissions. If a contractor only needs access on Tuesday mornings, the system can reflect exactly that.

One of the most significant developments in recent years is the move toward battery-free or self-powered locking technology. ILOQ has developed a system where the locking cylinder harvests energy from the user’s own interaction, removing the need for wired infrastructure or battery replacements. This dramatically reduces both installation costs and ongoing maintenance.

For large property portfolios, this kind of approach makes scaling up far more practical. There are no cables to run through walls, no electricians needed for every new door, and no service visits just to change a battery.

Choosing the Right System for Your Building

Not every building has the same needs. A listed historic building presents different challenges to a modern logistics warehouse. Before committing to any solution, it is worth assessing a few key factors.

  • How many access points need to be covered
  • Whether the building has existing IT infrastructure that can support integration
  • How frequently user credentials will need to be updated or revoked
  • What level of audit trail is required for compliance purposes

Understanding the fundamentals of Acces control is a useful starting point for any facilities manager or security decision-maker evaluating their options. Getting that foundation right means you can make a more informed choice between cloud-based, on-premise, or hybrid systems.

Digital access technology has matured significantly, and the barriers to adoption are lower than many expect. For organisations still relying on mechanical keys, the question is no longer whether to upgrade, but when.


INTERESTING POSTS

A Clean Domain Name Is No Longer a Trust Signal

0
A Clean Domain Name Is No Longer a Trust Signal

In this post, I will show you that a clean domain name is no longer a trust signal.

For years, it felt like you could spot a trustworthy website by its clean, professional domain name. We learned to avoid suspicious links with strange endings or obvious typos, thinking these were the main clues to danger online.

But the reality has changed, and so have the tactics of cybercriminals. Today, even domains that look perfectly legitimate can be used for phishing or spreading malware. Attackers now register or hijack reputable-looking domains at an unprecedented scale, making it much harder to judge safety at a glance.

This shift means that just seeing a clean URL isn’t enough anymore. In this analysis, we’ll explore why those old signals are no longer reliable and what that means for anyone trying to stay safe online.

Cybercriminals are redefining what a ‘trustworthy’ domain looks like

Cybercriminals are redefining what a ‘trustworthy’ domain looks like

For years, we’ve all been told that a polished domain name signals legitimacy. But cybercriminals have caught on to this habit and are using it to their advantage with surprising skill.

Attackers now create websites with domains that look just like familiar brands or trusted services, sometimes even blending in so well that it’s nearly impossible to spot the difference. In fact, these days you can search for something as ordinary as https://arabiccasinos.guide/ and still need to pause and consider whether everything is truly as it appears.

It’s not just about new domains either. Criminals often take over old, established domains—ones with years of clean history—and use them to launch phishing attacks or distribute malware. With 85% of malware campaigns now taking advantage of compromised legitimate domains, even seasoned internet users can find themselves at risk.

This evolution in online deception means that both individuals and businesses have to question what safety looks like online. Relying on a clean, professional URL as your main trust signal simply isn’t enough anymore. The gap between what appears trustworthy and what actually is has never been wider, and that’s exactly where attackers want you to let your guard down.

The rise of malicious and compromised domains

The trust gap isn’t just theoretical—it’s a daily reality. In late 2023 alone, an astonishing 1.5 million phishing domains were detected, showing just how aggressively attackers are exploiting the basic assumptions we all make about online safety.

And it’s not just about new, suspicious-looking websites. Around 85% of malware campaigns now use compromised legitimate domains, so even sites you’ve visited before or that look completely normal might suddenly become vehicles for fraud or data theft.

What makes this problem even harder is how attackers intentionally mimic the look and feel of trusted brands. They know people are scanning for familiar names and polished designs, so they put in the work to blend in. Sometimes, these malicious sites are so convincing that even experienced security professionals get caught off guard.

It’s become clear that relying on a domain’s appearance offers little real protection. Attackers are counting on our habits, and as the numbers show, they’re succeeding at scale. If you want to dig deeper into how these domains are weaponized, the Study on phishing domains details just how closely new registrations are tied to phishing strategies.

Users fall for surface signals—and attackers know it

This shift in domain abuse has real consequences for how people make decisions online. Most of us have gotten used to quickly scanning for professional design, familiar logos, and that reassuring clean domain—it’s what helps us move fast and feel safe.

But attackers have learned to build sites that mimic those cues perfectly. They know that if a site looks just right, most visitors won’t pause to question it. That’s not a coincidence—it’s calculated.

Behavioral studies keep showing that people are much more likely to trust something that “feels” right visually, even when technical warning signs are present. The subtle comfort of a polished domain or a known brand can override instincts to double-check before clicking or entering information.

Phishing attacks increasingly succeed not because victims miss a misspelled URL, but because the entire site seems legitimate at a glance. Attackers aren’t just targeting the careless or untrained—they’re betting on the natural human tendency to trust what looks familiar.

It’s clear that old advice around spotting typosquatting or weird domains just isn’t enough. The real danger now is that attackers are using everything we’ve been taught to trust, turning it back against us.

Rethinking domain-based security strategies

So if attackers are using clean domains to their advantage, just relying on a site’s appearance isn’t enough anymore. This new reality pushes us to change how we think about online safety—because no domain, no matter how established, is immune to compromise.

Organizations can’t afford to stick with surface-level checks. They need to layer their defenses with continuous monitoring of domains, stronger authentication methods, and regular training that goes beyond simply spotting misspelled URLs. The sheer scale of the threat is hard to ignore—recent data shows that 85% of malware campaigns now use compromised legitimate domains, so even “safe” sites can be weaponized.

Modern security solutions focus on how a site behaves, not just how it looks. That means checking for suspicious activity, validating user identities, and making sure there’s a backup plan if something gets through. For businesses, it’s about being proactive: monitoring domain registrations, using multifactor authentication, and preparing for the possibility of a breach, not just hoping it never happens.

For everyday users, it’s time to build habits that look past the URL. This includes verifying where information really comes from, using tools that add extra layers of protection, and staying informed about new threats. If you want to go deeper, you can read more about domain protection strategies that are working against today’s threats.

Looking past the URL: smarter detection and realistic caution

Looking past the URL: smarter detection and realistic caution

As we push for stronger defenses, it’s clear that simply checking for a clean domain is no longer enough. Modern security tools now go much deeper, scanning for suspicious behaviors and unusual patterns that might signal a threat—regardless of how the URL looks on the surface.

Behind the scenes, these tools analyze how websites interact with users, what information they request, and even how they’re connected to other domains. This kind of dynamic detection is helping to catch threats that would easily slip past old-fashioned, visual checks.

Even the biggest companies can get caught off guard. Some of the world’s largest organizations have gaps in their domain management, showing that no one is immune from these evolving risks. If you’re curious about the scale of this issue, the Domain security report highlights just how widespread these lapses can be.

For individuals, the takeaway is simple but critical: don’t let a slick URL lull you into a false sense of security. The safer path is to treat every site with a bit of healthy skepticism, and to make verification—not just visual judgment—your go-to habit online.

The only safe approach: proactive, not passive, online vigilance

That bit of healthy skepticism isn’t just wise—it’s necessary in a world where even the most polished domains can be weaponized. Relying on old habits, like trusting a clean URL or familiar branding, just isn’t enough anymore.

Instead, it’s time to browse with intention. This means pausing before sharing information, staying alert for anything that feels off, and using tools that help spot threats behind the scenes. Knowing how to identify phishing websites can turn caution into action, making you less of a target for evolving scams.

Online safety now depends on curiosity and double-checking, not just trusting what looks right. Every site deserves a second look, because even the cleanest domains are fair game for attackers today.


INTERESTING POSTS

When Roof Repairs Are Enough and When They Are Not for Long-Term Property Protection

0
When Roof Repairs Are Enough and When They Are Not for Long-Term Property Protection

In this post, I will talk about when roof repairs are enough and when they are not for long-term property protection.

A roof is constantly exposed to environmental stress, making it one of the most vulnerable parts of any property. Over time, even durable roofing systems begin to show signs of wear, ranging from minor damage to more serious structural concerns. Understanding how to respond to these issues is essential for maintaining long-term protection.

Many property owners face a common dilemma when roofing problems appear. Should they invest in repairs, or is it time to consider a more comprehensive solution? The answer depends on the extent of the damage, the age of the roof, and how frequently issues are occurring.

Knowing when Roof Repairs are sufficient and when they are no longer effective can prevent unnecessary expenses and protect the building from escalating damage. With insights from professionals like Emerald Roofing and Siding, property owners can make informed decisions that support long-term stability.

Understanding the Purpose of Targeted Roof Repairs

Roof repairs are designed to address specific issues without replacing the entire system. These fixes are ideal when damage is limited to a small area and the rest of the roof remains in good condition.

For example, replacing a few missing shingles or sealing a minor leak can restore the roof’s performance quickly. In these cases, repairs are both cost-effective and efficient.

However, repairs are only effective when they address isolated problems. If damage is widespread or recurring, temporary fixes may not provide lasting protection.

Signs That Repairs Are Still a Practical Solution

Localized Damage in Specific Areas

When damage is confined to a small section of the roof, repairs are often the best approach. Issues such as a few cracked shingles or minor flashing problems can be resolved without major disruption.

These targeted fixes help extend the life of the roof while maintaining its overall performance.

Property owners who act quickly in these situations can prevent minor issues from spreading into larger concerns.

Recent Installation with Minimal Wear

Roofs that are relatively new typically benefit more from repairs than replacement. Since the majority of the system is still in good condition, addressing isolated damage helps preserve the investment.

In these cases, Roof Repairs serve as a maintenance strategy that supports long-term durability.

When Repairs Begin to Lose Effectiveness

Frequent Recurring Issues

If roofing problems continue to appear despite repeated repairs, it may indicate deeper structural concerns. Constant patchwork can become costly and time-consuming without resolving the root cause.

Recurring leaks or repeated shingle damage often suggest that the roofing system is reaching the end of its lifespan.

Professionals at Emerald Roofing and Siding often recommend evaluating long-term solutions when repairs no longer provide consistent results.

Widespread Material Deterioration

As roofing materials age, they begin to lose their ability to protect the structure effectively. Shingles may curl, crack, or become brittle, while flashing can weaken over time.

When these issues affect large portions of the roof, repairs become less practical. Addressing individual sections will not restore the overall integrity of the system.

At this stage, continuing to rely on repairs may only delay necessary improvements.

The Hidden Risks of Delaying Major Decisions

Moisture Penetration Beneath the Surface

Roof damage often extends beyond what is visible from the outside. Water can travel through layers of the roofing system, affecting insulation and structural components.

By the time interior signs such as stains or leaks appear, moisture may have already caused significant damage.

Delaying action in these situations increases the risk of costly structural repairs.

Impact on Interior Spaces

Water intrusion does not remain confined to the roof. It can spread into ceilings, walls, and even electrical systems, creating additional repair challenges.

Addressing roofing issues early helps prevent damage from reaching these interior areas.

Ignoring warning signs often leads to more extensive and expensive restoration work.

READ ALSO: How Fence Repairs Help Maintain Safety and Prevent Costly Structural Damage Over Time

Comparing Short-Term Fixes and Long-Term Value

Cost Considerations Over Time

While repairs are generally less expensive upfront, repeated fixes can add up over time. Property owners who rely on continuous repairs may eventually spend more than they would on a long-term solution.

Evaluating the total cost of ongoing maintenance is important when deciding how to proceed.

In some cases, investing in a more comprehensive solution provides better value and stability.

Reliability and Peace of Mind

A roof that requires frequent attention can create ongoing uncertainty. Property owners may worry about leaks during storms or unexpected damage during seasonal changes.

Reliable roofing solutions reduce this stress by providing consistent protection.

Working with experienced professionals ensures that decisions are based on long-term performance rather than short-term convenience.

How Preventative Maintenance Supports Better Decisions

Preventative maintenance plays a key role in identifying roofing issues before they become severe. Regular inspections allow professionals to detect early signs of wear and recommend appropriate solutions.

By addressing problems early, property owners can extend the life of their roof and reduce the likelihood of major repairs.

Maintenance also provides valuable insight into the overall condition of the roofing system, helping guide future decisions.

Environmental Factors That Influence Repair Decisions

Climate conditions have a significant impact on roofing performance. Exposure to heavy rain, strong winds, or temperature fluctuations can accelerate material wear.

Roofs in harsher environments may require more frequent repairs or earlier replacement compared to those in milder conditions.

Understanding these factors helps property owners make more informed decisions about when repairs are sufficient and when larger improvements are necessary.

The Importance of Professional Evaluation

Accurately assessing roof condition requires experience and expertise. Some issues may appear minor but could indicate deeper structural problems.

Professional inspections provide a comprehensive understanding of the roof’s condition and help identify the most effective course of action.

Emerald Roofing and Siding offers detailed evaluations that allow property owners to determine whether repairs will provide lasting results or if a more extensive solution is needed.

Balancing Immediate Needs with Future Planning

Roofing decisions should consider both current issues and long-term goals. While repairs may resolve immediate concerns, they should also align with the overall condition of the roof.

Planning ahead allows property owners to avoid sudden emergencies and manage costs more effectively.

By taking a proactive approach, it becomes easier to maintain a reliable roofing system over time.

Extending Roof Lifespan Through Smart Choices

Every roofing system has a natural lifespan influenced by materials, installation quality, and environmental exposure. Making informed decisions about repairs helps maximize this lifespan.

Addressing small issues promptly prevents them from developing into larger problems that shorten the roof’s durability.

Strategic use of Roof Repairs can extend performance when applied at the right time and under the right conditions.

Conclusion

Roofing systems require careful attention to maintain their protective function. While repairs are an effective solution for minor and localized damage, they are not always sufficient for long-term protection.

Recognizing when Roof Repairs are appropriate and when they are no longer effective helps property owners avoid unnecessary costs and prevent structural damage. By evaluating factors such as damage extent, roof age, and repair frequency, it becomes easier to make informed decisions.

With guidance from Emerald Roofing and Siding, property owners can approach roofing challenges with confidence, ensuring their investment remains protected and their building continues to perform reliably for years to come.


INTERESTING POSTS