Home Blog Page 29

Why Traditional Keyword Targeting Doesn’t Fit ChatGPT Advertising

0
Why Traditional Keyword Targeting Doesn't Fit ChatGPT Advertising

In this post, I will show you why traditional keyword targeting doesn’t fit ChatGPT advertising.

The use of keywords has been a key building block of digital advertising for years. A person enters a website and types in the words “running shoes” and clicks on an ad for running shoes. Simple, right?

However, search engines have revolutionized this, as people typically typed out short phrases which would bring up what they were looking for. Advertisers would be able to recognize those terms, bid on them and develop ads based on them.

The interaction between humans and AI is different, however. People don’t have to type two or three words, they can tell it in full, explain what’s going on and give lots of context.

Discussions are not as simple as key words

Suppose a person goes in search of a laptop. On Google, they may search for “best laptop for students.

They could say, “I am a university student and am studying graphic design, and I need a laptop that I can use for Adobe illustrator and Photoshop, but I do not have much money to spend. What do I have to look out for?

The user has already expressed his/her interests, needs, budget and purpose. The conversation may convey a lot more than the traditional keyword “laptop for students.

So, is it still time for advertisers to concentrate on keywords? Probably not.

Be in the right intent than using the right words

Rather than asking that question, traditional ads should rather inquire, “Which keywords did they input?

But AI-driven advertising should be focused on a more pertinent query: “What is this person trying to achieve?”

Two individuals may have two different terms for the same answer. One person could wonder about the cheap accounting software, another could be wondering how to handle the invoicing of a small business.

Not exactly the same, but the meaning might be nearly the same.

Knowing what they want enables marketers to send a message that resonates more with the audience than a match for a key word.

The context changes in the Advertising Game

The difference between traditional search and conversational AI is one of the largest: Context.

With a typical search, an advertiser might be aware of the query, but not have a lot of information about why someone might be searching. When you speak to a user, you will usually be able to hear the reason behind the user’s question.

Context can tell you what the customer is really interested in.

A person seeking a fitness plan could discuss their fitness plan, objective, experience level or favorite type of exercise. Those pieces of information can help to create a much more relevant marketing message.

Conversational Advertising 

If there is a conversation in the audience, the ad should not be completely out of the conversation.

It’s here that marketers should rethink their creative strategy.

Brands can prioritize helpful messaging over just short headlines and promotional language to answer common questions and concerns. The aim of the game is to make the brand “live” in the user’s environment.

Would you prefer to get some sales pitch from someone asking for advice or a helpful recommendation that solves your problem?

Small niches | targeted keywords 

Longer and more specific queries are also much more significant with conversational AI.

Users will be able to pose extremely detailed questions which are not easily guessed by keyword research. The following questions can uncover particular pain points and purchase intentions.

This is a chance for marketers to start considering other popular keywords.

Rather than focusing on what words are searched the most, businesses can tap into customers’ common questions prior to making a purchase. These questions can then inform the advertising messaging, landing pages and content.

How Can Companies Change?

Don’t assume that you have to give up on keyword research altogether. Even keywords are relevant, particularly on old fashioned search engines.

The better way to do it is to mix in audience intent, customer questions and conversational context with the knowledge of the keywords.

Businesses need to understand customers’ problems as expressed in their own words. What areas of the story do they want to know more about? What is it that is holding you back from purchasing? What are some comparisons they make prior to selecting a product?

Impact of ChatGPT ads

ChatGPT Ads are just a sign of a new paradigm in advertising, one that moves beyond keywords to intent and context.

“That’s about matching a person and not an exact search phrase, and it’s a shift in mindset that marketers will need to make them more flexible,” he says.

It doesn’t imply that keywords are no longer of any value. It just means that they’re no longer in full view.

For businesses considering ChatGPT Ads, this is the opportunity to shift their focus from just using keyword lists to embracing conversations.

Final Thoughts

The traditional keyword targeting was based on searches. Conversational AI has a focus on questions, context, and intent.

This is the reason marketers must never depend on the same practices and techniques forever.

No longer are searchers restricted to typing a few words into a search box. They can describe their problems, ask follow-up questions and compare different options in one conversation, they can explain what they want.

What ads customers search for, not necessarily the words customers type, may be as important to the future of advertising as what ads they actually click on.


INTERESTING POSTS
Windows Security and Setup Guide for Chinese-Language Messaging Apps

0
Windows Security and Setup Guide for Chinese-Language Messaging Apps

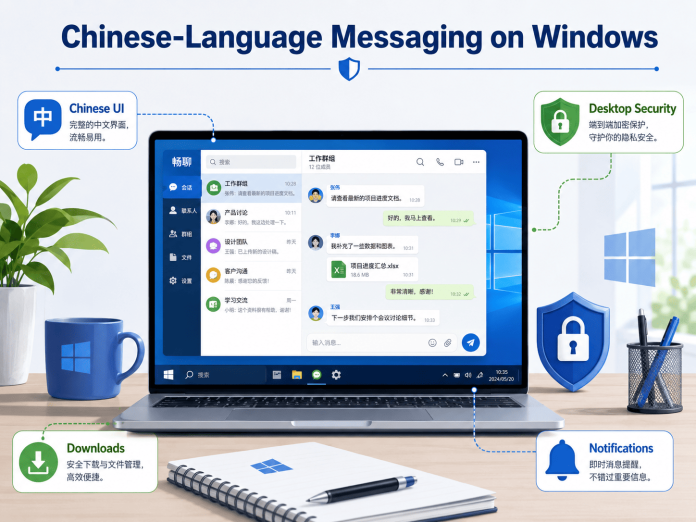
In this post, I will discuss Windows Security and Setup Guide for Chinese-Language Messaging Apps.

Chinese-speaking Windows users often need to solve three separate problems at the same time: finding the correct desktop client, downloading it through a trustworthy path, and configuring an interface that is comfortable to use in Chinese. Treating those tasks as one vague “Chinese version” search can make troubleshooting and source verification harder.

A user can have the correct Windows client but the wrong interface language, or a helpful Chinese-language guide that points to an installer whose origin still needs to be verified. Installation, localization, and software security should therefore be checked independently.

The most reliable setup sequence is to verify the Windows package first, install it normally, configure the supported Chinese interface second, and then review privacy, downloads, notifications, startup behavior, updates, and active sessions.

This guide explains that sequence for Windows users who want a Chinese-language messaging environment without weakening normal software-security checks.

Choose the Correct Windows Desktop Edition First

Before changing language settings, users need to make sure they have the correct desktop application.

Messaging platforms may offer several access methods, including:

  • Standalone Windows installers
  • Microsoft Store editions
  • Browser-based interfaces
  • Portable versions
  • Other desktop builds

These options can provide similar communication features, but they are not always identical in terms of updates, local storage, startup behavior, or system integration.

For users searching for telegram 電腦版中文, the search intent combines two requirements: a genuine Windows desktop client and a usable Chinese-language interface. Verify the desktop package first, then apply the supported language configuration rather than assuming a separate modified installer is required.

The correct setup sequence is usually:

  1. Verify the software source.
  2. Select the correct Windows desktop version.
  3. Install the application.
  4. Confirm that it launches normally.
  5. Configure the Chinese-language interface.
  6. Review notifications, storage, and security settings.

This sequence makes troubleshooting easier because users can identify whether a problem comes from installation or localization.

Separate Windows Installation From Chinese Localization

A common misconception is that a “Chinese version” must always be a completely different software package.

In many cases, the desktop application itself supports multiple interface languages. The same Windows installer can later be configured for English, Traditional Chinese, Simplified Chinese, or another supported language.

This means users should be cautious when unfamiliar websites claim that a special modified installer is required only to obtain a Chinese interface.

A safer model is:

Install the normal Windows desktop client first. Then configure the interface language through the software settings or another documented localization method.

This reduces the need to rely on modified third-party packages.

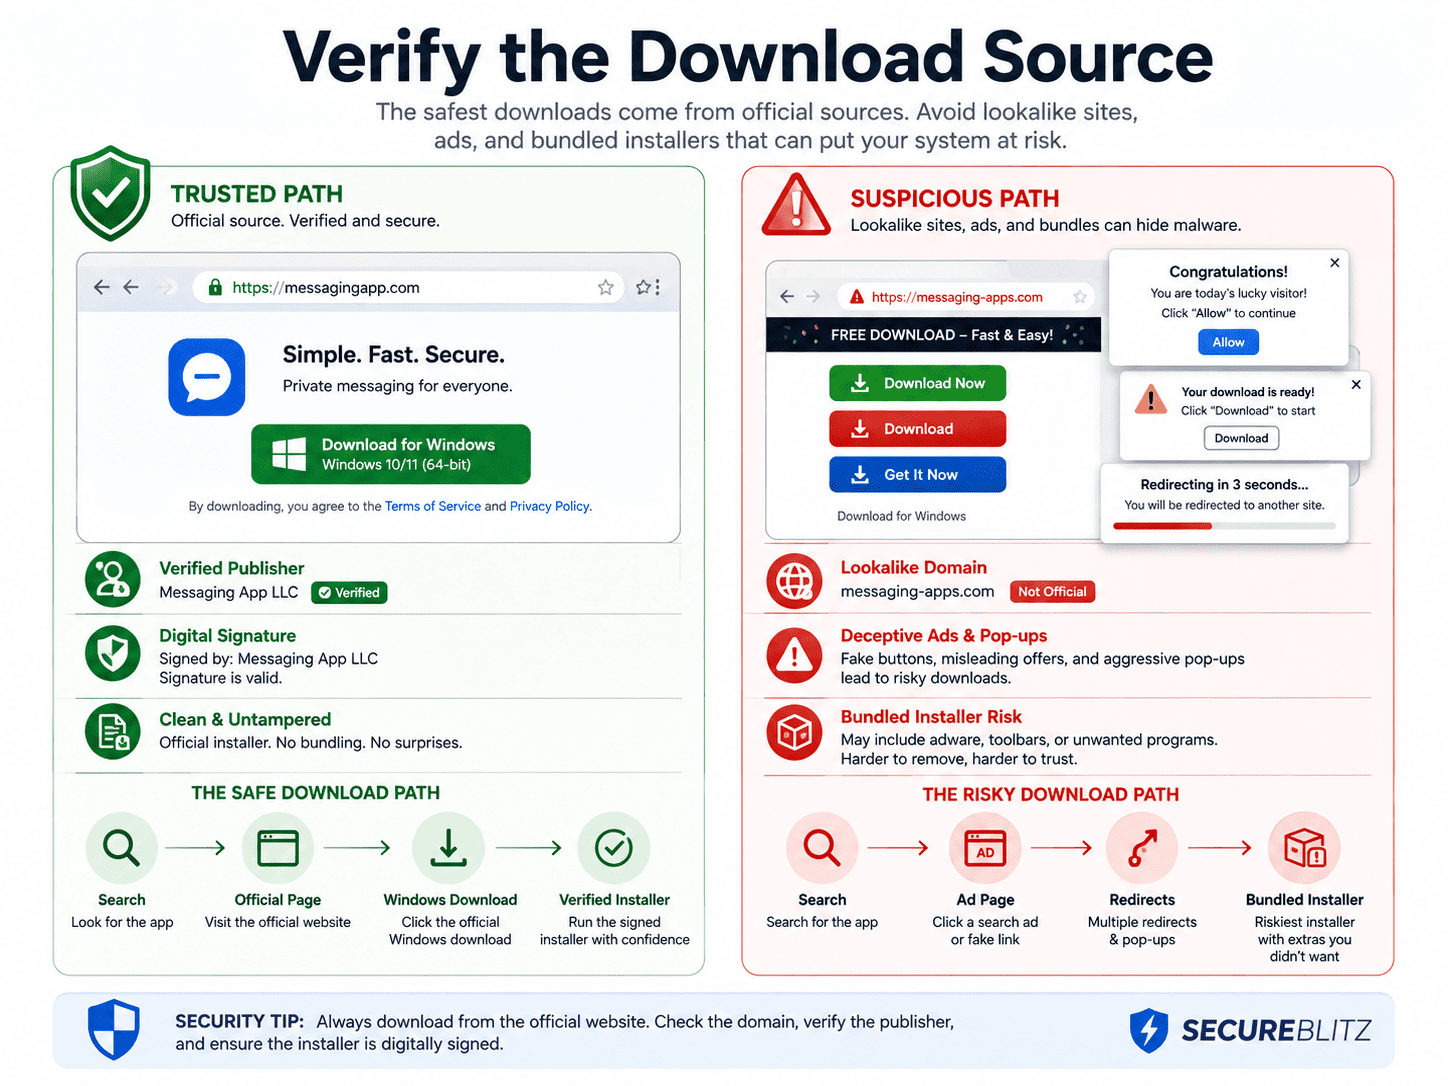
Verify the Windows Download Source Before Installation

Verify the Windows Download Source Before Installation

Language convenience should never replace source verification.

A page may provide useful Chinese-language instructions while still linking to a third-party installer. Users should evaluate the actual download path separately.

Before downloading, check:

  • Domain spelling
  • Page consistency
  • Download destination
  • Installer filename
  • Publisher information
  • Unexpected redirects
  • Additional bundled software

Users researching 电报电脑版下载 should first confirm that the selected file is actually intended for Windows desktop use. After that, check the download path, filename, publisher information, and installer properties before installation; a Chinese-language page by itself does not verify the software source.

The key question is not only:

Does this page explain the software in Chinese?

It should also be:

Where does the Windows installer actually come from?

Inspect the Installer Before Running It

Once the Windows installer has been downloaded, users should inspect the file before opening it.

Check the filename

The filename should look consistent with the software being installed.

Be cautious if it contains:

  • Random characters
  • Unrelated product names
  • “Download Manager”
  • Unknown utilities
  • Suspicious version labels

Review file properties

Right-click the file and select Properties.

Useful information may include:

  • Product name
  • File description
  • Publisher
  • Version
  • Digital signature

If the metadata does not match the expected application, installation should stop until the difference is understood.

Check the Digital Signature

Windows digital signatures can provide another verification layer.

When available:

  1. Right-click the installer.
  2. Open Properties.
  3. Select the Digital Signatures tab.
  4. Review the signer.
  5. Open the signature details.
  6. Confirm that Windows reports the signature as valid.

A valid signature does not guarantee that every software-related risk has been eliminated, but it helps users identify the publisher associated with the package.

For frequently used desktop software, organizations can document the expected publisher name as part of their internal setup guide.

Scan the File With Windows Security

Before installation, users should scan the installer with Microsoft Defender or the organization’s endpoint-security software.

A basic process can include:

  1. Right-clicking the downloaded file.
  2. Selecting the available security scan.
  3. Reviewing the result.
  4. Investigating warnings before execution.

Users should also take Microsoft Defender SmartScreen warnings seriously.

If Windows displays an unexpected warning, the safest response is to pause and verify the source rather than immediately bypassing the alert.

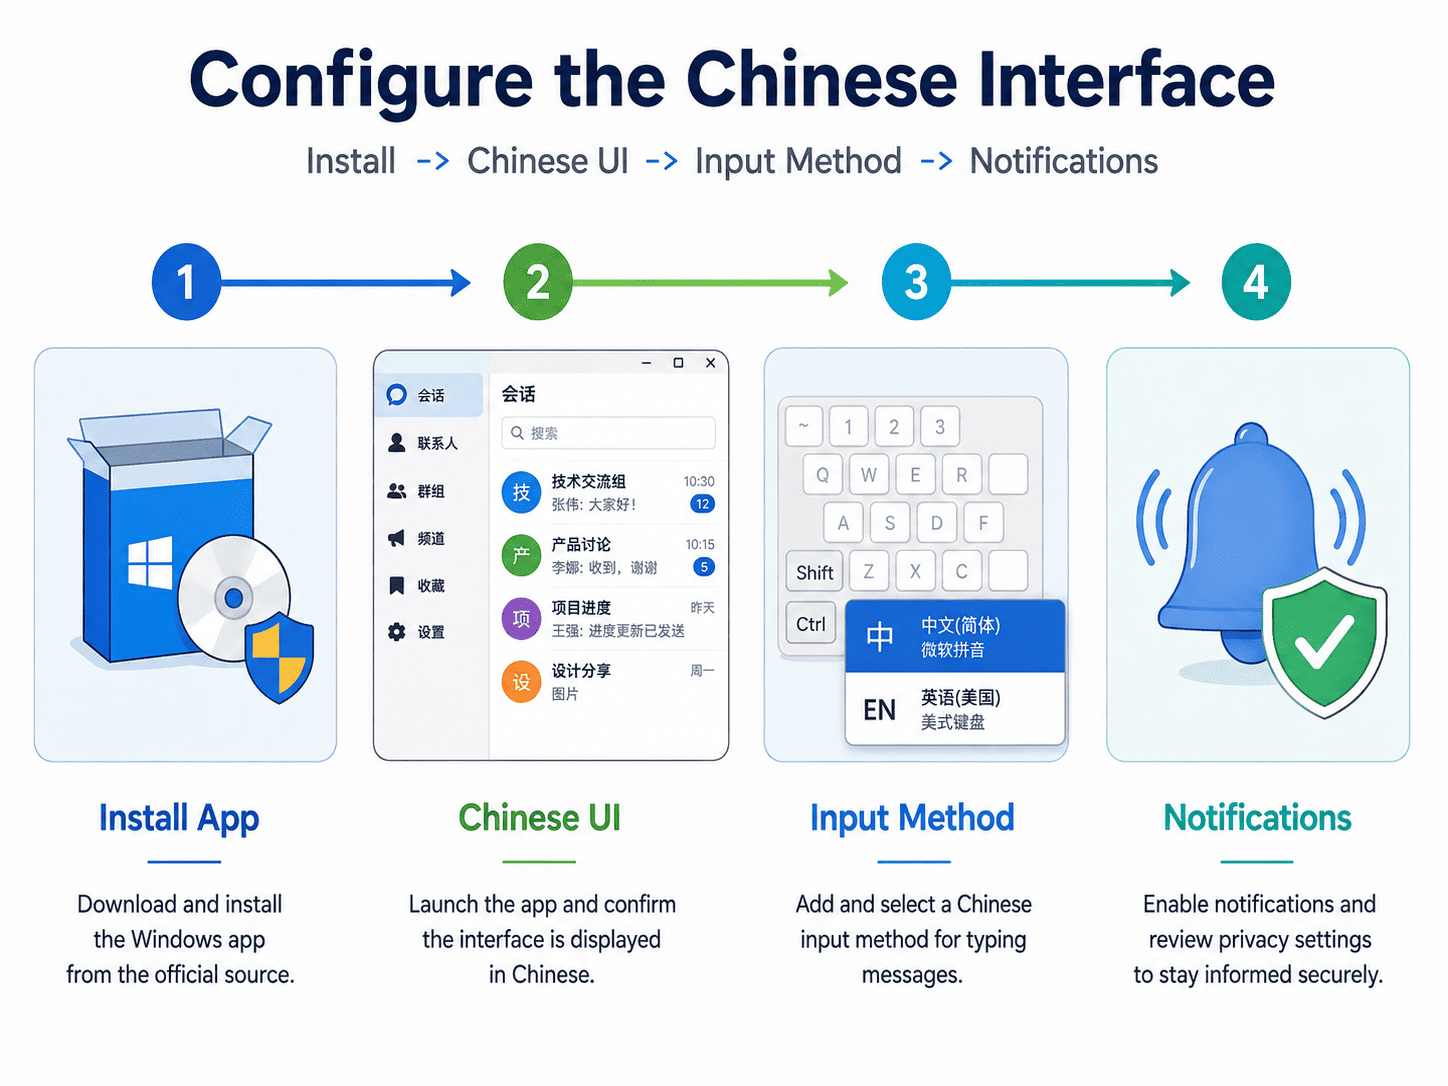
Configure the Chinese Interface After the Client Is Installed

Configure the Chinese Interface After the Client Is Installed

Once the desktop client is installed successfully, users can move to interface localization.

A typical process may involve:

  1. Opening application settings.
  2. Locating language or interface options.
  3. Selecting the preferred Chinese-language option.
  4. Restarting the client if necessary.
  5. Confirming that menus and settings display correctly.

The exact menu location can change as software updates are released, so users should rely on current instructions rather than old screenshots alone.

Organizations that support multiple Chinese-speaking regions should also decide whether they prefer:

  • Traditional Chinese
  • Simplified Chinese
  • English
  • Different defaults for different teams

The best choice depends on the actual users rather than technical capability alone.

Check Chinese Character Rendering

After localization, users should verify that Chinese characters display correctly throughout the application.

Check:

  • Menu labels
  • Group names
  • Notifications
  • Search results
  • File names
  • Contact names
  • Settings pages

Problems can sometimes occur because of unusual Windows language settings, missing fonts, remote desktop environments, or legacy system configurations.

If the interface language looks correct but some text appears incorrectly, the issue may be related to Windows rather than the messaging application itself.

Configure the Windows Input Method

The application interface language and the Windows keyboard input method are separate settings.

A Chinese-language interface does not automatically configure Chinese text input.

Users who regularly type in Chinese should confirm that Windows has the appropriate keyboard or input method enabled.

A basic Windows configuration may include:

  • Adding the required Chinese input method
  • Selecting Traditional or Simplified input preferences
  • Learning the keyboard shortcut for switching input methods
  • Checking punctuation behavior
  • Testing Chinese typing inside the messaging application

This is especially important for users who switch frequently between English and Chinese conversations.

Review Notification Settings

A secure and usable desktop setup should include notification configuration.

Messaging clients can display:

  • Sender names
  • Message previews
  • Group names
  • File information
  • Notification sounds

In shared offices or public environments, message previews may reveal more information than users expect.

Consider configuring:

  • Direct-message alerts
  • Group notifications
  • Sound behavior
  • Message-preview visibility
  • Windows notification permissions
  • Focus Assist behavior

Users who frequently share their screen during meetings should pay particular attention to notification previews.

Set a Dedicated Download Folder

Desktop messaging applications can generate large numbers of local files.

Users may receive:

  • PDFs
  • Images
  • Documents
  • Spreadsheets
  • Presentations
  • Archives
  • Other attachments

A dedicated folder can make these downloads easier to manage.

For example:

Downloads\Messaging Files

or:

Documents\Messaging Downloads

This helps users:

  • Locate files faster
  • Scan suspicious files
  • Remove old downloads
  • Separate messaging files from browser downloads
  • Move important documents into permanent storage

The messaging download folder should be treated as temporary working storage rather than a long-term archive.

Control Automatic Downloads

Automatic file downloads can be convenient, but they should be configured intentionally.

Users may choose to allow automatic downloads for:

  • Small images
  • Common documents
  • Trusted workgroup content

while requiring manual approval for:

  • Large files
  • Archives
  • Executable files
  • Unknown file types

This reduces storage clutter and gives users more control over what is written to the computer.

Be Careful With Files Received Through Messages

Installing a verified desktop client does not make every received file safe.

Users should still be cautious with:

  • Executable files
  • Unexpected archives
  • Unknown links
  • Documents from unfamiliar contacts
  • Files that do not match the conversation context

Software security and content security are separate layers.

A trusted application can still be used to deliver unsafe files if a malicious or compromised account sends them.

Review Startup Behavior

Many desktop messaging applications can start automatically when Windows launches.

This is useful for users who depend on the software throughout the workday, but it may not be necessary for everyone.

Users should decide whether automatic startup is appropriate.

Automatic launch can be useful when:

  • Messaging is a core work tool
  • Immediate communication is important
  • Users rely on desktop notifications

Manual launch may be preferable when:

  • Messaging is used occasionally
  • Users want fewer startup applications
  • Focused work periods are important

Teams should define a recommended baseline while still allowing reasonable personalization.

Keep the Desktop Client Updated

Updates may contain:

  • Security fixes
  • Stability improvements
  • New features
  • Interface changes
  • Windows compatibility improvements

Users should obtain updates through trusted mechanisms such as:

  • The application’s built-in updater
  • An approved store
  • A verified download source
  • An organization-managed deployment process

They should avoid searching random third-party sites for newer installers.

For organizations, update testing can be useful before a major version is deployed across many Windows PCs.

Recheck Language Settings After Major Updates

Software updates can occasionally change interface layouts or localization settings.

After a major update, users should confirm:

  • Chinese interface remains active
  • Menus display correctly
  • Input methods still work
  • Notifications behave normally
  • Download folders remain unchanged
  • Startup preferences remain correct

If support documentation relies heavily on screenshots, it may also need updating after interface changes.

Review Active Sessions

Desktop messaging clients often remain signed in for long periods.

Users should periodically review active sessions, especially after:

  • Reinstalling Windows
  • Replacing a computer
  • Using remote desktop environments
  • Accessing a shared workstation
  • Losing control of an old device

Old or unfamiliar sessions should be closed.

Account security should be considered part of the desktop setup process, not a separate concern.

Avoid Unknown “Chinese Edition” or Repacked Installers

Users may encounter websites offering specially modified “Chinese” editions of popular software.

These packages deserve extra caution.

A modified installer may:

  • Include unofficial changes
  • Add bundled software
  • Remove update mechanisms
  • Change default settings
  • Introduce unknown components

If the standard desktop application already supports localization, a separate modified installer may not be necessary.

Whenever possible, users should prefer:

  1. A verified Windows desktop package
  2. A documented localization process
  3. Normal application updates

This approach is easier to verify and maintain.

Standardize the Setup Across Multiple Windows PCs

Organizations with several Chinese-speaking users can reduce support complexity by creating a simple standard configuration.

A deployment guide can define:

  • Approved Windows client
  • Download source
  • Expected publisher
  • Preferred interface language
  • Notification defaults
  • Download folder
  • Startup behavior
  • Update method
  • Session-security practices

This makes onboarding easier and reduces differences between users.

Standardization does not mean removing all personal preferences. It simply establishes a consistent technical baseline.

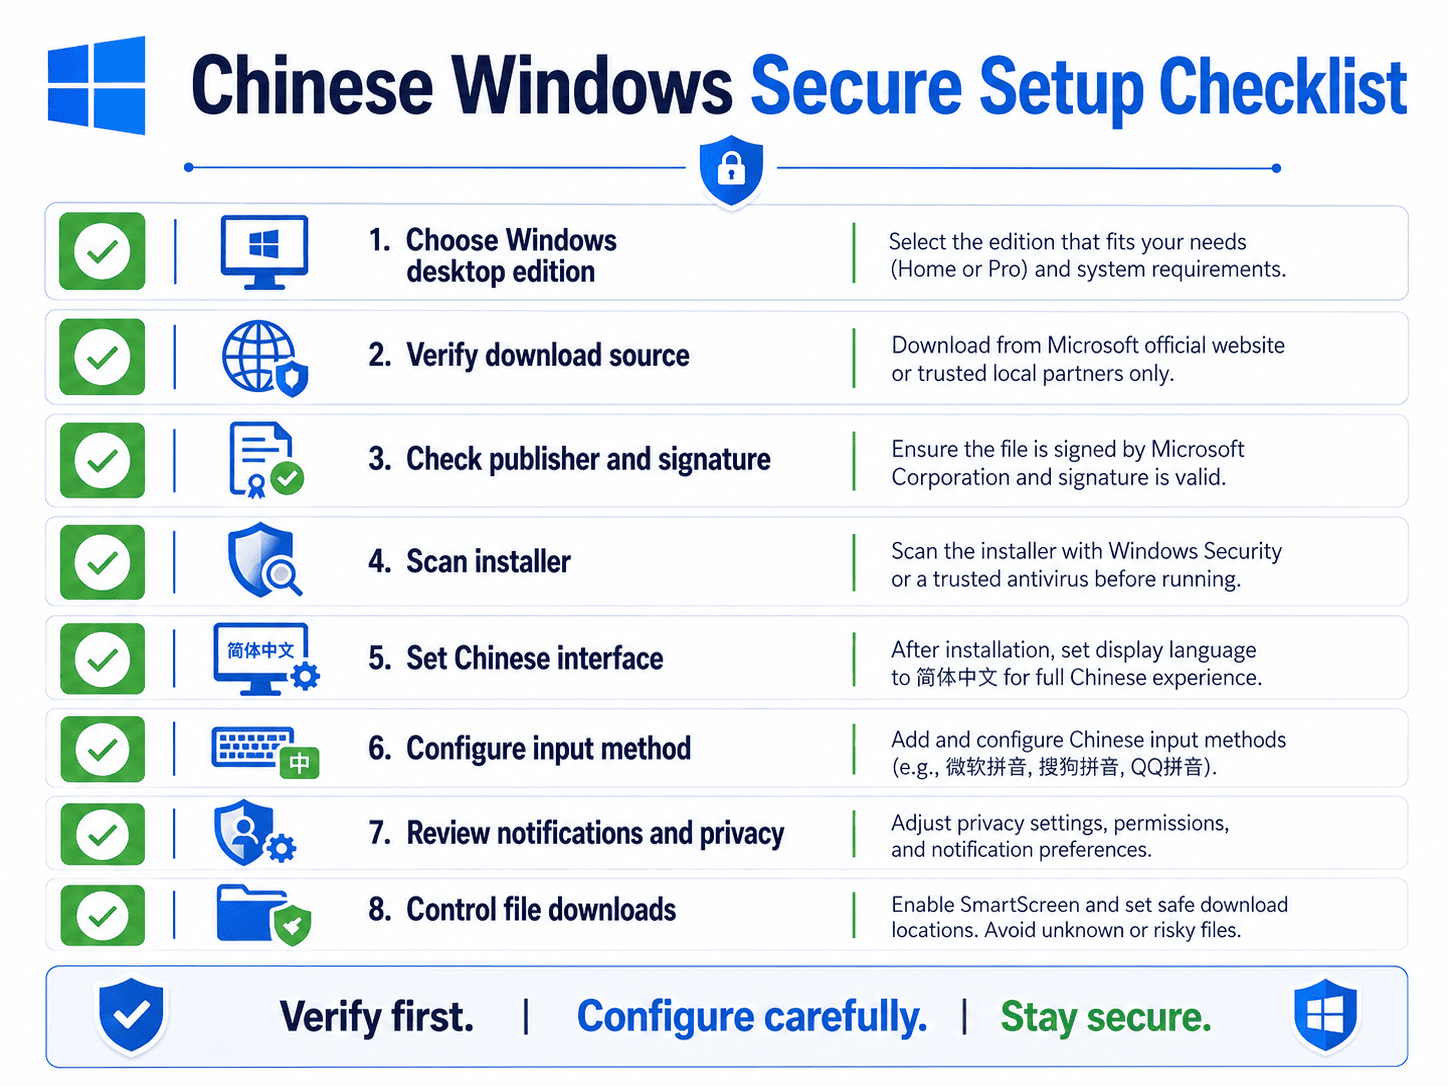
A Practical Chinese-Language Windows Setup Checklist

A Practical Chinese-Language Windows Setup Checklist

Before installation

  • Confirm the correct desktop edition.
  • Verify the download source.
  • Check the domain.
  • Review the installer filename.
  • Inspect publisher information.
  • Check the digital signature when available.
  • Scan the file.

During installation

  • Follow the normal Windows installation process.
  • Avoid unrelated bundled software.
  • Review installation prompts.
  • Confirm the installed version.

Localization

  • Open interface settings.
  • Select the preferred Chinese-language option.
  • Restart if required.
  • Verify Chinese character rendering.
  • Configure Windows input methods.

Desktop configuration

  • Set notification preferences.
  • Choose a download folder.
  • Review automatic downloads.
  • Configure startup behavior.
  • Check update settings.

Security

  • Review active sessions.
  • Use Windows Security.
  • Be cautious with received files.
  • Avoid unknown modified installers.
  • Keep the client updated.

Final Setup and Security Takeaways

A dependable Chinese-language messaging setup on Windows requires more than translating the interface.

The setup process should combine:

  • Correct desktop software selection
  • Verified download sources
  • Installer inspection
  • Chinese-language configuration
  • Windows input methods
  • Safe notification settings
  • Controlled file downloads
  • Reliable updates
  • Session security

Localization should never be used as a reason to bypass source verification or install an unfamiliar modified package.

A safer pattern is to obtain a verified Windows desktop client first, confirm that it runs normally, and then configure the supported Chinese interface and Windows input settings.

When download verification, localization, file handling, updates, and session security are treated as one repeatable workflow, the desktop environment becomes easier to maintain and less dependent on risky shortcuts.


INTERESTING POSTS
Using Seedance 2.5 Without Creating a Security Problem

0
Using Seedance 2.5 Without Creating a Security Problem

In this post, I will talk about using Seedance 2.5 without creating a security problem.

Generative video often enters a company through the creative team. Someone needs a campaign concept by Friday, sees a convincing demo, opens a browser, and starts uploading reference material. The test may look harmless. From a security perspective, however, it can involve customer footage, employee faces, unreleased product designs, brand assets, voice recordings, and a new cloud account—all before IT knows the tool exists.

That does not mean a company should ban the technology. It means the company needs to treat AI video as a production system rather than a novelty. A safe Seedance 2.5 workflow starts before the prompt and continues after the export.

This guide describes a practical control set for teams evaluating Seedance 2.5 through ClipDance’s browser-based creative platform. Security settings, retention policies, and data practices still need to be checked during procurement.

Why AI video changes the threat model

A conventional video project already contains valuable files. Generative video adds a less familiar problem: reference media is both production input and potentially sensitive data.

A single upload can reveal more than its owner intended. A product photograph may expose a prototype. A screen recording can show customer information in the background. A voice sample may contain biometric characteristics. A portrait can be used to create a plausible performance the person never gave. Even a harmless-looking location image may identify a private office or home.

The output presents a second set of risks. A realistic clip can be mistaken for documentary footage, forwarded without its original caption, or reused in a phishing campaign. A team may also publish a generated logo, person, claim, or scene it does not have the right to use.

NIST’s voluntary AI Risk Management Framework offers a useful way to organize this work: govern the use, map the context and risks, measure what can go wrong, and manage the remaining risk. For a marketing team, that can be translated into a short operating procedure rather than a new bureaucracy.

Start with a use-case boundary

The fastest way to make AI video safer is to decide what it is and is not allowed to do.

Low-risk uses may include abstract backgrounds, fictional environments, stylized product mood films, storyboard tests, and internal concept previews. Higher-risk uses include recognizable people, health or financial claims, political subjects, children, customer stories, news-like footage, safety demonstrations, and any material that could influence an important decision.

A written boundary should answer four questions:

  1. Which teams may generate video?
  2. Which kinds of source files may they upload?
  3. Which uses require legal, security, or executive review?
  4. Which uses are prohibited regardless of deadline?

Do not write the policy around one model name. Tools change. Write it around data classes and consequences. “No confidential product imagery in unapproved external tools” will remain useful long after a particular interface changes.

Classify every input before upload

Most preventable exposure happens at the input stage. A lightweight classification check can stop it.

Input typeTypical riskSafer handling
Public brand assetsOutdated or incorrect usePull from the approved asset library
Employee or customer imagesPrivacy, consent, likeness misuseObtain documented permission and define the intended use
Voice recordingsImpersonation and biometric concernsUse only with explicit authorization; restrict reuse
Unreleased product materialConfidentiality and competitive exposureKeep out of external tools unless specifically approved
Licensed music, images, or footageContract and copyright restrictionsConfirm the license permits the planned AI-assisted use
Screenshots and screen recordingsHidden personal data or credentialsRedact, crop, and inspect frame by frame

Treat prompts as data too. People regularly paste campaign plans, customer segments, unreleased names, and internal strategy into prompt boxes. A good prompt can describe the desired shot without disclosing the confidential reason the company wants it.

When testing the Seedance 2.5 generation workflow available through ClipDance, begin with synthetic or already-public references. That lets the team assess control and output quality without making the first experiment the riskiest one.

Verify the service, not just the model

The model may get the attention, but the surrounding service handles accounts, payments, uploads, job history, and downloads. Security review should therefore cover the actual vendor and product being used.

At minimum, ask:

  • What data is stored, where, and for how long?
  • Are inputs or outputs used to improve models, and can that use be disabled?
  • How are files deleted, including backups?
  • What account protections and administrative controls are available?
  • Which subprocessors receive data?
  • How are security incidents communicated?
  • Can the provider support applicable privacy and contractual obligations?

The answers may vary by plan and over time. Save the terms, privacy notice, and security responses that supported the decision.

Secure the account and the production handoff

AI tools often become shared production infrastructure while still being accessed like a disposable app. One password gets passed around, exports land in personal download folders, and nobody knows who created the final clip.

Use individual accounts where possible. Enable multifactor authentication if the service supports it. Store credentials in the company password manager, remove access when roles change, and avoid sharing browser sessions. If a platform lacks the access controls needed for sensitive work, limit it to low-risk projects instead of pretending the gap does not matter.

The handoff deserves the same care. Move approved exports into a controlled project folder. Keep the source brief, references, prompt or direction notes, generation date, editor, and final approval together. Do not let the only production record live in one person’s account history.

Separate creation from approval

Separate creation from approval

The person who generated a convincing clip is poorly positioned to be its only reviewer. Familiarity hides errors. Use a second-person check for public work and a specialist review for higher-risk categories.

A practical approval pass covers five areas:

Identity. Does the clip contain a real or look-alike person? Was the likeness or voice authorized? Could the performance embarrass, deceive, or endanger someone?

Confidentiality. Did a reference or generated frame expose a customer name, prototype, screen, badge, document, location, or other protected detail?

Accuracy. Does the video imply that a product can do something it cannot? Are labels, physical actions, demonstrations, and spoken claims correct?

Rights. Are the source assets cleared for this use? Does the output imitate a protected character, distinctive work, or recognizable public figure?

Context. Could a viewer reasonably mistake the clip for authentic evidence? Will the disclosure remain visible when the asset is cropped, reposted, or separated from its caption?

For regulated or safety-critical messages, creative approval is not enough. The relevant legal, compliance, medical, financial, or technical owner must review the actual final export, not merely the script.

Preserve provenance, but understand its limit

The C2PA standard provides a way to attach tamper-evident information about a digital asset’s origin and edit history. Its Content Credentials explainer also makes an important distinction: provenance can help establish where media came from and what happened to it, but it does not decide whether a depicted claim is true.

That distinction matters. A correctly signed AI-generated video can still be misleading. Conversely, a legitimate file may lose metadata as it moves through editing software or social platforms.

Use provenance where your toolchain supports it, but pair it with human-readable disclosure. Labels such as “AI-generated illustration” or “synthetic reenactment” should be specific enough to give the audience useful context. Do not bury the disclosure in a general website policy.

Maintain an internal record even when public metadata may be stripped. At minimum, record:

  • The project owner and business purpose
  • The service and model route used
  • The source assets and evidence of permission
  • The material prompt or direction history
  • The generated and edited versions
  • The reviewers, approval date, and disclosure text
  • The final destinations where the video was published

This record helps with corrections, rights disputes, vendor reviews, and incident response.

Plan for misuse after publication

Once a synthetic clip is public, the creator no longer controls its context. Someone can remove the caption, replace the audio, or pair the footage with a fraudulent offer. Brands with public-facing executives are especially exposed because polished video can lend credibility to impersonation.

Before publication, decide who will handle a report that the video is being misused. Preserve the original project evidence, collect URLs and screenshots, notify the platform, alert affected people, and coordinate legal or communications response where necessary. If customers may be targeted, publish a clear correction or warning through channels they already trust.

The response plan needs a named owner and a way to act before internal uncertainty consumes the first critical hours.

A compact pre-publication checklist

Before an AI-generated video leaves the team, confirm:

  • The use falls within the approved policy.
  • No restricted data was entered in prompts or references.
  • Every identifiable person has appropriate permission.
  • Source licenses cover the intended use.
  • Product and factual claims were checked by their owners.
  • A second person reviewed every frame and the complete audio track.
  • The disclosure matches the realistic risk of confusion.
  • Production records and approvals are stored centrally.
  • The public file contains supported provenance information where practical.
  • An owner knows how to respond to impersonation, takedown requests, or corrections.

Security should make experimentation repeatable

The choice is not between unrestricted experimentation and a total ban. Both are signs that an organization has not designed the workflow.

A small, well-defined pilot is more useful: approved users, public or synthetic inputs, a limited use case, documented reviews, and a clear measure of success. The team learns where Seedance 2.5 helps, security learns where data actually moves, and management gains evidence for a larger decision.

The best control is rarely a warning added after the video exists. It is a production habit: choose low-risk material, verify the service, limit access, keep records, review independently, disclose clearly, and prepare for misuse. That turns AI video from an unsupervised shortcut into a process the company can defend.

Frequently asked questions

Is it safe to upload a person’s photo to an AI video generator?

Only when the organization has permission for that specific use and has verified the service’s data practices. A publicly visible photo is not automatic consent to create a synthetic performance.

Do Content Credentials prove that a video is true?

No. They can provide tamper-evident provenance information about the asset and its history. Editors and viewers still need to evaluate the truth and context of the content.

Should a company ban AI video for confidential projects?

If an approved service and adequate contractual, technical, and procedural controls are not available, keeping confidential material out of external generators is a reasonable boundary. The team can still use public or synthetic inputs for lower-risk work.

Who should own the AI video policy?

The policy should have a clear business owner and shared input from security, privacy, legal, brand, and the teams doing the work. Security alone cannot decide whether a depiction is on-brand or factually correct, while a creative team alone should not determine acceptable data exposure.


INTERESTING POSTS
The Best Types of Games for Flights, Road Trips, and Long Commutes

0
The Best Types of Games for Flights, Road Trips, and Long Commutes

In this post, I will talk about the best types of games for flights, road trips, and long commutes.

The overhead light won’t turn off, the guy in 14C has his elbow in your armrest, and there are still hours left on the flight. Swap the plane for a car, and it’s not much different, with taillights bumper to bumper down EDSA at rush hour and the bus’s radio cycling through the same five songs. Even a daily commute wears you down the same way when you’re standing in a packed train or when the jeepney you’re on moves inch by inch through traffic.

Boredom on the move has a way of feeling heavier than boredom at home because there’s nowhere to pace, nothing new to look at, and no easy exit. A good game flips that equation, and the trip stops feeling like something to get through. Load a few of these games before you head out.

Quick, Bite-Sized Puzzle Games

Puzzle games earn their spot on this list by asking for very little: no story to keep track of, no steady internet connection, just a few minutes of focus. Word puzzles, sudoku, and match-three apps all fit that mold, and most save your progress automatically, so a tunnel or a dropped signal won’t undo anything. Even a two-minute wait at boarding is enough time for a full round.

The mental payoff is a nice bonus. Casual puzzle play has been linked to sharper memory and stronger problem-solving, so it’s one of the few travel time-killers that leaves you a little sharper than when you started.

Games for a Quick Adrenaline Fix

Some trips call for something with more edge than a word puzzle. Racing games, quick-draw shooter apps, and fast-paced arcade games all deliver a short burst of adrenaline that fits neatly into a layover or a stalled commute. For those who want that same rush without needing quick reflexes, you can play slots online or other popular online casino games, offering a few minutes of anticipation over a slot spin or a hand of cards from a phone screen. The appeal isn’t the reflexes; it’s the suspense of not knowing what the next round brings.

That said, these games are best kept as occasional, time-limited diversions rather than the main event of a trip, particularly where real money is involved.

Story-Driven Adventure and RPG Games

Longer hauls call for something with more staying power, and a transpacific flight or a multi-hour provincial bus ride is exactly where story-driven games earn their keep. Mobile RPGs and narrative adventure games give you a plot to follow and characters worth remembering, which reward sustained attention instead of the quick taps a puzzle game asks for. Most support offline play once the initial files are downloaded, so it’s worth doing that before leaving home Wi-Fi behind. A single chapter can easily stretch across an entire layover without feeling rushed.

Treat this kind of game like a good book: pick it before the trip, commit to it for the duration, and let the story carry the layovers along with it.

Multiplayer Games for Group Trips

You’re four hours into a road trip, the playlist’s been through twice, and conversation’s starting to run dry. This is where a shared game earns its place. The same goes for a delayed flight with a friend in the next seat, or a commute where two coworkers end up on the same train. Multiplayer trivia, word-guessing apps, and simple card games pull everyone into the same round instead of scattering attention across separate phones. Many work over local Bluetooth or minimal data, so a weak signal on a provincial highway or spotty airport Wi-Fi doesn’t end the game early.

Audio-Based Games and Trivia Podcasts

Eyes closed, seat reclined as far as it goes, turbulence rattling the tray table: this is the moment for a game that doesn’t need a screen. Audio trivia apps and interactive podcasts ask just enough of your attention to keep you engaged without adding to the screen fatigue that’s already built up over a day of travel. They work just as well on a night bus with the windows blacked out, or a commute where pulling out a phone isn’t an option.

Sometimes the best game for a trip is the one that lets you rest your eyes and still feel like you did something with the time.

A trip is really just a stretch of time with nowhere else to be, and that’s not always a bad thing. The right game doesn’t erase a delay or shorten a jeepney ride stuck at a red light; it just changes what that time feels like while the wait is happening. Load a few options before you leave the house, and the next flight, drive, or commute might be the first one you don’t spend checking how much longer it’ll take.


INTERESTING POSTS

How to Detect Fake Social Media Profiles

0
How to Detect Fake Social Media Profiles

In this post, we will show you how to detect fake social media profiles.

With the increasing prevalence of social media platforms in our daily lives, fake social media profiles have become a significant concern.

These profiles are often created for various malicious purposes, such as identity theft, online scams, cyberbullying, and misinformation spreading.

Detecting fake social media profiles is crucial to ensure your online safety and maintain the integrity of your online interactions.

In this comprehensive guide, we will explore various methods and techniques to help you identify and report fake social media profiles.

What Is A Fake Social Media Profile?

What Is A Fake Social Media Profile

A fake social media profile is an account that is created with the intent to deceive or mislead others. These accounts can be used for a variety of purposes, such as spreading misinformation, spamming, or catfishing.

To be more specific, a fake social media profile is an account that is not associated with a real person or is created with an actual person’s personal information without their consent. These accounts are often called imposter accounts or sock puppet accounts.

A fake social media profile is an account that is created with the intent to deceive or mislead others. These accounts can be used for a variety of purposes, such as:

  • Catfishing: Catfishing is a form of online deception in which someone creates a fake profile in order to lure someone else into a relationship. This can be done for financial gain, for emotional manipulation, or for simply having fun.
  • Spreading misinformation: Fake profiles can be used to spread false information about people, events, or organizations. This can be done to damage someone’s reputation, to promote a particular agenda, or to sow discord.
  • Spamming: Fake profiles can be used to send spam messages to people. This can be done to promote products or services, to spread malware, or to collect personal information.
  • Harassing or bullying: Fake profiles can be used to harass or bully people. This can be done by sending threatening messages, spreading rumors, or posting embarrassing photos or videos.
  • Identity theft: Fake profiles can be used to steal someone’s identity. This can be done by gathering personal information, such as their name, address, and date of birth, and then using that information to open accounts, apply for loans, or commit other crimes.

READ ALSO: Multilogin Antidetect Browser Review 2024

Social Catfish: Best Online Tool To Detect Fake Social Media Profiles

Social Catfish: Best Online Tool To Detect Fake Social Media Profiles

Social Catfish is a website that provides online investigation services to help people verify someone’s identity, find people online, and avoid online scams and fraud.

The website offers a variety of tools that can be used to investigate social media profiles, including:

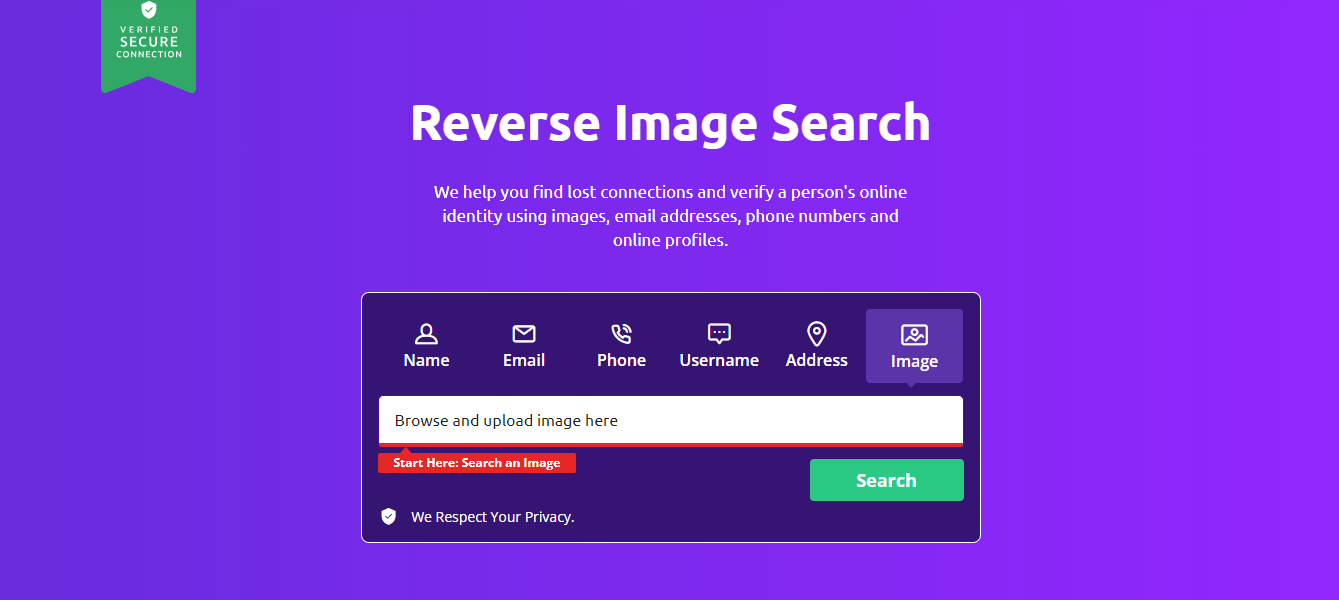
  • Reverse image search: This tool can be used to find out where a profile picture has been used online. This can be helpful in identifying stolen photos.
  • Public records search: This tool can be used to search for public records about someone, such as their name, address, and phone number. This can be helpful in verifying someone’s identity.
  • Social media search: This tool can be used to search for someone’s social media profiles across different platforms. This can be helpful in finding out more about someone’s online activity.
  • Email lookup: This tool can be used to find out the email address associated with a social media profile. This can be helpful in contacting someone or reporting a fake profile.

Social Catfish also offers a premium service that provides additional features, such as:

  • Background check: This feature provides a more comprehensive background check on someone, including their criminal history and financial records.
  • Phone lookup: This feature provides the phone number associated with a social media profile.
  • Address lookup: This feature provides the address associated with a social media profile.

Overall, sites like US People Search and Social Catfish are comprehensive tools that can be used to help you investigate social media profiles. It is a good option for people who want to be more careful about who they interact with online.

Social Catfish
Social Catfish
Social Catfish is an online service that helps individuals verify and investigate the identity of people they meet...Show More
Social Catfish is an online service that helps individuals verify and investigate the identity of people they meet online, including potential scammers and catfishers. Show Less

==>> Get Social Catfish

Signs Of Fake Social Media Profiles

detect fake social media profile

No matter how well-crafted they are, fake social media profiles often have telltale signs that cyber-savvy users can spot.

READ ALSO: 8 Popular Types of Cybercrimes in the 21st Century

Here are some tips to help you identify fake social media profiles:

  • Lack of profile information: Fake profiles often have very little information in their profiles. This could include things like a blank bio, no profile picture, or only a few friends.
  • Generic usernames: Fake profiles often have generic usernames that are not unique or memorable. For example, an account named “johndoe123” is more likely to be fake than an account named “johnsmith_photography.”
  • Unnatural activity: Fake profiles may exhibit unnatural activity, such as posting a large number of friend requests or messages in a short period of time. They may also share links to suspicious websites or ask for personal information.
  • Stolen photos: Fake profiles may use stolen photos or images that they find online. This is a common way for scammers to create realistic-looking profiles.
  • Verification status: Some social media platforms, such as Twitter and Instagram, offer a verification process for public figures and celebrities. If an account claims to be a celebrity or public figure but does not have a verification badge, it is more likely to be fake.
  • Location: Fake profiles may have a location that is different from the person’s actual location. This can be a red flag, but it is not always true. For example, someone who travels frequently may have a different location listed on their profile.
  • Language: Fake profiles may use language that is not consistent with the person’s claimed location or background. For example, an account that claims to be from the United States but uses British English is a red flag.

READ ALSO: Best Antivirus For 2023

  • Grammar and spelling: Fake profiles may have poor grammar and spelling. This is not always the case; some people are not good at grammar and spelling. However, it is something to keep an eye out for.
  • Age: Fake profiles may claim to be a different age than they actually are. This is a common way for scammers to target younger people.
  • Relationship status: Fake profiles may claim to be in a relationship or married, even if they are not. This is a common way for scammers to build trust with their victims.
  • Activity: Fake profiles may be inactive or have a sudden change in activity. This could be a sign that the person behind the profile has lost interest or that they are trying to avoid detection.
  • Friend requests: Fake profiles may send a lot of friend requests, even to people they don’t know. This is a common way for scammers to build up their follower count.
  • Messages: Fake profiles may send messages that are unsolicited or that are not relevant to the conversation. They may also ask for personal information or try to sell you something.

It is important to note that not all of these signs will be present in every fake social media profile. However, if you see a number of these signs, it is a good idea to be cautious and to do some further investigation by using a tool like Social Catfish.

READ ALSO: Best VPN For 2023

How to Detect Fake Social Media Profiles

  1. Profile Picture Analysis

One of the first things to check when assessing a social media profile’s authenticity is the profile picture. Fake profiles often use stolen or stock photos. Here’s how you can analyze the profile picture:

Reverse Image Search

a. Reverse Image Search: Use reverse image search tools like Social Catfish, Google Images, or TinEye to check if the profile picture appears anywhere else on the internet. If it’s a commonly used image or associated with multiple profiles, it might be fake.

b. Check for Inconsistencies: Look for inconsistencies in the image, such as pixelation, unnatural lighting, or signs of photo manipulation. Genuine photos usually have a more natural appearance.

  1. Examining the Username and Handle

Usernames and handles can also provide clues about a profile’s authenticity:

Usernames and handles

a. Unusual Characters: Fake profiles may use unusual characters or combinations of letters and numbers in their usernames. Legitimate users often opt for more straightforward handles.

b. Generic Names: Be cautious of profiles with overly generic names like “John Smith” or “Jane Doe.” Real users often have unique names.

READ ALSO: The Ultimate Social Media Security Guide for Individuals and Businesses

  1. Utilize Fake Social Media Detector Tools

In your quest to identify fake social media profiles, you can leverage dedicated tools and services designed for this purpose. One such tool is Social Catfish, which offers advanced features to help you uncover fake or fraudulent profiles:

a. Reverse Image Search: Social Catfish and similar platforms allow you to perform reverse image searches more efficiently. They search across various social media platforms, dating websites, and other online sources, making it easier to spot stolen or duplicated images associated with fake profiles.

b. Username and Email Search: These tools often enable you to search for usernames and email addresses associated with a specific profile. If the same username or email address appears on multiple profiles, it could be a sign of fake or malicious activity.

c. Social Media Cross-Referencing: Social Catfish and similar services can cross-reference information across different social media platforms, helping you detect inconsistencies or patterns that may indicate a fake profile.

d. Detailed Reports: These tools provide comprehensive reports that summarize their findings, making it easier for you to assess whether a profile is genuine or fake.

Social Catfish
Social Catfish
Social Catfish is an online service that helps individuals verify and investigate the identity of people they meet...Show More
Social Catfish is an online service that helps individuals verify and investigate the identity of people they meet online, including potential scammers and catfishers. Show Less

==>> Get Social Catfish

  1. Assessing Profile Activity

Fake profiles tend to have limited or unusual activity patterns:

Profile Activity

a. Lack of Posts or Updates: A clear sign of a fake profile is the absence of regular posts, updates, or interactions with other users.

b. Low Friend/Follower Count: Fake profiles often have a low number of friends or followers, especially if they are impersonating a public figure.

c. Duplicate Content: Scammers often reuse content or post spammy links repeatedly. Look for patterns of duplicative posts.

  1. Reviewing Friends and Followers

The composition of a user’s friend or follower list can be revealing:

a. Check for Mutual Connections: If you have mutual friends or followers with the profile in question, ask them about the user’s authenticity.

b. Assess Profile Pictures of Friends: Fake profiles might have friends with similarly fake or stolen profile pictures. Investigate their profiles as well.

READ ALSO: Exclusive Tips To Stop Cyberbullying [For Teens, Parents & Schools]

  1. Verify Contact Information

Contact Information

Legitimate users often provide contact information on their profiles, such as email addresses or phone numbers:

a. Cross-Check Contact Information: Verify the provided contact information. If it leads to a non-existent domain or appears suspicious, the profile may be fake.

  1. Analyze the About/Info Section

The “About” or “Info” section of a profile can reveal important details:

a. Incomplete Information: Fake profiles often provide minimal or vague information. Check for missing or inconsistent details.

b. Spelling and Grammar: Pay attention to the quality of written content. Many fake profiles contain spelling and grammar errors.

  1. Look for Consistency Across Platforms

Cross-reference the information and activity on the suspicious profile with their presence on other social media platforms. Consistency in information, profile pictures, and activity can help establish authenticity.

  1. Trust Your Intuition

Sometimes, your gut feeling can be a valuable tool. If something about a profile feels off or raises suspicions, trust your instincts and proceed with caution.

  1. Report Suspected Fake Profiles

Report Suspected Fake Profiles

Most social media platforms provide mechanisms to report suspicious or fake profiles. Use these reporting features to notify the platform administrators, who can investigate and take appropriate action.

READ ALSO: 5 Ways To Identify Phishing Or Fake Websites

What To Do If You Detect A Fake Social Media Account?

What To Do If You Detect A Fake Social Media Account

Discovering a fake social media account can be concerning, but taking the right steps can help protect yourself and others from potential harm. Here’s a comprehensive guide on what to do if you detect a fake social media account:

  1. Do Not Interact: First and foremost, refrain from engaging with the fake account. Do not accept friend or follower requests, reply to messages, like, comment, or share their posts. Interaction could potentially give the fake account access to your personal information or validate their presence.
  2. Do Not Click on Any Links: Avoid clicking on any links the fake profile sends you. These links may lead to malicious websites that can steal your personal information or infect your computer with malware.
  3. Document the Evidence: Take screenshots of the fake profile, including the profile picture, username, any messages or interactions, and any other information that may be relevant. This documentation can be useful if you need to report the account.
  4. Report the Account to the Platform: Most social media platforms have mechanisms for reporting fake or suspicious accounts. Follow these steps:a. On Facebook: Click on the three dots (…) on the fake profile’s cover photo, select “Find Support or Report Profile,” and follow the prompts to report it as a fake account.b. On Twitter (X): Click on the three dots (…) on the fake profile’s header, select “Report,” and follow the instructions to report the account for suspicious activity.c. On Instagram: Go to the fake profile, tap the three dots (…) in the upper right corner, and select “Report” to report the account as spam or fake.d. On LinkedIn: Visit the fake profile, click “More,” and select “Report/Block” to report it as a fake profile.
  5. Block the Profile: Blocking the fake profile is an additional step you can take to protect yourself. This will prevent the profile from contacting you and viewing your posts.
  6. Adjust Your Privacy Settings: Review and update your own privacy settings on the social media platform to limit the information that strangers can access. This can help protect your personal information from being exploited by fake accounts.
  7. Warn Others: If you have mutual friends or followers with the fake account, consider reaching out to them privately to inform them about the situation. They may also be at risk, and your warning could help them take necessary precautions.
  8. Maintain Vigilance: Keep an eye on your online accounts and be cautious when accepting friend or follower requests from unfamiliar individuals. Continue to report any suspicious activity you come across.
  9. Protect Your Personal Information: Review the information you share on your own social media profiles. Be cautious about the level of personal information you make public, as fake accounts often gather information from your posts and interactions.
  10. Consider Legal Action: In extreme cases where you have suffered harm due to a fake account, you may want to consult with legal authorities or an attorney to explore potential legal action.
  11. Educate Yourself and Others: Stay informed about the latest scams and tactics used by fake social media accounts. Share this knowledge with friends and family to help protect them from falling victim to similar schemes.

Remember that social media platforms take the issue of fake accounts seriously and usually investigate reports promptly. Your actions not only protect yourself but also contribute to making the online community safer for everyone.

READ ALSO: What Is A Fake Antivirus? Overview And How To Spot Them

How To Protect Yourself From Fake Social Media Profiles

How To Protect Yourself From Fake Social Media Profiles

Here are some tips on how to protect yourself from fake social media profiles:

  • Be wary of friend requests from people you don’t know. If you receive a friend request from someone you don’t know, take a moment to check their profile before accepting. Look for things like a verified account badge, a lot of activity, and a history of posts that make sense. If something seems off, don’t accept the request.
  • Don’t share personal information with people you don’t know. This includes your full name, address, phone number, or financial information. If someone asks for this information, be suspicious.
  • Be careful about clicking on links in messages. Fake profiles often send messages with links that lead to malicious websites. If you’re unsure about a link, don’t click on it.
  • Keep your security settings up to date. Make sure your social media accounts have strong passwords and that you’ve enabled two-factor authentication. This will make it more difficult for someone to hack into your account.
  • Be aware of the latest scams. Scammers are always coming up with new ways to trick people. If you see something that seems suspicious, do some research to make sure it’s not a scam.

Conclusion

Fake social media profiles are a growing problem, but there are steps you can take to protect yourself. By being aware of the signs of a fake profile, you can avoid getting scammed or harassed.

By being aware of the risks and taking steps to protect yourself, you can help keep your social media experience safe and enjoyable.

Nonetheless, I recommend that you check out the Social Catfish tool to investigate suspicious or fake social media profiles.

Social Catfish
Social Catfish
Social Catfish is an online service that helps individuals verify and investigate the identity of people they meet...Show More
Social Catfish is an online service that helps individuals verify and investigate the identity of people they meet online, including potential scammers and catfishers. Show Less

==>> Get Social Catfish


RELATED POSTS

Cybersecurity Tips From Squid Game TV Series [MUST READ]

0
Cybersecurity Tips From Squid Game TV Series

This post will show you essential Squid Game cybersecurity tips to learn.

Netflix’s Squid Game took the world by storm, captivating audiences with its brutal depiction of 456 debt-ridden individuals competing in deadly children’s games for a massive cash prize.

Beyond its gripping storyline, the series offers profound cybersecurity lessons that mirror today’s digital threats. Just as contestants face life-or-death challenges, your sensitive data battles against relentless cybercriminals daily.

CHECK OUT: Web Security Guide: Keeping Your Website Safe

What Is The Squid Game All About?

What Is The Squid Game All About
Image source: Rotten Tomatoes

The Squid Game’s rules mirror classic childhood games turned deadly. The perimeter drawn in sand represents a squid’s outline, with defenders patrolling the boundaries and attackers attempting to breach them while hopping on one leg. Once past the defenders, attackers can use both legs to reach the “squid head” and win—but one wrong move means elimination (or death, in the show’s context).

This high-stakes game serves as a perfect metaphor for cybersecurity:

  • Defenders = Your security systems and IT team
  • Attackers = Cybercriminals probing for weaknesses
  • Squid Perimeter = Your network’s digital boundaries

Cybersecurity Lessons From Squid Game

LessonDescriptionReal-World Application
Don’t Trust Easily (Red Light, Green Light)The unsuspecting players are eliminated for trusting the deceptive doll’s instructions.Be cautious of online interactions and information. Verify sources, avoid clicking suspicious links, and be wary of overly generous offers.
Information Asymmetry (Honeycomb Game)Players with prior knowledge of the game (shapes) have a significant advantage.Attackers often exploit vulnerabilities in software or human error. Stay updated on cybersecurity threats and best practices.
Strength in Numbers (Tug-of-War)The stronger team (more members) wins, highlighting the importance of teamwork.Utilize multi-factor authentication and implement security measures across your entire network (personal or business).
Physical vs. Digital Security (Glass Bridge Game)The “tempered” glass bridge represents strong security, while the “normal” glass is a security weakness.Implement strong passwords data encryption, and regularly update software to patch vulnerabilities.
Desperation Breeds Risk (Marbles Game)Players take extreme risks due to desperation in the game.Financial desperation can make people more susceptible to phishing scams or malware. Be cautious of online financial opportunities, especially those promising quick and easy returns.
Beware of Internal Threats (The Hostage Situation)The game’s mastermind is revealed as one of the participants.Insider threats can be just as dangerous as external threats. Implement access controls and be mindful of who has access to sensitive information.

Case Study: The Red Light, Green Light Phishing Lesson

In 2022, Google reported blocking 100 million phishing emails daily. Just like players who moved during “Red Light” were eliminated, employees who click malicious links often compromise entire networks. A 2023 IBM study found that 95% of cybersecurity breaches result from human error—proving why verification is crucial.

What Does The Squid Game TV Series Have In Common With Cybersecurity?

What Does The Squid Game TV Series Have In Common With Cybersecurity

Modern organizations face attacks from multiple vectors—cloud, mobile, IoT devices—just as Squid Game contestants faced unexpected challenges. Here’s the cybersecurity parallel:

  1. The Squid Perimeter = Your network’s firewall and endpoint security
  2. Defenders = Your SOC (Security Operations Center) team and tools like SIEM systems
  3. Attackers = Advanced Persistent Threats (APTs) or ransomware gangs

READ ALSO: 5 Cybersecurity Tips To Protect Your Digital Assets As A Business

Cybersecurity Tips From Squid Game Series To Help You Up Your Game: SEASON 1

1. Build Your Defenses Like The Squid Perimeter

Build your defenses

Actionable Steps:

  • Conduct a data audit to identify critical assets (customer data, IP, financial records)
  • Deploy next-gen firewalls with intrusion prevention (Palo Alto, Fortinet)
  • Use endpoint detection and response (EDR) tools like CrowdStrike
  • Budget at least 10-15% of IT spending on security (Gartner recommendation)

CHECK OUT: Best Antivirus For 2022

2. Network Segmentation: Isolate Like The Game’s Zones

Separate your networks and keep your most sensitive information assets locked away

Why It Matters: The 2023 Verizon DBIR found that 83% of breaches involved external actors jumping between systems.

Implementation Guide:

  1. Create VLANs for different departments (HR, Finance, R&D)
  2. Use zero-trust architecture (never trust, always verify)
  3. Implement micro-segmentation for cloud workloads
  4. Deploy privileged access management (PAM) solutions

CHECK OUT: Best VPN For 2022

3. Defense-in-Depth: The Glass Bridge Strategy

Build a defense-in-depth around your sensitive data

Like the tempered vs. normal glass in the show, layered security ensures attackers face multiple barriers:

LayerSecurity MeasureExample Tools
PerimeterFirewalls, Email FiltersCisco Firepower, Proofpoint
NetworkIDS/IPS, Network SegmentationDarktrace, Splunk
EndpointAntivirus, EDRSentinelOne, Microsoft Defender
DataEncryption, DLPVeraCrypt, Symantec DLP

CHECK OUT: GlassWire Network Firewall

4. Prepare For Unknown Threats (The VIPs’ Game)

Squid Game Cybersecurity Tips

The show’s unpredictable VIPs mirror advanced persistent threats (APTs). 34% of breaches in 2023 involved novel attack vectors (Source: Mandiant M-Trends).

Incident Response Plan Checklist:

  • Conduct quarterly tabletop exercises
  • Maintain an updated contact list for crisis response
  • Store offline backups (3-2-1 rule: 3 copies, 2 media types, 1 offsite)
  • Subscribe to threat intelligence feeds (Recorded Future, etc.)

Season 2 Cybersecurity Lessons: The Return of Deception 🎭

Season 2 Cybersecurity Lessons: The Return of Deception 🎭

1. Advanced Social Engineering (The Recruitments)

In Season 2, returning or new participants are subtly manipulated into joining the deadly games, often through promises or emotional appeals. Just like in real life, attackers exploit trust to gain entry into systems.

Real-World Application:

  • Train employees regularly to spot phishing emails, fake calls, and pretexting attempts.
  • Simulate attacks through controlled phishing campaigns (tools like KnowBe4 or PhishMe).
  • Verify unusual requests for sensitive information, even if they appear to come from leadership.
  • Example: An employee receives a convincing “urgent invoice” email from finance. Without verification, clicking it could unleash malware — just as a contestant trusting the recruiter faces elimination.

2. Multi-Layered Monitoring (The Underground Games)

The hidden games in Season 2 feature multiple surveillance points, catching every subtle move, ensuring that mistakes don’t go unnoticed. In cybersecurity, single-layer defenses aren’t enough; threats can bypass one system and exploit another.

Real-World Application:

  • Continuous network monitoring using SIEM tools like Splunk or LogRhythm.
  • Behavioral analytics to detect unusual user activity or privilege misuse.
  • Redundant checks for critical systems: firewall + EDR + endpoint monitoring.
  • Example: Just like a contestant is watched by cameras in blind spots, attackers may lurk in systems unnoticed without comprehensive monitoring. Multiple layers make detection faster and containment more effective.

READ ALSO: Cyber Security Management vs Traditional IT Security Approaches

Season 3 Cybersecurity Lessons: Insider Threats Amplified 🕵️‍♂️

Season 3 Cybersecurity Lessons: Insider Threats Amplified 🕵️‍♂️

1. Exploiting Familiarity (The Insider Advantage)

Returning players leverage their prior knowledge to exploit vulnerabilities in new contestants. Similarly, insiders in organizations — whether employees, contractors, or partners — have knowledge that external attackers do not.

Real-World Application:

  • Role-Based Access Control (RBAC): Only allow access necessary for a user’s role.
  • Audit trails & logging: Track every action to identify suspicious behavior.
  • Periodic access reviews: Revoke privileges that are no longer needed.
  • Example: A former employee retains access to shared folders and exfiltrates data. Proactive monitoring and strict access controls prevent such exploitation.

2. Contingency Planning (The Extreme Twists)

Season 3 throws unexpected twists at players — sudden rule changes, hidden traps, and ambushes. Cybersecurity faces similar uncertainty with zero-day exploits, ransomware, and advanced persistent threats (APTs).

Real-World Application:

  • Incident response plan: Keep it updated, test it quarterly, and include clear communication protocols.
  • Redundant backups: Apply the 3-2-1 rule (3 copies, 2 media types, 1 offsite).
  • Rapid patch management: Ensure critical updates are applied within hours of release.
  • Example: A ransomware attack encrypts critical servers. Organizations with tested contingency plans restore systems quickly, just as contestants adapt to survive sudden game changes.

✅ Key Takeaways From Seasons 2 & 3:

  • Trust is currency: Never assume trust — verify everything (Zero Trust).
  • Knowledge is power: Insider awareness and monitoring prevent exploitation.
  • Layer your defenses: One line of defense is never enough.
  • Plan for surprises: Cyberattacks evolve; preparation reduces damage.


Squid Game Cybersecurity Lessons Table: Seasons 1–3

LessonSeason & GameDescriptionReal-World Application / Actionable Tip
Don’t Trust EasilyS1 – Red Light, Green LightPlayers eliminated for trusting deceptive instructions.Verify online sources, avoid suspicious links, double-check offers. Implement zero-trust architecture.
Information AsymmetryS1 – HoneycombPlayers with prior knowledge have advantage.Keep software patched, educate staff, stay updated on threats, reduce knowledge gaps internally.
Strength in NumbersS1 – Tug-of-WarTeamwork increases survival chances.Apply multi-factor authentication across all systems; ensure network-wide security policies.
Physical vs. Digital SecurityS1 – Glass BridgeStrong glass = strong security; weak glass = vulnerability.Use strong passwords, encrypt data, patch software regularly. Conduct penetration tests.
Desperation Breeds RiskS1 – MarblesDesperation leads to risky decisions.Avoid hasty financial or security decisions. Train staff to recognize scams, phishing, and malware.
Beware of Internal ThreatsS1 – Hostage SituationGame mastermind is one of the participants.Implement RBAC, audit logs, insider threat monitoring, and access reviews.
Advanced Social EngineeringS2 – RecruitmentsReturning or new participants manipulated psychologically.Conduct phishing simulations, train staff on social engineering, verify all unusual requests.
Multi-Layered MonitoringS2 – Underground GamesMultiple surveillance systems catch mistakes.Deploy SIEM, EDR, and behavioral analytics for continuous monitoring. Redundant checks prevent undetected breaches.
Exploiting FamiliarityS3 – Insider AdvantageReturning players exploit knowledge to gain edge.Limit insider risk through RBAC, privilege reviews, logging, and monitoring suspicious behavior.
Contingency PlanningS3 – Extreme TwistsUnexpected twists force rapid adaptation.Maintain and test incident response plans, use 3-2-1 backups, and implement rapid patching for zero-day threats.

✅ How to Read This Table

  • Season & Game: Identifies the Squid Game season and specific in-show game that illustrates the lesson.
  • Lesson: The cybersecurity principle inspired by the show.
  • Description: Explains the in-show analogy for easier understanding.
  • Real-World Application: Concrete, actionable cybersecurity steps you can implement immediately.

Cybersecurity Lessons From Squid Game: FAQs

The show highlights distrust as a key cybersecurity principle. Isn’t that a bit extreme?

While absolute distrust isn’t practical, zero-trust architecture is now industry standard. Google’s BeyondCorp model proves that verifying every access request reduces breaches by 50%+.

How can small businesses implement Squid Game-level security affordably?

Start with these low-cost measures:

  • Enable free MFA (Microsoft Authenticator, Google Authenticator)
  • Use built-in security tools (Windows Defender, macOS Gatekeeper)
  • Train staff with phishing simulation tools (KnowBe4 has free tiers)

How does the “information asymmetry” in the Honeycomb Game apply to real-world cybersecurity?

Just like players with shape knowledge had an advantage, cybercriminals exploit unpatched vulnerabilities. The CISA KEV Catalog shows 60% of breaches use vulnerabilities where patches existed but weren’t applied. Always update systems within 72 hours of patch releases.

The Marbles Game shows desperation leading to bad decisions. How does this translate to cyber risks?

Financial stress makes people 3x more likely to fall for “get rich quick” scams (FBI Internet Crime Report 2023). During economic downturns, fake investment scams increase by 200%. Always verify opportunities through official channels before acting.

What’s the cybersecurity equivalent of the Glass Bridge’s “testing each step”?

This mirrors penetration testing:

  • Conduct annual red team exercises
  • Use automated vulnerability scanners weekly
  • Test backup restoration quarterly (40% of backups fail when needed)

How can teams collaborate securely like the Tug-of-War game winners?

Implement team-based security:

  • Shared password managers (Bitwarden, 1Password)
  • Role-based access controls (RBAC)
  • Security champion programs in each department

Microsoft found this approach reduces incidents by 58%.

The show features disguised threats. What’s the cybersecurity parallel?

This represents fileless malware and living-off-the-land attacks:

  • 31% of attacks now use legitimate tools like PowerShell
  • Deploy behavioral analysis tools (CrowdStrike, SentinelOne)
  • Monitor for unusual system tool usage patterns

How does the “elimination” concept apply to cybersecurity?

This mirrors automated threat containment:

  • Set SIEM rules to isolate compromised devices
  • Automatically revoke credentials after 3 failed logins
  • Quarantine suspicious emails with sandboxing

Gartner shows this reduces breach impact by 72%.

Conclusion – Squid Game Cybersecurity Tips

Just as Squid Game contestants faced escalating challenges, cyber threats grow more sophisticated yearly. A 2023 CyberArk study found attacks increased by 38% YoY. By implementing these layered defenses—network segmentation, EDR, employee training—you create a security posture as resilient as the show’s tempered glass.

For further protection, explore our guide on protection tools against hackers and learn how to secure your systems against emerging threats.


INTERESTING POSTS
The Unbiased CCleaner Kamo Review

0

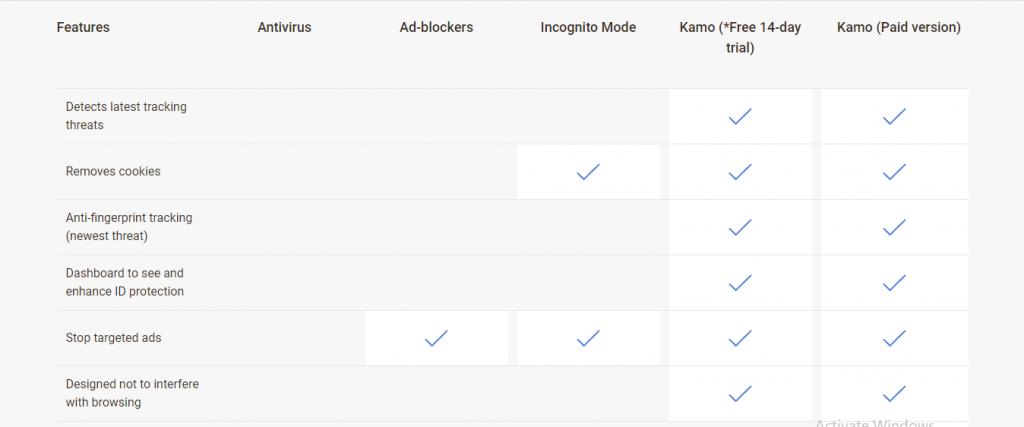
Here is the CCleaner Kamo Review; read on.

In the world of digital technology, it is imperative to protect your online privacy, secure your online activities, and optimize your device’s performance.

Kamo software from Piriform is a privacy protection tool designed to protect you from advanced tracking and data collection techniques; should you entrust Kamo with your privacy, and what is Kamo’s role in safeguarding your online activities?

Kamo isn’t the only way to fight browser fingerprinting: users who manage several online identities often go further with an antidetect browser, which gives every browser profile its own separate, consistent device fingerprint.

Read on to learn more about the Privacy app in this Kamo review.

What Is Kamo?

Kamo is a privacy app designed to protect your identity from advanced tracking techniques, such as fingerprinting and tracking, by combining a basic VPN with anti-fingerprinting technology into a single application.

In essence, Kamo employs VPN technology, often referred to as Kamo VPN, to encrypt your data traffic, mask your IP address, and obscure your exact geographic location. Along with its patented anti-fingerprinting technology to thwart digital fingerprinting, Kamo creates fake fingerprints by injecting fake data into your browser, which throws off trackers and third-party cookie collectors, offering robust tracking protection and tracker blocking.

📝Editor’s Note: We highly recommend that you remove your personal information from data broker sites and search engines. Get Incogni: Best Internet Scrubbing Service

How To Get Started With Kamo

  • Go to the official Kamo website to download and install it
  • Click ‘Yes’ in the User Account Control
  • Set your language option to English or choose a preferred language
  • Click ‘Next’ in the Kamo installation wizard
  • Confirm you have read the End User License Agreement by clicking on ‘I agree.’
  • Kamo automatically launches after installation is completed
  • Click ‘Next’ to review the tutorial on how to use Kamo
  • Type or paste the activation code when prompted.

CCleaner Kamo
Kamo
Kamo is a privacy app designed to protect your identity from advanced tracking techniques like fingerprinting and...Show More
Kamo is a privacy app designed to protect your identity from advanced tracking techniques like fingerprinting and tracking. Show Less

==>> Get Kamo

Features

Intuitive User Interface

Kamo features a user-friendly dashboard that lets you check your progress, monitor tracking activity, enhance ID protection with browser security features, and adjust settings to maintain your digital safety.

The interface is navigation-friendly, making it an easy-to-use tool for privacy protection.

IP address and location masking

Kamo uses VPN technology to encrypt and protect your data traffic and hide your IP address and location, providing a private connection that keeps you, an anonymous user, safe from hackers, government spies, and cookie trackers, while helping to hide sensitive data.

A privacy tool like a VPN protects your connection, but a mobile antidetect browser with Multilogin adds device-level defenses by emulating real mobile environments and isolating browser profiles to prevent fingerprint linking.

Anti-Fingerprint technology

Kamo’s anti-fingerprint technology protects you from fingerprint tracking by generating random and false fingerprints that block trackers from harvesting your digital fingerprint data.

This protects you from advertisers and cookie trackers that collect browser data and cookies to serve you with personalized ads, while also helping to remove cookies that could compromise your privacy.

Anti-data theft and browser protection

Anti-data theft and browser protection

Kamo safeguards your online privacy by performing a thorough browser cleanup, including the ability to clear browsing history and delete browser data. This ensures that third-party cookie trackers and advertisers can’t access your browsing activity, as Kamo leaves no trace.

Moreover, Kamo is designed to remove cookies, including zombie cookies and other persistent tracking elements, ensuring your browser remains clean and your personal information secure.

Uncovers trackers

Kamo enhances your digital security by pinpointing and blocking analytics from malicious websites. These sites often attempt to collect sensitive information, such as personal, medical, family history, and financial data; however, Kamo ensures that you only interact with trusted websites.

The tracking protection feature in Kamo provides a robust shield for your privacy, actively screening and blocking harmful data traffic from infiltrating your device.

Auto-data syncing and clearing

For me, Kamo significantly improves the browsing experience by eliminating the need for manual intervention. Without the hassle of installing plug-ins, you simply purchase and install Kamo, and it seamlessly syncs with your browsers.

Kamo automatically handles browser cleanup, wiping all history and cookies, relieving you of the burden of manually deleting browser data on each browser individually.

Ad blocker

While Kamo isn’t strictly an ad blocker, it effectively blocks social media tracking by clearing your browser history and cookies. Additionally, it injects fake fingerprints into your browser, disrupting the ability of trackers and advertisers to compile a complete profile for targeted ads.

Strict Privacy Policy

Kamo is committed to enhancing privacy with a strict data policy that ensures your personal data is neither logged nor sold to advertisers or third-party data collectors.

Kamo Compatibility

At the time of writing this Kamo review, which focuses on Windows privacy tools, I noted that Kamo supports only the Windows OS. It is, however, promising that future app versions may extend support to additional operating systems and devices, including Mac, Linux, Android, iOS, and others.

CCleaner Kamo review

Kamo Customer Support And Resources

Kamo does not offer helplines for support agents to contact or email support; however, there is a detailed, well-organized FAQ page that covers every issue you’re likely to encounter and answers common inquiries.

Piriform reviews often highlight the helpful video tutorials that guide users on how to use Piriform products. Additionally, there’s a fast-response online form for direct communication with Kamo’s customer care, a vibrant online community, and an intelligent live chatbot ready to handle your requests.

Below is a summary of Kamo’s support channels

  • LiveChat bot
  • Online form
  • Video tutorials
  • FAQs
  • A vibrant community of experts

Kamo System Requirements

Kamo supports only Windows OS 7 and above with X86-64 processors; however, it does not support ARM processors, Mac, iOS, and Android OS, which may be a consideration for those looking into subscription options.

Kamo Pros And Cons

Pros

  • Lifetime subscription
  • Blocks advanced trackers
  • Removes stubborn cookies
  • Protects you from fingerprinting
  • Intuitive user interface and dashboard
  • Robust ad blocker
  • Masks your IP and location

Cons

  • Compatible only with Windows OS
  • 14-day trial period
  • Auto-server selection.

Kamo Pricing

CCleaner Kamo review

A yearly subscription of $24.95 makes Kamo one of the most affordable privacy protection tools, thanks to its robust privacy features.

Kamo also offers a free trial valid for 14 days, after which you’ll need to purchase a yearly subscription to continue enjoying Kamo’s robust privacy protection services.

CCleaner Kamo
Kamo
Kamo is a privacy app designed to protect your identity from advanced tracking techniques like fingerprinting and...Show More
Kamo is a privacy app designed to protect your identity from advanced tracking techniques like fingerprinting and tracking. Show Less

==>> Get Kamo

Digital Privacy Product Deals

Incogni banner ad55% OFF
Incogni
Incogni wipes off your personal information from data brokers.
Incogni wipes off your personal information from data brokers. Show Less
BFDEAL25
Norton AntiTrack
Norton AntiTrack
Protects your personal information and browsing activities from online trackers.
Protects your personal information and browsing activities from online trackers. Show Less
MacKeeper
MacKeeper
The best Mac PC optimization tool for wiping out junk, blocking ads, protecting your personal information, and detecting...Show More
The best Mac PC optimization tool for wiping out junk, blocking ads, protecting your personal information, and detecting malware. Show Less
PC Matic Magnum
PC Matic Magnum
PC Matic Magnum is a PC optimization software that uses whitelisting technology to protect against malware and improve...Show More
PC Matic Magnum is a PC optimization software that uses whitelisting technology to protect against malware and improve the performance of a computer by removing unnecessary files and running regular system scans. Show Less
IronVest (Abine Blur)
IronVest (Abine Blur) is a privacy and security software that helps users protect their personal information online by...Show More
IronVest (Abine Blur) is a privacy and security software that helps users protect their personal information online by masking their email, phone number, and credit card information. Show Less
DeleteMe
DeleteMe
DeleteMe is a service provided by Abine that helps users remove their personal information from data brokers and other...Show More
DeleteMe is a service provided by Abine that helps users remove their personal information from data brokers and other websites to protect their privacy online. Show Less
Hushed
Hushed
Gives you a pseudo phone number to call and text with.
Gives you a pseudo phone number to call and text with. Show Less
IOLO ByePass
IOLO ByePass
This Password manager safeguards your passwords and financial info from online threats.
This Password manager safeguards your passwords and financial info from online threats. Show Less
IOLO Privacy Guardian
IOLO Privacy Guardian is a software that helps protect users' personal information by removing traces of online and...Show More
IOLO Privacy Guardian is a software that helps protect users' personal information by removing traces of online and offline activity. Show Less
CCleaner Kamo
Kamo
Kamo is a privacy app designed to protect your identity from advanced tracking techniques like fingerprinting and...Show More
Kamo is a privacy app designed to protect your identity from advanced tracking techniques like fingerprinting and tracking. Show Less
Localize
Localize
Localize is a phone tracking service that allows users to track the location of a phone by its number.
Localize is a phone tracking service that allows users to track the location of a phone by its number. Show Less
Social Catfish
Social Catfish
Social Catfish is an online service that helps individuals verify and investigate the identity of people they meet...Show More
Social Catfish is an online service that helps individuals verify and investigate the identity of people they meet online, including potential scammers and catfishers. Show Less
Surfshark Alternative ID
Safeguard your online identity with Surfshark Alternative ID, a unique feature that generates a brand-new persona and...Show More
Safeguard your online identity with Surfshark Alternative ID, a unique feature that generates a brand-new persona and email address for you to use online. Show Less
OmniWatch
OmniWatch
Safeguard your identity with OmniWatch, the comprehensive identity theft protection service that provides proactive...Show More
Safeguard your identity with OmniWatch, the comprehensive identity theft protection service that provides proactive monitoring, dark web surveillance, and expert assistance in case of a breach. Show Less
Glassagram
Glassagram
Glassagram is an anonymous Instagram viewer that allows you to peek at profiles and stories without revealing your...Show More
Glassagram is an anonymous Instagram viewer that allows you to peek at profiles and stories without revealing your identity. Show Less
Avast AntiTrack
Avast AntiTrack
Avast AntiTrack is a privacy-focused software designed to prevent online tracking and protect users' digital identities...Show More
Avast AntiTrack is a privacy-focused software designed to prevent online tracking and protect users' digital identities by masking their online behavior and clearing tracking cookies. Show Less
Saily eSIM
Saily eSIM
Saily eSIM is a new service by NordVPN that lets you buy affordable data plans for international travel on your phone.
Saily eSIM is a new service by NordVPN that lets you buy affordable data plans for international travel on your phone. Show Less
aloSIM
aloSIM
aloSIM is an eSIM app that lets you buy cheap prepaid data plans for travel in over 175 countries.
aloSIM is an eSIM app that lets you buy cheap prepaid data plans for travel in over 175 countries. Show Less

CCleaner Kamo Review: Frequently Asked Questions

Is Kamo Safe?

If you are wondering whether Kamo by CCleaner is safe, you should know that it is a privacy app you can use with confidence. In fact, it uses privacy protection tools like a VPN, anti-fingerprinting technology, an ad blocker, and the like for privacy protection and data security.

Is Kamo Different From CCleaner?

Both Kamo and CCleaner are from Piriform; however, they work differently and serve distinct functions. Kamo protects your identity by injecting fake digital fingerprints into your browser data to throw trackers and advertisers off track.

CCleaner is a system cleaner and optimizer that frees up space by clearing your system of junk and optimizing it to perform optimally.

Is Kamo An Antivirus?

No, Kamo is not an antivirus; however, it can protect your PC from malware and adware infections by blocking malicious traffic and preventing analytics that compromise your privacy.

Kamo enhances your online experience by establishing a private connection through a secure, virtual, encrypted tunnel, ensuring data transmission between your PC and the internet is private and shielded from government spies, hackers, and ISPs who might monitor your activities.

Therefore, to further enhance privacy, it is advisable to use a recommended antivirus alongside Kamo and CCleaner for comprehensive system protection.

Is Kamo By CCleaner Free?

No, Kamo by CCleaner is not free. The pricing for the software starts at $24.95 per year, depending on the plan you choose.

Kamo excels in safeguarding your online privacy, making it a highly effective tool for protecting your private data and ensuring the security of your devices. It offers robust tracking protection by detecting and blocking malicious websites and tracking cookies, while also safeguarding your online identity.

CCleaner emerges as an excellent option for those seeking a comprehensive security and privacy solution.

Kamo boasts an array of features designed to safeguard your devices, data, and identity, all available at a competitive subscription cost compared to similar offerings on the market.

What is CCleaner Kamo?

CCleaner Kamo is a privacy-focused tool designed to protect your online identity and prevent tracking while browsing the internet. It helps mask your digital footprint by blocking tracking cookies, preventing websites from collecting your personal information, and offering features like automatic clearing of browsing data.

How does CCleaner Kamo work?

CCleaner Kamo works by masking your online activity and blocking cookies and trackers that collect data about your browsing habits. It also helps clear sensitive data, such as your browsing history, cached files, and passwords, ensuring better privacy.

Does CCleaner Kamo slow down my computer?

No, CCleaner Kamo is lightweight and designed to run in the background without affecting your system’s performance. It operates efficiently, so you should not notice any significant slowdowns while using it.

Does CCleaner Kamo work with all browsers?

CCleaner Kamo is compatible with most major browsers, including Google Chrome, Microsoft Edge, and Mozilla Firefox. Although it may not be fully compatible with all lesser-known or niche browsers, it supports the most commonly used ones.

How much does CCleaner Kamo cost?

CCleaner Kamo operates on a subscription model, charging a monthly or annual fee; however, it often offers a free trial for new users. Pricing details can vary depending on promotional offers and your subscription plan.

Can CCleaner Kamo be used on mobile devices?

Currently, CCleaner Kamo is primarily designed for desktop usage (Windows and Mac). It doesn’t have a dedicated mobile app, but users can still gain some privacy benefits through other mobile privacy tools.

A Final Word On The CCleaner Kamo Review

The integration of Kamo Piriform’s patented anti-fingerprint technology with VPN capabilities makes Kamo a compelling tool for privacy and data protection.

Kamo’s unique ability to generate random and false digital footprints to protect your personal data, thereby thwarting advertising companies from compiling a matching profile of you, distinguishes it from other privacy-protection tools.

Overall, Kamo does not come in as a substitute for premium VPN services since it is lacking in essential features like Kill Switch, Split tunneling, robust VPN protocols, Multihop, etc.; it does serve as a good substitute for users who may not be able to afford pricey VPN services, but desire to enjoy online anonymity and data protection.

CCleaner Kamo
Kamo
Kamo is a privacy app designed to protect your identity from advanced tracking techniques like fingerprinting and...Show More
Kamo is a privacy app designed to protect your identity from advanced tracking techniques like fingerprinting and tracking. Show Less

==>> Get Kamo


INTERESTING POSTS
How To Identify And Avoid SMS Scams (With Infographics)

How to Identify and Avoid SMS Scams (With Infographics)

Today, I will show you how to identify and avoid SMS scams. I will also add an infographic.

The digital age has ushered in an era of unparalleled convenience. Our smartphones, once a novelty, have become an extension of ourselves, serving as organizers, communication hubs, and gateways to information.

However, this convenience has a dark side: the rise of sophisticated scams and phishing attempts targeting these devices. Short Message Service (SMS), commonly known as texting, has become a prime battleground for these malicious actors.

This guide equips you with the knowledge to combat SMS scams and protect yourself from their deceptive tactics. We’ll delve into the signs of these scams, explore preventative measures, and provide actionable tips to secure your information and finances.

The Rise of SMS Scams

The Rise of SMS Scams

SMS scams, also known as smishing (SMS phishing), exploit text messages to trick unsuspecting users into revealing personal information, clicking on malicious links, or sending money. These scams can have devastating consequences, leading to identity theft, financial loss, and even emotional distress.

The allure of SMS scams lies in their ability to appear legitimate. Scammers often employ various techniques to manipulate users, including:

  • Social Engineering: They exploit psychological tactics to create a sense of urgency, fear, or excitement, prompting users to react impulsively without due diligence.
  • Spoofing: Scammers can manipulate the sender’s information to make it appear as if the message comes from a legitimate source, such as a bank, government agency, or well-known company.
  • Sense of Scarcity: They might create a sense of urgency by claiming your account is locked, a limited-time offer expires, or a package requiring immediate payment.

The prevalence of SMS scams highlights the importance of cybersecurity awareness. Understanding how these scams work and recognizing the red flags can significantly reduce your risk of becoming a target.

READ ALSO: 12 Common Online Scam Tactics: Shielding Yourself from Digital Deception

Warning Signs of SMS Scams

Here are some key warning signs to be on the lookout for when you receive a text message:

  • Urgency and Pressure: Does the message create a sense of urgency or pressure to act immediately? Scammers often use scare tactics to cloud your judgment and prevent you from thinking critically.
  • Requests for Personal Information: Be wary of messages asking for personal details like your Social Security number, bank account information, passwords, or online account credentials. Legitimate institutions rarely request such information via text message.
  • Suspicious Links: Avoid clicking on links embedded within SMS messages, especially those from unknown senders. Clicking on these links might redirect you to phishing websites that steal your information or infect your device with malware.
  • Grammar and Spelling Errors: Grammatical errors, typos, and unprofessional language are often hallmarks of scam messages. Legitimate businesses typically maintain high standards for communication.
  • Offers That Seem Too Good to Be True: Beware of messages promising extravagant prizes, unbelievable discounts, or sudden financial windfalls. These are classic tactics used to lure unsuspecting victims.
  • Unexpected Fees or Charges: Do not respond to messages demanding immediate payment for unforeseen fees or charges, especially if you haven’t authorized such charges.

READ ALSO: How To Read Someone’s Text MessagesSomeone’sTheir Phone

Essential Tips to Avoid SMS Scams

Essential Tips to Avoid SMS Scams

By incorporating these practical tips into your daily routine, you can significantly reduce your vulnerability to SMS scams:

  • Verification is Key: If a text message appears to be from a legitimate source, such as your bank or credit card company, don’t respond directly to the message. Instead, contact the organization directly through a verified phone number or website to confirm its authenticity.
  • Don’t Engage with UnknoDon’tmbers: Avoid responding to text messages from unknown numbers, particularly those that seem suspicious. Silence unknown numbers or report them to your mobile carrier.
  • Strengthen Your Passwords: Use strong and unique passwords for all your online accounts and enable two-factor authentication (2FA) whenever possible. This adds an extra layer of security to prevent unauthorized access even if your password is compromised.
  • Beware of Spoofing: Be skeptical of any message, even if it appears to come from a familiar number. Scammers can spoof phone numbers to make them seem legitimate.
  • Educate Yourself: Stay informed about the latest scam tactics by following reputable cybersecurity resources. Share this knowledge with your loved ones to spread awareness and protect them.
  • Report Suspicious Activity: If you receive a suspicious text message, consider reporting it to your mobile carrier or relevant authorities. This can help them track down scammers and prevent others from falling victim.
  • Anti-Spam Applications: Consider using anti-spam applications that filter out suspicious text messages and protect you from potential threats.

READ ALSO: What Are Phishing Scams And How You Can Avoid Them?

Beyond Text Messages: Expanding Your Cybersecurity Awareness

While SMS scams are a prevalent threat, it’s crucial to remember that cybersecurity goes beyond text messages.

Here are some additional areas to consider fortifying your digital defenses:

  • Email Phishing: Phishing emails are a common tactic where scammers impersonate legitimate institutions like banks, social media platforms, or online retailers. These emails often contain malicious links or attachments that can steal your personal information or infect your device with malware. Be cautious of unsolicited emails; don’t click on suspicious links or attachments; verify the sender’s address before sending them.

  • Social Media Scams: Social media platforms are breeding grounds for various scams. Scammers might create fake profiles to impersonate friends, celebrities, or companies. They might also use social engineering tactics to manipulate you into revealing personal information, clicking on malicious links, or sending money. Be cautious of friend requests from unknown individuals, verify the legitimacy of profiles before interacting, and be mindful of what information you share publicly.

  • Malicious Apps: Download apps only from trusted sources like official app stores. Read reviews before installing an app, and be wary of apps that request excessive permissions. Keep your apps updated to benefit from the latest security patches.

  • Public Wi-Fi: Public Wi-Fi networks are convenient but can be insecure. Avoid accessing sensitive information like bank accounts or online financial portals while connected to public Wi-Fi. If you must use public Wi-Fi, consider using a Virtual Private Network (VPN) to encrypt your internet traffic and add an extra layer of security.

  • Physical Security: Cybersecurity isn’t just about digitaisn’teats. Be mindful of your physical surroundings as well. Don’t leave your phone Don’tptop unattended in public places, and be careful about what information you discuss in earshot of others.

  • Regular Backups: Back up your essential data on an external hard drive or cloud storage service. In case of a cyberattack or device failure, having a backup ensures you don’t lose critical information.

How To Avoid SMS Scams

Conclusion

The digital age offers immense opportunities for connection, information, and convenience. However, it also presents new challenges in the form of cyber threats.

By understanding the tactics used in SMS scams and expanding your cybersecurity awareness, you can become a more informed and secure digital citizen.

Empower yourself and your loved ones with knowledge. Share this information and encourage open conversations about cybersecurity. Working together can create a safer and more secure online environment for everyone.


RELATED POSTS
Why Do So Many Apps Ask for Phone Number Verification?

0
Why Do So Many Apps Ask for Phone Number Verification

In this post, I will answer the question – why do so many apps ask for phone number verification?

Creating an account used to require little more than an email address and a password.

Today, many apps ask for something else before allowing users to continue: a mobile phone number.

Messaging platforms, social networks, marketplaces, delivery services, dating apps and financial applications frequently use phone verification during registration or when users perform sensitive actions.

The process is usually simple. A user enters a phone number, receives a one-time password by SMS and enters the code inside the app.
For users, it may feel like one more registration step. For app developers and businesses, however, phone verification solves several important problems at once.

So why has it become so common?

Phone Numbers Make Automated Registrations More Difficult

One of the main reasons apps ask for phone numbers is to reduce fake and automated accounts.

Creating email addresses is relatively easy. Automated systems can generate large numbers of accounts quickly, particularly when an app only requires an email address and password.

This can create problems for businesses operating platforms where each account has economic or social value.

Fake accounts may be used to:

  • send spam;
  • abuse free trials or promotional offers;
  • create fake reviews;
  • manipulate ratings;
  • scrape information;
  • send unsolicited messages;
  • operate automated bots;
  • bypass account restrictions.

Adding phone verification introduces another step that automated account creators must overcome.

It does not completely eliminate abuse, but it can increase the cost and complexity of creating large numbers of accounts.

For many apps, that additional friction is enough to significantly reduce low-effort automation.

Why Apps Often Prefer Real Mobile Numbers

Not every phone number is treated equally by online platforms.

Some verification systems attempt to distinguish between traditional mobile numbers and numbers provided through internet-based VoIP services.

A real mobile number is generally associated with a mobile carrier and can receive SMS through the conventional cellular network. A non-VoIP number similarly refers to a number that is not primarily provided through a voice-over-IP service.

These distinctions matter because some apps restrict VoIP numbers during registration as part of their anti-abuse systems.

For users, this means that simply having a number capable of receiving messages does not always guarantee that an app will accept it.

The type of number, its carrier, country and previous usage can all influence whether verification succeeds.

SMS Verification Is Easy for Users to Understand

Another advantage of phone verification is familiarity.

Almost every mobile phone can receive an SMS message, and users generally understand what to do when an app says that it has sent a verification code.

There is no additional software to install and no complicated setup process.

A typical flow takes only a few steps:

  1. Enter a phone number.
  2. Receive a verification code.
  3. Enter the code in the app.
  4. Continue using the service.

This simplicity is one of the biggest reasons SMS verification remains widespread despite the availability of newer authentication technologies.

An app can introduce an additional verification layer without requiring users to understand authentication protocols or configure specialist security tools.

Phone Verification Helps Apps Limit Duplicate Accounts

Some services want to limit how many accounts one person can create.

This is particularly common in marketplaces, social platforms and services offering bonuses or free trials.

If registration only requires an email address, creating multiple accounts is relatively easy.

Requiring a phone number gives the platform another identifier that can be used to detect repeated registrations.

Again, this is not a perfect identity system. People may legitimately own multiple phone numbers, and numbers can change owners over time.

However, from the perspective of an app, phone verification provides another useful signal that can be combined with information such as device data, IP addresses and account behaviour.

Some Apps Need to Protect Communication Between Users

For messaging, marketplace and dating applications, fake accounts can create a particularly serious problem.

These platforms depend heavily on interactions between users.

If a large proportion of accounts are bots, scammers or spammers, legitimate users quickly lose trust in the service.

Phone verification helps platforms place an additional barrier between automated account creation and direct communication with other users.

That is why verification requirements are especially common in apps built around messaging, profiles and user-generated content.

The phone number itself does not guarantee that an account is legitimate, but requiring access to a real communication channel can make large-scale abuse more difficult.

Apps Also Use Phone Numbers for Account Recovery

Verification does not end when an account is created.

A phone number can later be used to help a user recover access.

For example, an app may send an SMS code when:

  • a password has been forgotten;
  • a login attempt comes from a new device;
  • unusual account activity is detected;
  • security settings are changed;
  • the account owner requests recovery.

This makes the phone number part of the account’s security infrastructure.

It also explains why users should think carefully about which number they use for important services.

A number that works during registration but becomes unavailable later may cause problems if the application asks for another verification code during account recovery.

Why Users May Not Want to Share Their Main Phone Number

From the user’s perspective, repeatedly providing the same personal phone number creates a different set of concerns.

A primary phone number may remain with someone for many years.

During that time, it can become connected to dozens or even hundreds of accounts across different services.

This makes the phone number a persistent digital identifier.

Users may be reluctant to provide it to every new app they want to try, particularly when they are unsure whether they will continue using the service.

There are several common reasons for this.

One is spam.

A number originally provided for verification may later become another channel for promotional communication.

Another is privacy.

The fewer companies that store a user’s primary number, the fewer databases contain that identifier.

Users may also simply want to separate important accounts from less important registrations.

A personal number might be reserved for banking, work, family and essential services, while other numbers are used for apps that do not require a permanent connection to the user’s identity.

Temporary, Secondary and Non-VoIP Numbers

Users now have several options when they do not want to provide their primary mobile number to every app.

A second physical SIM card is the traditional solution, while eSIM technology makes it easier to maintain another long-term mobile number without adding a physical SIM.

Another option is a temporary number designed primarily for receiving an SMS verification message.

Services providing temporary phone numbers for SMS verification can be useful when someone needs a number for a short-term registration and does not want to expose their primary phone number.

Depending on the provider and country, these services may offer access to real mobile numbers or non-VoIP numbers connected to mobile networks rather than purely internet-based VoIP services.

This distinction can be important because certain apps are more likely to accept traditional mobile or non-VoIP numbers for verification.

However, no number type guarantees acceptance. Apps maintain their own verification rules and may change them over time.

Temporary Numbers Are Not Suitable for Every Account

Using a temporary phone number can make sense for some registrations, but it is not appropriate for every service.

The biggest issue is future access.

An application may send another verification code weeks or months after registration.

If the temporary number is no longer available, recovering the account may become difficult or impossible.

This is the main difference between a temporary number used for a one-time activation and a number that remains under the user’s control.

For services that may require repeated SMS verification, maintaining access to the same real mobile number for a longer period is more practical.

A rental phone number, for example, can provide continued access during a defined period rather than being used only for a single verification message.

Depending on the service, users may therefore choose between short-term temporary numbers, longer rental periods, or a permanent secondary SIM or eSIM.

The correct option depends on how important the account is and whether future SMS access is likely to be required.

Why Non-VoIP Numbers Matter for Some Apps

The term non-VoIP number has become increasingly common around app verification.

VoIP numbers use internet-based communications infrastructure and can be perfectly legitimate for calls and messaging. However, because some VoIP services make it relatively easy to obtain numbers at scale, certain platforms apply additional restrictions to them.

This is why users sometimes encounter messages indicating that a particular number cannot be used for verification.

A non-VoIP or real mobile number does not automatically bypass an app’s security systems. The platform may still evaluate other signals, including the carrier, geographic region, previous account activity and its own anti-fraud rules.

Nevertheless, understanding the difference helps explain why one SMS-enabled number may work with an application while another does not.

Important Accounts Should Use Numbers You Control Long Term

There are situations where convenience and privacy should not outweigh reliable account recovery.

Banking applications, government services, primary email accounts, cryptocurrency platforms and important business systems can contain valuable information or assets.

For these accounts, users should generally register a real mobile number they expect to control permanently.

Losing access to a temporary number can become a serious problem if the service later requires SMS verification.

The same principle applies to any account where losing access would create significant financial or personal consequences.

Temporary or rental numbers are better suited to situations where the risk of losing long-term access is understood and acceptable.

Why Apps Do Not Simply Use Email Instead

Email verification remains extremely common, but it solves a slightly different problem.

An email address proves that a user can access an inbox.

It does not necessarily provide much resistance to large-scale account creation because email accounts can be generated relatively easily.

Phone numbers generally introduce more friction.

Real mobile numbers are connected to telecom infrastructure, and acquiring large numbers of them typically requires more resources than generating email addresses.

That makes phone verification attractive for apps that experience significant abuse.

Many services therefore combine both methods.

Email may be used as the primary communication channel, while phone verification acts as an additional trust signal.

SMS Verification Is Not Perfect Security

Although phone verification can reduce abuse, it should not be treated as proof that a user is legitimate.

Phone numbers can be reassigned.

Devices can be stolen.

SMS messages can sometimes be intercepted through attacks against mobile accounts or telecom infrastructure.

Fraudsters can also obtain access to multiple numbers.

For this reason, security-sensitive applications increasingly use multiple signals rather than relying entirely on SMS.

These may include:

  • device recognition;
  • authenticator applications;
  • passkeys;
  • behavioural analysis;
  • biometric authentication;
  • risk-based login systems.

SMS is therefore best understood as one component of a larger authentication system.

Its biggest advantages remain accessibility and simplicity.

Verification Is Ultimately a Trade-Off

Every app has to balance security against usability.

If registration is too easy, automated accounts and fraud become easier.

If verification becomes too complicated, legitimate users may abandon the registration process.

Phone verification has become popular because it sits somewhere in the middle.

It creates meaningful friction for automated registrations while remaining familiar to most users.

For businesses, this makes SMS verification a practical tool for reducing abuse.

For consumers, however, it also creates a reason to think more carefully about where their primary phone number is shared and what type of number they use for different accounts.

Temporary numbers can provide separation for short-term registrations. Rental numbers can retain access for longer periods. Real mobile and non-VoIP numbers may also be required by apps with stricter verification systems.

The question is therefore no longer simply whether an app can send a verification code.

It is which phone number should be connected to that app — and for how long.


INTERESTING POSTS