The supply chain doesn’t break at logistics anymore. It breaks at login.
According to the Thales Digital Trust Index 2026 report, 89% of partner users have delayed or abandoned work due to access issues. Let that sink in and imagine the impact on your topline.
This elevates the issue from an IT convenience to revenue at risk, forcing organizations to examine how friction in their partner/supplier/reseller onboarding and authentication processes might be undermining bigger, more long-term gains.
Smooth Partner Onboarding is the Exception, Not the Rule – Unfortunately
The Thales report reveals that among partners, only 22% receive working login details immediately; the rest have to wait.
In addition:
Only 30% get full permissions the first time
66% lose access to external partner systems while they still need it
92% experienced access issues overall
The problem (beyond what’s already been laid out) is that in these situations, partners find workarounds. When faced with access friction, nearly two-thirds (66%) have shared or borrowed credentials, with over half citing slow official processes as the cause.
These issues present even more business risks. Not only does delayed access prevent partners from doing their work or delivering value, but it also leads to the kind of technical fence-jumping that could cause companies to lose value they’ve already gained.
Beyond the productivity hit, delayed access and credential workarounds accumulate what the report calls ‘silent security debt’, a growing exposure to breaches and compliance risk that rarely gets priced into onboarding cost calculations.
When it takes an average of 30-60 days for third-party assessments alone and 1-6 months to bring them on board, these kinds of delays are as expensive as they are inexcusable.
Putting a Price Tag on Onboarding Delays
If your partners aren’t logging in cleanly and immediately, they’re not fully onboarded. And if they’re not fully onboarded, you’re not seeing full ROI.
Over a quarter (26%) of companies report losing $500k or more due to partner integration issues. Slow onboarding leads to missed deals, delayed time-to-revenue, and partner churn, incurring additional costs along the way.
It costs thousands of dollars to onboard a supplier, and companies are looking to make that up with quick time-to-value. Login issues, false starts, and ongoing friction not only delay start times but also throw off long-term timelines, wreck projected productivity, and force teams to redo expectations. The result: work waste and revenue loss.
To highlight just one area of loss, password resets still cost around $70 per incident, and, applied to real user populations, that equates to $37,800 annually for 3,000 registered users. Whether those users are your employees or third-party employees using those credentials to log in to your systems.
It is worth noting that most IAM administration is still done in-house, but research shows that more partners are willing to take this on. More on this in the next section.
In the worst cases, too much friction could lead to missed opportunities, and this holds true across the board. A quarter of businesses report losing a deal due to slow legal onboarding processes. According to Fenergo’s 2025 Financial Crime Industry Trends report, 70% of financial institutions globally lost clients due to slow or inefficient onboarding.
And like the opening stat introduced, “89% of partner users have abandoned or delayed a work task with an external partner in the past 12 months due to a website or app issue.” No matter the industry, or if it’s B2B or B2C, IAM friction in the onboarding process is a cost center, but it’s one that can be avoided.
What Partners Want out of B2B Access?
The Thales research revealed an interesting trend that could help companies offset the cost of B2B access: shifting more of the burden to partners themselves. Perhaps not surprisingly, partners want that.
According to the report, partners want more self-service access, so access is increasingly in their hands. Over half (54%) wanted the ability to reset authentication factors themselves, and 52% wanted to see their current entitlements.
Delegated User Management, a key component of Extended Enterprise Access, fills this need, allowing organizations to maintain overarching control over identity systems while the responsibility for third-party access is offloaded to the third parties themselves:
The host organization decides which IAM controls can be delegated. A delegated manager within the partner organization takes the lead on that, acting as a proxy admin for their users. That partner has the power to grant, revoke, or update access for their team, and all requests go through them.
This leads to offset costs for the host while resulting in greater (and faster) ROI. IT gets fewer repetitive tickets; access issues get resolved faster, so teams can get back to work sooner; and third-party IAM issues don’t result in greater costs as the partnership scales.
Offloading IAM may be step one. But no matter where the onus resides, automation has to be step two.
Making Automated B2B Access the Norm
When surveyed by Thales, only 22% reported that system access was automated or “provided immediately.” That means four out of five had to wait. And in an era of AI and hyperautomation, many are wondering why.
The absence of these automated workflows takes a toll in other areas as well: only 19% reported that access changes keep pace with working needs. This can be a problem. A sale could be lost if the distributor can’t retrieve the proper inventory information. Or a competing vendor may be quoted when a reseller can’t access pricing tools.
Partner/B2B IAM is a Financial Issue
All this underscores the fact that B2B IAM extends far beyond convenience and PX. IAM failures delay projects and billing cycles. They propagate outdated information and force host companies to bear supplier costs they shouldn’t.
This makes partner IAM not just an administrative issue, but a financial one with revenue at stake.
Because people are accessing these systems, friction leads to frustration, errors, time loss, and a domino effect of lost productivity. It sets everything off on the wrong foot, and in the case of many deals, things won’t recover.
Partnerships don’t have to come with a buffer for operational drain. To ensure they don’t, senior leaders have to take B2B access out of the IT weeds and into the boardroom.
This post will show you how to prevent Xiaomi from spying on you and stealing your data.
Xiaomi is a high-end budget smartphone producer with popular phone brands to its credit. However, there have been controversies about data theft and accusations of Xiaomi spying on users’ activities.
Cybersecurity researchers Garbi Cirlig and Andrew Tierney have reported several data breaches associated with the Redmi Note 8 and the Mi Browser. The browser collects users’ data while browsing in Incognito mode.
Although Xiaomi denied allegations of it collecting users’ data and spying on their browsing activities, it mentioned that data are collected with users’ consent, such data are collected as anonymous data and used for internal analysis, and no Personally Identifiable Information is linked to collected data.
If you’re a Xiaomi phone user, here are ways to protect your data and privacy on Xiaomi and Mi browsers.
How To Stop Xiaomi From Stealing Your Data And Spying On You
Data collection is turned on by default for most default apps on the Xiaomi smartphone brand. Hence, to prevent Xiaomi from collecting your data, you have to turn off default data collection for each of the pre-installed apps on your Xiaomi smartphone. That way, you can prevent Xiaomi spying activities.
Xiaomi phones offer great features at competitive prices, but concerns linger about data collection practices. While Xiaomi claims anonymized data collection, many users prefer to minimize the amount of information their phone sends back to the company’s servers.
Here are some steps you can take to reduce data collection on your Xiaomi phone:
During Initial Setup
Scrutinize Permissions: Pay close attention to app permissions when setting up your phone. Only grant apps the permissions they need to function. Deny access to unnecessary features like location tracking for apps that don’t require it.
Disable Personalization Services: Xiaomi offers personalization services that collect data to tailor recommendations and features. If you’re uncomfortable with this level of data collection, opt out of these services during setup.
Within MIUI Settings
Privacy Protection: Dive into the MIUI privacy settings menu. You’ll find options for managing app behavior, location tracking, and data access here.
Location Services: Control which apps have access to your location and when. Consider disabling location services for apps that don’t require it.
System Apps: Review system app permissions and disable access for features you don’t use, such as targeted advertising or app recommendations.
Usage Data & Diagnostics: This setting allows Xiaomi to collect data about your app usage patterns. If you’re privacy-conscious, disable this option.
Mi Cloud Sync: Xiaomi Cloud offers cloud storage and backup features. If you don’t use it, disable syncing to prevent unnecessary data upload.
Beyond Settings
Use Alternative Apps: Consider replacing Xiaomi’s pre-installed apps (like browser or security app) with open-source alternatives that offer more control over data collection.
Custom ROMs (Advanced Users): For experienced users, installing a custom ROM can replace MIUI with a different operating system that may offer more privacy controls. However, this process carries risks and requires technical expertise.
Be Mindful of App Choices: When installing new apps, be mindful of their permissions requests. Research the app’s privacy policy to understand its data collection practices. Choose apps with strong privacy reputations whenever possible.
By following these steps to prevent Xiaomi spying, you can significantly reduce the data your Xiaomi phone transmits. While achieving complete isolation is difficult, these measures offer more control over your privacy and can help you feel more secure using your Xiaomi device.
While ultimately preventing any data collection might be difficult, here are some steps you can take to significantly limit Xiaomi’s ability to “spy” on you:
Taking Control During Setup
Permission Patrol: Don’t rush through the initial setup. Scrutinize app permissions carefully. Only grant access to features essential for the app to function. Ask yourself, “Does this flashlight app really need access to my location?” Deny permissions that seem excessive.
Nix Personalization: Xiaomi offers personalization services that gather data to tailor features and recommendations. If this level of data collection makes you uncomfortable, opt out during setup.
MIUI Privacy Settings Deep Dive
Privacy Champion: Dive into the MIUI privacy settings menu. This is your central hub for controlling data collection. Here you can manage app behavior, location tracking, and data access for various features.
Location Lockdown: Control which apps have access to your location and when. Consider disabling location services entirely for apps that don’t inherently require it (like a photo gallery).
System App Scrutiny: Review system app permissions and disable access for features you don’t use. This could include targeted advertising or app recommendations.
Data Detox: The “Usage Data & Diagnostics” setting allows Xiaomi to collect data about your app usage patterns. If you’re privacy-conscious, disable this option to prevent this data transfer.
Cloud Control: Xiaomi Cloud offers cloud storage and backup features. If you don’t use it, disable syncing to prevent unnecessary data upload to their servers.
Going Beyond Settings
App Alternatives: Consider replacing Xiaomi’s pre-installed apps (like browser or security app) with open-source alternatives. These often offer more control over data collection and may prioritize user privacy.
Custom ROM Caution (Advanced Users Only): If you’re comfortable with technical tinkering, installing a custom ROM can replace MIUI with a different operating system that might offer more granular privacy controls. However, proceed cautiously as this process can be risky and requires technical expertise.
App Selection Awareness: Be mindful of app permissions when installing new apps. Don’t just blindly accept everything. Research the app’s privacy policy to understand its data collection practices. Choose apps with strong privacy reputations whenever possible.
How To Disable Xiaomi’s MIUI From Collecting Your Data
Xiaomi’s MIUI (Mi User Interface) collects your data to serve you with personalized ads. You can prevent MIUI from collecting your data by revoking MIUI’s data collection privileges by taking the following steps.
Launch the Settings app on your Xiaomi phone
Scroll through and tap on ‘Additional Settings.’
In the ‘Additional Settings’ page, tap on ‘Authorization & revocation
Toggle off the MSA (MIUI System Ads) button.
Follow the prompt and wait for 10 seconds, after which you can now tap on ‘Revoke.’
If you get a ‘Couldn’t Revoke Authorization’ message, ensure your data is turned on and retry again.
To disable ad services and data usage collection,
Returning to step iii, in the ‘Additional Settings’ page, tap ‘Privacy.’
In the ‘Privacy menu,’ toggle off the ‘User Experience Program’ and ‘Send diagnostic data automatically’ to prevent Xiaomi from sending your data remotely to its server.
Also, tap on ‘Ad Services’ in the ‘Additional Settings’ and ‘Disable’ ‘Personalized Ad Recommendations’ to prevent Xiaomi from collecting your data to serve you with ads.
Following the steps above is a surefire way of preventing Xiaomi from collecting and sending your data remotely to its servers while you enjoy a fantastic User Experience on your Xiaomi device.
By following these steps, you can significantly reduce the amount of data your Xiaomi phone transmits to Xiaomi’s servers.
While achieving complete isolation might be difficult, these measures empower you to regain control of your privacy and use your Xiaomi device more confidently.
In the latest development, the fastest way to trade prediction markets just went live.
Banana Predict is now live in beta at predict.bananagun.io, giving traders a dedicated terminal for prediction markets built on the same speed obsession that made Banana Gun a name in crypto trading.
You get a real order book, cent-priced Yes and No shares, and a live probability percentage on every market. No more toggling between three tabs to figure out what a trade actually pays out.
This matters because prediction markets moved fast in 2026 and most interfaces did not keep up. Banana Predict was built to close that gap, and the team is positioning it as the fastest way to trade Polymarket markets without leaving the Banana ecosystem.
What Banana Predict Actually Is
Banana Predict is a prediction-markets trading terminal inside the Banana Gun ecosystem. It mirrors liquidity from Polymarket, so you are trading against real depth, not a synthetic order book built just for the app.
Resolution follows a UMA-style oracle process, meaning outcomes get settled through the same optimistic-oracle logic that Polymarket itself relies on. That is the part traders tend to ask about first, and it is baked in from day one rather than bolted on later.
The platform runs as a mobile-first web app. You connect a wallet to trade, and from there every market shows a payout preview before you commit, along with a Rules panel so you know exactly what triggers a Yes or No resolution.
How the Trading Experience Works
Every market on Banana Predict trades Yes or No shares priced in cents, with a live order book behind each side. You see the current probability percentage update in real time as orders fill, which turns the abstract question of “will this happen” into a number you can act on.
Before you submit a trade, the interface shows you a payout preview so there is no guessing what a winning position actually returns. Pair that with the per-market Rules section and you get the kind of clarity that prediction-market traders have been asking platforms to build for years.
Twelve Categories, Five Ways to Discover Markets
Banana Predict organizes markets across twelve categories: Politics, Sports, Crypto, Finance, Geopolitics, Earnings, Tech, Culture, World, Economy, Climate and Science, and Elections. That range covers the events traders actually watch, from Fed rate decisions to championship outcomes to election calls.
Finding the right market is handled through five discovery tabs: Trending, Breaking, New, Recurring, and Bonding. Trending surfaces what volume is flowing into right now. Breaking flags markets tied to news as it happens. New and Recurring separate one-off events from markets that repeat on a schedule, and Bonding tracks markets still building liquidity before they hit full depth.
Tools Built for Traders Who Track Other Traders
Banana Predict ships with a full Portfolio view so you can track open positions and resolved trades in one place. A Leaderboard ranks top performers, and Copytrade lets you mirror their positions directly, a feature that fits naturally with Banana Gun’s history in copy trading on the spot side.
Wallet Tracker and Social Tracker, also called X Tracker, round out the toolkit. Wallet Tracker follows on-chain activity from addresses you choose to watch, while Social Tracker pulls signal from X activity tied to specific traders or accounts. Together they give you a way to follow smart money instead of guessing where it moved.
What This Means for Prediction-Market Traders
Speed has always been Banana Gun’s core identity, first in cross-chain sniping, then in copy trading through its Telegram bot. Banana Predict extends that same philosophy into prediction markets, where execution speed and clean data have historically lagged behind spot and derivatives trading.
The beta is open now. If you already trade Polymarket markets or you are new to prediction trading and want an interface that shows probability, payout, and rules in one screen, this is worth testing today.
Frequently Asked Questions
Is Banana Predict live yet?
Yes. Banana Predict is live now in beta at predict.bananagun.io.
Do I need a wallet to use Banana Predict?
You can browse markets without one, but trading requires connecting a wallet.
Where does Banana Predict get its market liquidity?
Markets mirror liquidity from Polymarket, so order books reflect real trading depth rather than an isolated pool.
How are markets resolved on Banana Predict?
Through a UMA-style optimistic oracle process, the same resolution logic used by Polymarket.
What categories of markets can I trade?
Twelve categories are live: Politics, Sports, Crypto, Finance, Geopolitics, Earnings, Tech, Culture, World, Economy, Climate and Science, and Elections.
In this post, I will show you how I’d use the GLM-5.2 API for a long-running coding agent.
If I were setting up a coding agent today — the kind that’s supposed to run for hours, work through a real codebase, and come back with something actually finished rather than a half-baked first attempt — GLM-5.2 api is where I’d start.
Not because it’s the flashiest name in the room, but because long-running agents fail in a very specific way, and this is one of the few models actually built with that failure mode in mind.
The Problem Nobody Warns You About Until It Happens
Here’s what nobody tells you before you build your first long-running agent: the failure isn’t usually a dramatic crash. It’s slower and quieter than that. The agent starts strong, makes good decisions for the first stretch of a task, and then somewhere around hour two or three, it starts losing the plot.
It forgets a constraint it agreed to earlier. It re-does work it already finished. It confidently “fixes” something that wasn’t broken. None of this shows up in a quick demo, because demos are short. It only shows up once you actually let the thing run.
That’s the exact scenario GLM-5.2 was built around, which is why it’s the model I’d reach for first rather than whatever’s topping a general leaderboard that week.
Why I’d Trust It to Actually Stay on Track
What sold me isn’t a single benchmark number, it’s the pattern across all of them. GLM-5.2 keeps showing up strongest specifically on the evaluations that simulate messy, hours-long engineering work rather than quick, self-contained problems.
On the kind of test that mimics an agent looping through a real repository — reading, planning, executing, checking its own work — it holds up close to the very best models out there, closed or open. That’s a different skill than being clever on a single tricky question, and it’s the one that actually matters once your agent’s task list is measured in hours instead of minutes.
Giving It Room to Actually See the Whole Project
The other piece I’d lean on hard is how much it can hold in view at once. A long-running agent working across a real codebase needs to see more than the one file it’s currently editing — it needs the surrounding context, the conventions the rest of the project follows, the pieces it touched three steps ago. GLM-5.2’s context window is big enough to hold a genuinely sizeable project in view all at once, instead of forcing the agent to work blind, one small slice at a time, and hope nothing important got left out of frame.
That’s less “nice to have” and more the actual difference between an agent that understands what it’s working inside of and one that’s just guessing.
If you’re building this kind of setup yourself, it’s worth spending a little time in theGLM-5.2 api listing before committing to anything — seeing what it sits next to, and what the nearby options trade off, tends to clarify what you actually need a lot faster than reading a single spec sheet in isolation.
The One Feature I Didn’t Expect to Care About This Much
GLM-5.2 can also be paired with a web-search tool during a task. Instead of switching to a separate model version, the agent can invoke search when it needs current documentation, recent release notes, or an external source to verify an assumption. That sounds like a small add-on until you picture what a long agent run actually needs.
A coding agent working for hours doesn’t just need to reason about the code in front of it — it occasionally needs to check something outside its own head. Did a library’s API change since the model’s training data was collected? Is there a known issue with the exact error it just hit? Rather than the agent confidently guessing at an answer that might be out of date, it can actually go look, mid-task, without a separate setup. For anything that touches fast-moving dependencies or recent library changes, that’s the difference between an agent that occasionally hallucinates its way past a stale assumption and one that just checks.
Where I’d Actually Draw the Line
I wouldn’t pretend this is the right tool for everything, and I’d be doing you a disservice if I acted like it was. If the job is a tight, well-specified algorithmic problem — something closer to a competitive programming puzzle than an open-ended engineering task — there are other models built specifically to be faster and cheaper at exactly that kind of question, and I’d route to one of those instead rather than defaulting to the same model for every job.
The honest way to think about it is that GLM-5.2 is the specialist for staying coherent across a long, messy, multi-step project, not the fastest or cheapest option for every single request an agent might make along the way. AGLM-5.2 API for coding comparison against a more math-and-algorithms-focused alternative is worth reading before you commit your whole pipeline to one model, because the right answer genuinely depends on which of those two failure modes worries you more.
What I’d Actually Build
If I were setting this up for real, I wouldn’t hand every single request to the same configuration. I’d let the long-horizon planning and the bulk of the repository work run through GLM-5.2, with the web-search variant switched on specifically for the moments the agent needs to check something outside its own training — a library version, a recent breaking change, a fix someone already published.
And I’d keep a faster, narrower model on standby for the quick, tightly scoped questions that don’t need any of that context or reasoning depth. That’s not a compromise so much as it’s just matching the tool to the job, one more time, the same way I’d want any agent I trust with real work to be built.
In this post, I will be talking about protecting business data when teams work from different locations.
The transition to remote work has shifted the approach companies use for safeguarding sensitive data. When staff members access company systems from geographically dispersed locations, traditional perimeter defences lose effectiveness, creating new entry points that adversaries seek to exploit. Threat actors frequently target remote desktop connections as these often present vulnerabilities for business networks.
Since 2020, there has been an increase in cyberattacks aimed at remote access systems. Attackers actively seek opportunities to breach business defences when individuals operate from home offices or off-site locations. Insufficient security protocols in remote desktop deployments open the door to malware, ransomware, or data theft. Lapses such as use of weak passwords or delays in applying necessary updates further raise the risk.
For organisations managing teams across different sites, maintaining a balance between data accessibility and strong protection is now essential. Secure remote access depends on layered measures that include strong authentication, full encryption, ongoing monitoring, and regular user security training. Companies adopting this strategy help sustain productivity and resilience while making severe security breaches less likely.
The Rising Security Risks of Remote Work Environments
The rapid shift to remote work has created increased opportunities for cybersecurity threats. Many businesses now support remote work, but a significant number lack proper security measures. Applying strong cyber hygiene and choosing to work securely with remote access software that builds in both data encryption and strong user authentication can close common gaps. This approach ensures that endpoints and connections benefit from layered protection, lowering risk from exploitable weaknesses.
Data breaches related to remote work vulnerabilities have become a growing concern for businesses, with costs and risks continuing to rise as more organizations adopt remote and hybrid work models.
Attackers frequently target Remote Desktop Protocol (RDP) connections. Common attack tactics include brute force password attempts, man-in-the-middle interceptions, and abusing unpatched RDP vulnerabilities. Traditional VPNs often fail to address all security risks in remote work settings because their protection usually ends at securing the tunneling of data between endpoints.
Essential Security Measures for Remote Desktop Access
Strong authentication forms the foundation of secure remote access. Multi-factor authentication (MFA) should be mandatory for all remote connections. This combines something users know (password), something they have (mobile device), and sometimes something they are (biometrics). MFA is widely recommended by security experts to reduce unauthorised access risks.
Data encryption protects information during transmission. All remote desktop connections should use end-to-end encryption with TLS 1.2 or higher because unencrypted sessions give attackers an opportunity to view or hijack sensitive data. Session management policies add another security layer. Organisations should implement automatic timeouts that disconnect idle sessions after a set period to prevent unauthorised access if users leave devices unattended.
IP filtering and geolocation restrictions limit connection sources. Companies can configure remote access systems to accept connections only from approved locations or IP ranges, blocking connection attempts from high-risk regions or unexpected places.
Implementing Zero Trust Architecture
Zero trust architecture requires companies to verify every user and device at every step, regardless of where the connection originates. For implementation, organisations should begin with segmenting their network so remote desktop users only access the exact resources needed for their tasks, and nothing more. Instead of full permissions, IT teams can assign application-level access and apply controls that check identities continuously, not just at login.
Administrators need to use strong authentication for every access attempt, apply end-to-end encryption for all remote sessions, and monitor user behaviour in real time. If any unusual activity is detected, such as a login from an unfamiliar location or attempts to access restricted files, system settings should automatically block the session and alert security staff.
Continuous verification is a key part of zero trust, unlike traditional perimeter-based security that validates users only at initial login. Remote desktop software with zero trust capabilities constantly monitors sessions for suspicious activities and can terminate connections if unusual patterns emerge. Using least privilege access is a practical step toward zero trust. Organisations should restrict user permissions to only what is necessary for their specific job functions.
Data Protection Strategies Across Distributed Teams
Organisations must carefully plan their data storage methods for remote teams, because each approach creates different security and management needs. Centralised storage means all business data stays on company-controlled servers, making it easier for IT teams to enforce uniform security policies, back up files, and maintain compliance.
However, securing remote access to these centralised resources becomes a major concern, as attackers may target remote desktop gateways or VPN connections searching for a single point of entry. Companies therefore need to implement identity verification, encrypted tunnels, and regular access audits to prevent breaches.
With distributed storage, some data is kept directly on remote user devices to speed up workflow and improve offline access. While this convenience allows staff to access documents without lag or connectivity barriers, it puts a heavier security burden on endpoint devices. Organisations need strict endpoint security protocols, including required encryption and automatic update enforcement.
Data classification systems help manage information security across locations. Companies should categorise data based on sensitivity (public, internal, confidential, restricted) and apply appropriate security controls to each level. This helps ensure the most sensitive information receives the strongest protections.
A strong remote work security policy needs several key components. These include device requirements, network security standards, authentication protocols, data handling rules, incident reporting procedures, and acceptable use guidelines. The policy should be clear, accessible, and regularly updated to address emerging threats.
Employee training is important for policy effectiveness. Each member of a remote workforce should regularly take part in security awareness training. This covers how to create strong passwords, ways to identify phishing attempts, methods for sharing files securely, and steps for setting up a home Wi-Fi network to reduce outside risks.
Incident response planning must cover remote access breaches. For this, companies should build clear procedures focused on remote work realities. Organisations should set up a central reporting channel like a dedicated email or hotline so staff can immediately flag suspicious activity including unauthorised logins or malware alerts.
Recovery plans should include actions like resetting passwords, restoring files from secure backups, and providing guidance to affected users about next steps. Clear communication protocols help everyone know what information must be shared and with whom. Regular practice drills help strengthen the process and support rapid, coordinated action during real threats.
Some industries are subject to additional legal and regulatory requirements regarding data protection and remote access. Organisations operating in these sectors should ensure their remote work solutions and policies align with relevant standards and undergo regular security assessments to identify and address potential vulnerabilities.
Discover how AI models are revolutionizing cybersecurity workflows through automated threat detection, incident response, secure development, and intelligent security operations.
Cybersecurity has always been a field where speed matters a lot. That’s because attackers are fast and new vulnerabilities come up almost every day. The timeframe between a threat appearing and it causing damage is sometimes only a few minutes.
Over the years, security teams have been fighting this battle with tools and processes that weren’t built for the speed of modern threats. Now, AI models are offering a much-needed change.
AI is transforming how cybersecurity works in threat detection, incident response, and vulnerability management. It’s not by replacing the humans already doing it. Instead, AI provides capabilities that weren’t possible before, and we’ll discuss how as you continue reading.
The Major Problem AI Is Solving in Cybersecurity
Before we go into why AI is having such a significant impact on cybersecurity workflows, let’s examine the problem. In one word, it’s volume.
Modern organisations generate large amounts of data, including network logs, authentication events, application behaviour, and more. Going through all that data manually to find information is not only difficult but more or less impossible at the speed threats demand.
Traditional security tools rely on rule-based systems. In other words, they use predefined conditions that trigger alerts when specific patterns are detected. These systems work well for known threats, but they struggle with newer attack methods. As a result, they often generate many false positives and require constant manual updating to stay relevant.
AI models fix the problem by learning from data rather than following fixed rules. They identify patterns, adjust to new behaviours, and improve over time. That’s why they’re a better fit for modern cyber threats.
Detecting Threat and Analysing Behaviours
An essential application of AI in cybersecurity is to spot threats early. Rather than looking for specific known attack patterns, AI models recognise normal behaviour for users, devices, and network traffic. Then, they flag significant differences once detected. This approach stops threats that rule-based systems miss entirely.
Security teams using AI-powered behavioural analysis achieve two things. First, they report significant reductions in the volume of alerts they have to review. Second, they spend less time identifying threats, meaning more focus on real incidents.
Accessing AI Models for Cybersecurity Applications
Based on our research, a significant development in how organisations use AI for cybersecurity is the rise of flexible model platforms. Teams don’t have to build proprietary AI systems from scratch, which can be expensive and time-consuming. They can instead access powerful AI models through APIs.
One of the best platforms for that is API QIK, which connects to many leading Large Language Models (LLMs). By providing a single access point to many AI systems, it makes a rather complex job much simpler. Plus, the platform helps reduce costs because you work with the best model per task.
For teams evaluating options, a unified AI model API platform is effective. It allows security engineers to test, compare, and deploy different models for various use cases. Such flexibility in a single platform significantly reduces the time from creating a concept to deploying it.
When an incident happens, how fast cybersecurity teams respond is crucial. The longer an attacker has access to a system, the more damage they can do. In this area, AI models are reducing the duration from detection to containment in ways that manual processes just can’t match.
With an AI-assisted incident response tool, it’s possible to correlate events on multiple systems. This way, teams can reconstruct an attack timeline, identify affected assets, and recommend actions to take. All this happens within seconds of a threat being detected.
To be clear, the automated process doesn’t remove the need for human judgment. At the end of the day, experienced analysts still make calls on how to respond. However, AI handles the time-consuming groundwork, so security professionals can focus on decision-making.
Large-Scale Vulnerability Management
Identifying and patching vulnerabilities before attackers can exploit them is one of the most important tasks in cybersecurity. Not to mention, it’s resource-intensive. Most organisations deal with more vulnerabilities at a time than they have the capacity to fix, so they’re forced to prioritise.
AI models help bring intelligence to this process. They don’t just list every known vulnerability by severity score. Instead, they can assess the actual risk each vulnerability poses, based on what the organisation does. As such, it’s a kind of contextual prioritisation that helps security teams channel resources toward the vulnerabilities that matter most.
AI Models and the Security Operations Centre
The Security Operations Centre (SOC) is where much of the day-to-day work of cybersecurity happens. You have analysts monitoring alerts, investigating suspicious activity, and responding to incidents. Basically, they work to stay ahead, so it’s demanding.
With a unified AI model marketplace in the SOC workflow, teams can skip the routine, repetitive tasks. We’re talking about actions such as log analysis, alert triage, and threat classification. The organisations making the most of this are those with a clear workflow for how AI outputs feed into human decision-making.
Human Review Remains Necessary
At this point, we want to be clear about something: AI is not replacing cybersecurity professionals. The industry threats are too complex and dependent on contextual judgment for that to happen.
What AI is doing is changing what cybersecurity professionals spend their time on. The systems allow less time sorting through noise or performing manual and repetitive investigation work. That leaves more room for strategic decisions, complex threat analysis, and the kind of creative thinking that attackers themselves use.
FAQ
Can AI replace cybersecurity professionals?
No. AI enhances productivity by automating repetitive tasks, but human expertise remains essential for investigation, decision-making, and strategic planning.
What cybersecurity tasks benefit most from AI?
Threat detection, log analysis, malware analysis, incident response, vulnerability assessment, secure coding, and threat intelligence processing are among the areas seeing the greatest impact.
Why use multiple AI models in cybersecurity?
Different AI models excel at different tasks. Combining them allows organizations to leverage the strengths of each model for more accurate and efficient workflows.
Bottom Line
The current trend of AI in cybersecurity isn’t temporary. From all indications, AI is becoming fundamental to how security work is done across the industry. It applies to detection, response, vulnerability management, and threat intelligence.
Organisations that prioritise AI integration today will be better positioned to handle the threats of tomorrow. The good news is that the tools are more accessible than ever. Also, there are well-proven use cases, and the operational advantages are real. So, in conclusion, AI matters in cybersecurity, and more organisations need to build it into their workflows.
In this post, I will show you why trading cards are winning over fans again.
Trading cards are seeing another big wave of popularity across Canada, with franchises like Pokémon helping introduce both new and returning collectors to the hobby. Parents buy them as birthday gifts, adults revisit childhood favorites, and kids discover the fun of opening packs at the kitchen table.
That broad appeal makes collecting feel welcoming instead of overwhelming. Whether you once sorted cards across your bedroom floor or are simply curious about the renewed interest, there are plenty of reasons trading cards continue to win people over.
Getting back into cards
Trading cards have made a strong comeback, with collectible games like Pokémon leading much of the revival. Nostalgia plays a major role, especially for adults who grew up with the original games, TV shows, and early card releases. At the same time, the excitement of opening a pack and hoping for a great pull still feels just as strong today.
For people unsure where to begin, shopping with a retailer that clearly organizes different products can make the process much easier.
Many newcomers, returning collectors, and gift buyers buy Pokémon cards from PayMore because the retailer carries everything from booster packs and Elite Trainer Boxes to collectible tins and other sealed products. Having a well-organized selection makes it easier for beginners and experienced collectors alike to choose products that match their interests and budget.
The good news is that no expert knowledge is required to start. You can begin with a few booster packs, a themed box, or even a single card featuring a favorite character. Collecting can stay casual or become more serious over time, and that flexibility is one of the biggest reasons the hobby remains approachable.
Why the hobby feels fresh
Trading cards continue to attract people because they combine nostalgia with something current. Adults who loved Pokémon years ago still feel connected to the franchise, while children and teens continue discovering it for the first time. That mix keeps the hobby from feeling stuck in the past.
Collecting also gives people a natural sense of purpose. Some chase favorite characters, others focus on artwork, and many try to complete a set from a particular series. Even without hunting rare items, building a collection piece by piece can feel rewarding.
For families, collecting is often more social than people expect. Opening packs together, comparing favorite pulls, and helping kids sort or organize their collections can turn the hobby into real quality time. It is also one of the few screen-free activities that still feels genuinely exciting rather than forced.
What buyers want
Most shoppers are not treating every purchase like an investment. More often, they want fair prices, clear product choices, and a seller that feels dependable. If products are difficult to compare or descriptions are unclear, many people lose confidence before making a purchase.
Gift buying is another major reason trading cards remain popular. Whether shopping for a niece, nephew, friend, or your own child who suddenly has a favorite collectible game, simple navigation and straightforward choices make a major difference.
Budget flexibility matters too. Sometimes shoppers want a small surprise that fits into a stocking, party bag, or quick reward. Other times, they are looking for a larger birthday or holiday gift. Most buyers value convenience and affordability, especially when hobbies need to fit into everyday budgets.
Starting a smart collection
If you are new to collecting or returning after years away, it helps to start with a simple plan. That does not mean making the hobby complicated unless you enjoy doing so. It simply means deciding what kind of collection you want to build.
Some collectors focus on a favorite character. Others collect around a particular generation, set, or artwork style they enjoy most. Having a theme gives direction to your purchases and makes the collection feel more personal.
Setting a budget early is just as important. Opening packs is exciting, but that excitement can make overspending easy. A monthly limit helps keep the hobby enjoyable and prevents impulse buying from becoming stressful. Collecting should feel rewarding, not financially draining.
It is also worth thinking about sealed products versus single cards. Booster packs are great for people who enjoy surprise and the possibility of finding something special. Single cards are often better if you already know what you want. Many collectors find that using both approaches gives them the best balance of fun and practicality.
Cards as everyday gifts
Trading cards make especially thoughtful gifts because they are so flexible. A small pack can work as a stocking stuffer, a reward, or a simple surprise, while a larger box or collection suits birthdays, holidays, and other celebrations. They appeal to collectors of many different ages.
Another advantage is how easy they are to personalize. If the recipient already has a favorite franchise or character, you can choose products that match those interests. If they are brand new to collecting, a beginner-friendly option often makes more sense than something highly specialized.
Adults should not be overlooked either. Many people who collected cards as kids genuinely appreciate receiving them as a nostalgic gift. It feels thoughtful and fun without being excessive. Often, a gift that sparks excitement and conversation is more memorable than something generic.
Keeping cards in shape
Protecting trading cards does not require expensive gear. A simple first step is using sleeves for the cards you care about most. Sleeves help prevent scratches, bent corners, and wear from regular handling.
A binder is also useful, especially if you want to organize your collection while keeping it easy to view. Binders can make a collection feel more complete and help collectors track favorite cards or missing pieces from a set.
Everyday handling habits matter as well. Cards are best handled with clean, dry hands. That may sound basic, but it makes a noticeable difference, especially when younger collectors are involved and snacks are nearby.
Storage matters just as much as handling. Cards should be kept in a cool, dry place away from direct sunlight. Leaving them in a hot car, a damp basement, or any space with changing temperatures can lead to warping and other damage. Even casual collectors benefit from these simple precautions because basic care helps collections stay in good condition over time.
Whether you collect for nostalgia, the thrill of opening a new pack, or simply to share the hobby with family and friends, trading cards offer something for almost everyone. You do not need a rare collection or years of experience to enjoy them. Starting small, collecting what interests you, and taking care of your cards can make the hobby rewarding for years to come.
In this post, I will show you how Swiss Buyers can snag deals from overseas sellers.
Swiss shoppers love quality products at reasonable prices. With ecommerce, international merchants often beat local Swiss retailers on costs. With this opportunity, potential Swiss shoppers sometimes hesitate to purchase due to concerns related to delivery and customs.
Knowing the right methods to purchase products through these channels will help you achieve great savings. Knowing ebay Switzerland shipping is very important for international ecommerce.
It will open many doors to the availability of great products at reasonable costs from the US, EU, Asia, etc.
ebay switzerland shipping has improved and many sellers offer tracked international delivery directly to Switzerland.
The next sections will take you through steps you can use to find great products and avoid the most common problems.
Why Overseas Deals Are Worth It for Swiss Buyers
Compared to Swiss shops, overseas sellers often price their products 30 to 60% lower. Meaning, electronics, clothing, vintage stuff, tools, and much more can all be found on international markets. Add in the CHF’s value against other currencies, and purchases overseas become more tempting.
Your knowledge of logistics overseas will set you up for more success.
As a non-EU country, Switzerland imposes customs and VAT (MWST) on overseas purchases beyond a certain value. Being informed helps you estimate the total cost to you and avoid negative experiences when receiving your purchases.
Top Platforms for Finding Overseas Deals
eBay is still one of the better options out there. Look for sellers with good international shipping ratings. Filter Worldwide and Europe results and check where sellers are located.
Many US or UK sellers have good shipping results to Switzerland. However, you should always check eBay Switzerland shipping in the listing.
You could also try Etsy for one of a kind or homemade goods, Amazon international sellers, and specialty electronics or accessory stores like AliExpress. Be sure to check shipping calculators and total prices across all platforms.
Smart Strategies to Maximize Savings
Include Total Costs: Always account the item cost + the cost of shipping + possible customs charges. Use a Swiss Post customs calculator or Zollrechner like the others, to calculate your duties. Many foreign based suppliers have free or reduced shipping for bulk purchases.
Choose Safe Shipping Methods: Choose shipping methods where tracking is possible, and use a delivery method that requires a confirmed signature. In comparison to standard shipping methods, DHL, Fedex, and UPS are often better shipping solutions to Switzerland, but are more expensive and reliable.
Costs and Convenience: Buy during large sales events like Black Friday, Cyber Monday and other events. Deep discounts on bulk purchases from foreign suppliers can help offset the shipping cost.
Risk vs Reward: Use a site that has strong buyer protection to help reduce your risk. eBay has a Money Back Guarantee and PayPal protection to help ease the concerns associated with poor delivery or product quality.
Handling Customs and Taxes Like a Pro
Switzerland has a VAT (currently 8.1%) levied on Imports. Goods less than CHF 5 typically are duty free. Goods greater than CHF 5 could be levied with additional tariffs. Do not abuse a seller request to mark a package “Gift” as this can cause issues.
Package forwarding is an option if direct shipping to Switzerland is unavailable. Shipito and MyUS are options that consolidate purchases and take care of customs on your behalf.
Conclusion
With the right preparation and planning, Swiss customers can enjoy great deals from sellers around the world. Utilizing reputable sites, learning how ebay Switzerland shipping works, figuring total costs and staying up to date on customs can save you a lot of money and help you avoid the stress.
Make your first purchase low-value. Gradually make more purchases as you trust the process more and get comfortable. With good research and a good process, you will find overseas purchases are cheaper and better than what you can buy locally.
Ultimately you, the buyer, are the one who gets to decide what a great deal is. You can find low overseas deals, but what you actually get to decide is the next overseas purchase to make.
This post showcases the 25 best hacking movies for cybersecurity enthusiasts.
Cybersecurity is an exciting and ever-evolving field, and it’s no surprise that it has inspired many great films.
These hacking movies offer entertainment and provide insight into the real-world threats posed by hackers and the challenges faced by cybersecurity professionals.
Cybersecurity is an exciting and attractive subject in the cinema. It’s also a way to learn about new concepts you didn’t know existed in the computer world. We recommend some films that deal with this topic.
📝Editor’s Note: We highly recommend using the best VPN service to protect your browsing activities from hackers and snoopers.
BEST MARCH VPN DEALS FOR NETFLIX AND OTHER STREAMING SITES
Surfshark
Surfshark is an award-winning VPN service for keeping your digital life secure. Surfshark VPN has servers located in...Show More
Surfshark is an award-winning VPN service for keeping your digital life secure. Surfshark VPN has servers located in more than 60 countries worldwide. Show Less
CyberGhost VPN
CyberGhost VPN is a VPN service provider with more than 9,000 VPN servers spread in over 90 countries. Complete privacy...Show More
CyberGhost VPN is a VPN service provider with more than 9,000 VPN servers spread in over 90 countries. Complete privacy protection for up to 7 devices! Show Less
ExpressVPN
A dependable VPN service that works on all devices and platforms.
A dependable VPN service that works on all devices and platforms. Show Less
ProtonVPN
A swiss VPN service that goes the extra mile to balance speed with privacy protection.
A swiss VPN service that goes the extra mile to balance speed with privacy protection. Show Less
Private Internet Access
Private Internet Access uses world-class next-gen servers for a secure and reliable VPN connection, any day, anywhere.
Private Internet Access uses world-class next-gen servers for a secure and reliable VPN connection, any day, anywhere. Show Less
One of the best hacking movies for cybersecurity of all time is WarGames. It is one of the first films to address cybersecurity. David (Matthew Broderick) is a computer scientist who unintentionally connects his computer to the U.S. Department of Defense.
In this central server, reality becomes confused with the game, and David will have to rely on the help of his girlfriend and a computer friend to try to prevent a possible Third World War.
Sandra Bullock plays Angela in La Red, a computer expert in finding viruses and system irregularities.
Angela discovers a program that enables users to access secret databases. Her life changed from then on, getting involved in a conspiracy, and corruption was endangering her life and family.
Another best hacking movie for cybersecurity that should make our is list is Matrix (1 – 3). This science-fiction hacking movie stars a computer programmer (Keanu Reeves) who lives a double life: at night, he becomes a hacker using the alias Neo.
When acting as Neo, he comes into contact with Trinity (Carrie-Anne Moss), who puts him in touch with Morpheus (Laurence Fishburne) and with the actual reality of the Matrix: a social simulation of the world that represents the end of the 20th century.
Machines enslave humans; they are in suspension, and they have their minds connected to this simulation. Neo will join Trinity, Morpheo, and their group of rebels to fight the machines and free the enslaved humans.
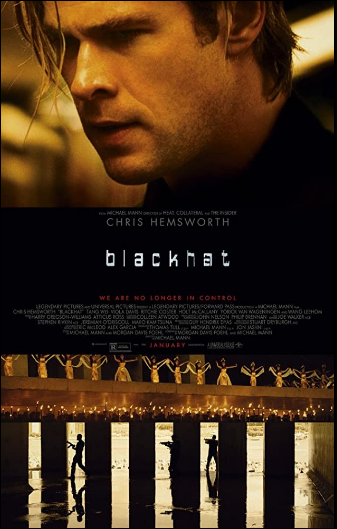
Maintaining the number 4 on our list of the best hacking movies is Blackhat. In this cybersecurity movie, the Chinese and U.S. governments are forced to cooperate to stop a network of high-level cybercrime.
To do so, they will need the help of a hacker (Chris Hemsworth)- a prisoner, who will help them protect the national security of both powers in exchange for reducing his prison sentence.
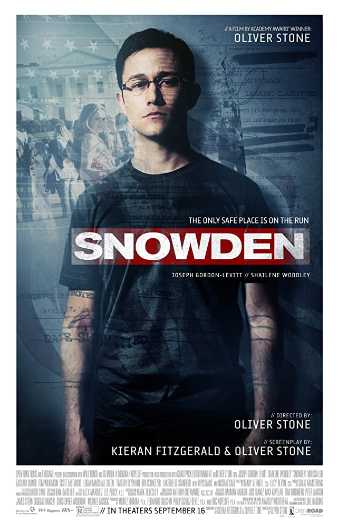
Oliver Stone directs Joseph Gordon-Levitt in this film that tells part of Edward Snowden’s life. Snowden is an adaptation of Luke Harding’s book “The Snowden Files: The Inside Story of the World’s Most Wanted Man.”
This hacking movie plot took us to Hong Kong in 2013, when Edward Snowden joined journalists Glenn Greenwald, Ewen MacAskill, and documentary filmmaker Laura Poitras to publish in The Guardian classified and confidential documents that Snowden had acquired while working for the NSA (National Security Agency).
They also tell us about subsequent events and the impact the publication of these documents had on public opinion and Snowden’s life.
In turn, they tell us, through flashbacks to the past, previous events: when Snowden enlisted in the army, when he met his partner Lindsay Mills, and about his beginnings in the CIA and NSA.
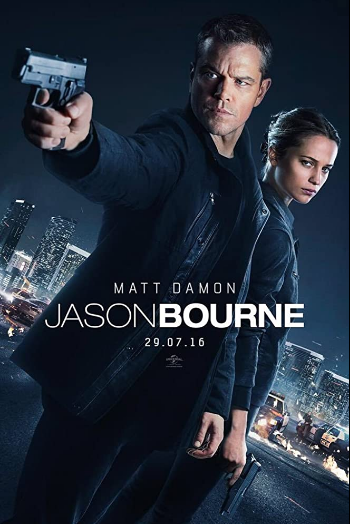
There are a total of five films about the fictional character, former CIA agent Jason Bourne (Matt Damon). All are based on the novels written by Robert Ludlum and continued by Eric Van Lustbader with a series of sequels starring Bourne.
The protagonist, who mysteriously disappeared after revealing secret details of the CIA’s murder programs, struggles to recover his identity, becoming involved in networks of manipulation and murder. This latest installment, which premiered in 2016, deals with various topics related to cybersecurity.
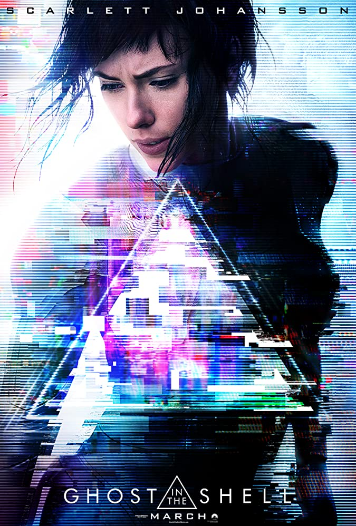
Ghost in the Shell is a popular science fiction manga created by Masamune Shirow that has been adapted for television, video games, and cinema, but always in animation format.
On March 31, the adaptation of Ghost in the Shell, featuring live-action actors and actresses, arrives in Spanish cinemas.
Scarlett Johansson has been in charge of bringing to life the futuristic cyborg secret police (cybernetic organism), Major Motoko Kusanagi, who fights against technological crimes.
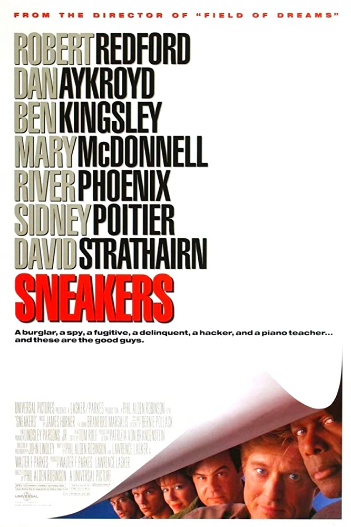
One of the best hacking movies for cybersecurity on our list is Sneakers, released in 1992. Robert Redford stars in Sneakers as Martin Bishop, a computer genius.
Martin leads a team of IT experts responsible for the security systems of large companies. All of them are involved in a situation that forces them to work for a secret agency, for which they must steal a black box capable of deciphering codes.
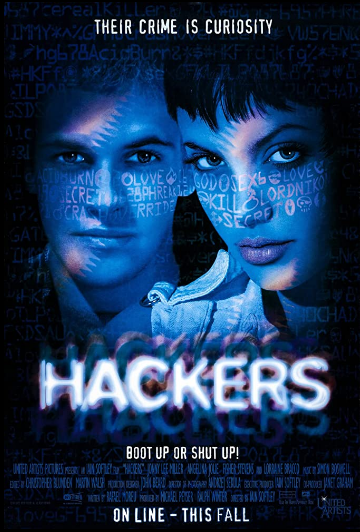
From the name, you should understand the concept behind this best hacking movie. In Hackers, Dade Murphy (Jonny Lee Miller) is a hacker who is not allowed to use any computer until he turns 18. This conviction stems from the fact that, in 1988, he caused the collapse of a large number of Wall Street servers.
When he comes of age, he moves to New York and meets another group of hackers, among them Kate (Angelina Jolie). It’s by hacking into the wrong person that they get into trouble.
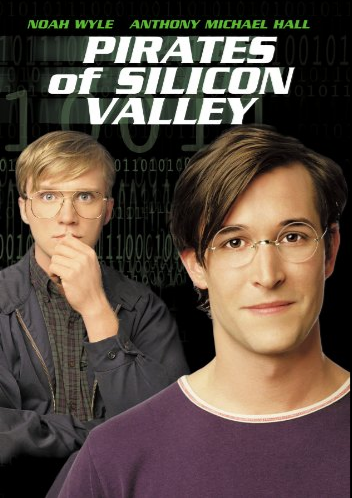
The origin of Microsoft and Apple is the central plot of Pirates of Silicon Valley. Based on the book by Paul Freiberger and Michael Swaine, Fire in the Valley: The Making of the Personal Computer.
It explains the rivalry that existed between Steve Jobs and Bill Gates in the development of the personal computer. Several films about Steve Jobs have been directed, including Jobs (2013) with Ashton Kutcher and Steve Jobs (2015) with Michael Fassbender, both directed by Danny Boyle.
We have highlighted this in our list because it deals with Jobs’ relationship with one of the first hackers in history, John Thomas Draper, also known as Captain Crunch.
Thomas was an outstanding figure in telephone hacking and the creator of Bluebox, a device made with whistles that allowed users to make phone calls without incurring charges. Both Jobs and his colleague, Stephen Wozniak, co-founder of Apple, dedicated themselves to selling this invention for a while before founding Apple.
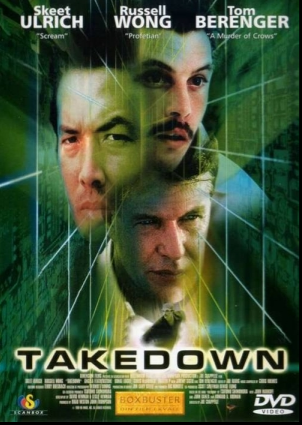
Also known as Hackers 2 and Track Down in the US. This take-down, best hacking movie is a film based on real events. The story is based on the book of the same name (Takedown) written by journalist John Markoff and by Tsutomu Shimomura, a computer security expert, who recounts his personal experiences in the book.
Takedown deals with how Tsutomu Shimomura helped the FBI capture Kevin Mitnick, a famous hacker who, even while on probation, tried to hack Shimomura’s computer security system. In short, an epic pursuit in cyberspace.
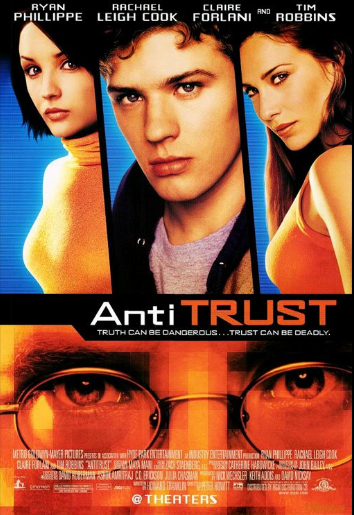
Also known as Hackers 3, Antitrust criticizes monopolistic practices in the 1990s. Milo Hoffman (Ryan Phillippe), a computer genius, is invited to work for one of the world’s largest technology companies.
After the death of his best friend, Milo begins to wonder if his new job has anything to do with it. The fictitious company Milo started working for was linked to Microsoft and its fictitious owner, Gary Winston, who was associated with Bill Gates.
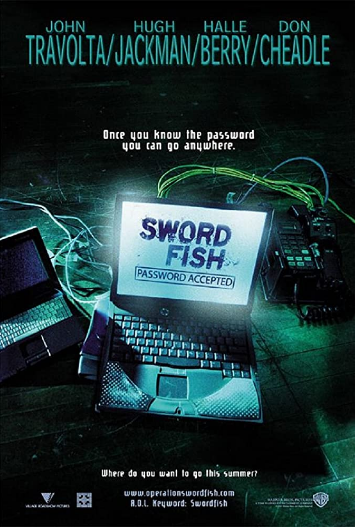
Hugh Jackman, John Travolta, Halle Berry, and Don Cheadle starred in the movie Swordfish. Jackman is Stanley Jobson, a computer expert who has recently been released from prison.
Gabriel Shear (John Travolta), who leads an anti-terrorist group called Black Cell, offers him a large sum of money to decode a complex security code from a secret account, enabling him to steal a multimillion-dollar fortune in illegal government funds.
On the other hand is Ginger Knowles (Halle Berry), who works for Gabriel and FBI agent J.T. Roberts (Don Cheadle), who is in charge of watching Stanley after his release from prison and who is interested in reaching Gabriel.
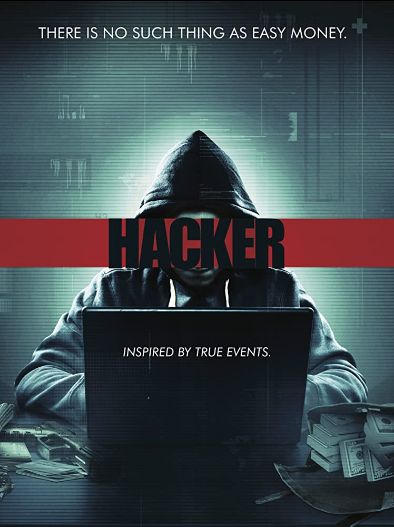
Our list of best hacking movies for cybersecurity enthusiasts won’t be complete without this movie. Hacker is an action movie and one of the most current in this list on topics related to cybersecurity.
Alex (Callan McAuliffe) is a Ukrainian immigrant who financially supports his family with illegal jobs on the Internet. Alex undergoes a drastic change when his family gets into financial trouble.
With the help of Kira (Lorraine Nicholson), a young hacker, they create chaos in the financial market and capture the attention of Z, a mysterious masked figure, and the leader of an organization known as Anonymous, who is persecuted by the FBI.
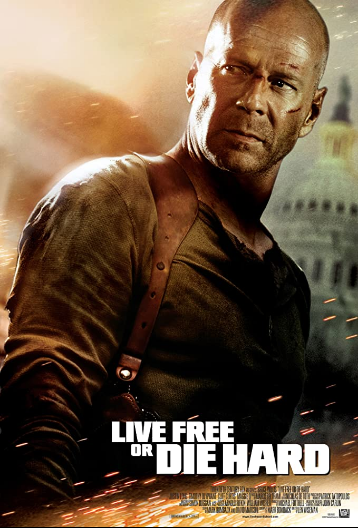
This popular hacking action movie with Bruce Willis also includes many entertaining dialogues on cybersecurity, as well as some abuses against the most popular “hacker themes.”
Although some of the tricks employed in the film, such as remote access to Closed Circuit Television (CCTV) or traffic light control, are technically possible, it’s rather complicated to put them into practice, especially in the times and order shown in the film.
Moreover, it is rather challenging to remotely blow up something using the Internet. Although there are real cases of factories being compromised by malware, this is not the most practical approach to preventing factory explosions, especially when the operation must be carried out within a specific time frame.
However, critical infrastructures require special protection from hackers. We would like to thank Bruce Willis for bringing this issue to public attention.
Unlike other best hacking movies for cybersecurity on our list, Skyfall is a memorable one. We remember the Internet-controlled explosion and a whole series of brilliant ideas that are entirely feasible (theft of top-secret information is something that already happens on the Internet). Other thriving scenes include sabotaging the curious headquarters, built on a deserted island.
However, in reality, there is no convenience in making a data center on a remote island in Asia, as it is easily tracked down, and it is challenging to bring the broadband connection here on the island.
Real-world hackers often establish their headquarters in major cities, particularly in Asia, where they can leverage powerful connections and access all the necessary resources. Physical isolation does not help. The best protection is encryption.
The authors of WarGames also created this movie. The story revolves around a device that can decipher any password and break all cryptographic systems. Of course, the secret services of many countries are seeking such a device (the NSA has played a vital role in history).
In reality, such a device is impossible to build (otherwise, the NSA would not have worked with such passion for crypto-mail providers). But the social engineering tricks work perfectly – both in 1992 and 2013.
The Matrix trilogy has given popularity to the philosophy of “simulated reality.” But geeks like the film above all for its aesthetics. Indeed, the Wachowski brothers’ masterpiece stages numerous sabotage and hacker actions, but they are presented almost like magic, Harry Potter-like spells.
In general, the problem of “sandbox escape,” which the heroes of the Matrix must solve, really exists, and modern malware often exploits it in the form of exploits, as in the case of Adobe Reader. However, the film’s creators didn’t think about it. Thanks for showing us again how to use NMAP.
Many people prefer the film adaptation of the novel by Stieg Larsson, also known by the same name. This is certainly true for the scenes of computer piracy, where the protagonist of the film uses an old NMPA to scan the computers of people of interest. This part of the story is plausible because hacking has become one of the most effective ways to uncover a person’s secrets.
Such a system is often more accessible, less expensive, and safer than establishing a covert surveillance system or breaking into the victim’s apartment. But there is an even more effective way: stealing his smartphone. It will undoubtedly be full of secrets and private information that you can use to your benefit.
Here is another entry among our list of the best hacking movies for cybersecurity.
In March 2018, it was discovered that data of millions of people was shared on Facebook. It was the Cambridge Analytica scandal.
The Great Hacker is a documentary hack movie based on that true story. It premiered on July 24, 2019, on Netflix and examines the darker side of social networks, exploring how they utilized the personal data of 87 million people to influence the 2016 U.S. presidential election.
Harry Paul, a detective renowned for his expertise in surveillance and security systems, is commissioned by a tycoon to investigate his young wife. She must listen to his conversations with an employee of this man, with whom she seems to be in love.
The mission, for an expert of his category, is, at first sight, challenging, as the couple offers no interest outside the ordinary. However, when Harry finishes his work, he notices something strange behind the banality he has been investigating, as his client refuses to identify himself and always uses intermediaries.
Despite being an old movie, The Italian Job is one of the best hacking movies of our time. After leaving prison, a criminal devises a plan to steal a massive shipment of gold and successfully escapes. How? By creating an enormous traffic jam in Turin.
Thanks to the manipulation of the city’s computer traffic control system and three small Minis with which to escape with the loot. Cars and vulnerabilities in a connected downtown.
One of the best hacking movies you should consider is The IT Crowd. Of British origin, it has turned out to be one of the most popular cybersecurity TV series of the last decade.
It follows the daily life of two young geniuses who work for the technology department of a company, and their supervisor, in charge, learns from all their talent. You’ll have a lot of fun just watching the first chapter.
Come on. You got it. If you are a fan of the world of computer science and hacking, here are some of the best options in movies and series. You’ll know what to do during the weekend, so you won’t get bored. Enjoy!
Elliot Alderson is a gifted computer man who works during the day as a digital national security agent. While at night, he develops into a computer hacker with an enormous reputation.
His incredible computer skills and depressive condition make him debate between being one of the “good” or “bad.” Anyway, it is one of the best series of hackers, and it is also available on Netflix. Would you like to see it?
The Social Network movie is one of the best hacking movies for cybersecurity enthusiasts on our list. How much do you know about the creation of Facebook?
In The Social Network, the university life of its creator is portrayed. Mark Zuckerberg’s life is told stage by stage. This includes how, in one night, he created Facebook, which is now the most popular social network.
However, that’s not the most impressive aspect of this hacking movie. But all the drama around his project partners and those who tried to usurp his great idea. Look it up now, and you’ll know why it’s one of the best computer movies available.
Surfshark is an award-winning VPN service for keeping your digital life secure. Surfshark VPN has servers located in...Show More
Surfshark is an award-winning VPN service for keeping your digital life secure. Surfshark VPN has servers located in more than 60 countries worldwide. Show Less
CyberGhost VPN
CyberGhost VPN is a VPN service provider with more than 9,000 VPN servers spread in over 90 countries. Complete privacy...Show More
CyberGhost VPN is a VPN service provider with more than 9,000 VPN servers spread in over 90 countries. Complete privacy protection for up to 7 devices! Show Less
ExpressVPN
A dependable VPN service that works on all devices and platforms.
A dependable VPN service that works on all devices and platforms. Show Less
ProtonVPN
A swiss VPN service that goes the extra mile to balance speed with privacy protection.
A swiss VPN service that goes the extra mile to balance speed with privacy protection. Show Less
Private Internet Access
Private Internet Access uses world-class next-gen servers for a secure and reliable VPN connection, any day, anywhere.
Private Internet Access uses world-class next-gen servers for a secure and reliable VPN connection, any day, anywhere. Show Less
Best Hacking Movies For Cybersecurity Enthusiasts: Frequently Asked Questions
Is hacking in movies accurate?
No, hacking in movies is not usually accurate. Hollywood often portrays hacking as a fast-paced, exciting activity that involves flashy graphics and rapid typing. However, in reality, hacking is a much more methodical and time-consuming process. It often involves social engineering, research, and patience.
Here are some of the ways that Hollywood hacking differs from real-life hacking, according to programming experts from https://assignmentcore.com:
Timeline: In movies, hacks often happen in a matter of minutes or hours. In reality, hacks can take weeks, months, or even years to complete.
Technology: Hollywood often uses outdated or fictional technology to make hacking seem more dramatic. In reality, hackers use real-world tools and techniques.
Skills: Hollywood often portrays hackers as lone geniuses who can hack into anything. In reality, hacking is often a collaborative effort that requires a diverse range of skills.
Motivation: In movies, hackers are often motivated by revenge or greed. In reality, hackers can have a variety of motivations, including political activism, curiosity, and financial gain.
Here are some of the most common inaccuracies in movie hacking:
Green screens and fake graphics: Real hacking happens on a black screen with lines of code. The flashy graphics and animations often seen in movies are not realistic.
Split-screen windows: In movies, hackers often have multiple windows open on their screens simultaneously. In reality, hackers usually focus on one window at a time.
Rapid typing: In movies, hackers often type very quickly. In reality, typing speed is not a crucial factor for hacking.
Virus spreading: In movies, viruses often spread quickly and easily. In reality, viruses are not as easy to spread as they are often portrayed.
Zero-day exploits: In movies, hackers frequently employ zero-day exploits to gain unauthorized access to systems. Zero-day exploits are vulnerabilities that are unknown to the software vendor. In reality, zero-day exploits are rare and very valuable.
Despite the inaccuracies, there are a few movies that do a good job of portraying hacking in a more realistic way.
Some examples of realistic hacking movies include:
Mr. Robot: This TV series follows a young hacker who works as a cybersecurity engineer by day and a vigilante hacker by night. The show is praised for its realistic portrayal of hacking and the psychological impact it can have on individuals.
WarGames: This 1983 film follows a young hacker who accidentally gains access to a military supercomputer and inadvertently triggers a nuclear war scenario. The film is considered a classic and is still relevant today.
The Social Network: This 2010 film follows the creation of Facebook and the legal battle between its founders. The film is praised for its accurate portrayal of the early days of social media and the challenges of online privacy.
While hacking in movies is not usually accurate, it can still be entertaining. If you are interested in learning more about real-world hacking, numerous resources are available online and in libraries.
What do hackers say in movies?
Movie hackers are notorious for their dramatic pronouncements and witty one-liners. Here are some of the most common things hackers say in movies:
1. “We’re in.” This is the classic hacker line that nearly all movie hackers say. It’s a simple phrase that signifies that the hacker has successfully gained access to a system.
2. “I’m in.” Similar to “we’re in,” this variation is a movie hacker’s way of announcing to the world—or just to the empty room around them—that things are about to go off.
3. “I don’t play well with others.” Hackers are often portrayed as loners who are distrustful of others. This line is a way for the hacker to establish themselves as an independent operator.
4. “I couldn’t think as slow as you if I tried.” This line is a classic example of a hacker’s arrogance. It’s a way for the hacker to show that they are intellectually superior to the average person.
5. “I invented it.” Hackers are often portrayed as creative geniuses who devise innovative solutions to problems. This line allows the hacker to take credit for their work.
6. “Now the hunted becomes the hunter.” This line is often used by villains who are about to turn the tables on their pursuers. It’s a way for the villain to show that they are not afraid of the challenge ahead.
7. “I’m just getting started.” This line is often used by hackers who are about to unleash some serious havoc. It’s a way for the hacker to show that the worst is yet to come.
8. “I’m in your system.” This line is a classic way for a hacker to intimidate their victim. It’s a way for the hacker to show that they are in control and that the victim is at their mercy.
9. “I’m one step ahead of you.” This line is often used by hackers as a taunt to their pursuers. It’s a way for the hacker to show that they are always in control and that the victim will never catch up.
10. “Game over.” This line is often used by villains who have defeated their opponents. It’s a way for the villain to show that they have won and that there is no hope for the victim.
Of course, these are just a few of the many things that hackers say in movies. The specific lines that a hacker will use will depend on the character’s personality and the situation.
It’s essential to note that these portrayals in movies are fictional representations of hackers and may not be entirely realistic. Real-life hacking is often much more complex and requires a variety of skills and techniques. However, the lines above can still be entertaining and provide some insight into how hackers are portrayed in popular culture.
What movie is based on a true story hacker?
There are several movies based on true stories of hackers, each offering a unique perspective on the world of cybersecurity and the fascinating individuals who inhabit it. Here are a few of the most notable:
Takedown (2000): This film tells the story of Kevin Mitnick, a notorious hacker who spent years evading authorities before being captured in 1995. The movie portrays Mitnick as a brilliant yet troubled individual driven by a deep-seated need to challenge the establishment.
The Social Network (2010): This movie chronicles the creation of Facebook and the legal battle between its founders, Mark Zuckerberg, Eduardo Saverin, and the Winklevoss twins. While not strictly a hacking movie, it does delve into the world of computer programming and the ethical implications of online privacy.
Mr. Robot (2015-2019): This television series follows Elliot Alderson, a young hacker who works as a cybersecurity engineer by day and a vigilante hacker by night. The show is praised for its realistic portrayal of hacking and the psychological impact it can have on individuals.
WarGames (1983): This classic film follows a young hacker who accidentally gains access to a military supercomputer and inadvertently triggers a nuclear war scenario. While the technology depicted is outdated, the film raises important questions about the dangers of cyberwarfare.
Blackhat (2015): This film stars Chris Hemsworth as a convicted hacker who is released from prison to help track down a cybercriminal who is causing global chaos. While the film received mixed reviews, it does offer an interesting glimpse into the world of international cybercrime.
The Fifth Estate (2013): This film tells the story of WikiLeaks and its founder, Julian Assange. While not strictly a hacking movie, it does explore the ethical implications of information leaks and the role of whistleblowers in the digital age.
Sneakers (1992): This action-comedy follows a team of hackers who are hired to test security systems for a living. While the film is lighthearted and humorous, it does offer a glimpse into the early days of cybersecurity.
Hackers (1995): This cult classic follows a group of teenage hackers who become involved in a conspiracy to steal money from a large corporation. While the film is not particularly realistic, it does capture the spirit of early hacker culture.
The Matrix (1999): Although not specifically about hackers, this sci-fi action film delves into themes of reality, simulation, and the nature of information. It has become a cult classic and has had a significant influence on popular culture.
Snowden (2016): This biographical drama tells the story of Edward Snowden, a former NSA contractor who leaked classified documents that revealed the extent of the government’s surveillance programs. The film raises important questions about privacy, security, and the role of whistleblowers in the digital age.
These are just a few of the many movies that feature hackers. Each film offers a unique perspective on this fascinating and complex subject.
How many types of hackers are there in cyber security?
There are many ways to categorize hackers, but some of the most common types include:
1. White hat hackers
White hat hackers are also known as ethical hackers. They are security professionals who use their skills to identify and fix vulnerabilities in computer systems and networks.
They typically work for companies or organizations that want to improve their security posture. White hat hackers are often considered the “good guys” of the hacking world.
2. Black hat hackers
Black hat hackers are also known as crackers. They are criminals who exploit vulnerabilities using their skills for personal gain.
They may steal data, install malware, or launch denial-of-service attacks. Black hat hackers are often considered the “bad guys” of the hacking world.
3. Grey hat hackers
Grey hat hackers operate between the lines of white-hat and black-hat hackers. They may use their skills for both good and bad purposes.
For example, a grey hat hacker might discover a vulnerability in a system and disclose it publicly without permission from the owner. Grey hat hackers can be challenging to categorize, as their motivations vary.
4. Script kiddies
Script kiddies are people who use hacking tools and scripts created by others. They often lack the technical skills to understand how the tools work and may use them for malicious purposes without fully understanding the consequences. Script kiddies are often considered the “wannabes” of the hacking world.
5. Hacktivists
Hacktivists are individuals who utilize hacking techniques to advocate for a political or social cause. They may launch cyberattacks against government agencies, corporations, or other organizations that they believe are doing harm. Hacktivists often see themselves as digital Robin Hoods, fighting for justice and equality.
6. Green hat hackers
Green hat hackers are a newer breed of hackers who are motivated by a desire to learn and improve their skills. They often participate in bug bounty programs or “capture the flag” competitions.
Green hat hackers are considered a valuable asset to the security community, as they help to identify and fix vulnerabilities before they can be exploited by malicious actors.
7. Blue hat hackers
Blue hat hackers are individuals who hack for personal enjoyment or intellectual challenge. They may not have any malicious intent, but their activities can still be disruptive or harmful.
Blue-hat hackers are often viewed as a nuisance by security professionals, but they can also offer valuable insights into new vulnerabilities and emerging attack techniques.
8. Red hat hackers
Red hat hackers are government-sponsored hackers who are employed to conduct offensive cyber operations. They may target foreign governments, critical infrastructure, or other high-value targets.
Red hat hackers are often shrouded in secrecy, and their activities can have a significant impact on national security.
9. State-sponsored hacker
State-sponsored hackers are individuals employed by a government agency to conduct cyber operations. They may be tasked with conducting espionage, sabotage, or other forms of cyberwarfare.
State-sponsored hackers are often well-funded and have access to sophisticated tools and techniques.
10. Organized crime groups
Organized crime groups are increasingly turning to cybercrime as a means of generating revenue. They may use hacking to steal money, launder money, or launch cyberattacks against businesses or individuals.
Organized crime groups are often ruthless and well-organized, posing a serious threat to cybersecurity.
These are just a few of the many types of hackers that exist. The threat landscape is constantly evolving, and new types of hackers are emerging all the time.
It is essential for organizations to be aware of the various types of hackers and to implement measures to protect themselves from potential attacks. Also, you can check out our guide on how to become an hacker.
What Are The Best Hacker Movies Released in 2023?
Here is a list of some of the best hacker movies released in 2023:
Blackwater: This South Korean action thriller follows a skilled hacker who is framed for cybercrime and must go on the run to clear his name.
Cypher: This American science fiction thriller follows a group of hackers who discover a dangerous conspiracy.
Unlocked: This French thriller follows a woman who is targeted by a hacker who has gained access to her phone.
No Escape: This American action thriller follows a family who is targeted by a group of hackers while on vacation in a remote island.
These are just a few hacker movies 2023 of the many great hacker movies that were released in 2023. I hope you enjoy watching them!
Bottom Line
Our preferred best hacking movie is: The Social Network
The Social Network transcends the genre of hacking films. It chronicles the birth of a digital behemoth – Facebook – and the man behind it: Mark Zuckerberg.
From a Harvard dorm room to global domination, witness the transformation of a student into the youngest billionaire, a testament to both ambition and the transformative power of the internet.
Which movie did not make our list of the best hacking movies for cybersecurity? Comment below.