In this post, I will show you how to create standout Christmas photos without professional editing skills.
If your Christmas photos look “almost right” but not quite polished, you’re not alone. The good news: you don’t need a degree in photography or expensive software to make your images look significantly better. With a simple, repeatable process—plus a quick way to fix tricky green color problems—you can create standout holiday photos that look clean, natural, and sharp.
In this guide, you’ll learn practical steps you can do in minutes, including how a grinch filter can help fix holiday color noise and improve subject separation when your pictures have a strong green cast.
What “standout” Christmas photos have in common
Before editing, it helps to know what you’re aiming for. Great holiday photos usually have:
Balanced lighting (skin tones look believable, not washed out)
Less visual clutter (decorations don’t “steal attention”)
Most amateur Christmas photos fall short in one of these areas—especially when green lighting, Christmas trees, or reflective decorations create color contamination.
Step 1: Pick the right photo (you can’t edit a bad capture)
Choose photos where the subject is in focus and properly exposed. If your image is too blurry, your edits won’t look natural.
Quick checklist:
Face is sharp (or at least eyes are sharp)
Subject isn’t blocked by bright lights
You have enough detail in shadows (not fully black areas)
Step 2: Fix white balance first (this is the “foundation”)
A lot of holiday color issues come from incorrect white balance, which affects overall color temperature and tint. Professional editors usually solve color problems by correcting white balance early—because fixing local details later can’t fully undo a wrong global color cast.
Simple approach (beginner-friendly)
Look at something that should be neutral: white ornaments, white snow, or a plain wall.
Adjust the temperature/tint until those neutrals look neutral again (not green, blue, or yellow).
If your photos are lit by mixed indoor/outdoor light (common at Christmas gatherings), color casts are more likely—so it’s worth taking 30 seconds here.
Step 3: Address the “holiday green” problem
Christmas photos often get a green cast because of trees, green costumes, garlands, colored lights, or reflective surfaces. This can make skin look odd and cause unwanted color spill around edges.
That’s where a grinch filter can be a big help.
What a grinch filter does (in plain terms)
A grinch filter is designed to isolate and correct green-tinted character details, costume elements, and holiday-style green color bias, especially in scenes where green tones overlap with the background.
It can help with:
Separating green costume tones from nearby backgrounds
Refining edge transitions around difficult details (like hair/fur)
Reducing harsh green spill while keeping texture visible
If your subject is wearing green (or your background contains lots of green), this is often exactly the problem you’re seeing.
When to use it
Use a grinch filter when you notice:
Green spill around hair or fuzzy fabric
Wreaths/trees blending into clothing edges
Skin or clothing looks tinted instead of natural
Step 4: Improve edges so your subject looks “real” (not cut out)
A common beginner mistake is doing edits that make the subject look pasted on. The goal is to preserve natural transitions around:
Hair
Fur-like textures
Sweater fibers and scarves
Ornament overlap
A good workflow is:
Fix overall color first (white balance)
Then fix green spill and separation (using a grinch filter when needed)
Finally, check edges at 100% zoom
Step 5: Make colors feel festive and believable
After correcting unwanted color, add subtle improvements:
Keep skin tones natural—skin is the “trust signal” of good edits
Remember: color contamination isn’t always solvable by a single slider. Lighting conditions and reflections can cause stubborn tinting that requires targeted correction.
Step 6: Don’t overdo sharpening and noise reduction
Christmas lights create tiny highlights and contrast. If you sharpen too aggressively, you can emphasize noise and halos around lights.
Beginner rule: Sharpen only enough that eyes and key details look crisp, not crunchy.
A simple editing recipe (you can repeat every time)
Here’s a quick “no-professional-skills” workflow:
Choose best photo (sharp subject, decent exposure)
Set white balance (neutral whites look neutral)
Use a grinch filter if green spill is harming edges or skin/clothing tones
Check edges at full zoom (hair/fabric should blend naturally)
Fine-tune color (vibrance, contrast, light haze)
Export at high quality (don’t downsample too early)
Optional: Editing for specific Christmas moments
Family portraits: prioritize skin tone and clean separation from the background.
Kids in costumes: focus on avoiding green/colored-light spill around hair and fabric.
Tree + ornaments in frame: use targeted corrections so decorations don’t “infect” clothing colors.
Conclusion: Standout photos are mostly consistency
You don’t need pro-level tools to get pro-looking results. The biggest wins come from (1) getting color balance right and (2) handling tricky green contamination that can ruin edges and realism. A grinch filter is specifically built for isolating green-tinted holiday details and improving separation—making it a practical option when your Christmas photos feel “off.”
If you want a quick way to test this on your own photos, try a grinch filter directly and compare the result on one of your most frustrating images.
Read on for the Dynadot domain registration service review.
Dynadot is a domain registrar that boasts thousands of users. But it’s not the only one. Hundreds of domain registrars exist with thousands of users.
If you want to build a website, the domain registrar you choose will majorly impact your experience.
Therefore, picking the best domain registrar is essential. To select the best, you must consider factors such as price, features, and customer service.
In that view, how does Dynadot rank among the best domain registrars? Is it a reliable domain registrar to use? This Dynadot Domain registration service review will answer all the questions. Read on.
What Is Dynadot?
The name “Dynadot” may not be widely recognized in the domain registration industry, but it is not new.
Dynadot began operating as a domain registrar in 2002, more than twenty years ago. Since its launch, the company has aimed to provide state-of-the-art domain and hosting services.
Dynadot offers a fully automated domain registration service, allowing anyone to register domains without any restrictions. With this, the company has managed to maintain a client base in more than 108 countries.
Domain registration isn’t all Dynadot offers. You can also transfer your domain from a different registrar to Dynadot or leverage the website-building tool to build your website. Dynadot offers additional domain-related services, which we’ll discuss later.
Like many top domain registrars, Dynadot is a US-based company. The company has its headquarters in San Mateo, California, the same location where it was founded. Likewise, Todd Han, the founder of the company, is its current President.
Furthermore, Dynadot holds ICANN accreditation to register domain names and offer hosting services. Aside from its headquarters in the United States, Dynadot has branch offices in China and Canada. In particular, these branch offices are in Beijing, Zhengzhou, and Toronto.
Dynadot
Dynadot is a domain name registrar that provides domain registration, website hosting, and website builder services.
Dynadot is a domain name registrar that provides domain registration, website hosting, and website builder services. Show Less
Dynadot Domain Name Registration Process
Dynadot makes domain name registration relatively simple. Simple, because you can register a domain in just five steps if you have an account:
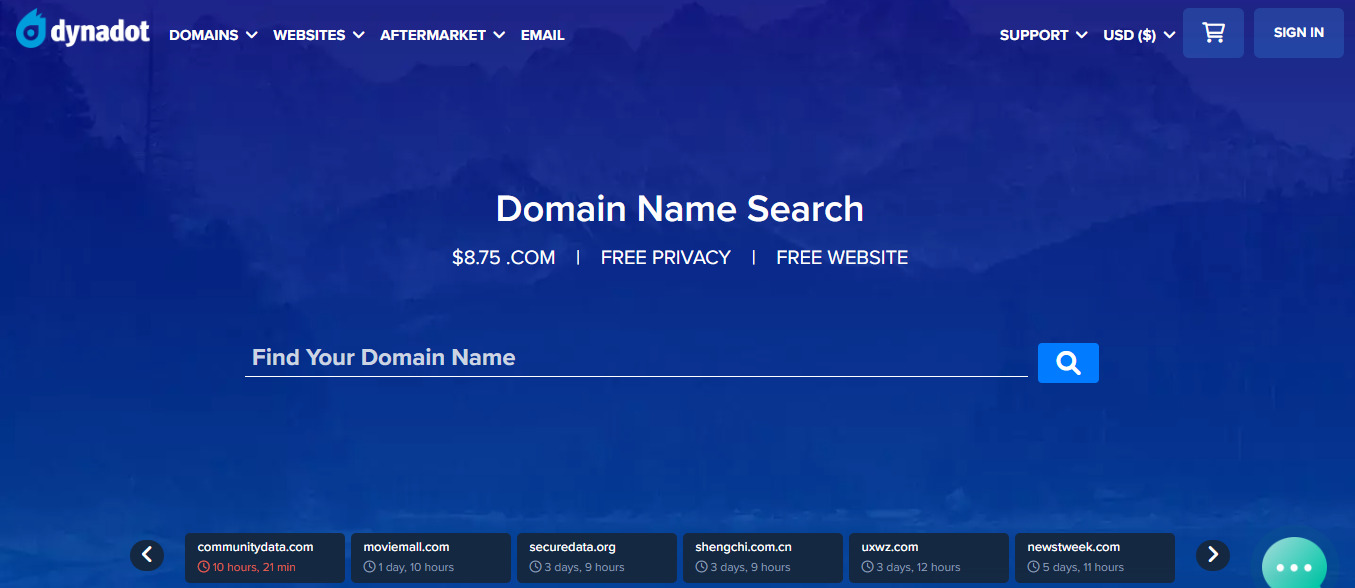
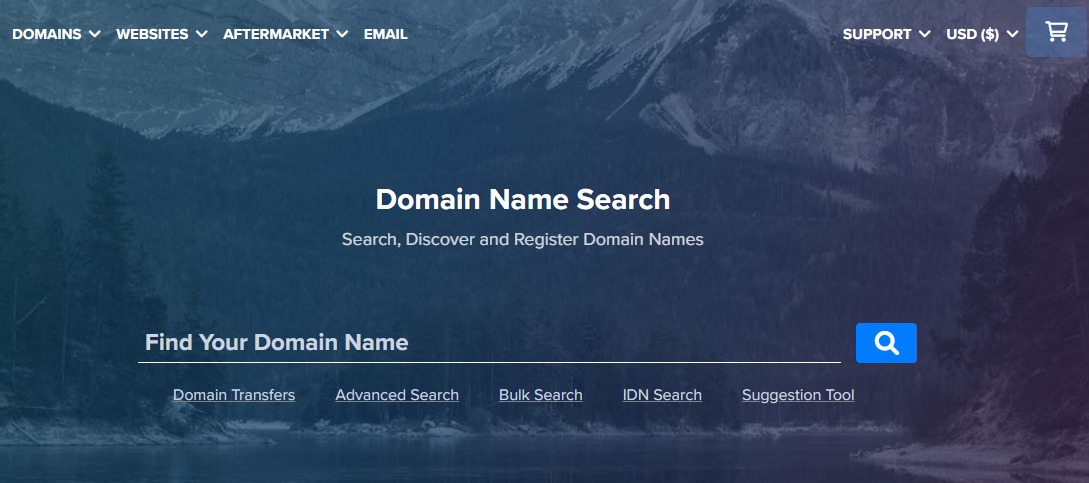
Visit the Dynadot website and enter a keyword on the homepage to find your domain name.
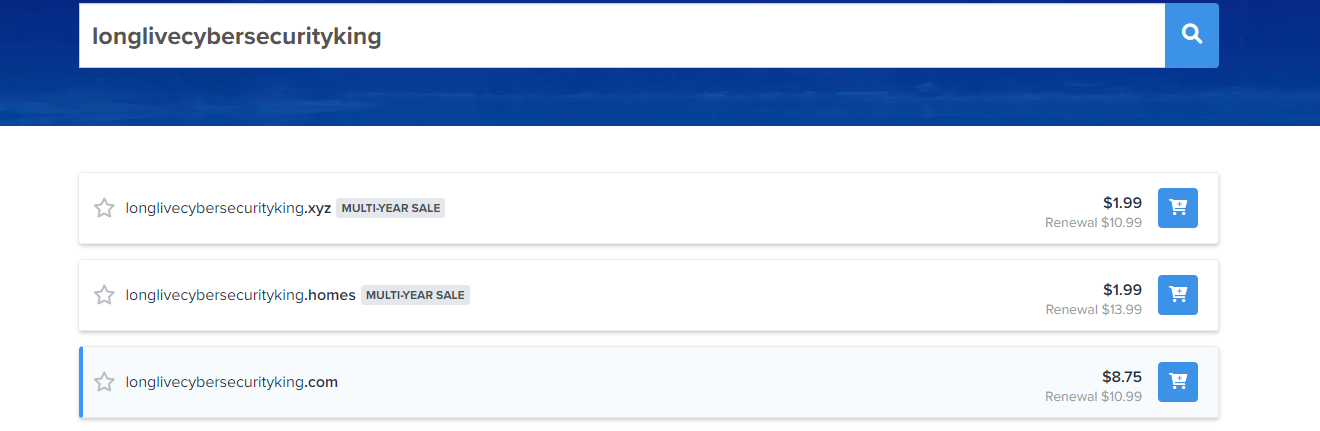
Review the available domain names obtained from your keyword. Click on the Cart icon beside any domain name you want to purchase. Please note that you can purchase multiple domain names simultaneously.
Click on the Cart button at the top-right corner of the page and click on “View Cart.”
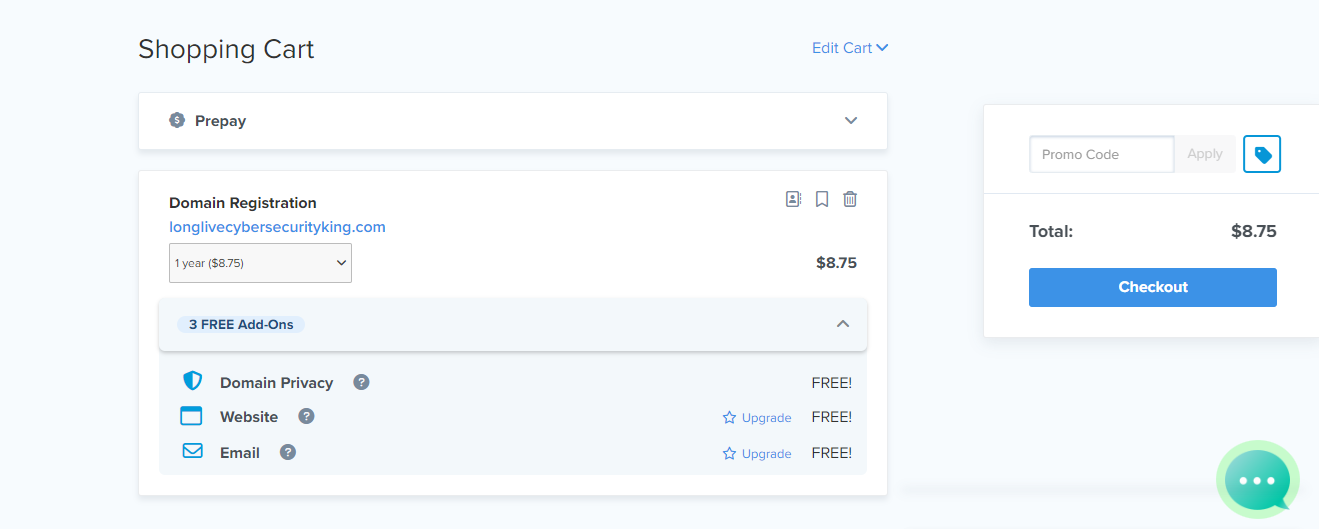
On the cart page, confirm your login details. Note, you can enter a promo code if you have one for a reduced price. Additionally, you can add other Dynadot services, such as a hosting plan or a website builder. Click on “Checkout” if everything is correct.
Pay for the domain name via a convenient payment method. Once payment is confirmed, you get an “Order Finished” message, and congratulations, you now have a registered domain.
When building a website, purchasing a domain is primary but preliminary. There are still things to do, so let’s look at other Dynadot services.
Dynadot
Dynadot is a domain name registrar that provides domain registration, website hosting, and website builder services.
Dynadot is a domain name registrar that provides domain registration, website hosting, and website builder services. Show Less
Dynadot Web Services
Below is a rundown of the different web services you get from Dynadot:
Domain Registration
Domain registration is the primary service offered by Dynadot. You can register top-level and second-level domains, and the company offers some of the lowest prices in the industry.
All you have to do is enter a keyword to find your domain name. In seconds, Dynadot will list out the available domains – by domain extension – for your keyword. If you find the right domain, you can purchase it outright. Since TLD and SLD are supported, it’s easy to find a domain extension that suits your business.
Dynadot offers web hosting via its Website Builder service. As you pay for the domain, you can add a hosting plan with just one click.
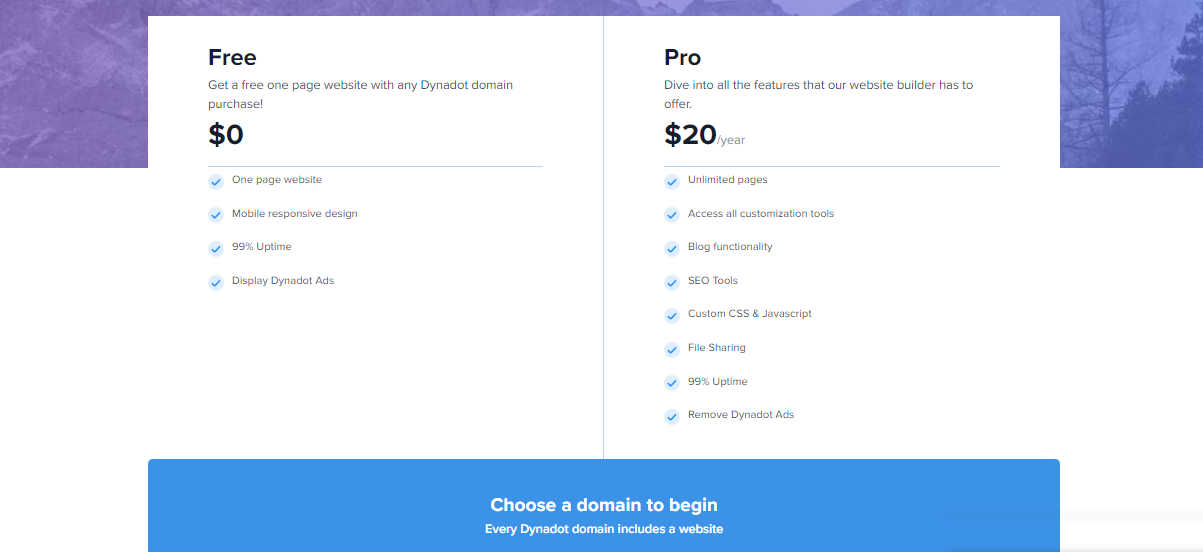
With Dynadot, you can choose from two hosting plans: Free and Pro.
The Free plan is what its name suggests: free, but it only supports one-page websites and includes ads. The Pro plan is a shared hosting plan, which does not display ads.
Website Builder
After registering your domain and paying for hosting, you can continue to build your website with Dynadot. The company has it all. You will also find the website builder easy to use.
While it’s easy to use, you can skip using the builder and opt for a template instead. Dynadot features hundreds of professionally made website templates. You only have to import and customize them.
You can use the Dynadot website builder tool for free or subscribe to the Basic, Pro, or Business plan.
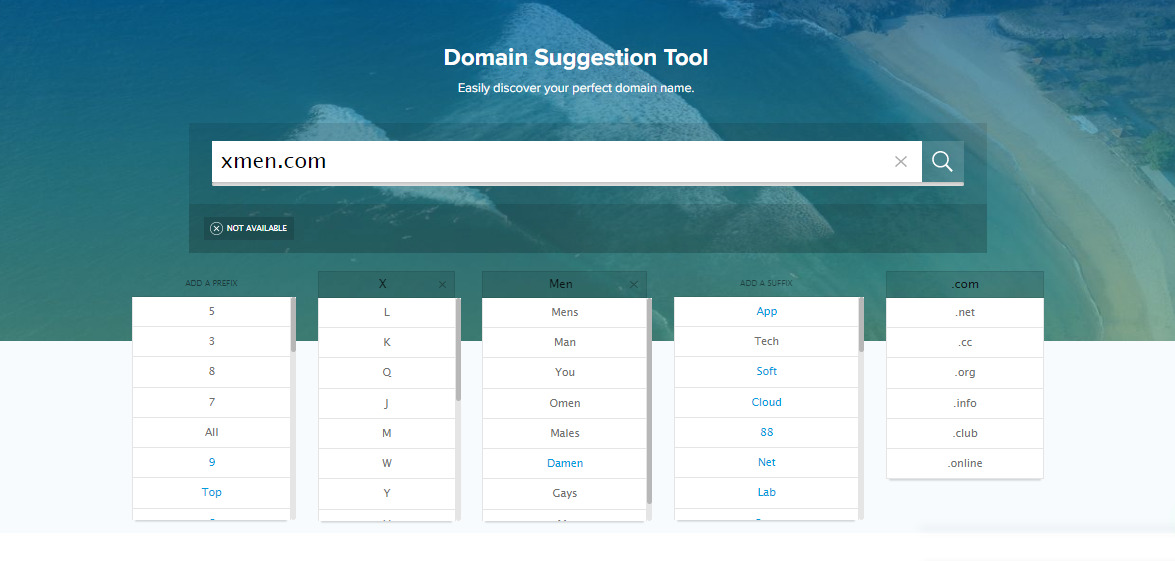
Finding the right domain name can be challenging. To facilitate matters, Dynadot comes with a domain suggestion tool. In simple words, the tool will help you pick the perfect domain name.
First, you enter your primary keyword. Second, you enter a prefix and a suffix and choose a preferred extension. As you select, the Dynadot domain suggestion tool will auto-generate domain names in real time.
Domain Security
By default, Dynadot ensures all registered domains and hosting plans are secure. But the company also offers additional security. This is a feature that business and agency websites can leverage.
In particular, Dynadot offers a unique domain security feature with Authentication I. It combines multiple security measures, including 2FA, account lock, SMS Authentication, and Google Authentication.
Please note that this additional security feature is complimentary as long as you have an active subscription. You’ll only need to set it up in your account settings.
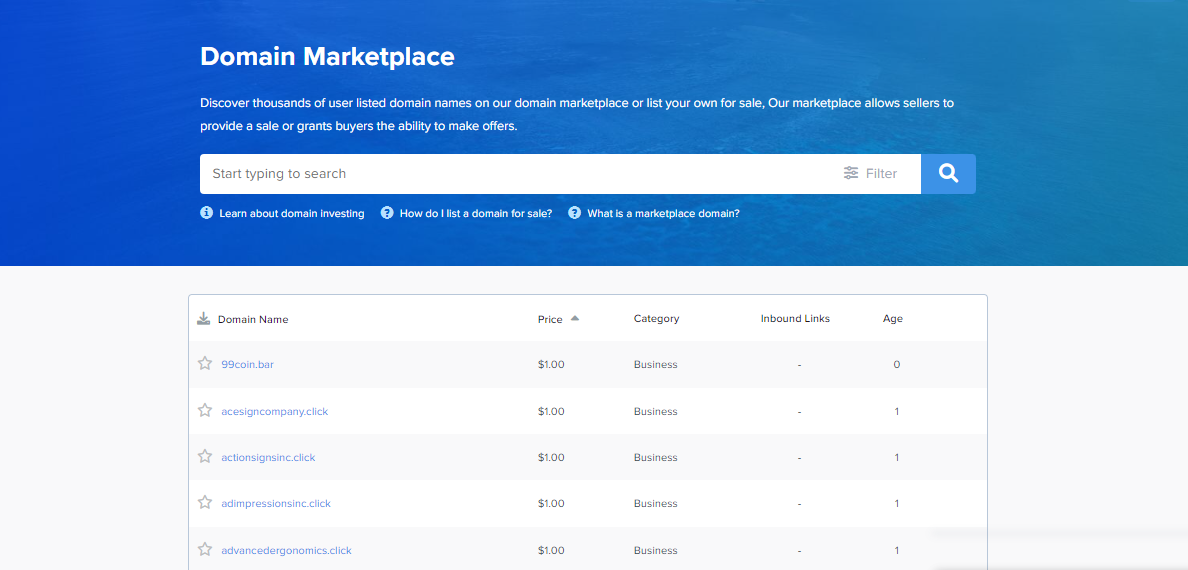
Domain Marketplace
Do you have old domains for sale? Or did you register a premium domain name you think someone else could buy? Dynadot provides a platform for you to reach hundreds and thousands of potential buyers. This platform is the Dynadot Domain Marketplace.
The Dynadot Domain Marketplace is free and straightforward to use. The only requirement is that you have a Dynadot account. You get paid without delay, and transferring the domain to the new owner won’t be a hassle.
Dynadot
Dynadot is a domain name registrar that provides domain registration, website hosting, and website builder services.
Dynadot is a domain name registrar that provides domain registration, website hosting, and website builder services. Show Less
Domain API
Another top feature you get from Dynadot is the Domain API. Basically, it’s a tool you’ll want to use if you have a large number of domains or Dynadot accounts. It lets you manage bulk domains and accounts from a single interface.
The Dynadot API will also enable the registration of new domain names, organizing domain folders, and engaging with the marketplace. Dynadot provides an in-depth request list with all actions you need to use the API. And the API is free for all active users.
SSL Certificates
What you get from Dynadot is not the regular SSL certificates. The domain registrar offers Alpha SSLs with 2048-bit certificates and a $10,000 warranty. Alpha SSLs differ in that they come with chained root certificates, providing enhanced security.
Furthermore, Alpha SSLs will also secure subdomains, and they don’t take long to validate. Aside from Alpha SSLs, Dynadot also offers Wildcard SSLs.
Whois Lookup
Suppose you have a domain name in mind and want to check if it’s available. In that case, Dynadot Whois Lookup is a tool you can use. The tool will uncover all publicly available Whois data on a domain, notably, including details of its owner.
The Dynadot Whois Lookup tool has an extra feature you don’t get with many Whois Lookup tools. It allows you to add domains to a watch list and monitor them for any changes in status.
Email
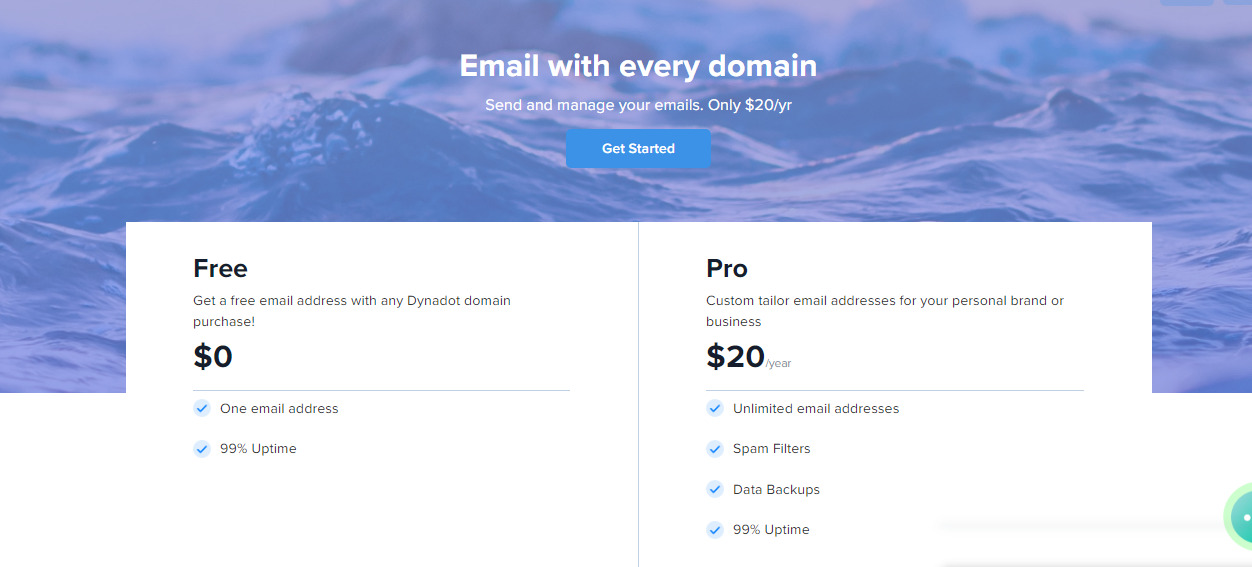
Dynadot gives you a custom email address for every domain you register. The email is free, but you can only register one address. For more features, you can upgrade to the Pro email plan for $20 per year.
With the Pro email plan, you can register unlimited emails. Additionally, the plan includes spam filtering and data backup features.
Dynadot Customer Service
Customer service is a critical factor to consider when choosing a domain registrar. Dynadot is aware of this, and that’s why the company offers multiple customer contact channels.
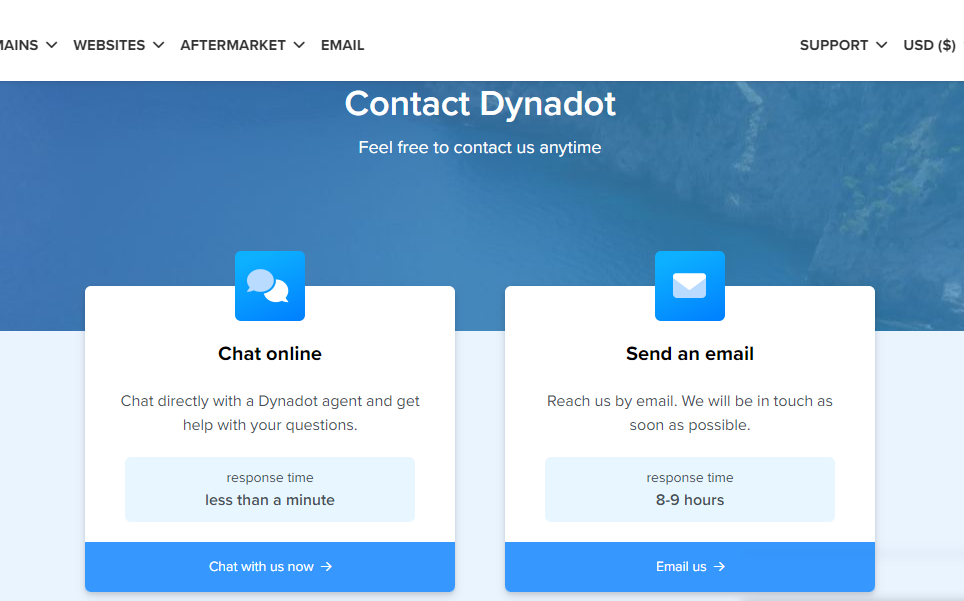
On the Dynadot website, there’s a Live Chat button, which allows you to talk to a support staff member in real time. In fact, you get a reply within a minute after sending your message.
You can also contact the support via email, but you’ll get a response within eight to nine hours. The other option you have is Fax.
Notably, if you live in the US, you can visit Dynadot’s offices in California for in-person support.
Dynadot Domain Registration Pricing
Dynadot domain registration service cannot serve you if you cannot pay for it. The good news is that the domain registration service is affordable compared to other popular services.
Here are the prices for Dynadot domain registrations for different domain extensions:
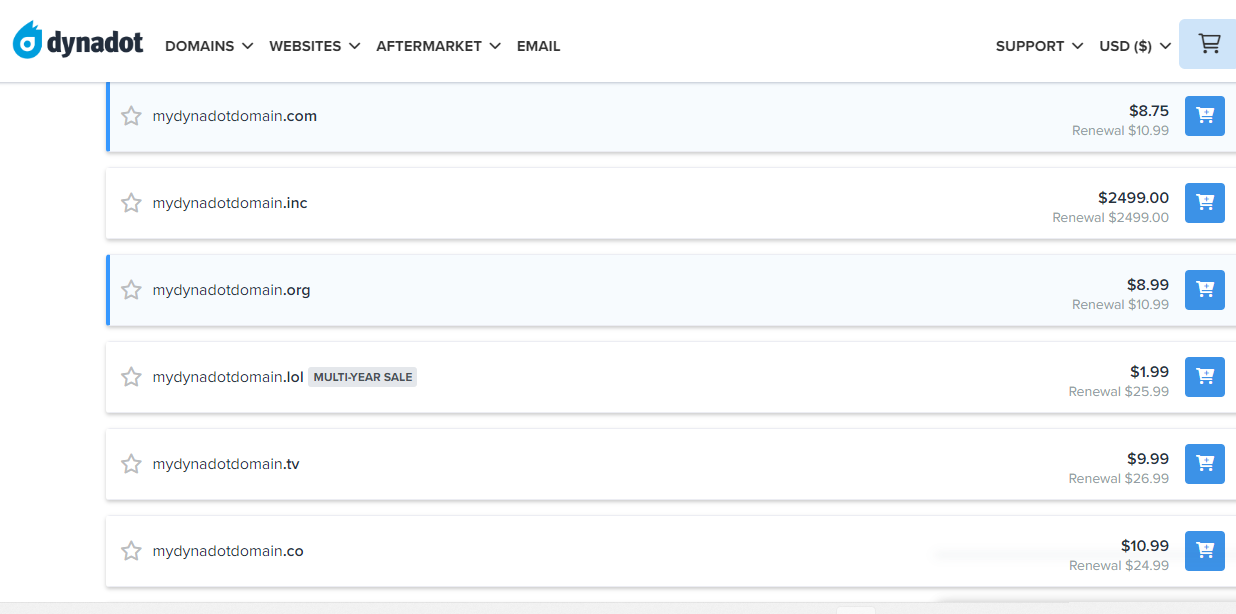
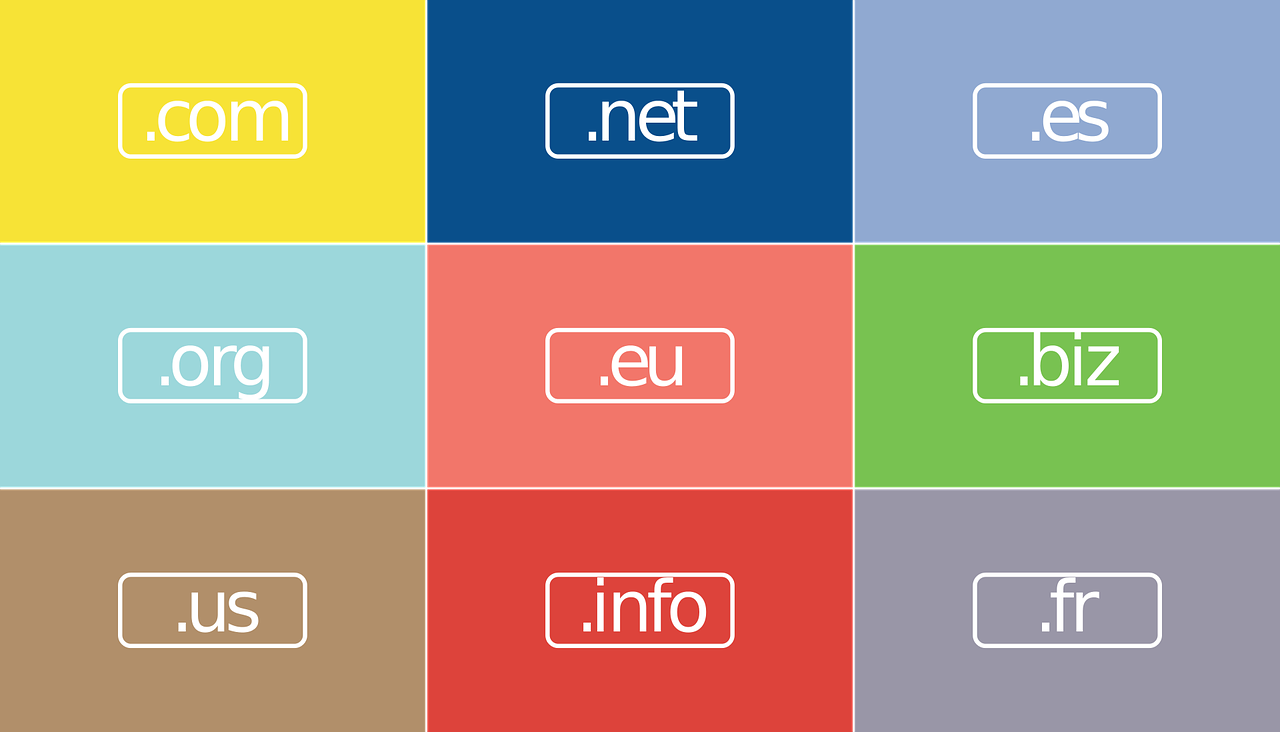
.COM: $8.75 per year (renews at $10.99)
.ORG: $8.99 per year (renews at $10.99)
.NET: $11.99 per year
.CO: $10.99 (renews at $24.99)
The above prices demonstrate the affordability of Dynadot for first-time customers. The prices decrease if you purchase in bulk and are the lowest when you buy in super bulk. In addition to the affordable cost, you also receive a free website builder.
Note that .COM, .ORG, .NET, and .CO are not the only domain extensions available on Dynadot. There are more; there are hundreds more.
Dynadot
Dynadot is a domain name registrar that provides domain registration, website hosting, and website builder services.
Dynadot is a domain name registrar that provides domain registration, website hosting, and website builder services. Show Less
Dynadot Domain Registration Service Review: Frequently Asked Questions
Before rounding off this Dynanot domain registration service review, let’s treat some frequently asked questions about the service.
Can you sell domains on Dynadot?
Yes, you can sell domains on Dynadot. The website has a domain marketplace where you can list domains for sale. This marketplace already houses thousands of domains. To add yours, you only need to be a registered Dynadot user.
Similar to registering a domain or website, selling domains on the Dynadot domain marketplace is straightforward.
When you list domains on the Dynadot domain marketplace, you can set whatever price you want. However, it’s ideal to be practical with your pricing if you want to make purchases.
Generally, the ideal listing price will depend on the domain category, characters, length, and, most importantly, age.
Does Dynadot provide free SSL?
Yes, Dynadot provides free SSL as part of its domain registration service. You get the SSL along with your domain when you pay for your subscription. Dynadot SSLs are Alpha SSLs, which are more secure and will secure both domains and subdomains.
The SSLs come with a 2048-bit CA certificate, which has 99% browser recognition. As a result, they follow the National Institute of Standards & Technology standards.
Dynadot SSLs are also fast to validate. In particular, your SSL certificate should be active on your website within twenty-four hours of purchasing.
Is Dynadot secure?
Dynadot is secure, and security is one of the company’s chief features. All Dynadot domains and accounts come with Account Lock, 2FA, SMS Authenticator, and Google Authenticator.
Account Lock will ensure no one takes over your account or highjack your domains. It typically requires entering a security detail – like your birthday – which you’ll set.
Two-factor authentication (2FA) is common and still effective in maintaining security. You can employ it in your Dynadot account via SMS or Google Authenticator. With this, you can secure your accounts and domains whether you have a smartphone – with Google Authenticator – or not – with SMS Authenticator.
How do I get a refund from Dynadot?
Dynadot does not issue refunds for domain purchases. But that doesn’t mean you cannot get your money back. In some situations, you can. You may have made a mistake by purchasing the wrong domain name.
In particular, you can get your money back from Dynadot if your domain is less than five days old. What you need to do is request a deletion of the grace period.
Once Dynadot admins approve it, they will credit your Dynadot account. Now, you cannot withdraw this money to your bank account. But you can use it to purchase other services from Dynadot.
Please note that not all domains support the deletion refund grace period. You can’t request it if you bought a .CO, .UK, .EU, .BE, or .PL domain.
A Final Word On The Dynadot Domain Registration Service Review
Dynadot ticks all the boxes for a reliable domain registrar when considering price, features, and customer service.
The company offers low-cost domain names; you can purchase domains, hosting, and a website builder; and there are multiple options to get help.
So, if you opt to purchase a domain name from Dynadot, you are making a good decision.
Feel free to drop your comment below regarding this Dynadot domain registration service review.
Dynadot
Dynadot is a domain name registrar that provides domain registration, website hosting, and website builder services.
Dynadot is a domain name registrar that provides domain registration, website hosting, and website builder services. Show Less
Learn why small businesses should invest in managed IT.
Running a small business is challenging enough without wrestling with tech issues. You’re juggling countless tasks, from managing team members to keeping your customers happy. Amid all this, you can easily overlook your technological needs. But here’s the thing: neglecting your Information Technology (IT) can cost you time, money, and even your hard-earned reputation.
Investing in managed IT services gives you a team of experts on standby, ready to tackle any issue that comes your way. From safeguarding your data to ensuring your systems run smoothly, managed IT services can transform how you do business.
In this article, you’ll learn the many reasons why investing in managed IT is a smart move for small businesses. Buckle up and explore how managed IT can take your business to the next level!
Cost Savings And Predictable Budgeting
Most small business owners think that robust managed IT solutions are too pricey for their company. However, managed services can actually lead to cost savings over time.
Instead of unpredictable tech expenses, you’ll pay a set monthly fee. This makes budgeting a breeze and helps you avoid surprises.
No more panicking when your server crashes or hackers strike. Your outsourced team has your back, tackling issues before they snowball. This saves cash and keeps your business operational.
But before you can enjoy these benefits, you need to find a reliable managed IT support service first. Start by researching providers in your area. Look for companies with experience serving businesses like yours. Check online reviews and ask for references from current clients.
Next, schedule consultations with your top picks. During these meetings, ask about their response times, security measures, and backup solutions.
With managed IT, digital nightmares become distant worries. You’ll sleep easier knowing experts are watching your business 24/7.
Access To Expertise And Advanced Technology
Hiring a full-time internal IT staff can be beyond your budget as a small business. But managed IT services offer a practical alternative. By partnering with these providers, you tap into a pool of experts who are up-to-date with the latest technologies and best practices.
Imagine leveraging advanced cybersecurity and cutting-edge cloud services without the steep costs of ownership. Managed IT services equip your business with these tools at a fraction of the cost, giving you a competitive edge.
You’ll benefit from their extensive knowledge and access to advanced technologies. You can stay current without continual investments in training and new tools. This saves you money and keeps your business agile and robust in a fast-evolving market.
Tech troubles stealing time from your internal IT team? Picture spending your day innovating instead of troubleshooting. You get to focus on your core business activity, bringing more products to life. By outsourcing IT management, you reclaim your focus and drive your business forward.
But this shift isn’t just about computers –it’s about unlocking growth. Maybe you’ll finally launch that new product line or revamp your marketing strategy. The possibilities are endless when tech issues no longer hold you down.
Think of it as clearing the clutter from your business brain. With the day-to-day tech worries off your plate, you can zoom in on what truly matters. You’ll be amazed at how much more you can achieve when technology supports your vision instead of hindering it.
Cyber threats don’t just target big corporations. They’re also after small businesses. Why? Because smaller operations often have weaker defenses. But don’t panic! The best IT service provider can be your secret weapon.
These tech experts act as your digital bodyguards. They build solid security walls to keep hackers out. Viruses, ransomware, phishing emails? They’ve got solutions for all of these.
But security is just the start. Remember those confusing data protection rules? Your IT team stays on top of them. They ensure you follow all the necessary guidelines, protecting you from fines and reputation damage.
Basically, managed support services fight your network security threat war for you. They protect your business and keep you compliant.
Access To Unlimited Support
Problems can strike at any time, and having help available 24/7 is essential. Late-night emergencies happen from time to time. For instance, your e-commerce site might crash during a holiday sale. Or your email server could go down before an important pitch. With round-the-clock technical support, you get immediate assistance, regardless of the issue and time.
This constant coverage is even more crucial for companies operating across time zones. Your New York office can get help even when your IT team in London is fast asleep.
Always-on support does more than fix problems. It gives you peace of mind, knowing that your business is safe. You can make bold moves with technical backup just a call away if things go sideways.
Proactive Maintenance And Reduced Downtime
IT support keeps evolving, making proactive management essential. Imagine a guardian watching over your digital world, spotting issues before they snowball. This keeps your business humming along smoothly.
Remember the last time your computer crashed right before a big deadline? Frustrating, right? Now, picture a world where those hiccups are rare. That’s the power of round-the-clock monitoring. It’s like having a safety net for your digital operations.
Smart businesses don’t just react—they prevent. Regular maintenance keeps your systems fit. It also ensures business continuity, and in this world, being ahead means staying online. So, embrace proactive IT, and watch your business thrive.
Business evolution demands adaptable technology. As your company expands, your IT needs also shift. Flexible support accommodates these changes, ensuring your systems align with your goals.
Are you adding new team members? Your IT partners quickly set up their workstations. Launching a product line? They’ll scale your infrastructure to handle increased demand. Even during slowdowns, you can easily adjust resources to optimize costs.
This approach eliminates disruptive overhauls and costly upgrades. Your systems evolve alongside your business, ensuring a smooth operation through every phase of growth. It’s like having a tailor-made solution that adjusts to fit your changing needs.
Improved Business Continuity And Disaster Recovery
Disaster strikes without warning, threatening your business continuity. A robust recovery plan acts as your company’s shield against the unexpected. When crises hit, you’ll be ready to bounce back quickly, keeping your operations running and data secure.
Innovative preparation pays off. Your disaster recovery strategy protects vital information and maintains smooth operations even in turbulent times. It acts as an insurance policy that keeps your business afloat.
Reliability in challenging times impresses customers. They’ll appreciate your service when others can’t. In fact, your resilience can strengthen their trust and loyalty.
With the right approach, potential catastrophes become manageable hurdles. Your business survives and thrives, turning setbacks into opportunities for growth and innovation.
Conclusion
Investing in managed IT services can transform your small business. By handing over your IT needs to experts, you gain access to top-notch technology and knowledge without the high costs.
Managed IT services provide round-the-clock support, proactive maintenance, and advanced security measures. This means less downtime, fewer tech headaches, and more time for you to focus on growing your business.
Whether it’s scaling up with your business needs or preparing for unexpected disasters, managed IT keeps you ahead of the curve.
1. Stuart Cooke from Evalian Cybersecurity Consultancy Firm
To secure and protect a website, you must limit the number of people you give access to. The more individuals have access to your website, the more likely their IP addresses are to be targeted by hackers.
Of course, for large organizations, it’s often necessary for a lot of people to log in to the back end of a website, and if that’s the case, then I would recommend being careful with the roles you grant.
Keep full admin access for the very few people who will require it regularly; for the rest, author, editor, or read-only access should suffice.
2. Dusan Stanar From VSS Monitoring
My most significant advice is to limit client access to the website. This means you determine how often a user can request a page over time. For example, maybe they can only access ten pages every 30 seconds.
This helps prevent automated hacking and scripts meant to hack your website, which requires them to be able to access your site thousands of times a minute. Doing so will drastically increase your security and reduce the risk of being hacked.
3. Jeff Neal, Owner of The Critter Depot
I am a big proponent of 2-factor authentication. Using two separate methods is a great way to force anyone to verify their identity. However, sim swapping has recently caused a lot of problems for people. This proves that 2FA is unsuitable if people rely on text messages or phone calls to verify their identity. Sim swapping is where a hacker successfully switches the target’s mobile number onto their device.
Then, when the hacker logs into their target account, the hacker will receive a text message or phone call with the secret code, allowing the hacker access to the target’s account. The best way to prevent this is to use a code generator app that changes the numbers every 30 seconds.
4. Saqib Ahmed Khan, Digital Marketer at PureVPN
The first and foremost necessity is to install an SSL certificate to secure and protect a website. Any website without HTTPS doesn’t encrypt data. Keep the plugins or any software for your website up to date because vulnerabilities are discovered from time to time.
Use two-factor authentication to provide specific data because the website administrator requires more security than a regular user. Store passwords in a hashed form, not plain text; if a data breach occurs, the passwords will still be secured.
Always validate inputs on your website because cross-site scripting and SQL injection attacks occur daily. Maintain timely backup mechanisms for your website because anything can happen in the real world.
5. Ashley Simmons, Webmaster at Avoid the Hack!
I recommend that all websites should force their HTTPS version at the server level:
HTTPS encrypts data sent to and from your web server(s)
Forcing HTTPS on the server level (for example, Apache) ensures that all versions served are secure
HTTPS helps protect against eavesdroppers
Without HTTPS, many browsers will encourage visitors not to interact with your site
Using HTTPS improves SEO (search engine optimization)
Forcing HTTPS at the server level means all visitors get directed to the secure version.
6. Per-Erik Eriksson, Author of VPNetic.com
Besides securing your website with proper hosting, firewalls, and anti-malware software, the best thing you can do for your website security are the following:
Enable Multi-Factor Authentication.
Use a strong password AND username.
Never click links in emails.
People often overlook these things because they will never slip up. Social engineering is the most common hacking method today, yet it rarely gets the attention it deserves.
7. Jessica Rose, CEO of Copper H2O
Since many of us work remotely and there is a greater chance of getting hacked due to less secure home office computers, ensuring your online systems are protected is more critical than ever.
Our #1 for businesses is to activate two-factor authentication on their website and related accounts. When started, no one can log into your website or accounts unless they know your password and the security code sent to your smartphone at the time of login. This method costs nothing and dramatically increases your website’s and business’s security.
8. Tom Winter Tech Recruitment Advisor & Co-Founder at DevSkiller
The strength of passwords is often neglected as an essential security factor. Sometimes, even experienced IT professionals will set weak passwords for admin accounts, exposing your entire website to outside attacks.
To prevent this from happening, insist on strong passwords for your admin panel and external users. If you have any logging option on your website, require all users to use different characters when creating a password. That way, you can secure and protect a website.
9. Hary Toledo, Strategic Partner at CenturyLink
Distributed denial-of-service (DDoS) attacks, the weapon for cybercriminals targeting Internet-based business sites, can cause prolonged outages for services like eCommerce, online bill pay, or VoIP telephony. These attacks can be devastating if you rely on web-based transactions to generate even a tiny portion of your revenue.
When users access websites, their requests are routed to the corresponding servers as appropriate during legitimate web use. However, the infrastructure (servers, routers, firewalls, switches, and circuits) can only process a finite amount of traffic. When that limit is reached, additional requests cannot be processed.
In a DDoS attack, hackers overwhelm targeted servers with many requests from a host of separate computers, blocking legitimate server access. A DDoS attack can be so enormous that it completely overwhelms routers, network links or servers — rendering the location unavailable for all Internet use.
10. Artur Yolchyan, Expert Software Engineer & Owner of Coding Skills
To develop a secure website, you should measure 10 OWASP protection for your website. To successfully do it, you should use a mature web development library such as Spring Security to reduce the risk of your website being attacked.
I recommend using already existing and well-tested security frameworks to protect your website and hiring experts to configure these frameworks.
11. Greg Scott, Author and Cybersecurity Professional at Infrasupport Corporation
My Ukrainian friend, Ihor, offered to penetrate my website a few years ago, and I agreed. What could he possibly find? After all, I am a professional… Every time I get cocky, I learn a lesson in humility. It took him only a few minutes to find a directory I had neglected to lock down from directory listings. I was embarrassed and angry and considered not fixing it. And so I can identify with people faced with the same stress on a larger scale. But after feeling sorry for myself, I did my homework and fixed it. I’m grateful to Ihor for his work. Embarrassment is better than penetration.
12. Stacy Clements, Owner of Milepost 42
Keeping the software updated is one of the most essential actions to secure and protect a website. This is especially important if you’re running a CMS like WordPress, Joomla, or Drupal, as these systems depend on multiple software packages for functionality. However, any website runs on a web server, and it’s just as important (and often overlooked) to ensure the software on that server is updated.
Another crucial component of securing a website is protecting access to the site. Use the principle of least privilege to ensure access is restricted to the lowest possible level and enforce strong passwords and two-factor authentication.
13. James LePage, Founder & CEO of Isotropic Design
The most effective thing a WordPress website owner can do to secure their site is install a plugin called Wordfence. Wordfence is a free web application firewall and malware scanner. This tool blocks all IP addresses the company has maliciously by logging in to your WordPress website’s admin dashboard, preventing brute force attacks.
You can set up two-factor authentication and incorporate Google’s reCAPTCHA bot protection system. The tool will also periodically scan the files that make up your website for any malicious code. If it identifies any files that shouldn’t be there, it will automatically delete them.
As an agency, we use this WordPress plugin on all our websites. It’s a free tool, is automatically installed and configured, and is the most comprehensive security solution for WordPress websites.
14. Rahul Gulati, Founder of GyanDevign Tech Services
This is a no-brainer, but people pay little attention to this. It is still a pity to find people having passwords like “987654321†or “admin12345â€. A WordPress user with a weak password is an open door for hackers. The lowest point on a website is your password; the stats are apparent. A Linux-based computer produces 350 billion guesses/second. So, there are a lot of chances for your password to be one of them.
Wordfence has to say that there have been six million attacks on WordPress websites in 16 hours. A strong password will keep you out of reach of such malicious threats. You can also see why WordPress emphasizes a stronger password as well.
Password strength meters are a simple add-on you can opt for. Just add the following line to your functions.php file.
wp_enqueue_script( ‘password-strength-meter’ )
Usually, the combination of 2FA is a username with a password or username with a HOTP. This OTP usually lasts for a minute, keeping the window very short.
The real advantage of 2FA is the integrated device to secure the WordPress website. Hackers cannot get through without the OTP, even when they get hold of your credentials,
15. Pushpraj Kumar, Business Analyst at iFour Technolab
You can add a security socket layer (SSL) to your website with HTTPS, a protocol that allows you to send secure communication over your computer network. You can shield your website against SQL injection.
Regularly watch your email transmission ports; you can also check your communication ports under email settings. Don’t allow highly suspicious file uploads. Invest more in website vulnerability scanners that will identify technical weaknesses on your website. Confidentiality refers to access control of information to ensure user authentications and access control components.
16. Samuel David, Founder of Smart Home Vault
For WordPress users (who represent about 20% of self-hosted websites globally), I’d recommend installing the Wordfence plugin. Wordfence plugin is a security plugin and has free and paid plans. Besides being an automated tool, Wordfence is straightforward hence ideal for users who aren’t tech-savvy.
Depending on settings, Wordfence will block an IP address for 4 hours after five failed attempts. For every failed attempt – and other issues detected (like plugins with security risks) – Wordfence will notify by email. Still talking about email alerts, I like that Wordfence is big on updates/news about the vulnerability and risks of WordPress and WordPress plugins. That way, users can act just in time.
17. Abdul Rehman, Cybersecurity Editor at VPNRanks
The one website security tip I’d like to give you is setting up a web application firewall like Sucuri on your website. A WAF is essential for your website security as it filters and blocks malicious and harmful traffic.
You can also block and allow specific types of traffic as you desire. It’s essential since it prevents harmful injections and hack attacks that can harm your site and the data it holds.
18. Bruce Sigrist, Web Developer + WordPress Specialist at Phase Three Goods
To secure and protect a website, be thorough and uncompromising.
On thoroughness… it’s easy to disregard crucial parts of website security because the jargon is new or the setup looks cumbersome. From 2-factor authentification to firewalls and IP-limited logins, these steps might seem overwhelming to non-specialists. Hackers and spambots are determined; every obstacle you throw at them will reduce the likelihood of a breach.
On being uncompromising… while searching for security improvements, you might find limitations in your site’s build or hosting environment. Don’t be afraid to switch hosts or frameworks if circumstances limit your site security.
19. Noman Nalkhande, Founder of WP Adventure
I take the utmost care to ensure no gaping loopholes for a security breach to occur. Since WordPress is hugely popular, some fantastic plugins are built primarily to serve this purpose.
Sucuri and WordFence are extremely popular and do a great job. Besides using a security plugin, I’d also advise keeping your WP themes and plugins up to date with the latest versions. Changing the default login URL from /wp-admin to something more unique using a plugin like ManageWP or adding a few lines of code directly in the .htaccess file is also wise.
20. Juan Pineda, Partner at Sofyma
Most attacks on business websites are happening because three aspects are disregarded: hosting security, website software maintenance, and password strength.
If possible, you should opt for a robust hosting platform that isolates the live environment from any server access. This guards against unauthorized updates that can result in compromise.
Independently of the hosting provider, it would be best to use strong passwords to access your server, control panel, or website management system.
Another essential aspect to consider is keeping your platform software updated. If you are not using a managed hosting provider, you should stay current with security releases for the operating system, SSL software, programming language, and database you use.
If you use a content management system or framework for your website, you should also keep it updated with the security releases published by the community.
21. Chris Love, Owner of Love2Dev
Using HTTPS for all communications is a no-brainer today. It was once complicated and expensive. Today, it takes about 30 seconds and is free.
A common mistake I see is improper use of identity for authentication. Many websites incorrectly use identity to block access to sensitive account data. Often, applications are brought to me. API APIs are not secured, and direct access to the database can be had with direct calls to the exposed API endpoints.
Another recommendation I am making more and more is using biometrics and passwordless authentication. Here, only verified tokens are made available to the application. The user’s device verifies the identity with facial recognition or fingerprint analysis. It is hard to crack, and storing a password hash is unnecessary.
22. Jessica Rhoades, Owner and Designer at Create IT Web Designs
Most people think that web security is just installing a WordPress plugin.
It is more than that. It is forming a plan around your website. First, do you take regular backups of your website and keep them off the webserver? Keeping a backup is critical to protecting your data.
Secondly, are you updating your plugins on a regular schedule? Vulnerabilities in plugins are constantly being discovered.
Lastly, do you have any subdomains, and are you updating and scanning those regularly?
An old test server on a subdomain that a customer forgot about was how one of my customers was hacked. The subdomain plugins were not updated for over two years and were hacked. Since they could get into the subdomain, it affected the main website. We quickly resolved the security with the subdomain, but the main website was down for about 6-8 hours.
23. Nir Kshetri, Professor at the University of North Carolina-Greensboro
Many strategies must be used to secure and protect a website, but I would emphasize two things. First, companies should practice extreme precautions and safeguards if they allow others to upload files through their websites to ensure that no malicious files are uploaded.
Moreover, if users upload too big files, they can bring the website down. An option to keep the website secure would be not to allow file upload.
However, this is not a practical strategy for many companies. Companies should allow uploads to support only one or a few file types. They can set up an email address and list on their Contact Us page to submit other file types. They should also limit the file size to avoid DDoS attacks and scan received files for viruses and malware.
Second, if the website stores passwords, it is critical to hash passwords and employ a more muscular hashing function (e.g., bcrypt) rather than a simple function (e.g., SHA1). In this way, even if hackers can penetrate a company’s network, it will make it difficult to steal passwords and use them for nefarious purposes.
24. Michael Miller, CEO of VPN Online
As a security evangelist, one tip I always preach is to update everything! Your first line of defence will always be your antivirus, operating system, hardware, and passwords. Make sure you religiously update them. As an added insurance, keep offsite backups. The easiest way to fix a problem is by restoring to a previous backup.
25. Nelson Sherwin, Manager of PEO Companies
Did you know your domain name is a target?: My one tip is to not forget about your domain name. It can be a massive attack target, so you must prioritize its security. A registrar with security as a primary focus is a great first move. It would be best to look into adding a domain lock and setting up multi-factor authentication for extra steps to ensure it is kept safe.
26. Chase Higbee, Lead IT Strategist at Atlantic.Net
The key to website security is to minimize the attack surface of the website infrastructure and place controls over how network traffic reaches the website.
Exposing only the front-end web server(s) to the public Internet using a DMZ is critical in logically positioning application and database servers behind additional firewalls.
Protect the front end by proxying TLS traffic through a secured web gateway and create strict security policies to manage end-to-end traffic inside the perimeter network.
27. Jon Rasiko, Managing Director at DeepCode
Starts with the basics. Ensure you take the time to carefully configure your web server using cryptographic solid parameters, a necessity for many frameworks such as PCI-DSS or HIPAA.
Learn and implement web security headers like the Content-Security-Policy header to mitigate some of the top 10 OWASP security issues. Secure your cookies with the proper flags, such as ‘HttpOnly’ and ‘Secure’.
One last piece of advice: protect your code repositories by removing passwords and tokens and cleaning up non-essential files on your production web servers.
28. Kyle Hrzenak, President & CISO at Green Shield Security
Some of the best ways to secure a website are as follows.
SSL – An SSL is essential because it ensures data safety if you protect SSLv3 Poodle.
Use website penetration software such as Acunetix Web Vulnerability Scanner. Tools similar will provide errors currently on your website or web server and provide documents to fix those issues.
29. Alex Artamonov, Cybersecurity Specialist at Infinitely Virtual
If a website is hosted in a shared environment, back-end server security is the hosting company’s responsibility. Security lies with the owner if the server is hosted within a private environment.
Special attention must be paid to front-end and back-end code in both cases. Many interactive websites have opted to use both pre-written and custom JavaScript libraries. It’s essential to ensure the code doesn’t include unwanted functionality when using public libraries.
With a website hosted on a private server, additional vigilance – e.g., an effective patch management policy – is essential. Likewise, close any unused ports, turn off filtering of any remote management ports, use secure passwords, and run regular vulnerability tests.
30. Nicholas McBride, Cybersecurity Consultant at Ecuron
When securing a website, four basic steps will prevent most attacks.
First, check that all permissions are correctly set. One of the most common avenues of attack is via improperly set file permissions, allowing attackers to view sensitive files or upload their own.
Second, ensure that HTTPS is adequately enabled and strictly required for all domains and subdomains.
Third, configure DNS properly to prevent the possibility of DNS hijacking.
And finally, patch your server and operating system software promptly. These four steps will do the most to keep your website secure.
31. Lumena Mukherjee, Cybersecurity Consultant at SectigoStore
Website security is often assumed to be the responsibility of hosting providers. However, that’s not the case. Securing the site is the site owner’s responsibility. The tips below can get you started in the right direction:
Run regular vulnerability scans and perform manual web application security assessments to identify and fix security weaknesses before a breach.
Use an SSL/TLS certificate to encrypt the communication between client browsers and your webserver to guarantee that no data is transmitted in plaintext.
Back up your website automatically using a third-party platform regularly to minimize the impact of any issues.
32. Vladlen Shulepov, CEO at Riseapps
It’s true that to provide website security, there should be a strategy in place. First, data encryption is one of the most important ways to protect a site, so such a well-known measure as an SSL certificate must be used.
Any framework, cloud service, firewall, etc., used in the development process should be trustworthy and safe, and the same applies to servers. Multi-factor authorization is the most secure choice if there is a login option. If an intrusion occurs, a data breach protocol can help minimize the damage.
33. Joe Tuan, CEO of Topflightapps
Our WordPress site has been recently hacked multiple times. In response, we are applying Cloudflare rate limiting. It can help determine excessive requests for specific URLs or an entire domain.
On top of that, we took stock of all external plugins we installed on our site and removed those posing a threat: no longer updated and used.
34. Maxim Ivanov, CEO of Aimprosoft
Besides standard website security measures, such as reliable hosting, patching all applications on the webserver to the latest version, etc., use more enhanced precautions.
Firstly, choose a firewall to secure your servers and restrict access to all undesirable ports except those that should be available (e.g., 80 and 443).
Secondly, use WAF (web application firewall) to secure your app from outside attacks, such as SQL injections, XSS (Cross-Site Scripting) attacks, file inclusion, etc. Remember that there are special services, such as Cloudflare, that function like reverse proxy, provide WAF and DDoS mitigation, and take care of website security for you.
Finally, security audits of a web application code are conducted to minimize its vulnerability and configure fuzzing using a tool like Fail2ban.
35. Swapnil Bhalode, Co-founder and CTO of Tala Security
Client-side vulnerabilities are the web’s weakest link, resulting in data breaches at leading global brands – and the biggest GDPR OK to date (BA, $230m). Known as Magecart or credit card skimming, these attacks succeed because only 1% of website owners deploy security policies that protect the client side.
The best strategy to secure websites against these attacks is to deploy browser-native security controls such as CSP, SRI, and other advanced standards.
Developed by the world’s leading web experts, like Google and GitHub, they’re constantly refined with the latest web developments. They provide the most comprehensive, future-proof protection against client-side attacks.
36. Rob Shavell, CEO of Abine/DeleteMe
To secure and protect a website as much as possible, you must use strong passwords for your server and website admin area. In addition, if your site requires a sign-in, you should encourage your users to use best password practices to protect their data.
37. Laura Fuentes, Operator of Infinity Dish
Keep your software up to date. Outdated software may prevent a leak of information. Strong passwords. Enforce a firm password policy and have users change them regularly. Every 3-4 months at most. Do not use cookies to secure susceptible information. Hackers easily manipulate them. Hold web security training for your employees. It helps them understand the importance of security and the ability to spot vulnerabilities readily.
38. Heinrich Long, Privacy Expert at Restore Privacy
There are three leading protective technologies to consider when implementing a solid web security strategy to secure and protect a website.
First and foremost, you should invest in a tremendous cloud-based firewall; Norton is a great provider with a range of products to suit almost any website. The firewall protects your website by evaluating visitors and blocking potential hackers from gaining unauthorized access to your data.
Secondly, support this with an application-level firewall that explicitly protects your site from vulnerabilities created by apps or services linked to your site.
Finally, invest in technologies to support application hardening. Application hardening is a crucial aspect of your security strategy and is required to prevent hackers’ efforts to tamper with an app and compromise your site.
Bottom Line
There you have it! Thirty-eight ways to secure and protect a website!
According to Webarx Security, about 30000 new websites were hacked daily in 2019. The most popular CMS, WordPress, is reportedly the most hacked CMS in cyberspace.
Thankfully, the interviewees have provided helpful website security tips that you can apply to secure and protect your websites.
Note: This was initially published in July 2020, but has been updated for freshness and accuracy.
The AI Product Owner takes ownership of everything regarding the project. Whether it is from prioritising work items to ensuring that their team delivers the right features, they play an important role in facilitating Agile product development along with the product manager.
When AI product owners have the POPM Certification, they can significantly contribute to the development of a product through the Scaled Agile Framework.
Who is an AI Product Owner?
An AI Product Owner is an individual who integrates artificial intelligence into their workflow. In an Agile team, they are in charge of prioritising, developing, and delivering products by using AI insights.
What is the Difference Between an AI Product Owner and a Normal Product Owner?
An AI Product Owner is a professional who uses AI tools to enhance product ownership in Agile through automated processes, data-driven insights, decisions, and enhanced stakeholder engagement through better presentation and metrics. On the contrary, normal Product Owners rely on traditional product management practices to guide agile teams.
What is the Difference Between an AI Product Owner and a Product Manager?
An AI Product Owner takes ownership of everything regarding a product. This includes the product backlog, program progress, and creating user stories. They integrate AI into these tasks for better efficiency. On the other hand, Product Managers manage the overall pathway of the project. They define the product’s vision, conduct market research, and develop the product roadmap.
What is POPM?
The SAFe® Product Owner/Product Manager certification, offered by Scaled Agile, helps professionals develop product-management and product-ownership skills within the Scaled Agile Framework (SAFe®).
The AI course enables professionals to integrate AI into Agile product development processes, which helps optimize the workflow. When youRegister for the SAFe POPM Live training, you will get access to AI-driven tools and practices that can help you effectively facilitate product development in high-stakes Agile teams through the Scaled Agile Framework.
Once professionals complete this certification, they will be able to work with agile teams to improve the backlog, understand customer and business needs, and deliver items of considerable work value through the insights of artificial intelligence.
How Does POPM Help AI Product Owners?
An AI Product Owner applies Agile product-management practices to guide the development of AI-enabled products. The role involves understanding customer needs, prioritizing the Product Backlog, collaborating with cross-functional teams, and supporting decisions throughout the product lifecycle. AI Product Owners also consider responsible AI practices, data quality, model limitations, and product risks while working to deliver meaningful customer value.
Product Backlog Management
POPM helps AI Product Owners manage backlogs in a smarter way. By using lean-Agile methodologies under the Scaled Agile Framework, Product Owners can cut down irrelevant items (waste) from their backlog to prioritise work items that bring customer or business value. AI can further refine the backlog by automating tasks of low priority and providing data-driven insights about the work items that should be prioritised.
Define Clear Goals
During product development, it is important for Product Owners to be able to define the goals of a product and its features. The POPM course helps Product Owners build the skills to communicate these goals effectively to stakeholders and customers. Through the analysis of current information and historical data, AI integration helps ensure that the goals align with business needs and remain relevant.
PI Planning
With a POPM certification, Product Owners will be able to effectively contribute to PI planning by ensuring that stakeholders and other Agile teams align towards the product’s goal and vision. By using AI in the PI planning process, Product Owners will also be able to predict outcomes and dependencies that may arise between teams.
Stakeholder Management
Product Owners will be able to effectively collaborate with stakeholders, which can help Agile teams better understand product requirements. With the inclusion of AI, Product Owners can present team progress to stakeholders in a way that is clear and concise. This improves a team’s relationship with them while also improving clarity.
Customer Feedback
AI helps product owners understand customer requirements, which ensures that the decisions taken by the teams align with those needs. AI helps make this process faster by using sentiment analysis to compile large amounts of feedback into definite pain points for the team to easily address.
The Certified Scrum Product Owner course (CSPO) provides an in-depth guide to product development in the Scrum framework. Byenrolling for the CSPO certification course with Simpliaxis, you will gain hands-on experience in prioritising the product backlog, measuring progress, and defining while working towards becoming a Certified Scrum Product Owner licensed through Scrum Alliance.
Conclusion
For an AI Product Owner, starting their day moves beyond simply checking the product backlog. It involves utilising AI-driven insights to make informed decisions, prioritise, and understand customer feedback.
A POPM certification can help professionals enhance these tasks while also helping them refine their product ownership and product management skills under the Scaled Agile Framework. When Agile skills are combined with AI insights, AI product owners can make choices that lead to their teams being able to build products that enhance business and customer value.
In this post, I will show you 3 simple tricks to verify a site is secure before signing up.
Halt! Have you checked it’s secure? This is exactly the mindset forsigning up to a new website for the first time — be it for shopping, gaming, info, lifestyle, or joining a membership community. The whole process can feel properly boring and routine, and your mind can go straight on autopilot.
But just think… every time you hand over your email, personal deets, preferences, or card information, you’re trusting that site with your entire identity as well as your money. Cybercrime is rife, and has grown only more sophisticated over the past two decades, as the digital realm has become widespread.
Fake sites or cleverly disguised phishing emails and pages look more convincing than ever, so verifying a site’s security before signing up isn’t old fashioned paranoia; it’s basic “digital hygiene” for the everyday person.
This is especially true when money is on the line! Just think about the number of people you may know who register on new sites for shopping or online casinos and digital betting platforms for gaming (both of which make use of your financial details).
The latter especially leads people eagerly to claim a bonus or try a new slot. So, knowing how to check a site’s credentials first is as important as understanding things like casino wagering requirements, because both are about making sure you know exactly what you’re getting into. A secure website can still have strict terms, but at least you know your personal and financial information is protected from outright theft, which you want to always avoidf.
Let’s look at three practical, low-tech ways to tell if a site is safe to sign up to, thinking about elements that are simple enough for anyone to apply, but detailed enough to catch most of the common red flags.
3 Simple Tricks to Verify a Site Is Secure Before Signing Up
1) Domain Research and Reputation
Just think, even a shiny SSL certificate won’t save you from a scam if the site itself is fraudulent! The trick is to look up the domain name, as scammers often use URLs that are very close to legitimate ones, changing just a letter or adding a hyphen. Take a moment to read the domain carefully and compare it with the official address you know.
Of course, there are loads of decent free tools, such as WHOIS lookups, to see when the domain was registered and who owns it. A brand-new domain registered anonymously may not always be a scam, but it’s another warning sign, especially if it’s claiming to be a big, established brand. Conversely, a domain that’s been active for years and has a named owner with a real address looks much more trustworthy.
Also, check online reviews and reputation scores and see what other users of the site are saying, because this is where you can often find useful discussions on forums or watchdog sites. Any pattern of complaints about missing payments, poor support, lack of contact, or disappearing accounts can reveal a problem before you ever sign up.
2) Check HTTPS and Valid Security Certificates
The first and most clear (and obvious) trick is to examine the web address bar. Secure websites use HTTPS (HyperText Transfer Protocol Secure) instead of plain HTTP. This means the data you send and receive is encrypted, making it far harder for hackers to intercept.
In modern browsers, you’ll see a padlock icon to the left of the URL, and clicking on it reveals information about the site’s security certificate. But don’t stop at just spotting the padlock!
Anyone can technically get a basic SSL certificate, so you have to look deeper by clicking the padlock or the “Site Information” tab to see who issued the certificate and for which domain, as reputable businesses typically have an extended validation (EV) certificate that lists their name or company.
While these EV certs are less common now, legitimate sites will at least have a certificate issued by a recognized authority (you can find these with a quick search online). Of course, if the browser warns you of an invalid certificate or mismatched domain, treat it as a red flag!
That doesn’t always mean the site is malicious, but it’s a clear sign you shouldn’t enter personal info until you know what’s fully going on- Think of HTTPS as the seatbelt: it won’t guarantee your safety in every scenario, but you’re at much greater risk without it!.
3) Evaluate Payment and Privacy Methods
Lastly, a site’s payment options and security policies tell you a lot about how it handles customer info, as a legitimate site typically offers well-known payment gateways (think PayPal, Stripe, Visa, Mastercard, and others) rather than obscure processors or cryptocurrency-only payments. Established payment providers have their own security vetting, so the presence of these options is a good sign!
On top of this, you can read the site’s privacy policy and terms of service. Yes, indeed everyone agrees that they are universally boring (not to mention often time consuming), but they’re also a space you’ll find out how your data is stored, whether it’s shared with third parties, and what recourse you have if something goes wrong. If the policy is vague, non-existent, sketchy or riddled with errors, that’s a signal to think twice before you act and move ahead.
Another useful check is whether the site supports two-factor authentication (2FA) for account logins, an extra layer of protection, as well as clear contact information (a physical address, a phone number, and/or a customer-service email). Scam sites often hide behind contact forms or provide no details at all.
Small Effort, Big Pay Off
The online realm is great, but full of risks if you’re unaware, such as malicious messages and email scams. By applying these three simple tricks: checking HTTPS and certificates, researching the domain, and evaluating payment methods and policies, you’re giving yourself a large and powerful layer of protection.
It’s not about being paranoid, it’s about staying informed and aware of those red flags that say to the prepared, “do not enter”. Next time you’re ready to sign up for a new website, just slow down long enough to verify it’s the real deal — think of it as a quick security checklist!
In this post, I will talk about the death of “Patch Everything”.
In 2026, “zero vulnerability backlog” is mathematically impossible. It’s also unwise.
The theme in cybersecurity today is simplification, unification, and power. And most importantly, aligning with business objectives.
To keep up, teams need to exit the “cybersecurity vacuum” in which all things revolve around security-only metrics (CVSS scores, how many on the backlog). Instead, they must adopt an approach that looks at what matters in the broader context of the business.
Even if that means leaving some “high value” CVEs behind.
Security Cannot Survive on VM Alone
Traditionally, vulnerability management programs discover and rate CVEs based on an objective, external severity score. The days when that was enough are gone.
Vulnerability fatigue is one indicator that “clearing the backlog” is no longer working—or workable. Hundreds and even thousands of vulnerabilities can be discovered in a single scan, and companies are doing these scans quarterly.
Even if resources-strapped teams could get to them all, they’d be wasting their time and doing nothing else. Meanwhile, sophisticated attackers are looking for more than just vulns; they’re searching for weak passwords, misconfigured access policies, missing database security controls, unprotected APIs, shadow data, and more.
Putting all your stock in the VM basket leaves all these other avenues exposed.
Not All Vulns Are Created Equal
Besides vulnerability fatigue, not all vulnerabilities are worth patching. Consider the opportunity cost of patching a benign CVE just because it’s on the list.
Think of what could have been done with that time, like threat hunting, discovering shadow data, or fixing something more important. For instance:
A “Medium” risk on a Domain Controller could be an emergency.
A “Critical” alert on an isolated print server may be noise.
CVSS scores don’t give you that extra data. They don’t tell you what’s best for the business. They just label which threat is most severe against an objective, external standard. And that doesn’t even tell you which threats attackers are actively exploiting. Even clearing out all “Critical” alerts isn’t guaranteed to get you any close to “safe.” You need additional context for that.
The bottom line? Teams need to shift the metric from counting (how many bugs did we squash?) to context (did we fix the security gap that actually threatens revenue?). This context-driven remediation is embodied in exposure management platforms today.
Exposure Management: Curing Vulnerability Fatigue
Exposure management (EM) platforms are purpose-built to deliver actionable insights that tell teams where the business value lies—and what’s at stake.
Once organizations determine which assets are most business critical, EM platforms scour the entire attack surface identifying what could go wrong. Does this include vulnerabilities? Yes. But it includes so much more.
While VM platforms give you part of the picture, they leave most of it out. Especially given the complex architecture of most modern enterprises today.
This is why single-minded investments in vulnerability management programs can only do so much. Even clearing the backlog one hundred percent would still leave organizations exposed. And because VM is still essentially reactive, it wouldn’t age well in an era when AI-driven attackers demand proactive mitigation.
This is why VM programs are on the way out, and exposure assessment solutions are on the way in. At least according to Gartner.
What Gartner Has to Say About Exposure Management vs. Vulnerability Management
“Security operations managers should go beyond vulnerability management and build a continuous threat exposure management program to more effectively scope and remediate exposures,” they state in their publication “How to Grow Vulnerability Management into Exposure Management.”
Additional insights include:
The limitations of VM: “Creating prioritized lists of security vulnerabilities isn’t enough to cover all exposures or find actionable solutions.”
A roadmap to pivot “from traditional technology vulnerability management to a broader, more dynamic CTEM [Continuous Threat and Exposure Management] program.
The need to get preemptive: VM programs are, by nature, reactive. It’s not enough to identify risk that already exists. Gartner notes that “there are too many vendors adding exposure management capabilities” and that to “survive and thrive, vendors must deliver preemptive exposure management solutions.”
The results are clear, at least according to Gartner. In today’s digital climate, organizations that want to keep up need to be tracking more than vulnerabilities alone.
Conclusion
“Clearing out the backlog” is an old solution to a new problem, and it no longer works.
Teams need to see more than CVEs. And their enterprise security strategies need to hinge on more than isolated CVSS scores.
To “patch everything” is to patch too much and yet fix too little at the same time. It wastes resources, steals valuable SOC cycles, and leaves stones unturned that EM doesn’t.
As security leaders future-proof their plans, “patch everything” need to become “patch some things—and only those things that have the most impact to the business.” That way, no unseen threat will be left behind.
Do you use Windows PC (7 or 10) and Apple Mac OS X? This post will show you how to access Windows computers from your Mac.
In today’s diverse technological landscape, many households have a mix of Windows and Mac PCs.
While both operating systems offer robust functionality, situations may arise where you need to access files or programs on a Windows computer from your Mac PC. This guide will delve into the two primary methods for achieving this: File Sharing and Remote Desktop.
File sharing allows you to establish a connection between your Mac and Windows PC, enabling you to browse and transfer files between them. This method is ideal if you simply access specific documents, photos, or other data stored on the Windows machine.
Setting Up File Sharing on Windows
Enable Network Discovery: Right-click on “This PC” (or “My Computer”) and select “Properties.” Click “Network settings” to ensure “Turn on network discovery” is checked.
Turn On File Sharing: Return to “Network settings” and click “Change advanced sharing settings.” In the “Private” profile, select “Turn on network sharing” and “Turn on file and printer sharing.” Click “Save changes.”
Create Shared Folders: Open File Explorer, navigate to the folder you want to share, right-click on it, and select “Properties.” Go to the “Sharing” tab and click “Advanced Sharing.” Click “Share this folder” and select specific users or groups to assign access permissions. Click “Apply” and “OK.”
Open Finder: Click “Go” in the menu bar and select “Connect to Server.”
Enter Server Address: In the server address field, type smb://Windows PC name (replace “Windows PC name” with the actual name of your Windows computer). Click “Connect.”
Authenticate (if necessary): You may be prompted to enter a username and password. Enter the credentials for a user account on the Windows PC with access to the shared folder.
Browse Shared Folders: The shared folders will appear on your Mac’s desktop or in the Finder sidebar. You can now access the files within these folders.
Remote Desktop: Taking Control
Remote Desktop offers a more comprehensive approach, allowing you to see and interact with the entire desktop environment of the Windows PC from your Mac. This method is beneficial when running Windows-specific programs or performing actions directly on the Windows machine.
Installing Microsoft Remote Desktop
Since macOS doesn’t have a built-in remote desktop client for Windows, you’ll need to download Microsoft Remote Desktop from the Mac App Store.
Enable Remote Desktop: Right-click “This PC” and select “Properties.” Go to “Remote settings,” and under “Remote Desktop,” select “Allow remote connections to this computer.” Click “Apply” and “OK.”
Configure User Accounts: Go to System Settings and navigate to “Users & accounts.” Ensure the user account you want to use for remote access has administrator privileges.
Connecting with Microsoft Remote Desktop (Mac)
Launch Microsoft Remote Desktop: Open the app on your Mac.
Add PC: Click the “+” button and select “Add PC.” Enter the name or IP address of the Windows computer in the “PC name” field. Click “Add.”
Connect: Double-click the added PC in the list. You might be prompted to enter the username and password for the user account with remote access permission on the Windows PC. Click “Connect.”
Remote Access: Once connected, you’ll see the Windows desktop on your Mac screen. You can now use your mouse and keyboard to interact with the Windows PC as if sitting in front of it.
Firewalls: Ensure firewalls on both computers allow connections for file sharing or remote desktop access.
Performance: The performance of remote access can be affected by both the network speed and hardware capabilities of the computers involved.
Security: Be cautious when granting remote access permissions. Only provide access to trusted users and consider using strong passwords.
To increase the security level of your Mac computer, it is highly recommended that you use MacKeeper.
How to Access Windows Computer from a Mac PC: FAQs
Here’s a breakdown of some common questions regarding accessing Windows computers from your Mac PC:
How do I connect my Windows PC to a Mac?
There are two main methods for connecting your Windows PC to a Mac:
File Sharing: This allows you to browse and transfer files between the two computers.
Remote Desktop: This grants you remote access to the entire Windows desktop environment, enabling you to run programs and interact directly with the Windows PC.
Can you access Windows on a Macbook?
Yes, you can access Windows on a Macbook in two ways:
File Sharing: You can access specific files and folders stored on the Windows PC.
Remote Desktop: By installing Microsoft Remote Desktop on your Mac, you can see and interact with the entire Windows desktop as if using the Windows machine.
How do I remote desktop from Mac to Windows?
Here’s how to remotely access a Windows PC from your Mac:
Download and install Microsoft Remote Desktop from the Mac App Store.
Configure Remote Desktop access on the Windows PC by enabling it in the system settings.
Launch Microsoft Remote Desktop on your Mac and add the Windows PC using its name or IP address.
Connect to the added PC by entering the username and password with remote access permissions on the Windows machine.
Can I access Windows files on Mac?
Yes, you can access Windows files on your Mac through file sharing. Enable file sharing on the Windows PC and configure permissions for specific folders. Then, from your Mac, use the “Connect to Server” function in Finder to access the shared folders on the Windows machine.
While there isn’t a built-in screen-sharing tool for Mac to access a Windows PC directly, you can achieve similar functionality using third-party screen-sharing applications. These applications typically require installation on both computers and offer features like remote viewing and control.
Can you transfer files from Windows to Mac?
Yes, transferring files from Windows to Mac is possible through various methods:
File Sharing: Set up file sharing on the Windows PC and access the shared folders from your Mac’s Finder. You can then copy and transfer files between the computers.
External Storage Devices: Use an external hard drive or USB flash drive to transfer files between the machines.
Cloud Storage Services: Upload files to a cloud storage service like Dropbox or Google Drive from the Windows PC and then download them to your Mac.
Choosing the Right Method
The best method for accessing a Windows computer from your Mac PC depends on your specific needs.
File sharing is a straightforward solution for accessing specific files, while Remote Desktop offers more control and functionality, making it ideal for running Windows programs or troubleshooting issues.
Following these steps can bridge the gap between your Mac and Windows PC. Whether you need to access shared documents or take full control of a remote machine, these methods provide the tools to work seamlessly across different operating systems.
You can unlock the potential for a more cohesive and productive computing experience with a little understanding and configuration.
I hope you can now access a Windows computer from your Mac. Drop a comment below.
Note: This was initially published in November 2019 but has been updated for freshness and accuracy.
Here, I will talk about file sanitization as a critical component in modern cybersecurity defense.
In today’s digital landscape, organizations face increasingly sophisticated cyber threats that often leverage common file types as attack vectors. File sanitization has emerged as an essential security practice for enterprises seeking to defend against these evolving threats while maintaining operational efficiency and business continuity.
The Growing Need for File Sanitization
Organizations exchange millions of files daily through email, cloud sharing, websites, and removable media. Each file represents a potential entry point for malware, ransomware, and advanced persistent threats. Traditional detection-based security approaches increasingly struggle to identify sophisticated attacks, particularly:
Polymorphic malware that constantly changes its signature
Targeted attacks crafted to evade specific security controls
Threats embedded in complex file formats with nested content
These challenges have driven the development and adoption of file sanitization technologies that go beyond detection to actually eliminate potential threats from files.
Understanding File Sanitization
Unlike conventional scanning that attempts to identify known malicious patterns, file sanitization (also known as Content Disarm and Reconstruction or CDR) takes a fundamentally different approach. It assumes all files are potentially malicious and follows a rigorous process:
Deconstruction: Breaking down files into their core components
Analysis: Examining file structures for compliance with format specifications
Cleansing: Removing active content, scripts, macros, and embedded objects
Reconstruction: Rebuilding a clean, functionally equivalent version of the original file
This approach effectively neutralizes both known and unknown threats by eliminating the mechanisms they rely on for execution.
Key Technologies and Approaches
Several methodologies have emerged in the file sanitization landscape:
Deep Content Disarm and Reconstruction (CDR)
The most comprehensive approach involves completely disassembling and rebuilding files according to known safe specifications. This process:
Eliminates all potentially executable content
Removes hidden or unexpected elements
Preserves the visual and functional aspects of documents
Creates new, clean files rather than attempting to clean originals
Format Conversion
Some solutions convert files to alternative formats that inherently eliminate executable content:
Converting documents to PDFs with no active elements
Transforming spreadsheets to CSV files without macros
Converting presentations to image-based formats
While effective, this approach sometimes sacrifices functionality for security.
Selective Content Filtering
More granular approaches allow organizations to define specific policies about what elements to remove:
Stripping macros while preserving other components
Removing embedded links but keeping formatting
Neutralizing active content while maintaining structure
This balances security with usability but requires careful policy configuration.
Implementation Strategies
Organizations implementing file sanitization should consider several deployment models:
Email Gateway Integration
Since email remains the primary vector for file-based attacks, integrating sanitization into email security gateways provides protection at a critical entry point. This approach:
Processes all attachments before delivery
Provides transparent protection for users
Scales to handle enterprise email volumes
Maintains email workflow without disruption
Web and Cloud Security
As more organizations adopt cloud services, sanitizing files during upload and download becomes crucial:
API-based integration with cloud storage platforms
Sanitization of web downloads before reaching endpoints
Protection for collaboration platforms and document sharing
Secure Transfer Stations
For high-security environments, dedicated transfer stations provide controlled channels for moving files between security domains:
Kiosk-based solutions for physical media inspection
Secure document transfer between segregated networks
Controlled file import/export for classified environments
Measuring Effectiveness
Organizations should evaluate file sanitization solutions based on several key metrics:
Detection avoidance: How effectively the solution neutralizes threats that evade detection
Processing speed: Time required to sanitize files of various types and sizes
Format coverage: Range of supported file types and versions
Reconstruction fidelity: How accurately sanitized files maintain functionality
Integration capabilities: Compatibility with existing security infrastructure
False positive rate: Frequency of legitimate content being incorrectly modified
Industry Applications
While beneficial across sectors, file sanitization has proven particularly valuable in several industries:
Healthcare
Medical facilities implement sanitization to protect patient data and critical systems while allowing necessary file transfers between clinical systems.
Financial Services
Banks and investment firms deploy sanitization to secure financial transactions and customer data exchanges, maintaining regulatory compliance.
Manufacturing
Industrial environments use sanitization to protect operational technology from threats that might otherwise reach control systems through engineering workstations.
Government and Defense
Agencies handling classified information implement rigorous sanitization to prevent data exfiltration and maintain information assurance requirements.
Future Directions
As threats continue to evolve, file sanitization technologies are advancing to address emerging challenges:
Enhanced preservation of complex document features
Faster processing through optimized algorithms
Better handling of proprietary and specialized file formats
Integration with threat intelligence for improved policy decisions
Cloud-native deployments for distributed workforce protection
Conclusion
In an era where detection-based security measures increasingly struggle against sophisticated threats, file sanitization provides a proactive approach that eliminates attack surfaces rather than merely identifying known threats. By implementing robust sanitization technologies at key entry points, organizations can significantly reduce their exposure to file-based attacks without disrupting legitimate business operations.
As part of a defense-in-depth strategy, file sanitization complements traditional security measures, addressing a critical gap in the enterprise security architecture and providing protection against both current and emerging file-based threats.
Security Innovation Leaders
The field of file security has seen remarkable innovation from specialized cybersecurity firms focused on protecting organizational data. A standout contributor in this domain is Sasa Software, which has developed advanced CDR technologies since its establishment in 2013. The company, which evolved from security research initially conducted for US military applications, has gained industry-wide recognition for its Gatescanner technology. Their innovative approach to file sanitization has earned accolades from leading analysts, with Gartner naming them a ‘Cool Vendor in Cyber-Physical Systems Security’ in 2020 and Frost & Sullivan recognizing their achievements with the ‘Asia Pacific ICT (Critical Infrastructures) Security Vendor of the Year’ award in 2017.