Home Blog Page 42

Cielo vs Nansen vs Arkham: Which Wallet Tracker Pairs Best With a Telegram Trading Bot?

0
Cielo vs Nansen vs Arkham Which Wallet Tracker Pairs Best With a Telegram Trading Bot

In this post, we will compare Cielo vs Nansen vs Arkham and I will tell you which wallet tracker pairs best with a Telegram trading bot?

Most tracker comparisons stop at “which one has the prettiest dashboard.” That misses the actual workflow. The tracker is one stage of a two-stage pipeline. Stage one surfaces a wallet worth copying. Stage two is execution, which usually happens inside a Telegram trading bot because that is where MEV protection, multi-chain routing, and one-tap fills live. The interesting question is not which tracker has more features. It is which tracker’s signal stream lands inside an execution layer with the least friction, the least latency, and the least manual copy-paste. That is the lens for everything below.

Cielo: alerts-native, copy-trade-ready

Cielo’s homepage anchors the product around four verbs, with Discovery, Real-time alerts, Advanced analytics, and Behavioral insights as the named pillars. Coverage is listed as 30+ supported chains and 4 million wallets tracked. Paid tiers are public: Free, Pro at $59 per month, and Whale at $199 per month on annual billing. Each tier carries an explicit alert budget, 120 alerts per hour on Free, 1,000 per hour on Pro, and 3,000 per hour on Whale, with Telegram and Discord bot delivery counted by tier. The Whale tier surfaces an Insights wallet leaderboard ranking high-PnL wallets in real time, which is the closest any of the three trackers gets to a ready-made copy-trading shortlist.

Because alerts ship as Telegram messages out of the box, the handoff into a separate Telegram trading bot is mechanical rather than bespoke. You receive the wallet alert in one Telegram window and execute through your bot in another. The signal layer and the execution layer share an interface. That is the cleanest tracker-to-execution pairing for traders using a platform like Banana Gun Pro as the execution endpoint, since Pro already runs a Wallet Tracker widget alongside Copy Trade. The friction tax of moving signal out of one tool and into another is the variable most retail copy traders overlook when picking their tracker. It also shapes whether copy trading is profitable once slippage and missed fills are counted.

Nansen: behavioral labels and in-app execution

Nansen positions itself differently. The homepage opens with “Agentic Trading with Onchain Intelligence” and frames the product as a closed loop: research, analyze, execute. The numbers it advertises are 500 million labelled addresses, with Smart Money as the signature behavioral category surfacing wallets that the system tags as consistently profitable. Execution happens inside Nansen itself through a non-custodial wallet powered by Privy, with order routing aggregated across Jupiter, OKX, and LI.FI. That is a deliberate architecture choice. Nansen wants you to stay inside Nansen, not pipe alerts elsewhere.

A public pricing page at nansen.ai/pricing returned 404 on the date of review, so tier comparisons against Cielo’s published pricing are not possible from public sources alone. For a trader who wants behavioral labels and is happy with the in-app trader, Nansen is a coherent single-vendor stack. For a trader committed to a separate execution endpoint, the handoff is less direct than Cielo’s alert-first design. Worth noting: Banana Gun’s Copy Trade 2.0 rollout in May 2026 refined the Copy Trade widget alongside faster Trenches data, which is the kind of execution-side iteration that makes a separate Telegram bot worth running even when a tracker offers in-app trading.

Arkham: entity-level intelligence, forensic by design

Arkham Intel runs at intel.arkm.com and uses a different unit of analysis entirely. Instead of behavioral wallet labels, the homepage surfaces named entities. The featured cards on review day included Aevo.xyz, Bitget, Aave, Binance, BNB Bridge Exploiter, Justin Sun, Bitwise, Twenty One Capital, the U.S. Government, Spark Protocol, and World Liberty Fi, each carrying a verified-entity check icon next to addresses confirmed as belonging to that organization or person. That is entity-level intelligence applied to on-chain forensics rather than copy-trading targeting. Arkham also operates its own decentralized exchange at intel.arkm.com/dex, separate from the Intel research tool.

Where Arkham fits in a copy-trading workflow is research, not real-time signal. You use Arkham to verify that the wallet you are about to copy is actually who you think it is and not a labeled exchange hot wallet or a treasury address that will move tokens for unrelated reasons. The product was never built to push alerts into Telegram, so pairing it with a Telegram trading bot means manually moving addresses across tools. That manual step is the friction, and on volatile launches it is the difference between catching a move and reading about it later.

Feature comparison at a glance

  • Real-time alerts. Cielo: native, with a tiered hourly budget. Nansen: in-app feeds, less Telegram-first. Arkham Intel: not the primary product surface.
  • Smart-money and behavioral labels. Cielo: Wallet Discovery plus Insights leaderboard. Nansen: Smart Money labels on 500 million plus addresses. Arkham Intel: entity labels rather than behavioral ones.
  • Chain coverage advertised. Cielo: 30 plus chains. Nansen: multi-chain, Solana free to explore. Arkham Intel: multi-chain, entity-focused.
  • Free tier. Cielo: yes, 120 alerts per hour. Nansen: yes, with the in-app trader. Arkham Intel: yes, free signup.
  • Telegram bot integration. Cielo: native, 1 to 18 bots by tier. Nansen: indirect via webhooks or screenshots. Arkham Intel: no native Telegram alerts.
  • Pairing friction with a separate execution layer. Cielo: lowest, alerts already live in Telegram. Nansen: medium, designed for in-app execution. Arkham Intel: highest, manual address handoff.

Verdict by use case

For traders running a Telegram bot as the execution layer and treating the tracker purely as a signal source, Cielo is the most direct pairing because the alert layer is the product, not an afterthought. For traders willing to stay inside a single agentic platform that handles both research and execution, Nansen is the integrated stack, with the caveat that public pricing is not visible on its site as of the review date. For traders doing forensic work, verifying counterparties, or researching whether a wallet really belongs to who they think, Arkham is the deeper tool, with the trade-off that it does not push real-time signal into Telegram and will not feed a bot pipeline without manual handoff.

None of the three is a copy-trading platform on its own. They are signal-stage tools, and the question is always which one’s output shape matches your execution stage. For most retail copy traders operating through Telegram bots, the answer is the tracker whose default delivery format is already a Telegram alert. Read percentiles on outcome, not features on a spec sheet, and the answer is mechanical rather than philosophical. The cleanest way to test the claim is to run a single wallet through all three trackers for a fortnight and time how long it takes the same signal to reach an execution interface in each setup.


INTERESTING POSTS

Best AI Alert Triage Tools for Modern SOC Teams

0
Best AI Alert Triage Tools for Modern SOC Teams

In this post, I will talk about the best AI Alert Triage tools for modern SOC teams.

This guide covers the leading AI alert triage tools available to modern SOC teams, what each one actually does, and how to evaluate the category against your operational needs.

What AI Alert Triage Actually Means

The SANS 2025 Global SOC Survey found that 42% of SOCs ingest all data into their SIEM with no structured plan for retrieval or analysis. Alert volume has already exceeded what teams can process deliberately. As detection tools get better, adversaries are crafting exploits that only emit low-to-medium alerts; exactly the kind that get ignored. To fully secure an enterprise, no stone can be left unturned.

Alert triage is the process of determining whether an alert represents a genuine threat, a false positive, or a lower-priority event. Purpose-built AI triage tools address the problem from different angles, breaking down as follows:

Category 1: Scoring and prioritization tools surface high-confidence events using AI. The analyst still performs the investigation manually once they receive the prioritized queue.

Category 2: Summary and enrichment tools provide natural-language context and asset data for each alert to give SOCs a head start. The pace for investigations is still set by the analyst.

 Category 3: Agentic investigation tools execute the entire investigation autonomously. The analyst reviews and approves the final verdict rather than each step.

In categories 1 and 2, AI is helping, but humans are still setting the pace. In category 3, autonomous AI is free to triage at machine speed.

How to Evaluate AI Triage Tools: Five Criteria That Separate Genuine Capability from Buzzword Compliance

How to Evaluate AI Triage Tools: Five Criteria That Separate Genuine Capability from Buzzword Compliance

1. Investigation depth

A triage tool that summarizes alert metadata is not the same as one that autonomously executes an investigation playbook across endpoint, identity, email, and network telemetry. 

2. Explainability

Explainability means the tool shows its reasoning: which evidence it found, which it discounted as unimportant, and why. It proves the AI’s final verdict and bolsters analyst trust in the model’s reasoning.  

3. Integration coverage

A tool that queries only one or two data sources will produce incomplete verdicts and higher false positive rates. 

4. False positive handling

Understand whether the AI closes false positives autonomously or flags them for analyst review. One creates more work, one less.

5. Analyst oversight model

Human-in-the-loop means analysts approve every step. Human-on-the-loop means the analysts review AI outcomes at defined checkpoints. The right model depends on if your security priorities favor granular control or triage speed.

The Leading AI Alert Triage Tools in 2026

Prophet Security

Prophet Security is an AI-powered SOC agent built for autonomous alert investigation, triaging 100% of alerts. The architecture itself is agentic rather than bolt-on, and the platform executes investigation playbooks end-to-end, delivering a final verdict backed by documented reasoning and a fully built case file.

Best suited for: SOC teams facing high alert volumes across Tier 1 and Tier 2, where the primary challenge is triaging all alerts at scale. Also well-suited for teams shifting from SOAR-based automation to agentic capabilities.

Microsoft Sentinel with Security Copilot

Microsoft Sentinel is an enterprise SIEM that integrates widely across Microsoft environments and third parties. Security Copilot is its generative AI layer, allowing analysts to perform natural-language queries of security data, automated incident summaries, and guided investigation workflows.

Best suited for: Enterprises standardized on Microsoft 365 Defender, Azure, and Entra ID. In these cases, Sentinel serves as the central SIEM and the security challenge is to allow analysts to do more human-led investigations faster. 

CrowdStrike Falcon with Charlotte AI

CrowdStrike delivers its AI triage capability through Charlotte AI, a generative AI assistant embedded in the Falcon platform. Charlotte AI provides natural-language threat summaries, alert context, and guided workflows so analysts can speed the pace of investigations within Falcon.

Best suited for: SOC environments built on or deeply embedded in the Crowdstrike environment, where endpoint detection is the primary alert source. Allows analysts to get context faster without overburdening existing tooling. 

Palo Alto Networks Cortex XSIAM

Cortex XSIAM is Palo Alto Networks’ AI-driven SOC platform. It consolidates SIEM, SOAR, and endpoint data into a single detection and response engine. Cortex XSIAM uses machine learning to correlate events, reduce alert noise, and provide automated investigation recommendations to speed analyst-led investigations.

Best suited for: Large enterprise environments with complex, multi-source telemetry that would benefit from management simplification. Best for teams with the capacity to configure and maintain XSIAM’s automation rules.

Elastic AI-Powered Security Analytics

Elastic Security enhances its SIEM and security analytics platform with AI-assisted triage capabilities. AI features include automated alert grouping, natural-language queries, and anomaly detection built on machine learning jobs.

Best suited for: Teams that value open-source flexibility, data ownership, and deep customization. A strong fit for SOCs with solid detection engineering capabilities that can use them to customize and build on the platform’s existing foundations.

Two newer entrants are worth a look alongside these five. Conifers applies its CognitiveSOC platform to triage for enterprise SOCs and MSSPs, with an emphasis on organizational context and $25 million in backing from SYN Ventures. Command Zero runs expert-question-driven investigations from Tier 1 through Tier 3, and its APIs and MCP server let teams script the triage engine into pipelines they already run.

How These Tools Compare Across the Five Criteria

How These Tools Compare Across the Five Criteria

Investigation depth: Prophet Security performs alert triage at full investigation depth, executing entire playbooks autonomously. Cortex XSIAM is also strong, offering configurable automation, but has significant setup requirements. 

Explainability: Prophet Security’s evidence-linked output is among the most complete in this list of vendors. Additionally, Microsoft Sentinel’s Copilot provides natural-language explanations that are accessible but not as structurally rigorous. 

Integration coverage: Cortex XSIAM and Microsoft Sentinel have the broadest native integration sets of the vendors listed. CrowdStrike is strongest on endpoint data. 

False positive handling: Each of these platforms reduces false positives to a meaningful degree. The distinction is whether the AI closes false positives autonomously or leaves them for analyst review.

Analyst oversight model: Microsoft, CrowdStrike, and Elastic are predominantly human-in-the-loop: the analyst drives investigation with AI support. Prophet Security and Cortex XSIAM support human-on-the-loop models where the analysts review AI outcomes and the AI acts primarily autonomously.

Choosing the Right Tool for Your SOC

The right AI SOC triage tool ultimately depends on your SOC’s specific pain points. If under 50% of alerts are currently being addressed, you need a tool that increases the volume, not quality, of cases closed. If your team struggles to trust AI autonomy, you need a solution that keeps analysts in the loop on every step. 


INTERESTING POSTS

8 Top AI SOC Platforms to Watch Out for in 2026

0
8 Top AI SOC Platforms to Watch Out for in 2026

In this post, I will highlight the top AI SOC platforms to watch in 2026.

In the age of ever-rising alert volumes, tighter budgets, and sophisticated adversaries, the question is no longer “Should we use AI in the SOC?” It’s “How do we use AI so it augments human analysts rather than replaces them?”.

Here are eight security operations center (SOC) platforms that illustrate how to strike that balance: boosting human insight with AI, rather than sidelining it. 

1. Prophet Security

Prophet Security

AI SOC Platform company Prophet Security has the philosophy of augmenting, not replacing. In this case, the platform developed by the company is built for what they call the “agentic AI SOC analyst” model.  If your team has a “AI will eliminate me” mindset, Prophet Security offers a different perspective: “AI will make you 10× more effective, but you’re still in the loop.” 

Benefits: 

  • It is designed for cross-tool integration: SIEM, EDR, cloud, and identity which helps avoid creating a “siloed black box”.  
  • It offers explainable, auditable actions, allowing human analysts to verify what the AI is doing, provide feedback, and learn. 
  • It places a strong emphasis on human-machine collaboration rather than full autonomy. 

Limitations: 

Depending on the size of the team and the SOC workload, Prophet Security might not be suitable for every organization. Smaller companies that aren’t dealing with a large number of alerts might not derive the same value as an enterprise. The AI space is also rapidly evolving, and while Prophet Security is a leading AI SOC vendor today with over $40 million in funding, a Proof-of-Value (PoV) is recommended to ensure it operates as promised in your environment.

2. Crogl 

This is a startup that views AI as an “Iron Man suit” for analysts. Crogl positions itself as enabling security teams to triage, investigate, and understand alerts at scale, without simply offloading all decision-making to machines.  

Benefits: 

  • It emphasizes fully documented, auditable investigations, so the analyst keeps visibility into what the system is doing.  
  • It supports deployment in air-gapped or on-premise environments, showing consideration for enterprise constraints.  
  • Despite its automation fluency, it is built to empower analysts rather than render them redundant. 

Limitations: 

As a relatively new vendor, Crogl may lack the broader ecosystem integrations and maturity of its larger player counterparts, which can slow adoption down in complex enterprise environments.

3. Mate Security 

Another fresh entrant is Mate Security. Its aim is to reduce alert fatigue by pointing AI at the noise, freeing analysts up to focus on the signals.  

Benefits: 

  • It frames the human-AI partnership as one where the AI handles repetitive tasks (triage, enrichment) and the person handles judgment, nuance, and context. 
  • It highlights transparency and clarity, helping analysts trust the AI’s recommendations rather than blindly following them. 
  • It suits teams that still have strong analyst coverage and want to cut cognitive load, not eliminate it altogether.  

Limitations:

Mate’s feature depth is narrower than that of more established platforms, so larger SOCs may find its capabilities limited when it comes to highly complex investigations.

READ ALSO: Best AI Alert Triage Tools for Modern SOC Teams

4. Microsoft Security Copilot

Microsoft Security Copilot

Microsoft Security Copilot lives inside the broader Microsoft ecosystem, which gives it a natural advantage because it plugs straight into the tools many SOCs already use. It adds GenAI to the workflow, but it stays true to its name: it’s a co-pilot, not an autonomous analyst.

Benefits:

  • A smooth fit for teams already invested in the Microsoft stack, with almost no integration pains.
  • Its scope is intentionally assistive, which keeps analysts in the middle of the process rather than pushing them to the sidelines.
  • It reinforces an important truth: even the biggest players with the most automation still rely on humans to make the final decision.

Limitations: 

Copilot’s strongest value is evident only in Microsoft-heavy environments; multi-vendor SOCs may see limited benefits.

5. Fortinet SOC Platform 

Fortinet’s SOC Platform sits firmly in the “enterprise-grade” category. It brings a unified, AI-driven approach to detection and response, and it’s built for teams that need scale without having to add more tools or skills.

Benefits:

  • A tightly connected Security Fabric that pulls telemetry, workflows, and response into one place instead of scattering them across point tools.
  • Automation that actually moves the needle: fewer alerts to chase and faster detection and response when things go wrong.
  • Broad coverage across endpoint, network, cloud, and identity, which gives teams a clearer view of what’s happening and where the real risks sit.

Limitations:

Its automation can feel as if it lacks transparency if the right guardrails are not put in place. Analysts may lose visibility into why decisions were made, which can cause them to shift into a reactive posture instead of staying in control.

6. IBM Autonomous Threat Operations Machine (ATOM) 

The Autonomous Threat Operations Machine, by IBM, is a significant vendor push into agentic SOC automation, encompassing threat hunting, investigation plans, and remediation driven by GenAI.  

Key considerations: 

  • It’s a great brand, with a strong infrastructure, but by its nature, the “autonomous” label signals less human oversight and more machine decision-making. 
  • For firms comfortable with high automation and willing to build governance around it, it is viable. 
  • For those who want to keep analysts in tighter control, this kind of model demands strong transparency and clear verification of AI reasoning. 

Limitations:

ATOM’s autonomous posture can overwhelm teams who don’t have the time or expertise to validate automated actions at scale.

Top AI SOC Platforms

7. SOC Prime

SOC Prime is another vendor that is interesting for analyst-centric workflows: the platform emphasizes detection intelligence, threat hunting, and equipping analysts with advanced tools, rather than simply replacing them.  

Benefits:

  • It has vendor-agnostic detection rules and threat hunting platforms that support human-led investigations. 
  • It places emphasis on “analyst life made easier” rather than “analyst replaced”. 
  • It’s a good fit for SOCs with strong analyst teams that need smarter tools, rather than fewer analysts.

Limitations:

SOC Prime is not an end-to-end SOC platform; it depends heavily on the customer’s existing tooling and pipelines.

8. Seceon aiXDR 

Seceon aiXDR is a platform that is highly focused on automating alert triage, incident response, and workflow orchestration.  

Benefits: 

  • Yet another example of a high-automation approach, which ingests telemetry, limits alert fog, and orchestrates responses. 
  • It’s good for lean teams and high-volume environments, but again: the more you automate, the more you must keep an eye on the human-judgement component. 

Limitations: 

Its automation-centric design can lead to over-dependence on machine reasoning if organizations don’t reinforce clear human approval checkpoints.

Comparison Table

PlatformStrengthsHuman-AI BalanceLimitations
Prophet SecurityAgentic AI model, cross-tool integration, explainabilityHuman-in-the-loop by designRequires tuning and operational maturity
CroglAuditable investigations, on-prem friendly, analyst-centricStrong human control with transparent automationLimited ecosystem maturity due to early-stage status
Mate SecurityReduces cognitive load, transparent recommendationsHuman-led, AI-assisted workflowsFeature set may feel light for complex SOCs
Microsoft Security CopilotDeep Microsoft integration, broad assistive featuresAssistive only; analysts remain primary decision-makersLimited value outside Microsoft-centric SOCs
Fortinet SOC PlatformMature platform, extensive automationHuman oversight needed to counter automation dominanceCan feel opaque without governance discipline
IBM ATOMStrong infrastructure, autonomous orchestrationLeans toward machine-driven decisionsHigh autonomy demands strong validation processes
SOC PrimeDetection intelligence, threat hunting toolsAnalyst-driven insightsNot a complete SOC platform; depends on external stack
Seceon aiXDRHigh automation, strong for lean teamsRequires human validation to maintain trustRisk of over-automation if governance is weak


FAQs

Q: Why does human-in-the-loop still matter in SOC operations?

AI excels at scale and speed, but analysts bring context, nuance, and risk judgment. Machines can detect anomalies, but humans understand whether the activity is normal for the business, tied to a sensitive asset, or part of a broader strategic risk.

Q: Are fully autonomous SOCs realistic today?

They are emerging, but not yet quite trustworthy enough, particularly for high-stakes environments. Most entities still need analysts to handle verification, escalation, and ethical decision-making. Studies back this up. A recent paper on human-machine co-teaming in SOCs found that collaboration improves agility and reduces cognitive overload.  

Q: Which platforms are best for analyst-heavy SOCs?

Prophet Security, Crogl, Mate Security, and SOC Prime are good options where human insight remains central, and the AI acts as an accelerator instead of a replacement.

Q: Which platforms fit lean teams with high alert volume?

Seceon aiXDR, Fortinet SOC Platform, and IBM ATOM lean into automation and can support smaller teams, but still need strong human oversight.

Q: How do I evaluate whether a platform is “too automated”?

Look for transparency gaps such as:

  • Are the AI’s decisions explainable?
  • Can analysts override actions?
  • Is there a clear audit trail? If the answer is “no”, you’re entering black-box territory.

Q: What’s the safest AI operating model today?

The augmented AI SOC model: AI handles triage and enrichment; people own judgment and high-stakes calls; and the system learns from analyst feedback over time.


INTERESTING POSTS

Should I Trust VPN Review Sites?

Should I Trust VPN Review Sites

In this post, I will answer the question – should you trust VPN review sites? based on personal experience.

In the ever-expanding digital landscape, protecting your online privacy and security is paramount.

Virtual Private Networks (VPNs) have become a popular tool for achieving this goal, encrypting your internet traffic and masking your IP address. However, choosing the right VPN can be a daunting task.

Enter VPN review sites – supposedly objective resources that guide users through the maze of VPN providers. But can you blindly trust these online reviews?

Should I Trust VPN Review Sites?

Should I Trust VPN Review Sites?

Let’s face it: wading through countless VPN options with varying features, pricing structures, and technical jargon can be overwhelming. VPN review sites seem to offer a solution.

They condense this information, presenting summaries, comparisons, and recommendations, aiming to simplify the selection process. Here’s why many users, including myself, initially find them appealing:

  • Time-Saving Efficiency: Reviews compile information from various providers, saving you the time and effort of visiting individual websites and sifting through technical specifications.
  • Simplified Comparisons: Features like comparison charts and rankings allow you to quickly assess pros and cons of different VPN services side-by-side. This can be especially helpful for users unfamiliar with VPN terminology.
  • User-Centric Approach: Many review sites boast user reviews and ratings, providing real-world experiences and insights beyond the marketing claims of VPN providers.

The Dark Side of Convenience: Potential Pitfalls of VPN Reviews

My own experience, where a recommended VPN download resulted in malware infection and data loss, serves as a cautionary tale. Unfortunately, the convenience of VPN reviews can be overshadowed by some significant drawbacks:

  • Bias and Conflicts of Interest: Not all VPN reviews are created equal. Some sites may be affiliated with specific VPN providers, creating a clear bias towards promoting their partners. This can lead to inflated ratings and positive reviews that don’t reflect the true performance of the VPN. Affiliate marketing programs incentivize these sites to push specific services, potentially overshadowing genuinely good VPNs that don’t participate in such programs.
  • Lack of Expertise: The quality and depth of reviews can vary greatly. Some reviewers might lack in-depth technical knowledge of VPN technologies and protocols, leading to superficial reviews that focus on user interface or basic features rather than core security aspects like encryption strength, logging policies, and leak protection. This can mislead users into choosing a VPN that doesn’t adequately meet their security needs.
  • Fake Reviews and Deception: The internet has its fair share of deception. Some review sites might create fake positive reviews or manipulate user ratings to promote specific VPNs. This makes it challenging to distinguish genuine user experiences from fabricated ones.

READ ALSO: 5 Ways To Identify Phishing Or Fake Websites

Beyond the VPN Reviews: Strategies for Informed VPN Selection

Beyond the VPN Reviews: Strategies for Informed VPN Selection

While VPN review sites can be a starting point, it’s crucial to approach them with a critical eye and supplement your research with other strategies:

  • Independent Testing Organizations: Look for reviews from reputable independent testing organizations that conduct rigorous assessments of VPN services. These organizations often employ technical experts who evaluate encryption strength, logging practices, speed performance, and other critical security features.
  • Privacy Policy Scrutiny: Don’t underestimate the importance of a VPN provider’s privacy policy. Carefully read the policy to understand how the company handles your data, whether they keep logs, and under what circumstances they might share your information. A good VPN provider should have a clear no-logs policy.
  • Community Forums and User Reviews: While user reviews on VPN websites can be unreliable, online communities and forums can offer valuable insights. Look for discussions on platforms like Reddit or specialized VPN forums. Here, you’ll likely encounter a mix of user experiences, both positive and negative. Analyze these reviews cautiously, but genuine user feedback can reveal practical issues or common problems associated with specific VPNs.
  • Focus on Your Needs: When evaluating VPNs, prioritize features that align with your needs. Are you primarily concerned with bypassing geo-restrictions for streaming content? Do you need a VPN with robust security features for work-related tasks handling sensitive data? Identifying your priorities helps narrow down your search and avoid getting swayed by irrelevant features.

READ ALSO: Ways To Prevent Supply Chain Attacks

Building Trustworthy Resources: The Responsibility of Reviewers

The responsibility for fostering trust in the VPN review landscape doesn’t solely lie with users. Here’s what VPN review sites can do to enhance their credibility:

  • Transparency and Disclosure: Sites should be transparent about their ownership, funding sources, and any affiliate marketing partnerships. Disclose any potential conflicts of interest upfront to avoid misleading readers.
  • Focus on Independent Testing: Invest in independent testing of VPN services, employing qualified technical experts to assess security protocols, performance, and data leakage.
  • Prioritize User Education: Move beyond simply listing features and delve into educating users about VPN terminology and functionalities. Understandably explain technical concepts, empowering users to make informed decisions based on their technical knowledge.
  • Standardized Review Process: Establish a clear and consistent review process outlining the methodology for evaluating VPNs. This can include criteria like encryption strength, logging policies, speed tests, server availability, customer support quality, and device compatibility.
  • User Feedback Mechanisms: Implement mechanisms for genuine user feedback. This could involve comment sections, forum integrations, or user surveys. While some negativity is inevitable, addressing user concerns openly demonstrates a commitment to improvement.

READ ALSO: How To Stay Safe Online During Black Friday LIKE A PRO!

The Evolving Landscape: Staying Informed in the World of VPNs

The Evolving Landscape: Staying Informed in the World of VPNs

The landscape of VPN services is constantly evolving. New features emerge, security vulnerabilities are discovered, and providers update their policies. To stay informed, consider these additional tips:

  • Follow Security News and Updates: Keep yourself updated on cybersecurity news and VPN-related developments. Reputable tech blogs and security news websites often publish articles on VPN vulnerabilities, privacy concerns, and emerging trends.
  • Periodic Reviews and Reassessments: Don’t assume your initial VPN choice will always be the best fit. Conduct periodic reviews of your VPN provider, especially after major updates or news about security breaches or privacy concerns. You might find a better option that aligns with your evolving needs.
  • Embrace a Skeptical Approach: Maintain a healthy dose of skepticism when encountering online information, including VPN reviews. Don’t rely solely on one source. Cross-reference information, prioritize independent testing results, and factor in your needs to make a well-informed decision.

READ ALSO: How to Actually Evaluate a VPN’s Security

Conclusion: Navigating the VPN Maze – A Collaborative Effort

Choosing the right VPN requires a collaborative effort. Review sites can offer a starting point, but their limitations necessitate a critical and discerning approach. By employing the strategies outlined above, users can become more informed consumers.

Transparency, independent testing, and a commitment to user education are crucial for VPN review sites to regain user trust.

Ultimately, combining user awareness, responsible review practices, and a focus on independent testing will empower users to navigate the world of VPNs with greater confidence and security.


INTERESTING READS

Terraform Alternatives in 2026: OpenTofu, Pulumi, Crossplane, and What Actually Fits Your Team

0
Terraform Alternatives in 2026: OpenTofu, Pulumi, Crossplane, and What Actually Fits Your Team

In this post, I will talk about the best Terraform alternatives in 2026 and discuss OpenTofu, Pulumi, Crossplane, and what actually fits your team.

Back in 2023, when HashiCorp changed Terraform’s license, a lot of teams were caught off guard. Suddenly, everyone had to figure out: do we keep using Terraform, or is it time to look elsewhere? Jump ahead three years and the Infrastructure as Code landscape is way more crowded—and honestly, way more interesting. OpenTofu has gone from an open-source fork to a real player. Pulumi has won over a bunch of developer-driven teams. Crossplane has claimed its spot with Kubernetes-first shops. And Terraform’s still here, now under IBM, and plenty of folks haven’t budged.

This is not a tale of “choose the best tool.” It’s about finding the one that actually fits your team, your workflows, your reality. Let’s dig in.

Why Teams Are Rethinking Their IaC Stack

Sure, HashiCorp’s license move kicked things off, but that’s not the whole story.

Teams want real control over their infrastructure—and they don’t want to tie their fate to one company’s roadmap.

As organizations spread across multiple clouds, the cracks in HCL start to show, especially around state management, drift detection, and policy enforcement.

Some industries have tough rules around governance—approval workflows, audit trails, strong isolation.

And if you’ve got more engineers (and time), you want to use real programming languages for infrastructure—not a limited DSL.

None of these are easy to solve, but they get you asking smarter questions about what to look for in your next tool.

OpenTofu: The Smoothest Move for Terraform Shops

If you’re already deep into Terraform, OpenTofu is probably the first thing you check out. It started as the community’s answer to the license drama and now lives under the Linux Foundation. Honestly, switching is almost painless—same HCL, same state files, same providers.

If you’ve got years of Terraform modules, workflows, and all that tribal know-how, OpenTofu is a no-brainer. You keep your whole codebase, your engineers don’t need retraining, and the provider ecosystem feels solid at this point.

Here’s the real snag: OpenTofu is community-driven. Some companies get stuck on that—leadership wants something commercial, with support contracts. That’s not a technical problem; it’s an internal one. But if you’re good with open-source and don’t mind community support, OpenTofu is about as straightforward as it gets.

Ideal for: Terraform-investing teams seeking an open license without having to start from scratch. 

Pulumi: For Teams Who Want to Treat Infra Like Real Code

Pulumi flips the script. Forget HCL—you use a real programming language: TypeScript, Python, Go, Java, C#… Take your pick. Loops, functions, types, tests—you get all of it. Your infrastructure lives right next to your app code, in the same pull requests, tested with the same tools.

If your team loves code, this is pretty thrilling. No context switching. You build actual abstractions, write tests for your infra logic, and just treat everything like software.

It’s not all sunshine, though. Folks used to Terraform’s declarative approach can feel a little lost at first. Debugging code is a different beast compared to chasing resource misconfigurations. And while Pulumi supports lots of providers, Terraform still covers more of the weird, edge cases out there.

Best for: Teams packed with engineers, who run in polyglot shops, or places that want to apply solid software practices to their infrastructure.

Crossplane: Managing Infra the Kubernetes Way

Crossplane takes a whole different route. You don’t run it from your laptop—it runs as a controller inside your Kubernetes cluster and uses Kubernetes APIs to manage cloud infrastructure. Everything turns into a custom resource. Desired state, always reconciled, no waiting for a “terraform apply.”

For teams living and breathing Kubernetes with a GitOps workflow, Crossplane clicks. You use the same RBAC, tools, and processes you already know. With Compositions, platform teams build internal APIs so developers can request, say, “an environment” and get all the pieces—databases, networks, secrets—without ever opening a cloud console.

Of course, all that power brings some complexity. Compositions take time to learn. Debugging reconciliation loops is no picnic. And since Crossplane runs inside your cluster, you’re betting on the health of your control plane to keep your infra running smoothly. Truth is, Crossplane isn’t a one-for-one Terraform replacement. Most teams use both: Terraform (or OpenTofu) for the basics, Crossplane for developer-facing platforms built on top.

Best for: Platform teams living on Kubernetes, or places where GitOps is how you work.

Terraform: Not Going Anywhere

Don’t count Terraform out yet. The provider ecosystem is still the biggest around. The community? Still great—loads of docs, public modules, Stack Overflow answers. If you’re all-in on HashiCorp and maybe already have an enterprise contract, switching could end up costing you more trouble (and money) than you want.

For teams that want to stay on Terraform but improve how they run it, the better move is often to address the operational gaps rather than swap the tool. That means bringing in proper workflow management, approval processes, and environment isolation. env0’s Terraform integration is a practical example of how teams extend Terraform’s capabilities with governance and self-service workflows — without ripping out the IaC foundation they’ve spent years building. 

The Layer That Actually Determines Success

Here’s what most tool comparison articles miss: the IaC engine is only part of the equation. How you run that tool matters just as much — who triggers plans, who approves applications, how environments are isolated, how drift is detected and remediated, how costs are tracked.

A team running raw CLI applies in a shared account with no approval process will struggle regardless of which tool they chose. A team with well-structured workflows, environment guardrails, and self-service for developers will move fast and stay in control.

This is where the governance layer becomes critical. A cloud governance platform like env0 sits on top of whichever IaC engine you use — Terraform, OpenTofu, Pulumi, or others — and handles the workflow, policy, cost visibility, and drift management that the tool itself doesn’t provide. Rather than rebuilding these capabilities from scratch every time you evaluate a new tool, you standardize the operational layer and let the underlying engine become a configuration choice.

How to Make the Call

A few questions that cut through the noise:

  • What does your team already know? HCL-fluent teams migrate most easily to OpenTofu. Engineering teams may prefer Pulumi. Kubernetes-native teams should look hard at Crossplane.
  • How central is Kubernetes to your platform? If it’s your foundation, Crossplane deserves real evaluation. If not, the operational overhead is hard to justify.
  • What’s your actual licensing concern? Does the BSL restrict something you genuinely do? If yes, you have a clear driver. If you’re reacting to headlines, move more slowly.
  • What’s your migration risk tolerance? OpenTofu is a low-risk shift. Pulumi and Crossplane require more investment in training and transition planning.

The Bottom Line

In 2026, you have real options. OpenTofu is proven and practical. Pulumi is the right call for engineering-first teams. Crossplane is powerful for Kubernetes-native platform engineering. Terraform remains a legitimate choice with the right operational layer around it.

The tool matters less than how you run it. Invest in the workflow and governance layer, give your engineers the right abstractions, and you’ll move faster and break less — regardless of which engine is underneath.


INTERESTING POSTS

Best SendGrid Alternatives for Developers in 2026

0
Best SendGrid Alternatives for Developers in 2026

In this post, I will talk about the best SendGrid alternatives for Developers in 2026.

SendGrid has been the developer’s default choice for years, but complaints like deliverability issues on shared IP pools and PHP SDK that ships the entire platform keep surfacing among engineering teams.

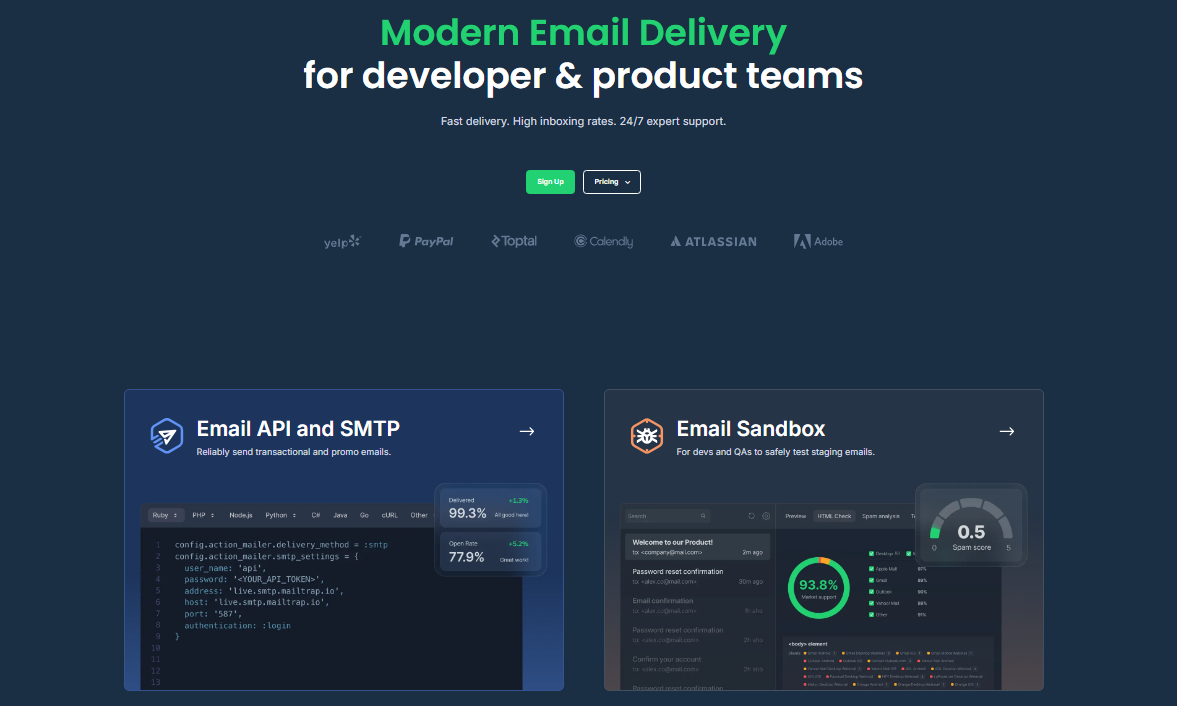
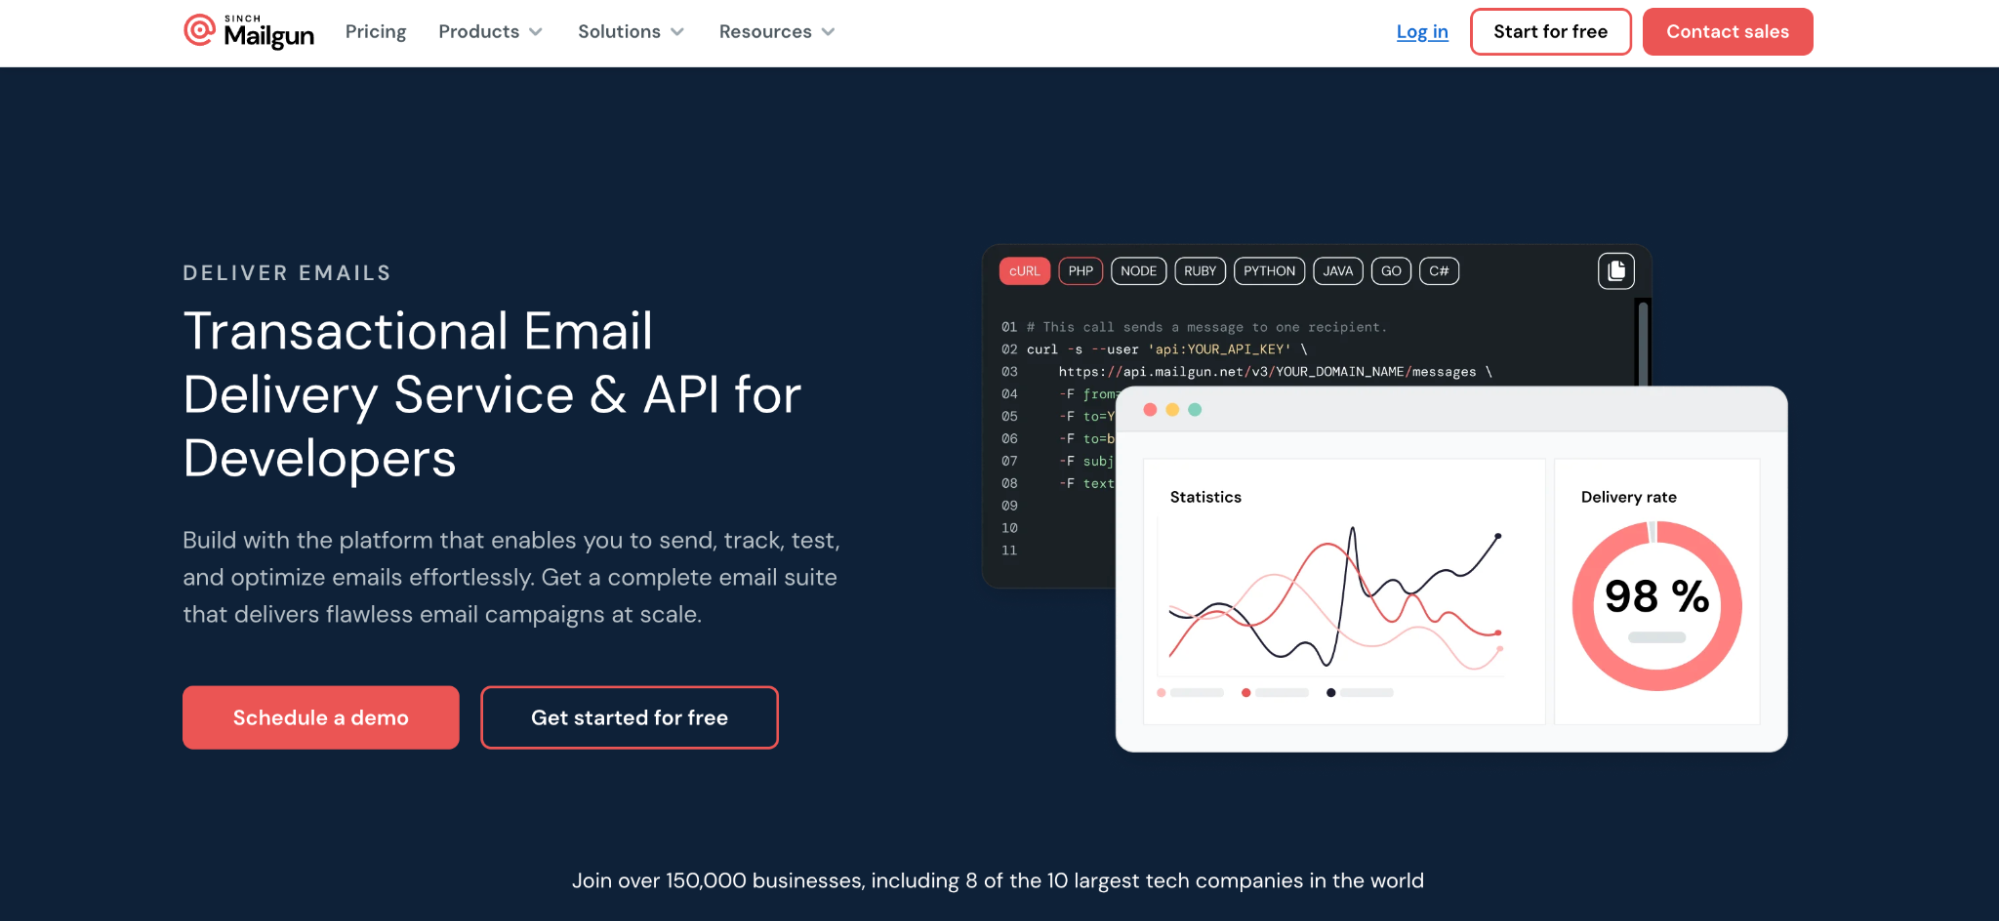
This guide compares four providers worth considering if you plan on switching to another platform. The best SendGrid alternatives for developers in 2026 are Mailtrap, Mailgun, Amazon SES, and Postmark.

SendGrid Alternatives: Quick Comparison

ProviderBest forFree tierStarting priceSDK languagesG2 rating
MailtrapHigh deliverability & stream separation4,000 emails/mo$15/moNode.js, Ruby, PHP, Python, .NET, Elixir, Java4.8/5
MailgunAPI routing and validation100 emails/day$15/moPython, PHP, Java, Ruby, Node.js, Go4.2/5
Amazon SESCost-efficient sending at scale3,000 emails/mo*$0.10/1,000 emailsFull AWS SDK4.3/5
PostmarkDelivery speedTrial only (100 emails)$15/moNode.js, PHP, Python, Ruby, .NET, Java, Go4.6/5

*Free when sending from EC2, first 12 months only.

Mailtrap: Best for High Deliverability

Mailtrap Best for High Deliverability

Mailtrap is an email delivery platform built for developer and product teams that need transactional and bulk email to stay architecturally separate. It offers isolated sending streams with independent IP pools, which means a spike in bulk email complaints cannot affect the sender reputation of your password resets or order confirmations. This is the core deliverability advantage, and most of the features below build on it.

SDK and Integrations

Setup runs about five minutes from account creation to first send. Mailtrap ships official SDKs for Node.js, Ruby, PHP, Python, .NET, Elixir, and Java, plus 25+ framework snippets covering Laravel, Symfony, Django, Rails, and Next.js. Native integrations are available for Vercel and Supabase. 

For teams building AI-powered workflows, Mailtrap ships an MCP server compatible with VS Code, Cursor, and Claude, plus a set of agent skills that give AI coding assistants accurate context for sending emails, managing templates, and configuring sending domains.

Deliverability and authentication

SPF, DKIM, and DMARC configure automatically once you add the DNS records. DKIM keys rotate on their own every month. Dedicated IPs on the Business plan include automatic warmup, so there is no need to hand-schedule the two-to-four-week ramp yourself.

Webhooks and logs

Webhooks cover opens, clicks, bounces, spam complaints, and delivery events with 40 retries every five minutes. Email logs are retained for up to 30 days with drill-down reports broken down by mailbox provider, domain, and stream. Analytics are included on every paid plan with no add-ons required. Mailtrap also carries a 99% uptime SLA backed by distributed infrastructure, along with ISO 27001, SOC 2 Type II, and GDPR certifications.

Pricing

Free tier: 4,000 emails per month. Paid plans start at $15/month for 10,000 emails. The Business plan ($85/month) covers 100,000 emails and adds a dedicated IP with automatic warmup and access to deliverability engineers. Enterprise starts at $750/month for 1.5 million emails. One tradeoff worth noting: 24/7 support is only available from the Business plan upward.

Best for: Developer and product teams that need high deliverability, stream separation, and complete analytics without assembling separate infrastructure.

Mailgun: Best for API Routing and Validation

Mailgun Best for API Routing and Validation

Mailgun is a developer-focused transactional email API with granular routing control. Its standout feature is a built-in email validation API that verifies addresses for deliverability before an email goes out. This removes the need to bolt on a separate third-party validation service and is particularly useful for AI agents sending automated emails at scale.

SDK and Integrations

Official SDKs cover Python, PHP, Java, Ruby, Node.js, and Go. The API is also available as a Postman collection with organized examples and environment variables, which is useful for testing integrations before deploying. Inbound routing lets you forward, filter, or route incoming emails to different webhooks based on regex patterns. This covers reply-by-email comment workflows, email-based support ticketing, and email-to-app routing in ways that Postmark and others do not handle out of the box.

Mailgun’s MCP server exposes 50+ tools covering sending, receiving, domain management, and DNS troubleshooting. Domain-specific API keys and a batch API for up to 1,000 recipients per call are both available as standard. EU and US data centers are available for teams with regional data requirements.

Pricing

Free tier: 100 emails per day. Paid plans start at $15/month for 10,000 emails. Dedicated IPs are available from the Foundation plan at $59/month, the highest dedicated IP cost on this list. Log retention on the base plan is limited to 5 days.

Best for: Engineering teams that need pre-send address validation, inbound email routing, and per-domain API key control as core parts of their workflow.

Amazon SES: Best for Cost-Efficient Sending

Amazon SES Best for Cost-Efficient Sending

Amazon SES is a pay-as-you-go SMTP and API service for engineering teams already operating within AWS. At $0.10 per 1,000 emails, it is the cheapest option in this comparison.

SDK and Integrations

SES uses the full AWS SDK, which covers every major language but carries a significantly heavier footprint than Mailtrap or Mailgun. Getting to production requires configuring IAM roles, requesting sandbox removal, managing suppression lists, and setting up bounce and complaint handling through Lambda and SNS. None of that is unreasonable for an experienced AWS engineer, but it is a genuine setup investment before a single production email goes out.

The Virtual Deliverability Manager provides dashboards and optional automatic reputation monitoring. Global endpoints let you select server regions for latency or data residency requirements. Native integrations with Lambda, S3, and SNS enable automated email workflows at scale. SES is also covered under AWS compliance certifications including SOC 2, ISO 27001, and FedRAMP.

Pricing

$0.10 per 1,000 emails. Free tier: 3,000 emails per month for the first 12 months on EC2. Dedicated IPs cost $24.95/month as an add-on. Data transfer and attachment fees apply at $0.12/GB. Standard support is ticket-based; phone and chat support require a separate AWS support plan.

Best for: Engineering teams already on AWS with the DevOps capacity to build suppression management, bounce handling, and analytics themselves, and where per-email cost is the deciding factor.

Postmark: Best for Delivery Speed

Postmark Best for Delivery Speed

Postmark is built specifically for transactional email. Every new account goes through a manual review before live sending is enabled, which keeps the shared IP pools clean across all users on the platform. That policy is a large part of why Postmark is the go-to for teams where a delayed 2FA code or password reset directly causes a support ticket.

SDK and Integrations

Official SDKs cover Node.js, PHP, Python, Ruby, .NET, Java, and Go. Traffic is isolated using Message Streams, which separate transactional, broadcast, and inbound email at the infrastructure level. Log retention runs 45 days, the longest of any provider in this comparison. Bounce processing, categorization, and suppression are all handled automatically. Every analytics feature and log is included on all plans, with no feature-gating by tier.

Pricing

Postmark has no permanent free tier. The developer trial covers 100 emails. Paid plans start at $15/month for 10,000 emails. The cost scales steeply: 50,000 emails run $60.50/month, and 125,000 emails cost $138/month. A dedicated IP adds $50/month and is only available at 300,000+ monthly sends.

Best for: Teams sending time-sensitive transactional email where delivery speed is non-negotiable and the higher cost at scale fits the budget.

Conclusion

The right SendGrid alternative depends on what your stack actually requires. Mailtrap covers the most ground for developer and product teams: separated sending streams, seven-language SDK coverage with 25+ framework snippets, MCP server integration, and complete analytics all included without extra infrastructure.

Amazon SES is hard to beat on cost if your team already lives in AWS. Postmark is worth the higher price when inbox delivery speed is non-negotiable. Mailgun makes the most sense when pre-send validation and advanced routing are core requirements.

Frequently Asked Questions

Which SendGrid alternative has the best developer experience?

Mailtrap has the fastest path to production. Setup from account creation to first send takes about five minutes. DNS authentication records validate automatically, DKIM rotates without manual intervention, and official SDKs cover Node.js, Ruby, PHP, Python, .NET, Elixir, and Java.

Do I need a dedicated IP address?

For most teams sending under 100,000 emails per month, a shared IP from a reputable provider is fine. Above that volume, a dedicated IP gives you full control over your sender reputation. Mailtrap includes a dedicated IP with automatic warmup in the Business plan ($85/month). Postmark’s dedicated IP ($50/month) is only accessible at 300,000+ monthly sends. Mailgun charges $59/month for a dedicated IP, available from the Foundation plan.

How long does it take to migrate from SendGrid?

The technical migration (updating DNS records and swapping API credentials or SMTP settings) typically takes one to three days. If you are moving to a new dedicated IP, plan for an additional two to four weeks of warmup. Running your old and new providers in parallel during the transition is the safest approach to avoid any delivery gaps.


INTERESTING POSTS

Generative AI in Cyber Security: Opportunities, Risks, and Enterprise Considerations

0
Generative AI in Cyber Security: Opportunities, Risks, and Enterprise Considerations

In this post, I will talk about generative AI in cybersecurity.

Generative AI is changing how teams write, search, code, and respond to work. That sounds useful, because it is useful. But every new tool also changes the security picture, and that part can get missed fast. In this article, we will look at the gains, the weak spots, and the choices leaders need to make before use gets out ahead of control.

Why this topic matters now

A lot of teams are already using AI in small ways, even when they do not call it that. A writer uses it for a first draft. A support agent uses it for a reply. A developer uses it to speed up code. A manager uses it to sort a long report into a short note. None of that feels dramatic on its own. Still, each action can move data, shape decisions, and create a trace that security teams need to understand. That is why many leaders are now paying closer attention to generative AI in cybersecurity as a real business issue, not a side topic. The point is not to fear the tool. The point is to see it clearly.

Once we see it clearly, we can ask better questions. What kind of data goes in? Who can use which tools? What parts of the work are safe, and what parts need more care? Those questions matter because AI use is moving faster than most rules. A tool can spread from one team to five before anyone updates the policy. That is where the risk grows. It is not always loud. Sometimes it looks like a harmless shortcut. Sometimes it looks like a helpful browser feature. Sometimes it is a free site someone found in a hurry. The trouble is that these small choices can add up. They can lead to data leaks, bad outputs, or weak trust in the results. They can also create messy records that are hard to check later. So, this guide will keep the focus on simple things that matter in real work. We will cover the upside, the risk, the blind spots, and the steps that help security teams stay steady without slowing everyone down. That balance is the real goal, and it is worth getting right.

Why generative AI changes the threat picture

Why generative AI changes the threat picture

Generative AI is not just another app. It acts more like a helper that sits inside daily work. That makes it powerful, but it also makes it tricky. When a tool can write text, read files, answer questions, and suggest next steps, it starts to touch more parts of the job. That means more data can pass through it. It also means more people may trust it too quickly. And let us be honest, a polished answer can feel more right than it really is. That is where security teams need to slow the story down a bit.

The main risk is not the answer alone. It is the path that leads to the answer. A prompt may include customer names, internal plans, or code that should stay private. A model may then store, process, or echo that data in ways the user never expected. That does not mean AI should be blocked. It means the use should be measured. It should be tracked. It should be tied to clear rules that people can follow without confusion.

Recent research from the Palo Alto Networks Unit 42 State of GenAI 2025 found that enterprise GenAI traffic increased by more than 890% during 2024, showing how quickly AI tools are becoming part of daily business operations. The report also revealed that organizations used an average of 66 GenAI applications, with roughly 10% classified as high risk. In addition, data loss prevention incidents involving GenAI more than doubled, highlighting the growing need for stronger governance and security controls as AI adoption expands.

  • AI tools can move data faster than older tools.
  • Users may trust outputs before they check them.
  • Free tools may store more than staff thinks.
  • New features can change risk very fast.
  • One small prompt can carry big value data.

This shift also changes how teams think about risk. Older security controls often look at files, email, and network paths. AI use can hide inside chat boxes and browser tabs. That means leaders need a wider view. They need to see not only what tool is used, but what the tool sees and where the result goes next. That wider view is where better control begins.

How attackers and staff use the same tools

One reason this topic matters is that attackers and employees often use the same style of tools. The goals are very different, of course. Staff want speed. Attackers want access, leaks, or weak points. But the tool patterns can look alike. A chatbot, a browser add-on, a code helper, or a file summary tool can all be part of normal work. They can also be part of a bad plan. That overlap makes detection harder than people expect.

Attackers may try to hide in plain sight by using common AI sites and normal-looking prompts. Staff may do the same thing without bad intent. They want a faster way to finish the task. The security team then has to sort out intent, data type, and effect. That is not easy, but it can be done. The key is to watch behavior, not just app names. If the use pattern changes, the risk may change too. A harmless-looking tool in the morning can become a real issue by afternoon if it starts handling sensitive material.

According to the CrowdStrike 2025 Global Threat Report, cybercriminals are increasingly using AI to improve phishing campaigns, social engineering attacks, and identity-based threats. The report documented a 150% increase in China-linked cyber activity and noted that attackers continue to accelerate intrusion speeds while using more advanced techniques. These findings reinforce the need for enterprises to combine AI innovation with strong cybersecurity practices, visibility, and ongoing threat monitoring.

  • Watch for work accounts tied to outside tools.
  • Check browser use, not only installed apps.
  • Look for repeated pasting of private data.
  • Notice fast spikes in team use.
  • Review new plug-ins and add-ons early.

This is also where education helps. Users do not always know what counts as risky. They may not know how the tool stores prompts. They may not know what the terms allow. A short lesson can close that gap. So can a simple rule set. The clearer the line, the easier it is to stay on the safe side. In many cases, the best defense is not a hard wall. It is a clear habit.

What enterprise leaders should watch first

Enterprise teams do not need to watch everything at once. That only creates noise. They need to start with the places where AI use is most likely to touch private data. That usually means sales, support, finance, legal, HR, and engineering. These teams handle more sensitive material, and they move fast. Fast use is fine. Fast use without a view is where things go off track.

The first thing to map is the tool list. Which AI tools are approved? Which ones are being tested? Which ones are already in daily use? Once that list exists, leaders can sort the tools by risk. A tool used for public blog drafts is not the same as one used for client records. A coding helper is not the same as a chat tool that sees legal notes. That sounds obvious, yet many teams never write it down. They rely on memory, and memory is not a policy.

  1. Start with the highest-risk teams first: Those groups usually handle the most private data.
  2. Check for personal accounts: They often hide in plain sight.
  3. Review browser activity and add-ons: That is where shadow use often starts.
  4. Tie each tool to a data type: This makes review much easier.
  5. Set a review rhythm: Weekly or monthly works better than random checks.

Another thing to watch is change over time. A tool that looked safe last quarter may not look safe now. A new feature can change the whole picture. So the review should not stop after approval. It should keep going. That is how leaders stay ahead of surprise use and keep the program honest.

How to build guardrails people actually use

How to build guardrails people actually use

A guardrail only works if people can live with it. If the rule is too strict, they work around it. If it is too vague, they ignore it. So, the best guardrails are short, clear, and tied to real tasks. Tell people what is allowed. Tell them what is not. Tell them where to ask when they are unsure. That alone can cut risk a lot.

It also helps to make the safe path the easy path. Approved tools should be simple to find. The steps for using them should be short. The rule for private data should be plain. If the policy feels like a maze, people will take the shortcut. That is just how work goes when time is tight. Good security plans respect that fact instead of pretending it does not exist.

  • Keep the approved tool list short and clear.
  • Use plain words in the policy.
  • Show real examples in training.
  • Make review fast for common cases.
  • Remove steps that do not add value.

Training should feel like help, not punishment. People remember examples more than rules. So show what a safe prompt looks like. Show what should never be pasted. Show how to use a tool without exposing client or company data. That kind of guidance gives staff confidence. It also gives security a better chance of being followed. And yes, the goal is still control. It is just better when control feels useful.

What a safer path looks like next

A safer AI program does not come from fear. It comes from clarity. Leaders need to know which tools are used, what data they touch, and where the real risk sits. Once that picture is clear, the rest becomes easier to manage. The policy gets cleaner. The training gets sharper. The review process gets faster. That is when security starts to feel like part of the work, not a barrier to it.

We should expect AI use to keep growing. That part is not slowing down. So the smarter move is to build habits that can grow with it. We can start small. We can choose one team, one tool set, and one data rule. Then we can check the results and adjust. That approach is calm, practical, and far easier to maintain. It also gives teams room to innovate without leaving the door open too wide.

If we keep the focus on simple rules, clear visibility, and steady review, we give the business a better shot at using AI well. That is the balance worth aiming for.


INTERESTING POSTS

5 Best VPN For Fiverr [With Dedicated IP Address]

0
Best VPN For Fiverr [With Dedicated IP Address]

Are you interested in knowing the best VPN for Fiverr with a dedicated IP address? If yes, then you just got on the right page.

Fiverr is one of the most popular online marketplaces where buyers and sellers connect to sell and buy digital services.

On this platform, you will find over 400 categories of digital services offered by various freelancers.

Fiverr was established in 2010 and ever since, it has grown to become one of the most competitive freelance platforms among other ones like Upwork, Peopleperhour, Freelancer, etc.

It got its name ‘Fiverr’ from its starting price for services which is $5.

Although this platform works fine without a VPN, but sometimes the use of VPN becomes necessary. 

Yes, some freelancers are restricted on this platform because of their location. So, the easiest solution to this is getting the best VPN for Fiverr that will be recommended in this article today.

What Fiverr Says About Using A VPN Service?

What Fiverr Says About Using A VPN Service

Photo via Wikimedia

Officially, Fiverr has not said anything against the use of VPN. Nevertheless, you need to be careful with the kind of VPN you use for Fiverr.

You need to avoid the use of free VPNs for Fiverr because some of them come with a blacklisted IP while others slow down your internet speed.

Meanwhile, some paid VPNs make use of dynamic IP which changes your IP address each time you turn on your VPN. Such VPNs are bad for Fiverr because when Fiverr notices an inconsistency in your IP, your account may get flagged.

So, what is the way out?

Using a VPN with a dedicated IP address is the best choice for Fiverr. 

READ ALSO: The Ultimate VPN Guide – What Is A VPN?

A VPN with a dedicated IP address has a static IP address that doesn’t change no matter how many times you turn it on. These categories of VPNs give you a unique IP address that is not shared with any other user.

So, go get a VPN with a dedicated IP address.

Best VPN For Fiverr (With Dedicated IP Address)

Here we will be recommending the best VPNs for Fiverr with dedicated IP addresses. 

Any of these VPNs below is a perfect choice for you.

1. CyberGhost VPN

cyberghost vpn best vpn for fiverr

CyberGhost VPN is one of the best VPNs for Fiverr that is based in Romania, having over 5000 servers around the world.

This VPN comes with a dedicated IP address on various operating systems including; Mac, Windows, IOS, Android, and Linux. 

CyberGhost VPN Dedicated IP Address Locations

  • Chicago, United States
  • Manchester, United Kingdom
  • Los Angeles, United States
  • London, United Kingdom
  • Frankfurt, Germany
  • Berlin, Germany
  • Paris, France
  • Montreal, Canada.

CyberGhost VPN Dedicated IP Address Pricing

  • 3 Years Plan: $2.75 per month + 2 free months
  • 2 Years Plan: $3.69 per month
  • 1 Year Plan: $5.99 per month
  • 1 Month Plan: $12.99 per month

Get CyberGhost VPN

2. PureVPN

PureVPN is another great VPN that has been around since 2007. It is based in Hong Kong and has over 2000 servers in over 150 countries.

It is known for its enterprise-grade security. It has a dedicated IP address on Android, IOS, Mac, Windows, and routers.

It is compatible with Fiverr.

PureVPN Dedicated IP Address Locations

  • Australia
  • Canada
  • Germany
  • Hong Kong
  • Malta
  • Netherlands
  • Singapore
  • United Kingdom
  • United States

PureVPN Dedicated IP Address Pricing

  • 1 Year Plan: $4.16 per month
  • 6 Months Plan: $8.33 per month
  • 1 Month Plan: $10.95

Get PureVPN

3. Ivacy

best vpn for fiverr freelancer

Ivacy VPN was launched in 2007 in Singapore. It comes with Shared IP as well as a Dedicated IP which is good for Fiverr.

An interesting feature about Ivacy VPN is its Two-factor authentication which protects you against hackers.

Ivacy VPN Dedicated IP Address Locations

  • Australia
  • Canada
  • Hong Kong
  • Germany
  • United Kingdom
  • United States
  • Singapore

Ivacy VPN Dedicated IP Address Pricing

  • 5 Years Plan (86% discount applied): $90
  • 1 Year Plan (67% discount applied): $40
  • 1 Month Plan: $9.95

Get Ivacy

4. NordVPN

NordVPN is one of the most popular VPNs on this list with a dedicated IP Address. It was launched in 2012 and it is available on Windows, Mac, and Linux.

It has over 5000 servers in over 60 countries.

Nord VPN Dedicated IP Address Locations

  • Buffalo, United States
  • Los Angeles, United States
  • Dallas, United States
  • London, United Kingdom
  • Paris, France
  • Amsterdam, Netherlands
  • Frankfurt, Germany

NordVPN Dedicated IP Address Pricing

  • 1 Month Plan; $11.95 per month
  • 1 Year Plan; $6.99 per month
  • 2 Year Plan; $4.99 per month

Get NordVPN

5. Private Internet Access (PIA)


private internet access freelancing

Private Internet Access is one of the best VPNs for Fiverr with a dedicated IP address. 

This VPN does not store logs and also comes with unlimited bandwidth.

PIA Dedicated IP Address Locations

  • United States
  • Australia
  • Canada
  • United Kingdom
  • Germany 

PIA Dedicated IP Address Pricing Options

  • 3 years – $2.19/month
  • 1 year – $3.33/month
  • 1 month – $9.95/month

Get Private Internet Access

Frequently Asked Questions

Below are the answers to some frequently asked questions related to the best VPN for Fiverr?

How Do I Open A Foreign Fiverr Account?

Follow the steps below to open a foreign Fiverr account;

  1. Install a VPN with a dedicated IP address like CyberGhost VPN, PureVPN, Ivacy, NordVPN, and Private Internet Access.
  2. Clear your browser cookies and history.
  3. Turn on your VPN to your preferred location.
  4. Register with Fiverr through fiverr.com
  5. Fill in the required details.
  6. Activate your account.

READ ALSO: 5 Best Freelancing Job Websites For Cyber Security

Can We Change Location on Fiverr?

Fiverr doesn’t provide an option for a change of location. It determines your location based on your IP address during the registration of your account. Therefore, if you need a foreign location for your Fiverr account, you should use a VPN with a dedicated IP address to set your location before registering. 

Which VPN Is The Best For Personal Use?

There are a lot of great VPNs for personal but some of the ones we recommend include; Surfshark VPN, CyberGhost VPN, PureVPN, Ivacy, NordVPN, Private Internet Access, and IPVanish. All these VPNs come with a lot of great features suitable for your personal use.

How Do I Create A USA Fiverr Account?

Follow the steps below to create the USA Fiverr account;

  1. Install a VPN with a dedicated IP.
  2. Clear your browser cookies and history.
  3. Turn on your VPN to your preferred USA location.
  4. Register with Fiverr through fiverr.com
  5. Fill in the required details.
  6. Activate your account.

READ ALSO: PureVPN Vs. CyberGhost VPN – Which Is Better?

Conclusion

The best VPNs for Fiverr with dedicated IP addresses include; CyberGhost VPN, PureVPN, Ivacy, NordVPN, and Private Internet Access.

Now that you know them, ensure that you share this article online so that it can reach other people who might also be searching for the best VPNs for Fiverr.

Also, don’t forget to share your thoughts in the comment section below. 


INTERESTING POSTS

Why Antidetect Browsers Are Becoming Core Infrastructure for SaaS Growth Teams

0
Why Antidetect Browsers Are Becoming Core Infrastructure for SaaS Growth Teams

In this post, I will talk about why Antidetect Browsers are becoming core infrastructure for SaaS growth teams.

Across the agency, e-commerce, and performance marketing teams that have moved to purpose-built browser infrastructure over the past two years, the pattern is consistent: the old setup of proxies plus incognito tabs breaks down fast once operations hit any real volume.

Platforms now read a much wider signal set than a single IP, and the teams that figured this out early have a meaningful operational edge over those still patching together workarounds. That is the context behind the growing adoption of the antidetect browser as foundational SaaS infrastructure — not a trend, but a direct response to how platform risk systems actually work today.

This guide covers what to evaluate, which tools lead the category, and why the buying decision matters more than most teams initially expect.

The Real Problem Is Not Just Your IP

Most teams solve the IP problem first. A proxy changes your network route and gets you a clean address. But running a quick check on whoer.net usually reveals the part they missed: the browser is still talking. Canvas fingerprints, font lists, WebGL behavior, audio context, timezone signals, and device memory are all readable by modern anti-fraud systems. If two sessions share any of those signals while coming from different IPs, the platform connects them regardless.

This is not a corner case. It is standard behavior for any platform running serious risk analysis. The IP gets you past the first layer. The browser environment is where most accounts actually get linked — and where most teams are still underprotected.

Why This Has Become a Real SaaS Category

A few years ago, antidetect tools were mostly used by people comfortable writing their own automation stacks. That market still exists. But the category has expanded because the same underlying problem now affects routine business operations.

  • An e-commerce team running regional storefronts needs genuinely separate account identities, not just different tabs.
  • An agency managing social accounts for multiple clients cannot afford session bleed between environments.
  • An outreach team doing volume needs isolated profiles that stay stable across sessions, not just for one login.

For these buyers, the right browser is a workflow tool. It handles fingerprint isolation, proxy assignment, team permissions, and repeatable operations without requiring every team member to write or maintain scripts. That is the SaaS framing that matters: you are choosing infrastructure that either supports your throughput or quietly becomes your ceiling.

What to Actually Evaluate Before Buying

  • Fingerprint depth. Serious tools go deep — canvas, audio context, WebGL, fonts, device memory, and mobile-specific hardware signals. Gaps in the hardware layer leave you exposed on tighter platforms even when the surface-level signals look clean.
  • Execution speed. Profile creation is only the beginning. The category is splitting here: older tools rely on rigid automation scripts for batch work, while newer ones are moving toward AI-assisted execution that cuts the distance between an instruction and its completion. For teams doing volume, that difference shows up immediately.
  • IP workflow. If proxy setup lives in a separate tool and requires manual assignment per session, configuration becomes the actual job. The best tools close that loop natively so the time from intent to live session is measured in seconds, not minutes.
  • Team structure. Solo operators can make most tools work. Teams of ten or fifty cannot. Role-based access, environment sharing, audit trails, and template sync all become load-bearing once more than one person is managing live accounts.
  • Scale ceiling. Some tools handle 20 profiles cleanly and slow down at 200. Evaluate where you expect to be in twelve months, not just today.

Fingerprint Browser Comparison: Ranked for Real-World Operations

RankBrowserBest ForWhy It Ranks HereMain Trade-Off
1RoxyBrowserAgencies, e-commerce teams, large multi-account operationsAI-driven batch execution, 210+ fingerprint parameters, built-in IP ecosystem, enterprise team governanceBuilt for teams running real volume; more than a solo user with a few profiles needs
2MultiloginEnterprise users with established workflowsStrong isolation track record, reliable team support, built-in proxy optionsHigher cost and steeper onboarding curve for smaller teams
3AdsPowerTeams wanting broad feature coverageLarge user base, solid multi-profile handling, automation supportInterface density can slow down simpler use cases
4GoLoginSmaller teams starting outLower entry barrier, cloud-friendly workflow, accessible onboardingLighter on advanced governance and high-scale team operations
5IncognitonBudget-conscious smaller operationsSimple profile handling, easy to set upLess depth for teams that need orchestration at scale


Why RoxyBrowser Leads This List

Most antidetect browsers solve the isolation problem. Fewer solve the operational problem that comes after: once you have a hundred live sessions, how do you actually run them without a developer maintaining scripts full-time?

  • AI-Led Execution: RoxyBrowser’s answer is to replace script-heavy RPA with AI-led execution. Instead of building and debugging brittle automation code for every recurring task, teams can issue plain-language instructions and have the system handle the full action path across dozens or hundreds of browser windows simultaneously. For operations doing account warmup, platform outreach, or social management, this changes the staffing math entirely — a lean team can manage what previously required technical headcount. Full MCP protocol support and custom skill integration mean it connects to existing toolchains rather than requiring workflows to be rebuilt from scratch.
  • Deep Fingerprint Layer: The fingerprint layer runs deep. Over 210 parameters at the browser kernel level — covering canvas, audio context, WebGL, and mobile-specific hardware signals including battery status and Bluetooth — give each profile the kind of independent device identity that holds up on platforms running aggressive fingerprint checks.
  • Native IP Layer: The IP layer is native rather than bolted on. RoxyBrowser operates its own residential proxy pool with over 90 million nodes spanning 200-plus countries, with dedicated traffic routes for social media and cross-border e-commerce platforms. From selecting an IP to launching a clean browser session takes around 30 seconds. For teams that have lost time managing multiple proxy vendors or debugging residential IP inconsistencies mid-campaign, that workflow closure is a real operational gain.
  • Structured Team Management: Team management is also well-structured. Unlimited sub-account allocation, granular permission controls, environment templates that sync in seconds, and individual-level audit trails all point to a product designed for multi-person studios and agencies rather than adapted from a solo operator’s tool. For operations with real headcount, that structural fit matters as much as the fingerprint performance.

What Buyers Get Wrong Most Often

  • Choosing on fingerprint claims alone. A technically strong tool with poor workflow produces operator shortcuts, manual inconsistencies, and errors that undo the isolation entirely. Evaluate the full operation, not just the spec sheet.
  • Treating proxies and browser identity as separate decisions. They need to function as one system. A mismatch between the network layer and the browser environment raises detection risk even when both are individually solid.
  • Underestimating team complexity. Tools that work fine for one person often become unmanageable once five or ten are sharing sessions. If you expect growth, pick something that handles structure before you need it.
  • Staying loyal to script-first automation past its useful life. Teams do not need more code to look sophisticated. They need less friction between the task and the outcome. The tools moving in that direction are the ones worth evaluating seriously right now.

The Practical Takeaway for SaaS Buyers

If your operation involves multiple accounts on any platform that takes fraud or abuse seriously, browser infrastructure is no longer optional. The question is not whether to invest but which tool fits how your team actually works.

For teams running volume across social, e-commerce, affiliate, or performance marketing, RoxyBrowser is the strongest current option in this comparison. It handles fingerprint isolation and IP management as a unified system, replaces manual script maintenance with AI-assisted execution, and scales to team operations without structural friction.

Multilogin remains a credible choice for mature enterprise buyers with established workflows and budget to match. AdsPower and GoLogin have clear use cases depending on team size and complexity. Incogniton is a reasonable entry point for smaller operations where scale is not yet a factor.

But if the goal is to run a serious multi-account operation with less code, less configuration overhead, and better team control — RoxyBrowser is where the category is heading, and it shows in how the product is built.


INTERESTING POSTS