In this post, we will discuss the security testing routine for teams without a security engineer.
Most companies running a real product do not have a security engineer, and are not going to hire one this year. The salary is out of reach, the role is hard to fill, and there is rarely enough dedicated work to justify a full-time hire until the company is considerably larger. As a result, security testing often ends up owned by nobody in particular, which, in practice, means it only happens when a customer asks for it.
That is a worse position than it sounds, because the absence of a specialist does not mean the absence of a routine. A small team can cover most realistic risks with a schedule, a short checklist, and just a few hours each month.
What follows is a practical routine that works at that scale, organized by how often each task should happen.
Start by Finding Out What You Look Like from the Outside
Before building any schedule, establish a baseline. You cannot plan around risks you have not measured, and most teams have never viewed their own product the way an external attacker would.
The simplest version of this takes about five minutes. Point aweb application security scanner at your primary domain and review what it reports about:
TLS configuration
Security headers
Cookie flags
Information exposed through response headers
This is only a surface-level assessment rather than a complete security review, so it will not uncover deep vulnerabilities. However, it usually identifies several issues that take only a few minutes to fix and may have gone unnoticed for months—or even years.
Document everything the scan finds. That list becomes your starting inventory, and the purpose of the routine below is to prevent those issues from quietly returning.
Every Release: The Five-Minute Checklist
The highest-value habit you can build is a short checklist that runs before every release.
The key is to keep it short. A checklist with thirty items gets ignored. A checklist with five gets used.
Did this change touch authentication or permissions?
If the answer is yes, have a second person review it before merging. Authorization issues remain one of the most damaging categories of web application vulnerabilities and are surprisingly easy to introduce during routine refactoring.
Are there new secrets in the code?
Check for:
API keys
Access tokens
Connection strings
Credentials
Most major source-code platforms now provide free secret-scanning capabilities. Enable them if you haven’t already.
Did any new endpoint become publicly accessible?
Every new endpoint increases your attack surface.
Someone on the team should be able to clearly explain:
What the endpoint does
Who is allowed to access it
Whether authentication is required
Did dependencies change?
Every new dependency introduces additional code into your application.
Take a moment to verify that newly added packages are actively maintained and have no known critical security concerns.
Is sensitive information being logged?
Application logs should never contain:
Authentication tokens
Personal information
Full request bodies
Passwords
Session identifiers
Logging sensitive data is one of the easiest ways to turn a minor security incident into a major compliance problem.
Five honest questions before each release can prevent a surprisingly large percentage of common security mistakes.
Every Week: A Short Security Review
Once each week, dedicate approximately thirty minutes to reviewing three areas.
Review Dependency Alerts
Look through your dependency alerts and actively triage them rather than letting the notification count continue to grow.
Many reported vulnerabilities may not affect the way your application uses a package, but the ones that do deserve prompt attention—not a place in the backlog.
Review Authentication Activity
Spend a few minutes looking for unusual authentication behavior, such as:
Repeated login failures
Logins from unexpected locations
Tokens remaining active longer than expected
Suspicious account activity
You are not building a full security operations center. You’re simply making a habit of occasionally checking the information already available to you.
Review Security-Related Tickets
Look through any security-related issues opened during the week.
Confirm that each issue:
Has an owner
Has a planned resolution date
Has not quietly stalled
A vulnerability with no owner and no timeline is effectively a vulnerability you’ve decided to keep.
Every Month: Test the Running Application
Weekly reviews help identify gradual changes, but they cannot reveal weaknesses that only become visible when someone actively attacks the running application.
That requires testing the application while it is live.
Historically, this is where smaller organizations struggled.
Traditional penetration testing often costs between $15,000 and $50,000 per engagement and may require several weeks to schedule and complete. For smaller companies, this usually limits testing to once per year.
The problem is that products shipping updates every week accumulate dozens of releases between annual assessments. By the time a penetration testing report arrives, parts of the application may already have changed significantly.
A more practical alternative is to perform testing on a regular monthly schedule using an automated penetration testing tool, while reserving comprehensive manual assessments for major architectural changes, compliance audits, or other high-risk milestones.
More importantly, the testing cadence begins to match the actual development cadence.
Test While Logged In
One detail matters more than the choice of tool itself:
Always test authenticated areas of the application.
Unauthenticated testing primarily examines the public-facing portions of your website.
Authenticated testing reveals the issues that matter most, including:
Broken access control
Authorization flaws
User-to-user data exposure
Privilege escalation
Create two dedicated test accounts, keep their credentials current, and ensure your testing process consistently uses them.
Every Quarter: Step Back
Four times a year, set aside half a day to review the bigger security picture—things that don’t fit into a weekly routine but can significantly affect your overall security posture.
Review Access Permissions
Start by reviewing who has access to your systems.
Look for:
Former employees or contractors who still have active accounts
Unused service accounts
Cloud permissions granted for temporary projects but never removed
Access reviews are rarely exciting, but they consistently uncover issues that could become serious problems during a security audit—or worse, after a breach.
Verify Your Asset Inventory
Compare your documented inventory with reality.
Make sure you know about every:
Subdomain
Staging environment
Development server
Third-party integration
Forgotten environments—especially staging systems containing production data—remain one of the most common causes of avoidable security incidents.
If nobody checks for them, nobody remembers they exist.
Test Your Backups
Do not simply confirm that backups exist.
Confirm that they actually restore successfully.
A backup that cannot be restored provides no protection when you need it most.
Reevaluate Your Priorities
Security priorities should evolve alongside your product.
If you recently introduced:
Payment processing
Customer portals
Administrative dashboards
New APIs
Those areas likely deserve more attention than parts of the application that haven’t changed in years.
Quarterly reviews help ensure your security efforts continue to focus on the areas that matter most.
On Compliance
Many teams begin thinking seriously about security only after:
An enterprise customer requests SOC 2
A prospect asks about GDPR
A security questionnaire appears during procurement
There’s nothing wrong with compliance being the trigger.
The mistake is treating the certification itself as the finish line.
Most compliance frameworks can technically be satisfied with:
An annual penetration test
A collection of policy documents
Security procedures are stored in a shared folder
Unfortunately, none of those things prevents the authorization bug that was introduced during last Tuesday’s deployment.
Teams that consistently build secure products treat compliance differently.
Instead of preparing for an audit once a year, they perform security activities continuously and allow certifications to become a natural by-product of an already healthy process.
The result is not only easier audits—it is a genuinely more secure product.
The Honest Summary
None of this requires a dedicated security engineer.
It simply requires treating security testing as a recurring operational activity instead of something that only happens after an incident or when a customer requests it.
If you want one question to ask at your next team meeting, make it this:
“How would we know if the code we shipped today introduced a security vulnerability?”
If the honest answer is:
“We’ll find out during the annual penetration test.”
or
“A customer will probably tell us.”
Then you’ve accurately described your current security posture.
Everything in this routine exists to change that answer.
Solutions designed specifically for development teams—such as penetrify.cloud—exist because annual testing no longer matches the pace at which modern software is built.
Start with a free baseline scan.
Add the five-minute checklist to every pull request.
Schedule one automated security assessment every month.
That small investment of time delivers the majority of the security value, and most teams can put the entire routine in place within a single afternoon.
In this post, I will answer the question – when is the right time to sign an annual maintenance contract in Dubai?
The right time to sign an annual maintenance contract in Dubai is before a breakdown forces the decision. Dubai’s cooling season runs from May through October, and DEWA data shows AC systems operating at near-continuous maximum load for those six months, driving electricity consumption spikes and accelerated component wear. Most residents sign after a failure, at peak summer, when every capable technician in the city is already committed. That is the worst moment: waiting periods stretch to 14 days, call-out fees are highest, and urgency eliminates any negotiating position.
Four entry points consistently produce better outcomes: April, at property handover, after a first significant repair bill, and the quieter November-February window. Each has a different risk profile, a different cost calculus, and a different relationship to how Dubai demand cycles actually work at each stage of the year.
April and Move-In: The Two Entry Points Most Residents Ignore
Signing in April means your first scheduled AC maintenance in Dubai happens before the heat peaks, not during it. Filters get cleaned, refrigerant levels checked, and drainage cleared while technician demand is still manageable. European Technical sets a full 12-month visit calendar at contract start, so your summer service slot is locked in before the June rush rather than competed for mid-season. A standard AC call in July under a general contractor means 7 to 14 days of waiting; under contract, your slot is pre-booked.
Move-in is equally underused. When you take over a property, you have no maintenance history for the systems you are inheriting. Starting a contract at handover solves this: the first inspection round gives you a documented baseline, with a photo report sent to WhatsApp within 24 hours. The Essential tier at AED 1,499 per year covers two AC visits, one plumbing inspection, and one electrical inspection with no call-out fees, at the equivalent of AED 125 per month.
After a Repair Bill: When the Calculation Becomes Clear
A compressor replacement, a burst pipe behind a bathroom wall, a tripped breaker traced back to deferred maintenance: these situations move residents from abstract awareness to active interest fast. European Technical’s published comparison puts reactive maintenance for a two-bedroom apartment at AED 6,000 or more per year, against a contract from AED 1,499. The company attributes a saving of 50 to 75 percent to the contract model.
The Premium tier at AED 2,499 includes three AC visits for up to six units, two plumbing and two electrical inspections, minor repairs included, a 20 percent discount on extras, and a two-hour emergency response. A 14-day money-back guarantee removes the financial risk. Dubai’s RERA and the Dubai Land Department’s tenancy-maintenance framework place the obligation for servicing of major installed systems on the landlord.
The Winter Window: Lower Demand, Better Terms
November through February is the most convenient entry point for anyone not under immediate pressure. AC demand drops, technicians have more availability, and you choose visit dates rather than accepting whatever slot remains. All tiers include a 12-month workmanship warranty on every repair, and exit terms are measured: leave after six months with 30 days’ notice and receive a prorated refund for unused months.
For villas, individual reactive servicing typically exceeds AED 10,000 per year according to European Technical’s own comparison; villa contracts start from AED 2,999 per year. The Platinum tier at AED 3,999 covers unlimited AC units with quarterly inspections and a one-hour emergency response for anyone who cannot absorb system downtime in August.
Can you sign an annual maintenance contract in Dubai mid-year, or does it have to start in January?
You can sign at any point in the year. The contract runs for 12 months from your start date, not from a calendar year. European Technical schedules the full-year visit calendar at signing, so your pre-summer AC service is locked in regardless of when you join. The 14-day money-back period applies from the contract date.
What happens if the cooling season is already underway when you sign?
The first AC service is typically scheduled within the first few weeks of signing. Existing AMC clients are prioritised when slots tighten mid-season. Emergency response guarantees apply from the contract start date. For specialist repair in Dubai, contracted clients get priority access during peak demand.
Is an annual maintenance contract worth signing for a newer property still under developer warranty?
Developer warranties cover structural defects and major system failures for a defined period; they do not cover routine preventive servicing. A maintenance contract fills that gap with scheduled AC cleaning, plumbing and electrical inspections, and documented visit records that matter when escalating a warranty claim or negotiating a lease renewal. The Essential tier at AED 1,499 makes the two annual AC services alone a strong share of the total value.
Find out the key differences between Cat6, Cat6A, and Cat7 cables. Discover which option delivers the right balance of speed, cost, and future readiness for your business network.
Every business depends on reliable connectivity. Whether it is a small office, a retail store, a school, or a growing enterprise, the network infrastructure behind daily operations plays a major role in performance. Yet many organizations struggle with one common question. Should they install Cat6, Cat6A, or Cat7 cable?
At first glance, the differences may seem minor. All three cable categories support Gigabit networking and modern business applications. However, factors such as speed, distance, interference resistance, and future expansion can make one option a better fit than another.
Understanding these differences helps businesses invest wisely instead of paying for features they may never use or choosing a cable that becomes outdated too quickly.
Why Cable Choice Matters
Network cabling is often expected to remain in place for many years. Unlike computers and switches that can be upgraded regularly, cable infrastructure is usually hidden behind walls, ceilings, and conduits.
For this reason, experienced network installers often recommend evaluating future requirements alongside current needs. A cable that performs well today should also support new technologies and increased bandwidth demands several years down the road.
Understanding the Category Options
Each cable category was developed to meet higher networking requirements than the one before it. While they may look similar from the outside, their performance capabilities are different.
Cat6 Ethernet Cable
Cat6 supports speeds up to 1 Gbps at 100 meters and can support 10 Gbps over shorter distances of 50 meters. It remains one of the most widely used network cables in offices because it balances performance and affordability.
Cat6A Ethernet Cable
Cat6A was designed as an enhanced version of Cat6. It supports 10 Gbps speeds across the full 100 meter channel. It also offers improved protection against crosstalk and electromagnetic interference.
Cat7 Ethernet Cable
Cat7 includes extensive shielding and higher frequency ratings. It was developed for specialized environments where interference control is a priority. However, its adoption in commercial networking has been more limited than many people expect.
Businesses researching long term installations often evaluate a quality Cat6 plenum Ethernet cable because it combines strong performance with suitability for spaces that require plenum rated cabling.
Speed and Distance
One of the biggest differences between these cable types is how they handle high speed data transmission over distance.
Cat6 performs exceptionally well in standard office environments. For many organizations using cloud applications, VoIP phones, and video conferencing, it provides more than enough bandwidth.
Cat6A becomes valuable when consistent 10 Gigabit performance is needed across longer cable runs. Data intensive environments such as engineering firms, healthcare facilities, and larger corporate networks often benefit from this capability.
Cat7 can support high bandwidth applications as well, but many businesses discover that Cat6A already meets their performance goals without introducing additional complexity.
The Role of Shielding
Shielding is often discussed when comparing these cable categories, but its importance depends heavily on the environment.
Cat6 is commonly available in unshielded and shielded versions.
Cat6A typically offers stronger protection against interference.
Cat7 uses extensive shielding around individual wire pairs and the overall cable.
In practical experience, many office buildings operate successfully with Cat6 or Cat6A because modern network environments do not always require the additional shielding found in Cat7. Areas with heavy industrial equipment, electrical machinery, or significant electromagnetic noise may benefit more from higher shielding levels.
Cost and Installation
The most advanced cable is not always the smartest investment.
Cat6 generally offers the lowest installation cost. It is lighter, easier to handle, and compatible with most business networking requirements.
Cat6A costs more because of its larger construction and improved performance characteristics. Installation may require additional planning due to its size and bend radius requirements.
Cat7 is typically the most expensive option. Specialized connectors and installation considerations can increase project costs even further.
When selecting an Ethernet networking cable, businesses should compare total installation value rather than focusing only on technical specifications.
Making the Right Choice
The best choice depends on business goals, network size, and future growth plans.
Small and medium sized offices often find Cat6 sufficient for daily operations. Organizations planning for long term 10 Gigabit networking frequently choose Cat6A because it provides a practical balance between performance and scalability. Cat7 may be appropriate in specialized environments where enhanced shielding is necessary.
Final Verdict
There is no universal winner between Cat6, Cat6A, and Cat7. Each category serves a different purpose. The key is matching the cable to the environment and expected workload. Businesses that understand their bandwidth needs, installation conditions, and future expansion plans are far more likely to make a cost effective decision. A well planned cabling infrastructure supports productivity, reduces future upgrade costs, and helps ensure reliable network performance for years to come.
In this post, I will show you how artificial intelligence is changing project management.
Projects rarely go exactly as planned. A task takes longer than expected, priorities change midway through, or a small issue suddenly affects the whole schedule. Most project managers have dealt with situations like these. That is why many professionals look into Project Management Tools Courses to learn better ways of managing day to day project challenges.
At the same time, Project Management Tools are becoming more capable with the help of Artificial Intelligence. Instead of spending hours chasing updates or adjusting schedules, teams can now get support from technology that helps them work faster and make more informed decisions. This shift is changing the way projects are managed across industries.
In this blog, we will look at how Artificial Intelligence is changing project management.
Key Ways AI is Changing Project Management
Here are some of the most significant ways AI is helping project teams work more efficiently and make better decisions:
Goodbye Repetitive Tasks, Hello Smart Automation
Project managers frequently work long hours on standard administrative tasks. Meeting notes and status updates can divert time from more crucial tasks.
Many of these tasks can be automated with the use of artificial intelligence. Reports and preliminary project plans can all be automatically generated by AI-powered systems.
This is one reason why Project Management Tools Courses are becoming increasingly popular among professionals who want to understand how AI driven automation is changing daily project activities.
This enables project managers to concentrate more on leading teams and accomplishing project objectives. Automation elements in modern Project Management Tools increase efficiency while decreasing manual labor.
Spotting Risks Before They Slow Projects Down
One of the biggest challenges in project management is detecting risk before they become serious problem.
AI can examine massive volumes of past project data and identify trends that would be missed by humans. It can identify delays and predict possible delays before they happen.
Project managers can take remedial action more quickly thanks to this early warning system. Teams may proactively lower risks and keep projects moving forward rather than responding to problems as they emerge.
To improve project outcomes and strengthen risk management, many organization now depend on AI-enhanced Project Management Tools.
Smarter Resource Allocation That Maximizes Team Potential
It is not always easy to find the proper person for the job, particularly when teams are working on several projects.
Artificial intelligence is capable of assessing the workload and availability of employees. It can suggest the best team members for particular tasks based on this data.
This helps avoid team burnout and enhances the use of resources. Better workforce planning helps projects, and employees are given tasks that play to their abilities.
A growing number of professionals registered in Project Management Tools courses are studying how AI facilitates more efficient resource management.
Making Better Decisions with Real Data
Every day, project managers have to make important choices. In the past, a lot of these choices mostly depended on judgment and experience.
AI gives decision-making a new degree of assurance. Before decisions are made, it may estimate possible outcomes and analyze project data.
For instance, AI can forecast how a change in a project’s deadline would impact expenses and schedules. This aids managers in selecting the best course of action.
Through Project Management Tools Courses, project professionals can also learn how AI generated insights support faster and more confident decision making.
Organizations may lower uncertainty and make better decisions with the help of intelligent Project Management Tools.
Project Scheduling Becomes More Accurate
Making a schedule for a project is one thing. Maintaining its accuracy over the course of the project is a completely different challenge.
Artificial intelligence assists by automatically modifying schedules in response to changes and continuously tracking project progress. It can pinpoint important tasks and streamline project processes.
AI can provide different strategies to keep projects on schedule when unforeseen delays occur.
Modern Project Management Tools are therefore assisting businesses in increasing the precision and effectiveness of their scheduling.
More Accurate Forecasting and Performance Tracking
A crucial component of project management has always been project forecasting. It is now more dependable than before, thanks to artificial intelligence.
AI can find patterns that could affect future results by comparing the performance of ongoing projects to that of past projects. It offers information on schedule health and budget performance.
This makes it possible for project managers to keep a closer eye on developments and deal with possible problems before they become serious ones.
Businesses that use AI-powered Project Management Tools frequently see improvements in project performance and overall business outcomes.
Conclusion
By improving automation and making decisions, AI is transforming project management. These developments lower risks and enhance project results. Project managers will find it more and more useful to comprehend how AI interacts with Project Management Tools as it develops.
Those looking to strengthen their expertise and stay competitive can benefit from PMP Training, which provides practical knowledge to support success in modern project environments.
In this post, I will talk about CS2 scams and show you red flags you should never ignore.
If you want to trade CS2 skins seriously, a few fundamentals matter before anything else, and account security tops the list. Without proper protection, your skins and your balance are both at risk. This article focuses on how to trade safely: how to recognize the most common scams, spot the warning signs early, and protect your account and inventory. Let’s get started.
Disclaimer: This article is provided for general informational purposes only and does not constitute legal, financial, or professional advice. Platform features and security procedures vary and may change over time. Always refer to official sources before taking action.
“Steam” and “Valve” are trademarks of Valve Corporation. This content is not affiliated with, endorsed by, or sponsored by Valve.
Common CS2 Scams Every Player Should Know
Understanding how these schemes work is the foundation of protecting your skins and account. The more familiar the tactics are, the sooner you’ll spot suspicious behavior.
Phishing Scams
Phishing is one of the most common threats CS2 players face. Scammers build fake login pages that closely mimic Steam or a known trading site, then spread the links through Discord, social media, or trade chats, usually claiming you’ve won a skin or need to “verify” your account.
Enter your details and they have instant access to move your items. A useful tell is that these fake pages often sit on lookalike domains and wait a few seconds before triggering a counterfeit Steam pop-up, so the login window itself can be fake even when the page looks perfect.
Trade Offer Scams
Trade-offer scams are everywhere in CS2. A common version is the last-second switch, where a valuable skin is swapped for a cheaper lookalike just before you confirm. Another is the impersonation angle: scammers pose as well-known traders or fake a connection to professional players, sometimes decorating their profiles with Major Championship medals to look authentic.
This isn’t hypothetical, when content creator OzznyCS2 flagged a wave of these, scammers were specifically adding Major tournament items to their profiles to pass as pros. Others promise extra payment outside Steam and disappear once you’ve sent the item.
Case and “Free Skin” Site Scams
Fraudulent case-opening and “free skin” sites are another major risk. They often claim to be officially supported by Valve to seem trustworthy, then display fake user wins and unrealistic offers to encourage you to transfer skins. Once items or funds are sent, withdrawals get blocked or delayed, and accounts are sometimes suspended without explanation.
A frequent escalation, documented by Bitdefender Labs, pairs these fake sites with crypto-doubling promises, where you’re told to send Bitcoin or Ethereum to “double” it back; the money simply goes to the scammer. The throughline is that these schemes prey on excitement and the urge to upgrade fast, and nothing valuable in CS2 is ever actually free.
Signs of CS2 Scams and How to Recognize Them
Scammers don’t all follow the same script, so the smaller details matter too. Here’s what should raise a flag.
Promises That Are Too Good to Be True
An offer that sounds too good to be true is one of the clearest warning signs. Messages promising free knives, big “guaranteed” returns, or large overpayments for ordinary skins should put you on alert immediately, since scammers lean on excitement and greed to lower your guard.
If someone claims they can double your inventory or hand you rare items for no clear reason, treat it as a red flag, not an opportunity.
Urgency and Pressure
Manufactured urgency is a staple tactic. Phrases like “accept now,” “last chance,” or “I’ve got other buyers waiting” are designed to stop you reviewing the trade carefully.
The same pressure shows up in fake tournament invitations and limited-time promotions. A legitimate deal can wait the thirty seconds it takes you to check it.
Suspicious Links and Profiles
Fake pages can copy Steam’s design closely, but small URL differences, spelling errors, or missing security indicators give them away. Scammer profiles tend to be recently created, low-activity, or have private inventories, and they’ll sometimes copy the names and photos of well-known traders or esports players.
This pro-impersonation tactic is common enough that real pros have had to push back publicly: Team Vitality captain Dan “apEX” Madesclaire posted a scam alert on X warning fans that a YouTube giveaway using his name and the Vitality brand was fraudulent and had nothing to do with him. Similar fakes have used the names of s1mple, ZywOo, NiKo, and major orgs, so a famous name attached to a giveaway is a reason for more scrutiny, not less.
Impersonation and Copycat Platforms
Worth its own mention, because it’s growing fast: scammers increasingly copy a well-known CS2 platform rather than building their own, and this happens across the whole niche, to every established brand. They clone a trusted site on a near-identical domain, sometimes buying ads so the fake outranks the real one, or they message you on Steam or Discord posing as a platform’s “support” or “promotions” team.
Before logging in or sending anything, check the fundamentals: read the domain character by character for typos or an odd extension, confirm the page uses HTTPS with a valid padlock, and be wary of any “platform” with no two-factor authentication option at all. No legitimate site or support agent asks for your password or API key in a message, and any unexpected “support” contact should be verified through the platform’s official website first.
Tips to Prevent CS2 Scams and Protect Your CS2 Skins
Staying safe isn’t complicated, but it takes attention and a few good habits. Here’s what to put in place.
Secure Your Account
Start with the basics that block most attacks: a strong, unique password and two-factor authentication on your Steam account. The Steam Guard Mobile Authenticator adds a critical layer when confirming trades or market listings.
Avoid logging in on shared or public devices, and never save your credentials in browsers you don’t control. This advice is universal across the major scam-prevention guides for a reason, it’s the single highest-impact step you can take.
Double-Check Every Trade
Before confirming any trade, review the item details closely, the skin name, condition, stickers, and float value, to be sure nothing changed at the last second. Scammers count on small visual similarities to slip a swap past you.
Take the extra few seconds to compare the offer against what was actually discussed, and if anything looks off, cancel immediately. A widely shared community trick is to add a low-value decoy item to a trade you’re unsure of; many API-redirection bots run empty inventories and can’t complete a trade that requires sending it back, so a vanished decoy is a clear warning.
Be Careful with External Platforms
If you use third-party case-opening or trading sites, research them before sending any skins. Look for a real reputation, genuine user feedback, and transparent policies, and reach them through your own bookmark rather than a link from Discord or social media, even one that appears tied to Valve or an official event.
Fake sites copy the design of trusted platforms closely, so the domain and the login behavior matter more than the look.
Learn From Platforms That Have Seen It All
Some of the most useful scam-prevention advice comes from platforms that have operated in the CS2 space for years and have watched these schemes evolve firsthand. Several have turned that experience into detailed public guides worth reading. Hellcase, which has been around for roughly a decade, maintains asecurity guide built around real Steam-account and case-opening scam cases its own users have reported.
Skinport takes a checklist approach in itsguide to never getting scammed, laying out a strict set of rules covering trade habits and account security. For the recovery side, DMarket’sexplainer on Steam trade protection walks through how the seven-day reversal window functions and when it actually applies. Reading a couple of these in full is one of the highest-value things you can do for your account’s safety.
Conclusion
This article covered the core of safe CS2 trading: the most common scam types, the warning signs worth never ignoring, and the practical steps that protect your account and inventory.
These risks are part of the trading world, but staying informed and unhurried is most of the defense. Verify every trade, never let anyone rush you, and keep your security settings tight. Stay sharp, and trade safely.
In this post, I will talk about CS:GO skins in CS2 and how they look now.
When Counter-Strike 2 launched, many players wondered what would happen to their skins. The good news is that all CSGO skins were carried over—the developers fully migrated them to the new version of the game.
Furthermore, thanks to the transition to the Source 2 engine, familiar skins got a new look. Now, even older items can appear as if you bought them yesterday.
Migrating Skins from CS:GO to CS2
Valve made the transition process as simple as possible for players. All items you had in CS:GO automatically appeared in CS2. Players didn’t have to do anything—their inventory was just there. All the important details stayed the same, including:
original Float Value;
unique pattern index;
all applied stickers;
wear level;
StatTrak™ history.
This way, rare patterns, low-float skins, and expensive collectibles kept their value. If you had a perfect Fade or a rare Doppler with a specific pattern, it’s still the same skin—it just looks better now, thanks to the new lighting.
Source 2 Lighting and PBR Effect
The biggest visual change came with the move to Source 2, driven by physically based rendering (PBR). Such a system provides more realistic lighting and reflection, interacting with weapon materials in new ways.
Metallic surfaces look deeper and more saturated. Glossy finishes reflect light more accurately. This effect is particularly noticeable on popular skin lines like Doppler, Fade, Marble Fade, and other “shiny” skins.
In CS2, light reacts dynamically to its environment. This is why the same knife can appear different depending on the map and the player’s position. As a result, many older skins look more expensive and striking. Some models that previously appeared dull now have more volume and contrast.
Along with the lighting upgrades, the developers also updated the weapon models themselves. They are more detailed, with sharper textures. This directly impacts the appearance of applied stickers.
In CS2, stickers better blend into the weapon’s surface. Dynamic lighting can make them look more reflective or, conversely, more matte, depending on the material. Holographic and foil versions especially benefit from the new graphics.
While some combinations previously looked a bit clunky, they now appear much more harmonious. This has given players additional motivation to experiment with customization.
Inventory Update: Is It Worth Changing Skins?
After the graphics upgrade, it became clear that some skins perform better in CS2 than others. Therefore, many players reconsidered their loadouts and thought about replacing items.
If you’re looking to update your inventory or trade in old items, the DMarket marketplace can be a convenient solution. The platform allows you to buy, sell, and trade in-game items, including CS2 skins. Offers can be compared easily, the right float or matching pattern can be found quickly, and transactions can be completed swiftly.
Conclusion
The transition to CS2 did not devalue the old skins. On the contrary, it gave them a new lease of life. The automatic migration preserved all item stats. The Source 2 engine made weapon appearances more realistic and impressive.
Now is the time to review your inventory if you haven’t done so in a while. Some of the skins look brighter, deeper, and more expensive than ever before. And if you want to update your collection, modern marketplaces like DMarket make the process more convenient.
In this post, I will show you how mobile forensics shape personal injury claims.
Most drivers involved in a motor vehicle collision assume that police reports, physical damage photographs, and eyewitness testimony will serve as the primary evidence in their civil case. In reality, modern personal injury litigation increasingly hinges on the pocket-sized supercomputers carried everywhere: smartphones. Today’s mobile devices function as continuous telemetry loggers, quietly recording physical speed, geographic coordinates, screen engagement, and biometric fluctuations. When a severe wreck occurs, insurance adjusters and legal teams aggressively seek mobile forensic extractions to reconstruct the exact seconds before, during, and after impact. Navigating how this digital trail entersthe discovery process in injury claims has quickly become one of the most decisive factors in personal injury litigation.
The Digital Footprint of Physical Motion
Smartphones contain sophisticated hardware sensors designed to track physical movement with remarkable accuracy. Accelerometers, gyroscopes, and barometers work in tandem with native health applications to log steps, elevation changes, walking speed, and sudden shifts in velocity. In personal injury cases, this biometric data acts as an objective witness to physical trauma and post-accident recovery claims.
When a collision triggers an automated crash detection system on a modern smartphone, the device records a sharp spike in G-force followed by immediate deceleration. Forensic experts can extract this precise sensor log to verify the exact moment of impact. Beyond the crash itself, health applications continuously record physical activity levels prior to and following an incident. If a claimant asserts that an injury completely prevents them from walking or performing daily routines, defense counsel often subpoenas wearable fitness metrics and smartphone step counts. Conversely, a sudden drop in daily steps following an accident can provide powerful, unassailable evidence of physical impairment.
Location History and the GPS Trail
Geographic positioning data provides another critical layer of evidence in accident litigation. Mobile devices interact constantly with global positioning satellites, cellular towers, and nearby Wi-Fi networks to maintain location accuracy for mapping applications and background services. This creates an intricate digital breadcrumb trail that can either confirm or refute driver accounts.
In disputed liability claims, location telemetry reveals far more than just a destination. Advanced GPS logs capture vehicular speed, route selection, stopping behavior, and time spent idling at intersections. If a driver claims they came to a complete stop at a red light before proceeding, forensic mapping can analyze the device’s positional data down to a matter of feet per second. Furthermore, location history helps establish whether a driver was navigating an unfamiliar route while operating a vehicle, raising questions about potential driver distraction.
Cell tower handoffs and Wi-Fi probe requests complement GPS data by providing circumstantial evidence of location even when location services are turned off. Every time a phone searches for a familiar Wi-Fi network or connects to a new cellular site, a timestamped entry is generated. Reconstructing these connection logs enables digital forensics specialists to build a reliable timeline of events surrounding a crash.
Cloud Backups and Deleted Data Traps
A common misconception among device users is that deleting a text message, closing a browser tab, or clearing an app cache removes the information permanently. Modern mobile operating systems rely heavily on automated cloud backups and flash memory structures that store remnants of deleted data long after a user attempts to erase it.
Specialized mobile forensic software can pull detailed relational databases from cloud storage mirrors and local flash storage. These extractions reveal text message threads, instant messaging logs, photo metadata, and app usage history with millisecond-level precision. If a driver was actively typing a message, scrolling through a social media feed, or streaming video at the moment of impact, digital forensics will expose that activity regardless of whether the application was closed immediately after the crash.
The deliberate deletion of device data after an accident carries severe legal consequences. Courts view the intentional destruction of evidence as spoliation, which can lead to harsh judicial sanctions. Judges may issue adverse inference jury instructions, telling jurors to presume that the destroyed mobile data would have proven the driver’s fault. Preserving device states immediately following an incident is therefore paramount for both plaintiffs and defendants.
Colorado Privacy Act Limits Versus Civil Discovery Obligations
The intersection of state privacy statutes and civil litigation rules creates a contentious battlefield in courtrooms. In jurisdictions like Colorado, robust consumer data protections under the Colorado Privacy Act establish strong rights regarding personal data control, collection limits, and individual privacy. However, these consumer protections frequently collide with broad civil discovery obligations mandated by state courts.
Under the Colorado Rules of Civil Procedure, parties in a lawsuit are entitled to obtain discovery regarding any non-privileged matter that is relevant to a claim or defense and proportional to the needs of the case. When a defense attorney issues a sweeping subpoena for a plaintiff’s entire smartphone content, or when a plaintiff demands full access to a defendant’s personal device, privacy rights take center stage. Colorado privacy principles dictate that individuals maintain a reasonable expectation of privacy over personal communications, health records, and private media that have no bearing on the accident.
Judges must balance these competing interests by carefully evaluating the scope of forensic requests. Courts rarely grant unrestricted access to a personal device. Instead, judges often require targeted forensic protocols that restrict extractions to specific time windows—such as thirty minutes before and after a collision—and limit keyword searches to relevant topics. When disputes arise over sensitive personal data, judges may conduct an in-camera review, inspecting the extracted phone data in chambers to determine what information is genuinely relevant before disclosing it to opposing counsel.
Navigating the Scope Fight in Digital Subpoenas
Because smartphones hold a person’s entire life—from private family photos and financial banking records to confidential work emails—battles over subpoena scope are increasingly fierce. Overly broad discovery requests that demand an entire device dump are routinely challenged as invasive fishing expeditions.
Legal teams must draft precise, narrowly tailored requests when seeking mobile device evidence. A proper forensic request targets specific artifacts, such as cellular call detail records, screen interaction logs during a defined time window, or specific application telemetry. Requests that fail to establish a direct connection between the requested digital data and the cause of the accident are vulnerable to protective orders.
Protecting non-relevant private data requires proactive legal measures. Attorneys frequently establish protective orders and non-disclosure agreements that govern how extracted data is handled, stored, and ultimately destroyed after litigation concludes. Establishing these safeguards ensures that essential digital evidence is brought to light without needlessly compromising personal privacy.
Mobile device forensics has permanently reshaped personal injury litigation, making digital data as influential as physical evidence. Understanding your rights regarding device preservation, privacy boundaries, and evidence collection is vital when navigating a complex injury claim. Attempting to manage device requests or insurance negotiations without seasoned legal counsel can put your claim or personal assets at significant risk. Understandingthe discovery process in injury claims and consulting an experienced personal injury attorney can help protect your privacy, preserve critical evidence, and secure the compensation you deserve.
In this post, I will talk about the best managed DDoS testing services to stress-test without risking an outage.
Last year, a single botnet hurled 31.4 Tbps of junk traffic at one target—shattering every distributed-denial-of-service (DDoS) record on the books. Regulators moved fast: under Europe’s NIS2 directive and the new U.S. four-day disclosure rule, boards now have to prove their defenses can take that kind of beating. The safest route? Run a controlled “friendly-fire” drill with specialists at the helm.
Managed DDoS-testing teams launch the traffic, watch live KPIs, and kill the stream before customers feel a bump. In this guide, we compare the top providers by engagement style, scale, and reporting depth so you can choose the drill that fits your risk and budget.
How we picked the contenders
First, every vendor had to clear two non-negotiables:
run legal, enterprise-grade DDoS simulations (no gray-market “booter” traffic), and
show real-time safeguards that stop a drill before it degrades production.
With that safety baseline set, we scored each candidate against seven weighted factors security leaders say shape the buying decision:
Attack realism (25 percent). Do their playbooks mirror today’s multivector campaigns, from terabit UDP floods to HTTP/2 rapid-reset volleys?
Safety controls (25 percent). Is there a live kill switch, gradual ramp-up, and health-metric telemetry?
Scalability (15 percent). Peak firepower: 20 Gbps or multi-terabit?
Reporting depth (10 percent). Packet captures and board-ready takeaways, or a simple pass/fail?
Expert guidance (10 percent). Will a seasoned engineer be on the bridge, or are you self-navigating?
Compliance readiness (5 percent). Cloud-provider approval letters and auditor-friendly artifacts.
Safety and realism carry double weight because a glossy PDF is useless if the test never strains your defenses—or, worse, takes the site down.
Finally, we grouped the winners by engagement style: white-glove consultancy, self-service portal, or DIY lab gear, so you can jump straight to the model that fits your culture.
Fully managed fire drills: experts in the driver’s seat
With a managed engagement, a dedicated DDoS team plans the scenario, launches traffic from its controlled “friendly botnet,” and watches your KPIs in real time, ready to kill the stream the moment latency or error budgets spike. You walk away with raw packet captures and a live debrief that turns the test into practical training without burning hours on setup uncertainty.
Red Button: Azure-approved depth and detail
Red Button Azure-Approved DDoS Testing Partner Screenshot
Microsoft lists Red Button as an authorized DDoS attack-simulation partner for Azure, so every drill follows the cloud provider’s own rules and telemetry hooks. Their latest breakdown of ddos testing options—managed engagements, self-service portals, and automated SaaS probes—helps clients see exactly where this white-glove service lands on the spectrum before any packets fly. Before traffic flies, Red Button engineers run architecture reviews, mitigation walk-throughs, and stakeholder sign-offs; so the test plan is signed off before anything launches.
During the exercise, a senior consultant stays on a live bridge with your team, narrating each vector while dashboards stream KPIs. If latency or error rates cross the thresholds you agreed on, the operator stops the traffic within seconds.
Their cloud attack engine tops out near 300 Gbps, enough to stress most enterprise or SaaS stacks. Afterward you receive:
a minute-by-minute timeline of every attack phase
full packet captures for root-cause analysis
a DDoS Resiliency Score (Red Button’s open-standard metric) that benchmarks your protection level against peers in your industry
Engagements start in the low five figures, and clients leave with prioritized fixes and an audit-ready paper trail, far cheaper than an unplanned outage.
NimbusDDOS: Live-fire drills that double as incident-response practice
NimbusDDOS Live-Fire DDoS Simulation Service Screenshot
NimbusDDOS treats every engagement as a rehearsal for the real thing. Before launch, the team runs a half-day workshop where network and security leads chart critical services, set “safe-fail” thresholds, and test comms channels. When test day arrives, everyone already knows which metric triggers a pause.
A dedicated Nimbus engineer joins your bridge and adjusts vectors on the fly. If a 50 Gbps SYN flood barely dents your firewall, they pivot to a slow-loris HTTP attack or a DNS amplification burst, pressure-testing both tech and people. Traffic ramps in measured steps, and the operator hits a global kill switch the instant latency or error budgets tip.
After the drill, you receive a minute-by-minute timeline, packet captures, and prioritized fixes. More important, your team walks away with lived muscle memory; the next 2 a.m. alert feels familiar instead of chaotic.
Engagements are project priced, often mid-five figures for a full-scale drill, and suit organizations that want to test infrastructure and sharpen human reflexes in the same controlled session.
Self-service and hybrid platforms: power on your schedule
Sometimes you don’t need a consulting entourage; you just need to light up a test at 1 a.m., watch the graphs, and go back to shipping code. Self-service and hybrid platforms let you pick vectors, set peak bandwidth, and press Launch while an on-call engineer shadows the run in case KPIs wobble. The outcome is consultant-grade safety with DevOps-grade speed.
RedWolf focuses on raw capacity, yet you stay in control. Its cloud portal lets you choose from more than 300 attack vectors, pick launch regions, and set peak bandwidth. Want to see whether your anycast CDN can take a 1 Tbps UDP flood? Dial it in and hit Launch; the platform can scale to multi-terabit traffic across dozens of nodes without a support ticket.
Safety is built in. Traffic ramps gradually while telemetry watches latency, error rates, and mitigation logs. Cross a predefined threshold and an automatic kill switch stops the test in about 10 seconds. A big red Stop button is always on your dashboard for manual aborts.
Customers often start in “concierge” mode, where RedWolf engineers sit on the bridge and refine scenarios, then graduate to pure self-service, scheduling monthly drills straight from CI/CD pipelines. Same-day reports overlay attack curves with mitigation events and leak points, so dev and network teams can patch issues before the next sprint closes.
Pricing is usage based. One-off tests are available, while most enterprises choose a subscription that offers unlimited drills up to a bandwidth quota. You pay only for the traffic you generate, not idle capacity. If your culture prizes autonomy and your threat model includes headline-level floods, RedWolf puts the terabit cannon in your hands without the risk.
LoDDoS: self-service portal with a human safety net
LoDDoS gives you dashboard control without the solo pressure. Build a test, pick vectors, peak bandwidth, and start time, then hit Schedule. A LoDDoS engineer shadows the run in real time and can pause or tune traffic the moment latency or error rates drift.
Typical drills run 50–200 Gbps from cloud regions already cleared with major providers, so you avoid last-minute ISP paperwork. Results land in a shareable web portal, handy for looping in your ISP or scrubbing-center vendor without shipping giant PDFs.
The platform is sold on an annual subscription. Teams running quarterly or monthly drills get predictable costs, while one-off compliance checks may find the model expensive. For organizations that want repeatable, self-driven tests without the “what if we break prod?” anxiety, that silent co-pilot is often worth the premium.
Cyttack.ai: AI-planned drills for lean security teams
Cyttack.ai turns DDoS testing into a SaaS signup. Enter a credit card, answer a guided questionnaire about your stack, and an AI engine assembles a tailored attack plan in minutes. Choose an intensity preset (Breeze, Blast, or Storm) and schedule the run.
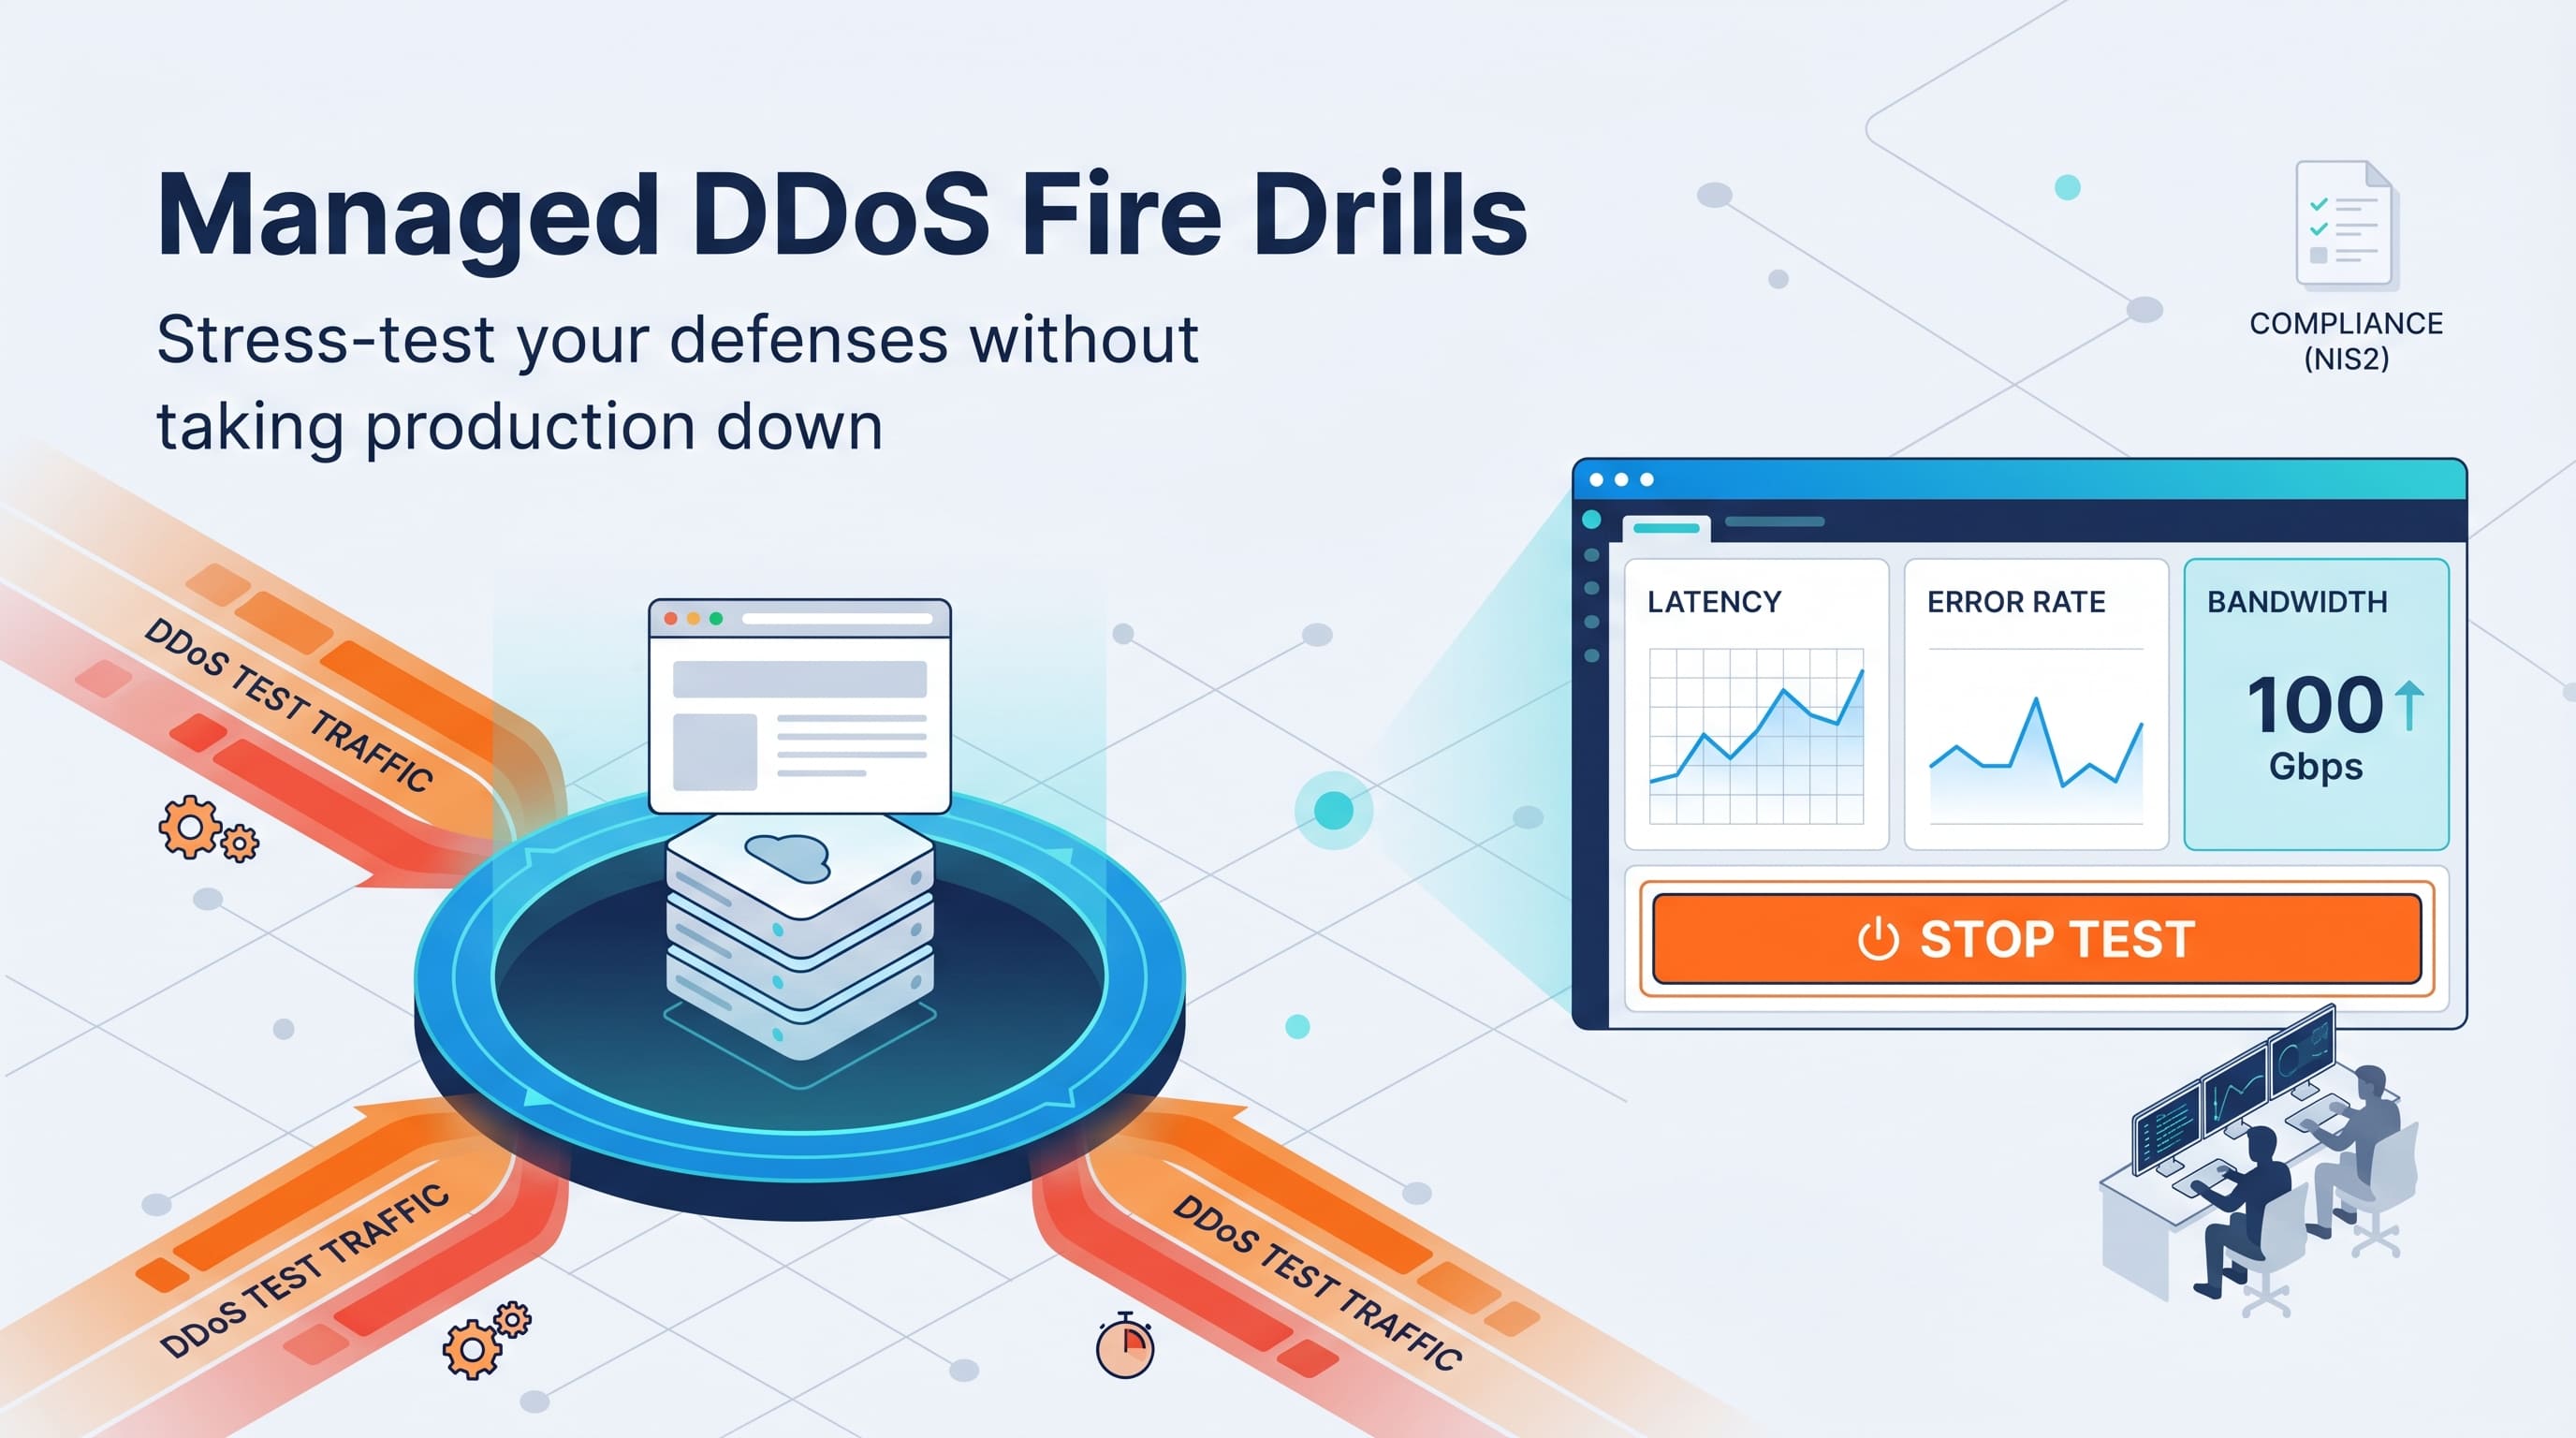
A web dashboard streams live bandwidth, latency, and error rates, with a one-click Stop test button for peace of mind. The cloud botnet peaks near 100 Gbps, enough for most SaaS or fintech workloads, and already includes modern HTTP/2 rapid-reset vectors alongside classic floods.
Within minutes of completion you receive a PDF that pairs an executive pass/fail summary with a technical appendix of packet traces, sample WAF rules, and rate-limit values. In-platform chat connects you to an engineer when deeper questions arise, but the default is self-service speed.
Pricing is posted up front. Packages start in the low-four-figure range per month and scale by Gbps and test frequency. For teams with tight headcount but strict audit demands, Cyttack condenses a month of consulting into a same-day checklist.
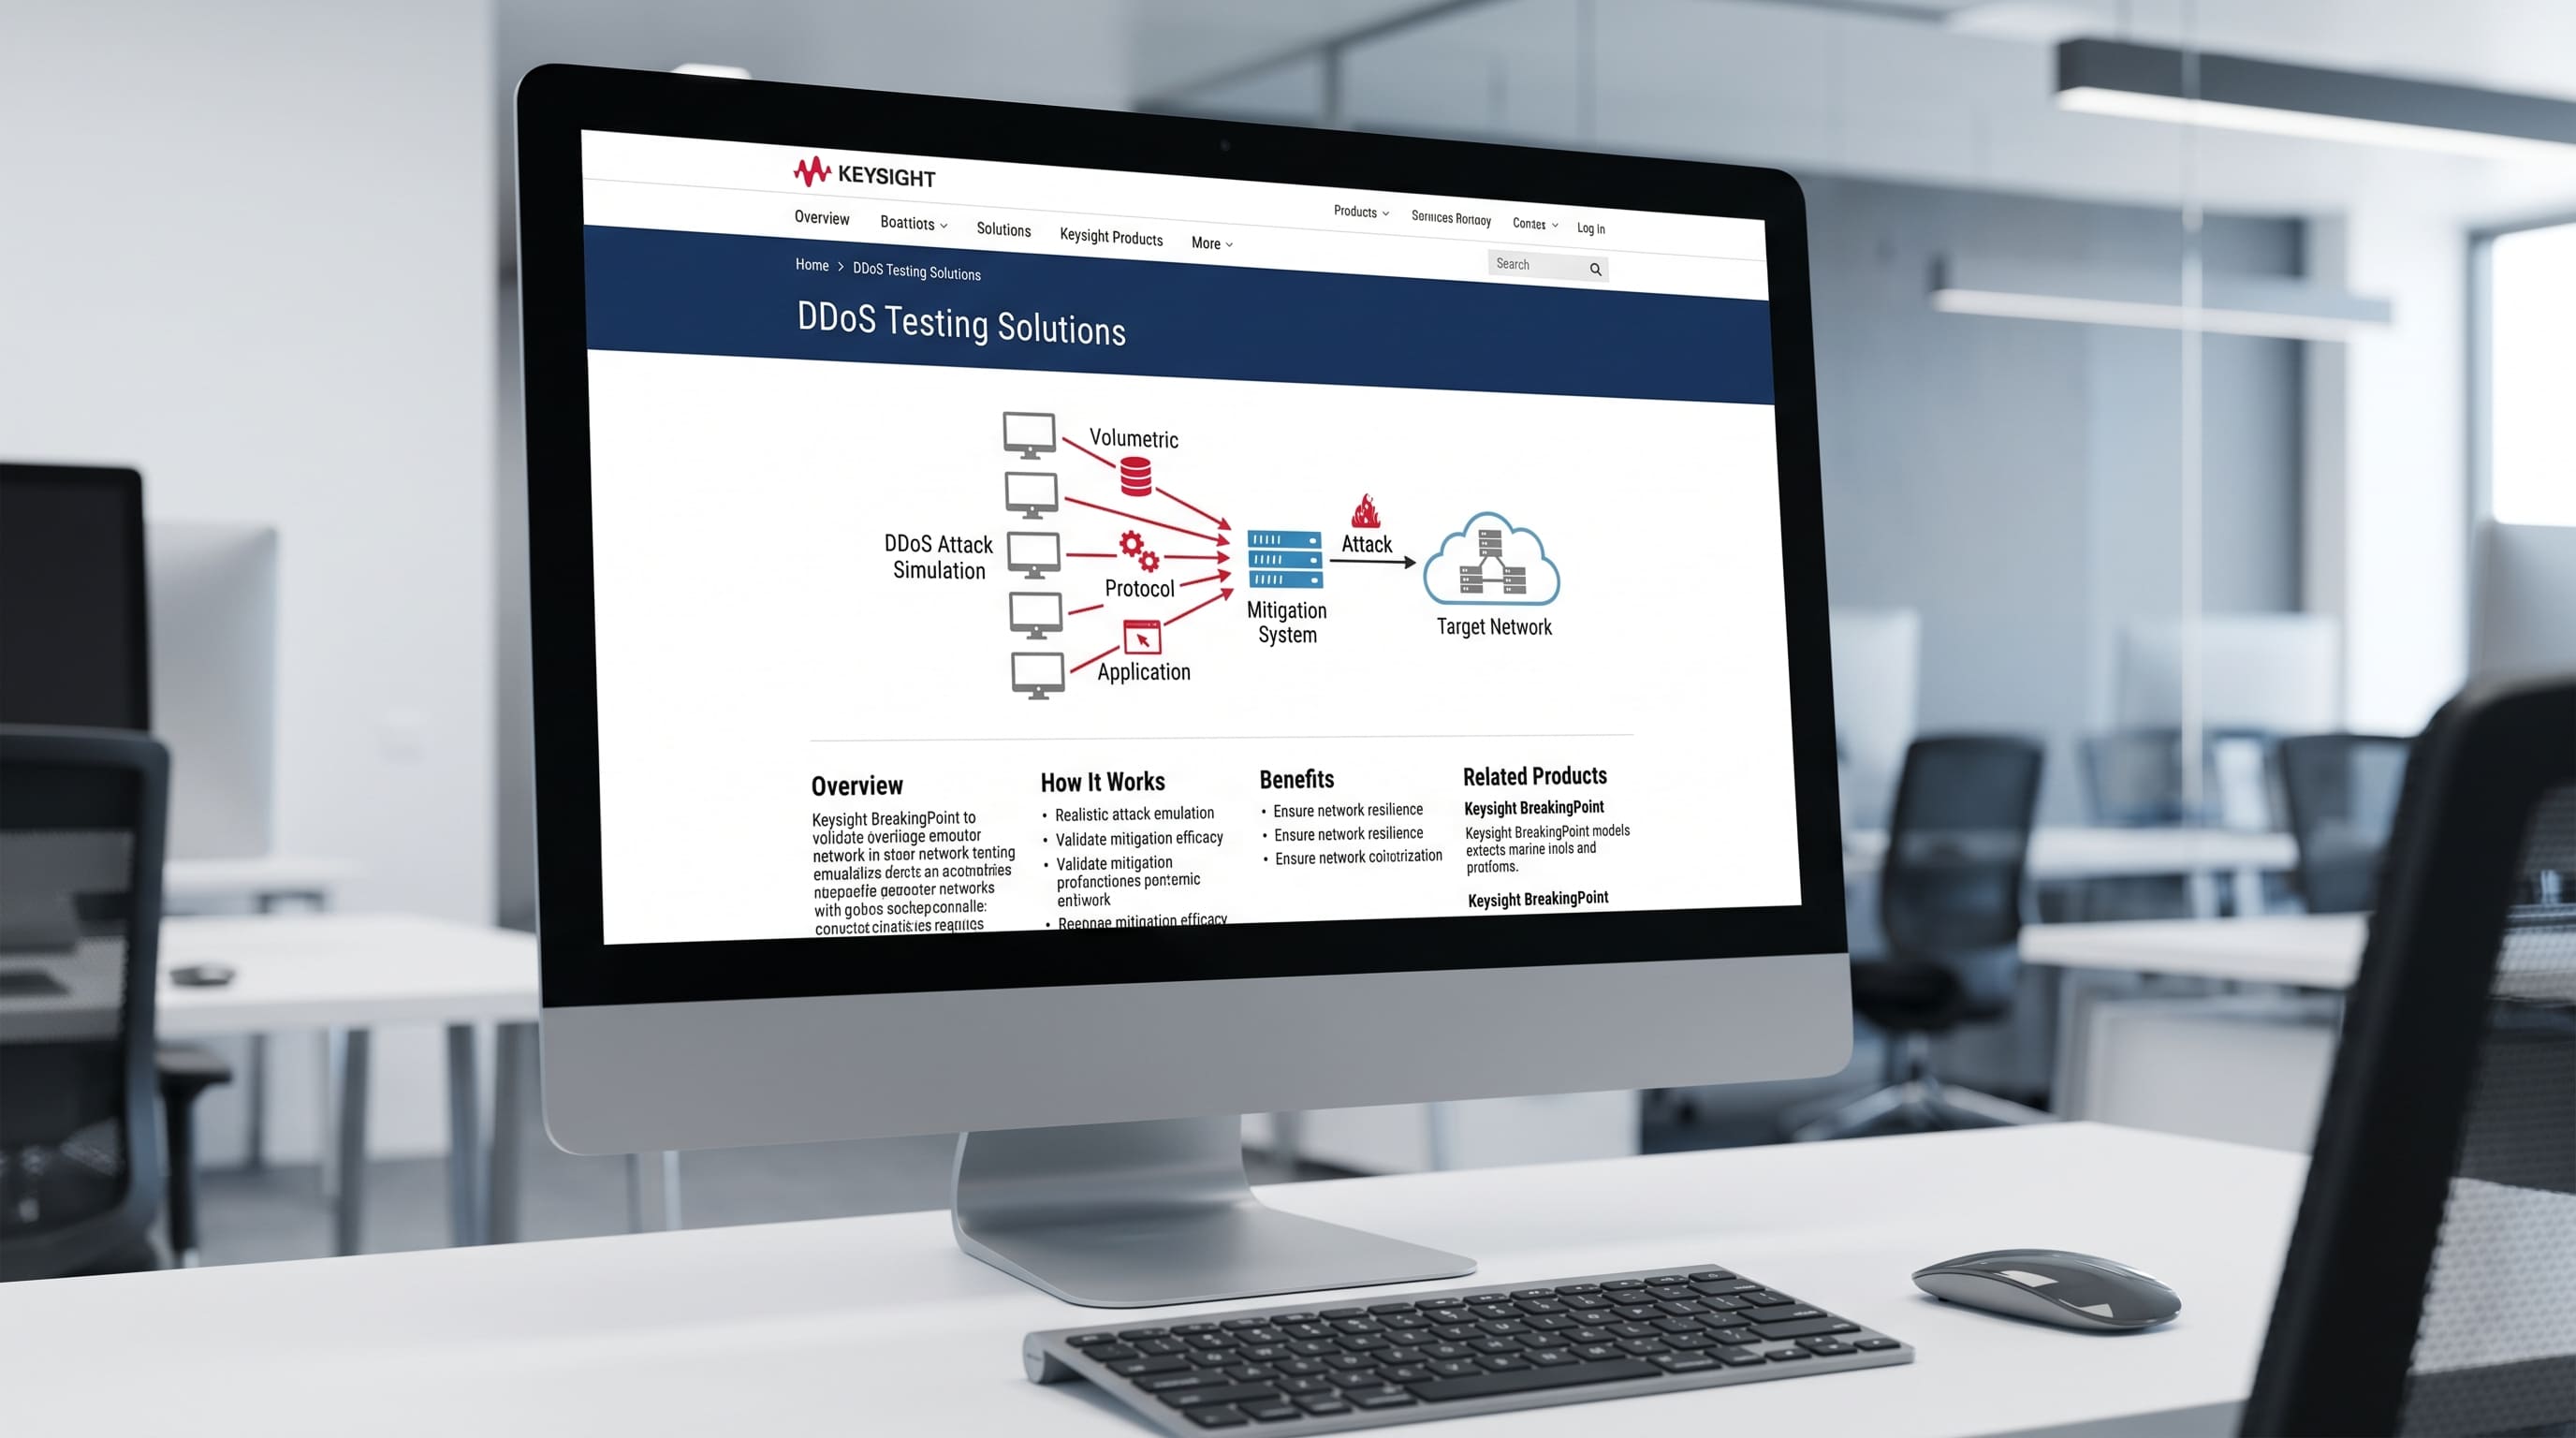
Keysight BreakingPoint & CyPerf: build-your-own test lab
Keysight BreakingPoint and CyPerf DIY DDoS Test Lab Solution Screenshot
For some organizations, trust comes only from generating every packet in-house. BreakingPoint hardware and CyPerf cloud agents give large enterprises and telcos that do-it-yourself option: rack the chassis (or spin up virtual agents), script any mix of legitimate and malicious traffic, and launch it across isolated links or sand-boxed testbeds.
A single chassis delivers about 150 Gbps of stateful traffic; cluster a few and you reach multi-terabit scale, which is why firewall vendors and mobile carriers use BreakingPoint to certify new gear. The trade-off is responsibility: there’s no managed kill switch. Misroute a flood toward production and the outage is on you, which is why most users keep the system in a dedicated lab and staff it with engineers who live and breathe packets.
The upside is freedom and repeatability. You can replay last night’s attack at 2× scale, or spin CyPerf agents in three clouds to validate a firmware patch before rolling it global. Upfront costs (hardware, licenses, support) run well into six figures, plus staff time for test design and analysis. If DDoS validation is a weekly engineering task rather than an annual checkbox, owning the toolchain can be cheaper and faster than booking outside drills.
DDoS services at a glance
Provider
Engagement model
Peak traffic
Key vectors
Safety control
Reporting depth
Pricing model
Best fit
Red Button
Fully managed consultants
~300 Gbps
L3–L7, including HTTP/2
Live engineer with instant kill switch
Executive summary plus packet captures and resiliency score
Project based
Azure-hosted enterprises that need audit-ready depth
NimbusDDOS
Managed drill with incident-response coaching
High-hundreds Gbps (per scenario)
Adaptive multivector
Embedded engineer, soft ramp
Minute-by-minute timeline and fixes
Project based
Teams seeking a full incident-response rehearsal
RedWolf Security
Self-service portal (concierge optional)
Multi-terabit
300+ L3/L4/L7 vectors
Auto kill within 10 s
Same-day portal and PDF
Subscription or per test
Operators that need terabit-scale bursts on demand
LoDDoS
Self-service with human safety net
50–200 Gbps
Common floods plus HTTP
Operator monitors live
Shareable web reports
Subscription
Orgs wanting frequent drills plus backup eyes
Cyttack.ai
Automated SaaS
Up to 100 Gbps
Modern L3–L7, including HTTP/2
One-click stop
Auto report with AI-generated fixes
Published SaaS tiers
Lean teams needing quick, low-cost proof
Keysight BreakingPoint / CyPerf
DIY hardware and cloud agents
150 Gbps per chassis; stackable to Tbps
Script any traffic mix
User managed
Raw captures and stats
Capital expense plus support
Telcos or labs with in-house experts
Conclusion: managed vs. DIY — picking the model that matches your culture
First decision: who’s at the console when packets start flying?
Managed service. Think of it as hiring a race team. Consultants design the scenario, watch KPIs in real time, and hand you a remediation plan. Your staff learns without touching traffic generators. Typical cadence: one or two large drills per year at a five-figure project cost.
DIY toolkit. You buy the hardware or cloud agents, write the scripts, and own every safety check. Great for weekly change cycles or lab certification, but you’ll budget skilled engineers plus six-figure CapEx.
Hybrid/SaaS platform. A web portal lets you launch tests on demand while automated throttles, or a remote operator, stand by to stop traffic if KPIs wobble. Ideal for DevOps teams that fold security tests into CI/CD.
Before you choose, answer three questions:
How often will we test? Annual show-me drills fit managed services. Monthly or continuous checks align with hybrid or DIY options.
Do we have DDoS expertise on payroll? If not, outsource the first engagements and learn by watching.
What’s our outage tolerance? Industries that can’t afford a single blip lean on tightly staged consultant drills.
Line up your answers with the options above and your shortlist writes itself.
In this Kinguin review, we will answer the question – is Kinguin safe? Is Kinguin legit? Or is Kinguin a scam?
Kinguin is a third-party online marketplace for trading game keys. The platform has over 4 million users who buy or sell game keys and other software keys like Microsoft Windows 10, etc.
Established in 2013, Kinguin is one of the largest secondary marketplaces for buying Steam, Battle.Net, and Origin cheaply.
Non-English users can access Kinguin in French, Portuguese, Spanish, and four other international languages. The popularity of Kinguin provoked a surge of interest in gaming marketplaces building.
Kinguin Overview
Kinguin is an online marketplace that allows you to buy and sell digital products like video games, software, and gift cards. It’s a great place to find the best deals on all your favorite games, as well as great discounts on software and gift cards.
Kinguin is a great one-stop shop for digital products. They have a massive selection of games from all the major gaming platforms, including PC, Xbox, PlayStation, and Nintendo. You can browse through their extensive catalog to find the perfect game for you.
They also have a wide selection of software, including anti-virus programs, office suites, and more. And if you’re looking for gift cards or other digital products, you’ll find them here too.
Kinguin is easy to use, and they have a helpful customer service team that can answer any questions you have. They also have a secure payment system so you can buy with confidence.
Plus, they offer free shipping on orders over $30 and free returns within 30 days.
Overall, Kinguin is a great online marketplace for finding deals on digital products. Whether you’re looking for video games, software, or gift cards, you’ll be sure to find what you need at Kinguin.
However, given the number of visitors and enhanced security requirements, a Kinguin clone is the task you should entrust to no one but an experienced and reliable marketplace development company.
Users need to be 16 to register an account with Kinguin. However, underage users can register an account with the consent of parents or guardians.
For this Kinguin review, let’s check out its buyers’ protection policy.
Since Kinguin is a third-party marketplace majorly for gamers, the probability of buying illegal products or product keys not functioning cannot be ruled out.
There’s an example of gamers whose license keys were revoked by Ubisoft for buying from hackers who bought and resold Ubisoft game keys with stolen credit card details. Ubisoft, however, decided that gamers can keep their keys.
Due to the high risk of buying products from fraudulent sellers, Kinguin introduces the ‘Buyer Protection,’ which costs a little extra; but it does assure buyers of getting ‘certified working’ products or getting a 100% refund on purchasing fake product keys.
Kinguin is a legally registered third-party gamers marketplace, and it does put in place checks to verify sellers on its platform to reduce the chances of sellers scamming buyers.
In as much as Kinguin is a legit marketplace, sellers’ activities are not under check; however, buyers are encouraged to use ‘Kinguin’s Buyers Protection’ to guard against scams and buying fake product keys.
You may be wondering is Kinguin legit. While there are many legit sellers on the Kinguin marketplace, there are also a few who are not.
Here are the things you should look for when purchasing your Kinguin. Listed below are some tips to make your Kinguin buying experience a pleasant one.
Avoid buying game keys from unknown sellers. Many Kinguin sellers are simply not trustworthy. These people could be anywhere. Furthermore, Kinguin does not background check their sellers.
Therefore, you’re responsible for any problems you may encounter. It’s also not worth it if the seller does not deliver what they promised.
You can also buy games directly from the developer or through legitimate channels. But if you’re not sure if the seller is legit, you can opt for the Buyer Protection program.
When buying games, always remember that pirated software is not legit. Some games are cracked or do not support online multi-player gaming. If you’re planning to purchase Windows software, you should purchase it from an authorized seller.
Although there are many scam websites offering cracked software, you can be sure that a product that’s not legit will never work. In addition, Kinguin does not verify the identity of the seller or the origin of the product.
If you’re worried about purchasing from Kinguin, you may want to contact the company’s customer support team to check if the seller is legit.
If you’re not able to get a refund or your key has expired, you can take advantage of the Buyers Protection Program. If your key is fake or expired, Kinguin will refund you in full. If you have a question, contact them right away.
Yes, Kinguin is legit as long as there are no laws banning the resale of legally purchased items. Kinguin is legit is a legit GREY eCommerce marketplace like G2P and CDKeys. Hence, it is dedicated to the resale of legitimately purchased software keys.
Every individual can do whatever he pleases with purchased items; hence Kinguin allows for the resale of software licenses purchased using legal means only.
Therefore, Kinguin does not permit the resale of keys illegally acquired through stealing, fraud, data breaches, etc., on its platform.
To ensure that only legally acquired software keys are sold on Kinguin’s platform Kinguin verifies the originality and authenticity of software keys and ensures that such licenses are acquired with legitimate means.
Hence, part of Kinguin’s responsibility is to reduce the sales and circulation of fraudulent and defective software.
Another reason you can consider Kinguin a legit marketplace is the use of robust security measures and strong privacy policies to keep its users’ data safe and private.
There is no easy answer when it comes to whether or not Kinguin is a scam. The website has been accused of being a scam in the past, but there is no concrete evidence to support these claims. However, there are some things to be aware of when using the site.
First, it is important to note that Kinguin does not guarantee the authenticity of the products sold on their marketplace.
This means that there is a possibility that you could end up with a fake product if you purchase something from Kinguin.
Additionally, some users have reported issues with customer service in the past. While this doesn’t necessarily mean that Kinguin is a scam, it’s something to keep in mind if you’re considering using the site.
The first question you should ask yourself before buying Kinguin game codes is “Is Kinguin safe and secure?”. The answer to this question depends on how much you value your privacy. Kinguin promises buyer protection, which promises to protect you from trolls, fake sellers, and scammers.
While there are some drawbacks to buying game codes from Kinguin, they are still cheaper than the original prices, so it is a good option.
While it is true that Kinguin codes come from discounted markets, some are sold by mistaken users, insiders, or even game developers. However, Kinguin acts as a broker and tries to ensure all sellers are legitimate.
If you’re unsure about the legitimacy of a seller, you can always seek help from other sources, including online forums and message boards. Kinguin also tries to keep its prices low, which can make it a safe option for you to buy games and game keys.
While Kinguin may be safe and secure, be sure to keep your wallet protected. While Kinguin is entirely legal in most countries, a reputable seller will always display their badge and ratings on the website.
Always make sure you’re dealing with a legitimate seller – one who is willing to refund you if you’re unhappy with the purchase. There are many scammers out there who will lure you into purchasing items that you’ll never get.
Kinguin is a safe online marketplace to shop from. Financial details shared with Kinguin remain safe with Kinguin, and Kinguin does not sell its customers’ data to third-parties.
Therefore, if you’re shopping on Kinguin, Kinguin does assure you of the safety of your credit card and financial details. Hence, every transaction done on Kinguin is safe and secure.
Kinguin is a marketplace where you can buy game keys and other product keys at prices way cheaper than buying from authorized market places.
Although the sellers’ sources cannot be ascertained, some sellers source for product keys from promotional offers, while other sellers live in regions where product keys are sold at great discounts. However, other sources can be illegal or fraudulent, including buying product keys for resale with hacked credit card details.
Kinguin is safe for your credit card because it uses a combination of robust security protocols along with a strong privacy policy to protect users’ credit card information.
Kinguin reviews abound on Reddit about the safety of credit card details of users who had purchased on Kinguin using credit cards.
In as much as you’re using your credit card details to make purchases on Kinguin, I suggest that you confirm that you’re making your purchases on Kinguin’s official website.
You should also take care not to use your credit card details when browsing with public WiFi networks to prevent your credit card from being compromised. If you must do so, make sure you do so using a premium VPN like Planet VPN to encrypt and protect your data traffic.
Other means of compromising your card might include exposing credit card details to third parties.
If you doubt the safety of your credit card details while making purchases on Kinguin, you can try using other payment channels like PayPal, Payoneer, Wise, etc.
Is Kinguin Safe To Buy From?
Yes, Kinguin is a safe marketplace to buy software codes from. The chances of getting scammed on Kinguin is extremely low, but you can take additional measures to ensure that you’re making a safe purchase by checking out the seller’s ratings and reviews from other buyers who have patronized such seller in the past.
Much like other eCommerce platforms, the risk does not come from Kinguin but from sellers who might want to take advantage of Kinguin’s marketplace platform to scam unsuspecting buyers.
However, Kinguin goes the extra mile to ensure that sellers on its platform are authenticated and that they sell codes that originated from genuine sources and are purchased using legal means.
Also, considering that Kinguin uses a combination of strong security protocols, including encrypting users’ data in transit with military-grade encryption protocols and strict privacy policies to protect users’ data, I will consider Kinguin, a safe marketplace for its users.
Kinguin has ‘buyer protection,’ which you pay for (not compulsory), and it will give you a refund if you purchased a fake or defective software code.
However, this policy only applies to some purchases, and you must meet Kinguin’s condition to be eligible for a refund if your purchased software key is fake or defective.
However, since it is an open marketplace, you should verify the authenticity of the seller you’re purchasing from before making a payment.
Software licenses are cheap on Kinguin for the following reasons:
Sellers on Kinguin acquire software licenses from cheap marketplaces outside of the US, where software licenses are sold at a much lower rate for economic reasons. Hence, developers can adjust prices based on economic indices like demand rate and average income. For example, a software license costing $100 in the US can cost $35 when purchased in Thailand. A reseller can make bulk purchases of software code in Thailand for $35 and resell in the US at 100% profit which would amount to $70, yet cheaper than the average cost of the software code in the US.
Sellers on Kinguin can buy software codes in bulk directly from developers at discounted rates and resell on Kinguin for profit at rates considered good buys by buyers.
Some sellers want to sell codes they purchased but didn’t use; hence they will be willing to sell at cheaper rates.
You’re not getting a physical copy of software licenses purchased on Kinguin.
You can purchase OEM keys at a much-reduced price
Does Kinguin Have Stolen Keys?
Keys sold on Kinguin’s marketplace are sourced legitimately; hence Kinguin does not offer stolen keys for sale.
Therefore, the chances of you ending up with a stolen key are very slim; however, you should ensure that you’re making purchases from verified resellers who have earned good ratings and reviews from previous buyers to ensure that you’re not purchasing a stolen or defective key.
Kinguin is not illegal because it is a legitimate eCommerce marketplace for the resale of software keys which in itself is not an illegal activity worldwide.
If you’re doubtful of Kinguin’s legality, you can look it up on Trustpilot or other trusted review websites.
In attesting to Kinguin’s legality, Kinguin has more than thirty thousand reviews with 4-star ratings on Trustpilot.
You should note that Kinguin does not permit the sale of stolen, defective, or illegally acquired keys on its marketplace; as such, Kinguin has put in place extra measures to discourage scammers from using its platform for illegal activities.
Is Kinguin Legit For Windows Keys?
Kinguin isn’t selling the keys themself. They’re a platform connecting buyers with third-party sellers. It’s like a digital flea market for software licenses.
That means the key’s legitimacy depends entirely on the seller. Some vendors offer genuine keys sourced directly from publishers, while others might sell grey-market keys obtained through less conventional means.
Grey-market keys can be legal but come with risks:
Shorter warranties or regional restrictions.
Higher chance of key revocation by Microsoft.
Potential for scams or unreliable keys.
Kinguin offers buyer protection, but it’s not foolproof. Negative reviews and reports of key revocations exist.
So, can you get a legit Windows key from Kinguin? Absolutely. But you’re taking a gamble.
No coupons found.
Why Are Kinguin Keys So Cheap?
Kinguin’s prices often undercut official retailers significantly. This can be due to:
1. Bulk Discounts: Some sellers on Kinguin purchase keys in bulk at significantly lower rates than official retail prices. This allows them to offer competitive prices even after factoring in platform fees.
2. Grey-Market Keys: These keys, while legal, are often obtained through less conventional means like regional price discrepancies or promotional offers. They might be intended for specific regions or acquired through authorized but unconventional channels. This allows sellers to offer lower prices but carries potential risks like shorter warranties or key revocation.
3. Lower Operating Costs: Compared to established stores, Kinguin operates with a leaner model, bypassing physical storefronts and relying on a digital platform. This translates to lower operating costs and possibly lower prices for consumers.
4. Competition: Kinguin operates in a highly competitive market with numerous grey-market key resellers. To attract buyers, they need to offer enticing prices, leading to a downward pressure on prices across the platform.
Remember: Cheap doesn’t always equal good. Consider the potential trade-offs:
Grey-market keys: Increased risk of key revocation, regional restrictions, or shorter warranties.
Unverified sellers: Potential scams or unreliable keys.
Buyer protection limitations: While Kinguin offers protection, it might not cover all issues.
Weigh the potential risks and rewards before purchasing from Kinguin. Ultimately, the decision rests on your comfort level with grey-market keys and online marketplaces.
Here are some alternative choices:
Official Microsoft Store: Offers guaranteed genuine keys and direct support but often at higher prices.
Other reputable retailers: Authorized resellers like Amazon or Newegg can provide reliable keys with warranties and customer support.
Choose wisely and game on!
What Country Is Kinguin Located?
While Kinguin operates globally with regional websites, its registered headquarters are in Hong Kong. They have additional offices in Poland and China, but their main legal and administrative base is located in Hong Kong.
Here’s a breakdown:
Registered company: Kinguin Limited
Headquarters: On Hing Terrace, Central, Hong Kong
Other offices: Poland (Warsaw) and China (Shenzhen)
So, although you might access Kinguin through a regional website, its official legal entity and governing jurisdiction reside in Hong Kong.
Does Kinguin Windows Key Work?
Absolutely! Kinguin can be your gateway to a genuine Windows experience at a fraction of the price. But before we dive in, let’s be transparent: Kinguin is a marketplace, not a store. This means the key’s legitimacy hinges on the seller.
Here’s the good news: Kinguin prioritizes verified sellers and offers buyer protection, ensuring a smooth ride most of the time. Millions of users worldwide have successfully activated Windows with Kinguin keys, unlocking a world of possibilities.
But here’s the cautionary note: Grey-market keys are common on the platform. These keys, while legal, may have limitations like shorter warranties or regional restrictions. A small chance of activation errors or key revocation also exists.
So, does it work? In most cases, yes! But with a bit more awareness and careful selection, you can maximize your chances of a seamless Windows experience.
Here are some tips for Kinguin success:
Choose sellers with high ratings and positive reviews.
Prioritize Microsoft-sourced keys for increased reliability.
Use secure payment methods like PayPal for buyer protection.
Be aware of the potential drawbacks and proceed with caution.
Bottom Line
Now, let’s conclude the Kinguin review. Kinguin is a legit online marketplace where you can find great deals on video games and other digital content.
However, as with any online marketplace, there is always the potential for scams, so it’s important to be aware of the risks before making any purchases. Overall, Kinguin appears to be a safe and reputable site, but buyer beware!
Although the sources of products sold on Kinguin cannot be ascertained as legal or illegal sources, Kinguin remains a legit marketplace where buyers can get cheap product keys for games and other software products.
In this post, I answered the questions – is Kinguin safe? is Kinguin legit? or is Kinguin a scam? If you have a different opinion, you can contact us or leave a comment below.