In this post, we will discuss about Guerassim Nikolov on securing firewalls, VPNs and other edge devices.
In February 2026, the US Cybersecurity and Infrastructure Security Agency (CISA) issued a binding directive aimed at technology that many organisations rarely revisit once installed: firewalls, VPN gateways, routers and other equipment at the boundary of the network that manufacturers no longer support. The directive describes the threat from these unsupported edge devices as substantial and constant, states that CISA is aware of widespread exploitation campaigns targeting them, and requires US federal civilian agencies to remove them within 18 months.
The directive itself applies only to those federal agencies. However, in a joint fact sheet, CISA, the FBI and Britain’s National Cyber Security Centre (NCSC) strongly urge every organisation to examine it and implement the recommended mitigations. The same document notes that as these devices age, managing their risks becomes increasingly challenging and costly.
Network security is one of Guerassim Nikolov’s core areas of expertise, and he puts the issue plainly: “Edge devices are the front door of the enterprise network. When that door is running on equipment its manufacturer has stopped maintaining, every newly discovered weakness stays open for good, and attackers know exactly where to look.”
Table of Contents
The edge as a target
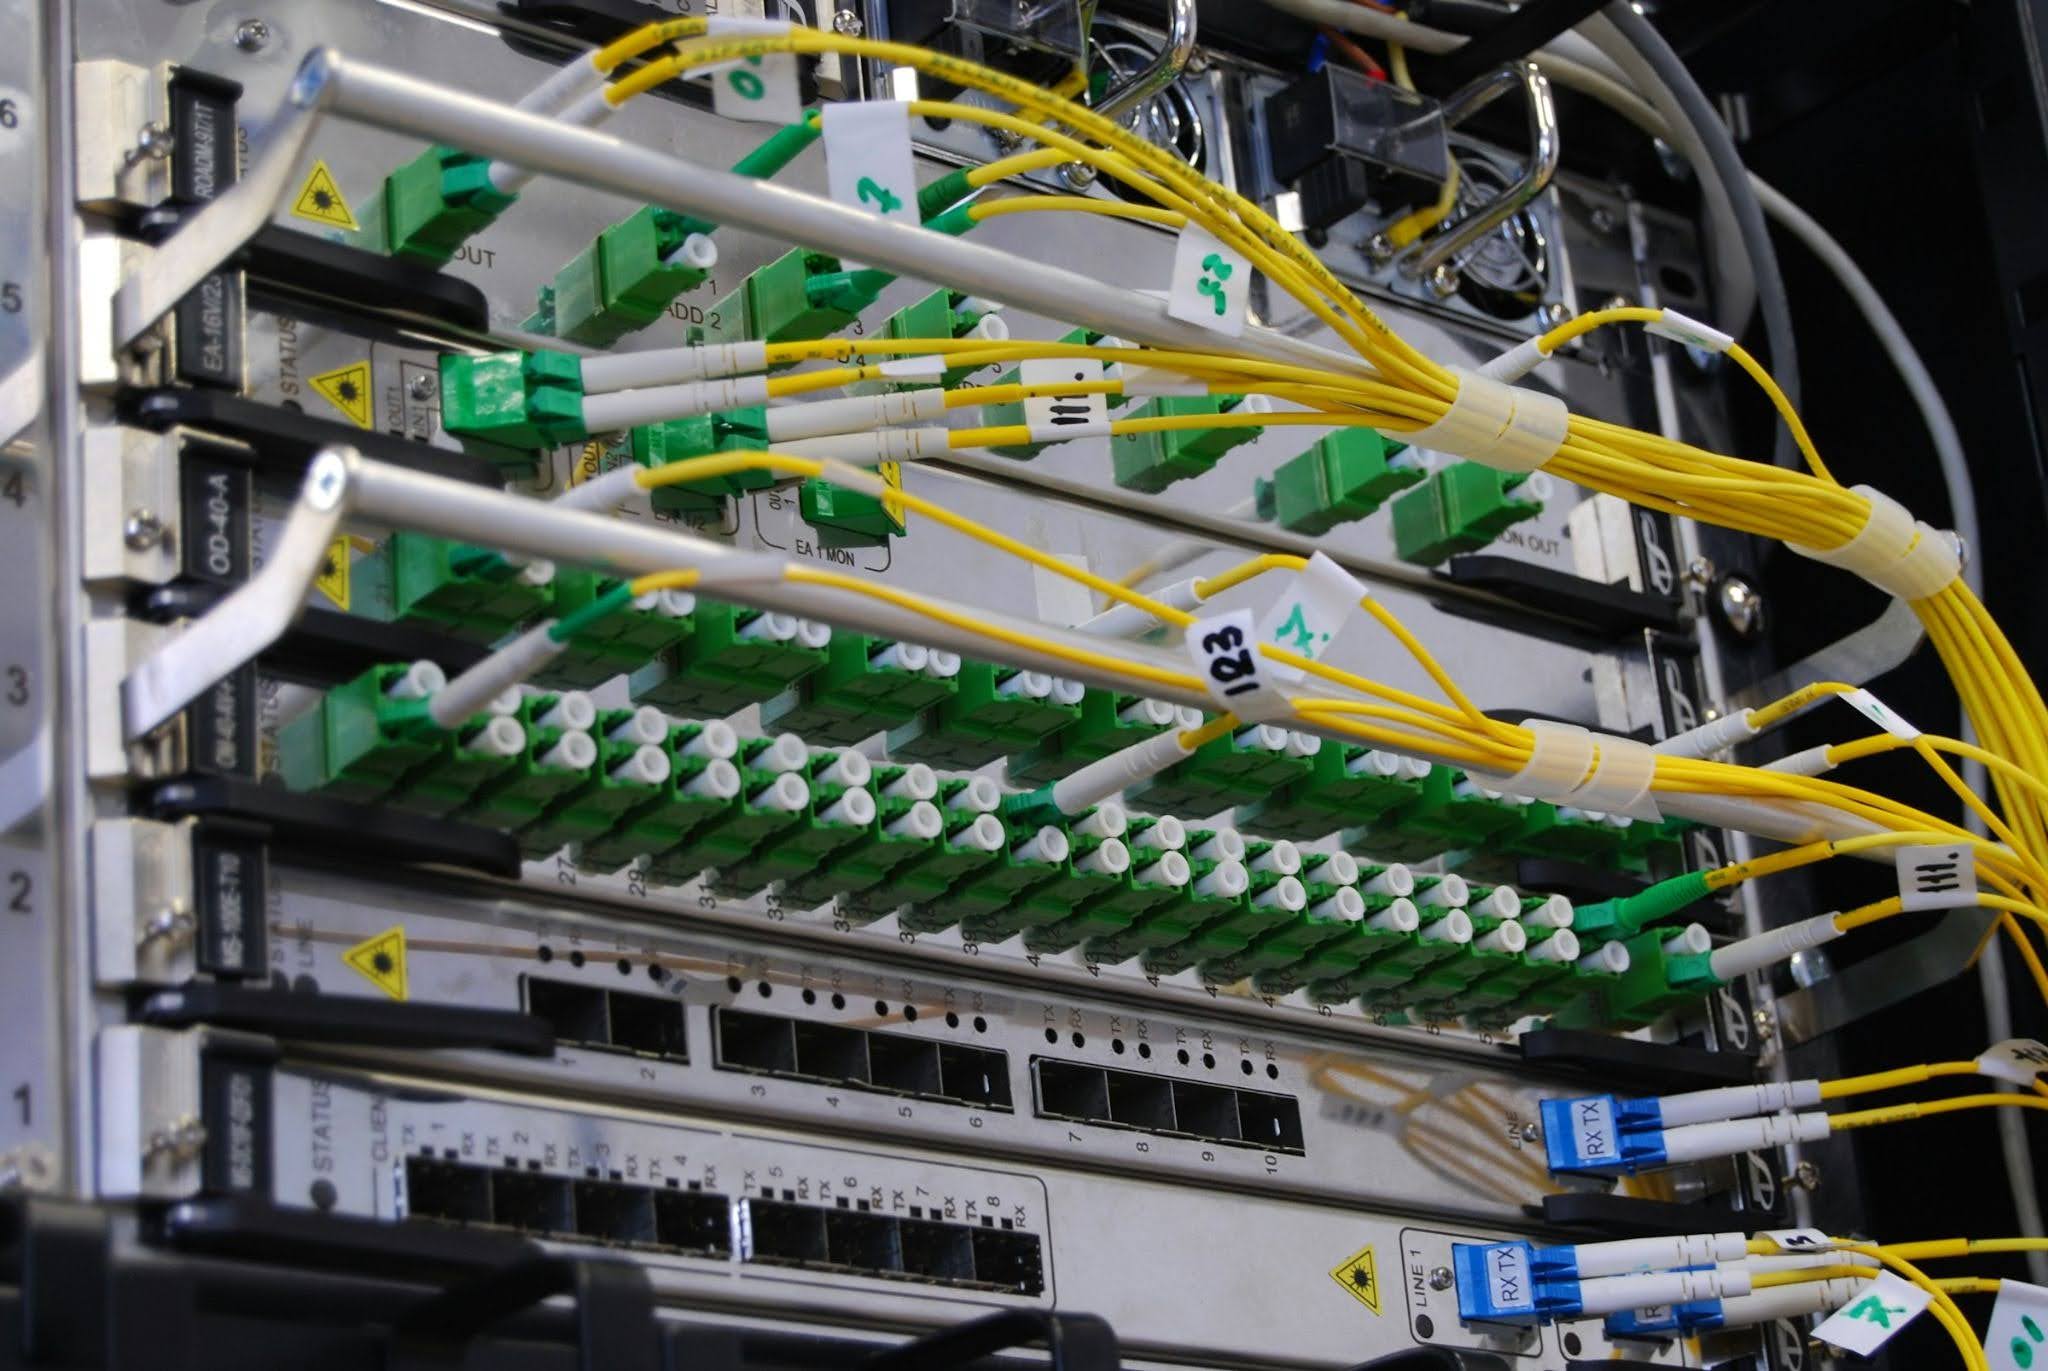
The joint fact sheet defines edge devices as technology that sits on the boundary of an organisation’s network and is accessible from the public internet and other external environments. A device becomes end-of-support when its manufacturer no longer monitors it for defects or issues patches for known vulnerabilities.
That combination of exposure and neglect makes such equipment valuable to attackers. The fact sheet states that nation-state threat actors exploit end-of-support edge devices, using them to gain network access, maintain presence and compromise sensitive data. It adds that these devices can serve as entry points into modern, supported environments, so a single outdated gateway can undermine investment elsewhere in the estate.
Visibility before anything else
Knowing what sits at the edge is harder than it sounds, because devices installed for a project, a branch office or a temporary need often remain long after their purpose is forgotten.
The joint fact sheet recommends actively scanning networks for undocumented and outdated edge devices, maintaining an inventory of every edge device together with its support timeline, and regularly reviewing that inventory and the associated end-of-support dates. Recorded properly, those dates turn a hidden liability into a predictable schedule of replacement.
“Most organisations know how many laptops they own, yet far fewer can produce a reliable list of every device facing the internet and the date each one stops receiving updates,” Guerassim Nikolov says. “That list is the foundation for every other decision, from patching priorities to capital budgets.”
Patching by real-world risk
Not every vulnerability carries the same urgency. CISA maintains its Known Exploited Vulnerabilities catalog as the authoritative source of vulnerabilities that have been exploited in the wild, and advises organisations to use it as an input to their vulnerability management prioritisation. For edge devices, where exposure to the internet is constant, flaws that appear in the catalogue warrant immediate attention.
The joint fact sheet also recommends installing updates, patching known vulnerabilities and enabling automatic updates on all devices. Where an end-of-support device cannot be replaced straight away, it advises keeping it on the latest supported software version until it can be retired.
Specialist managed service providers are well placed to take on external scanning and patch tracking. A provider that views the estate from the internet inwards can flag a newly exposed device or an unpatched flaw quickly, leaving decisions on architecture and replacement with the organisation’s engineers.
Retiring devices on schedule
The most effective point to address an end-of-support device is before support ends. When support dates are known in advance, replacement can be built into capital plans, timed to avoid disruption and specified with security in mind.
International guidance gathered by CISA, drawing on work by Canadian, Australian and UK agencies, covers securing, hardening and managing edge devices, and includes NCSC specifications noting that security logging and data collection features enabled by default help defenders detect and investigate intrusions. Those expectations can be written into procurement requirements for replacement equipment.
“Retiring a firewall or VPN gateway should be a planned milestone in the life of the asset,” Guerassim Nikolov says. “Leadership teams that see the end-of-support dates in advance can fund replacement deliberately, and the organisation avoids the far higher cost of investigating an intrusion that started at an unmaintained device.”
The practical sequence
For organisations outside the US federal government, the directive offers a useful framework rather than an obligation. Find every device at the network edge through regular scanning. Record when each one stops receiving manufacturer updates. Patch actively exploited flaws first. Replace equipment before its support ends. Taken together, those steps reduce one of the most exposed parts of the enterprise to a manageable, well-understood risk.
About the Author:
Meet Angela Daniel, an esteemed cybersecurity expert and the Associate Editor at SecureBlitz. With a profound understanding of the digital security landscape, Angela is dedicated to sharing her wealth of knowledge with readers. Her insightful articles delve into the intricacies of cybersecurity, offering a beacon of understanding in the ever-evolving realm of online safety.
Angela's expertise is grounded in a passion for staying at the forefront of emerging threats and protective measures. Her commitment to empowering individuals and organizations with the tools and insights to safeguard their digital presence is unwavering.